Azure-AD-Incident-Response-PowerShell-Module

The Azure Active Directory Incident Response PowerShell module provides a number of tools, developed by the Azure Active Directory Product Group in…

The Azure Active Directory Incident Response PowerShell module provides a number of tools, developed by the Azure Active Directory Product Group in…

PowerShell module for administering and auditing Azure AD and Office 365, enabling token manipulation, user enumeration, and security assessments of…

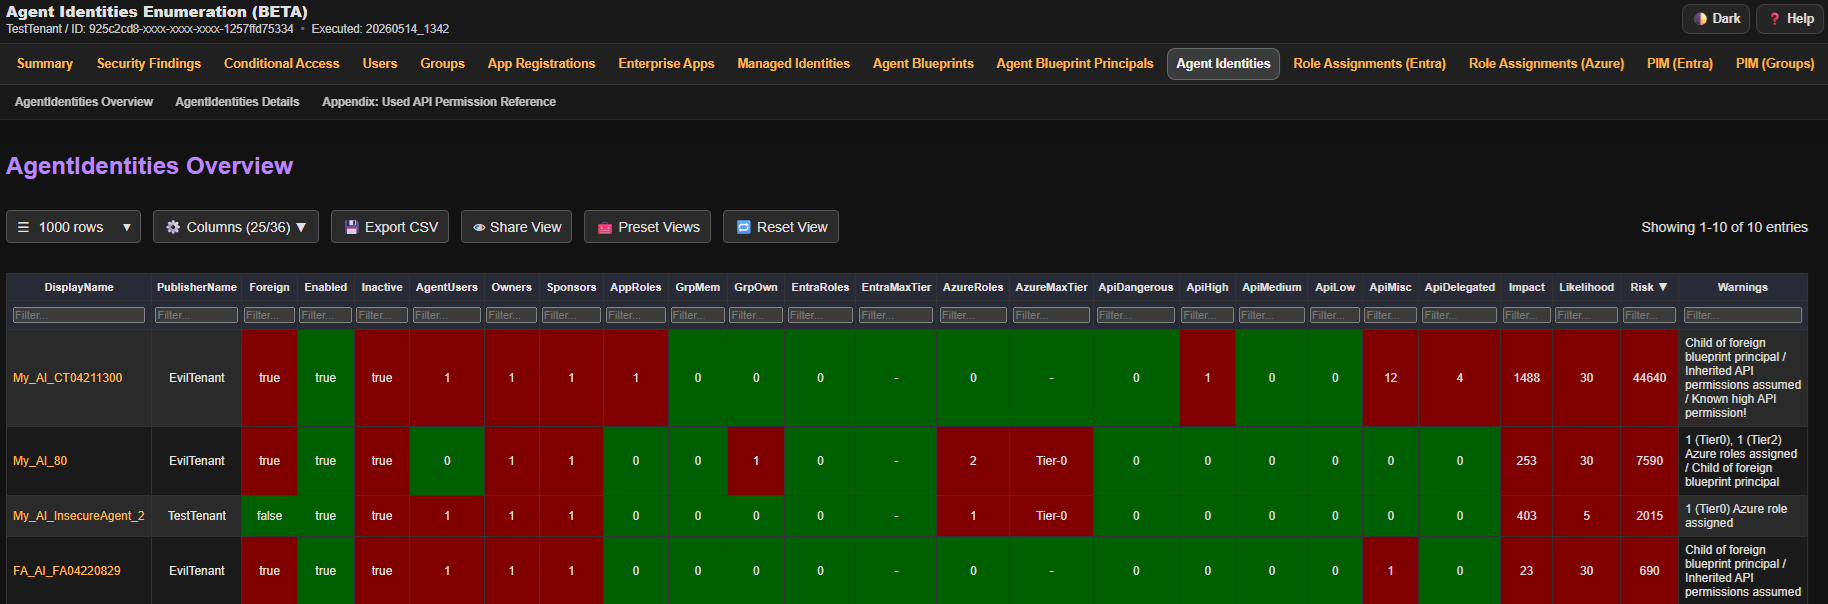
A lightweight PowerShell tool for assessing the security posture of Microsoft Entra ID environments. It helps identify privileged objects, risky…

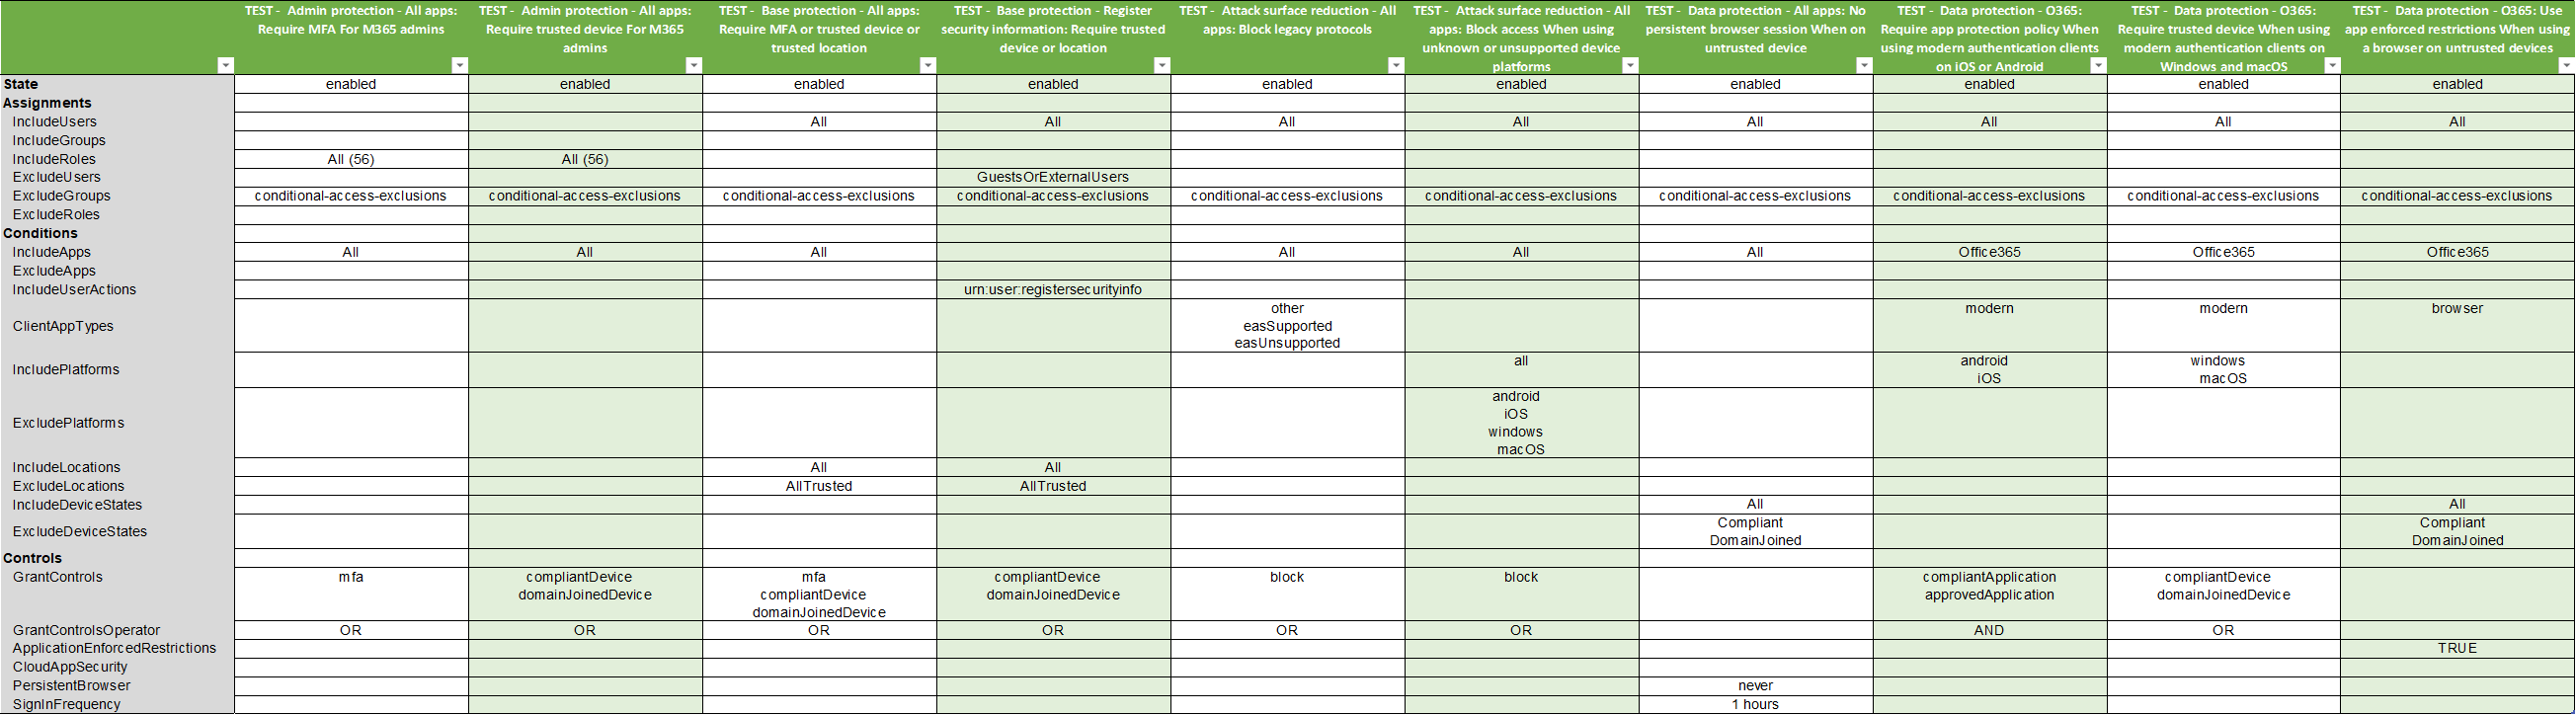
Microsoft Entra Conditional Access Documentation with PowerShell

Bash and PowerShell scripts for Azure security assessments, covering IAM privilege escalation, container registry exploitation, Key Vault exposure,…

Read-only PowerShell module for detecting UNC2452 and other threat actor artifacts in Azure AD, auditing federated domains, service principals,…

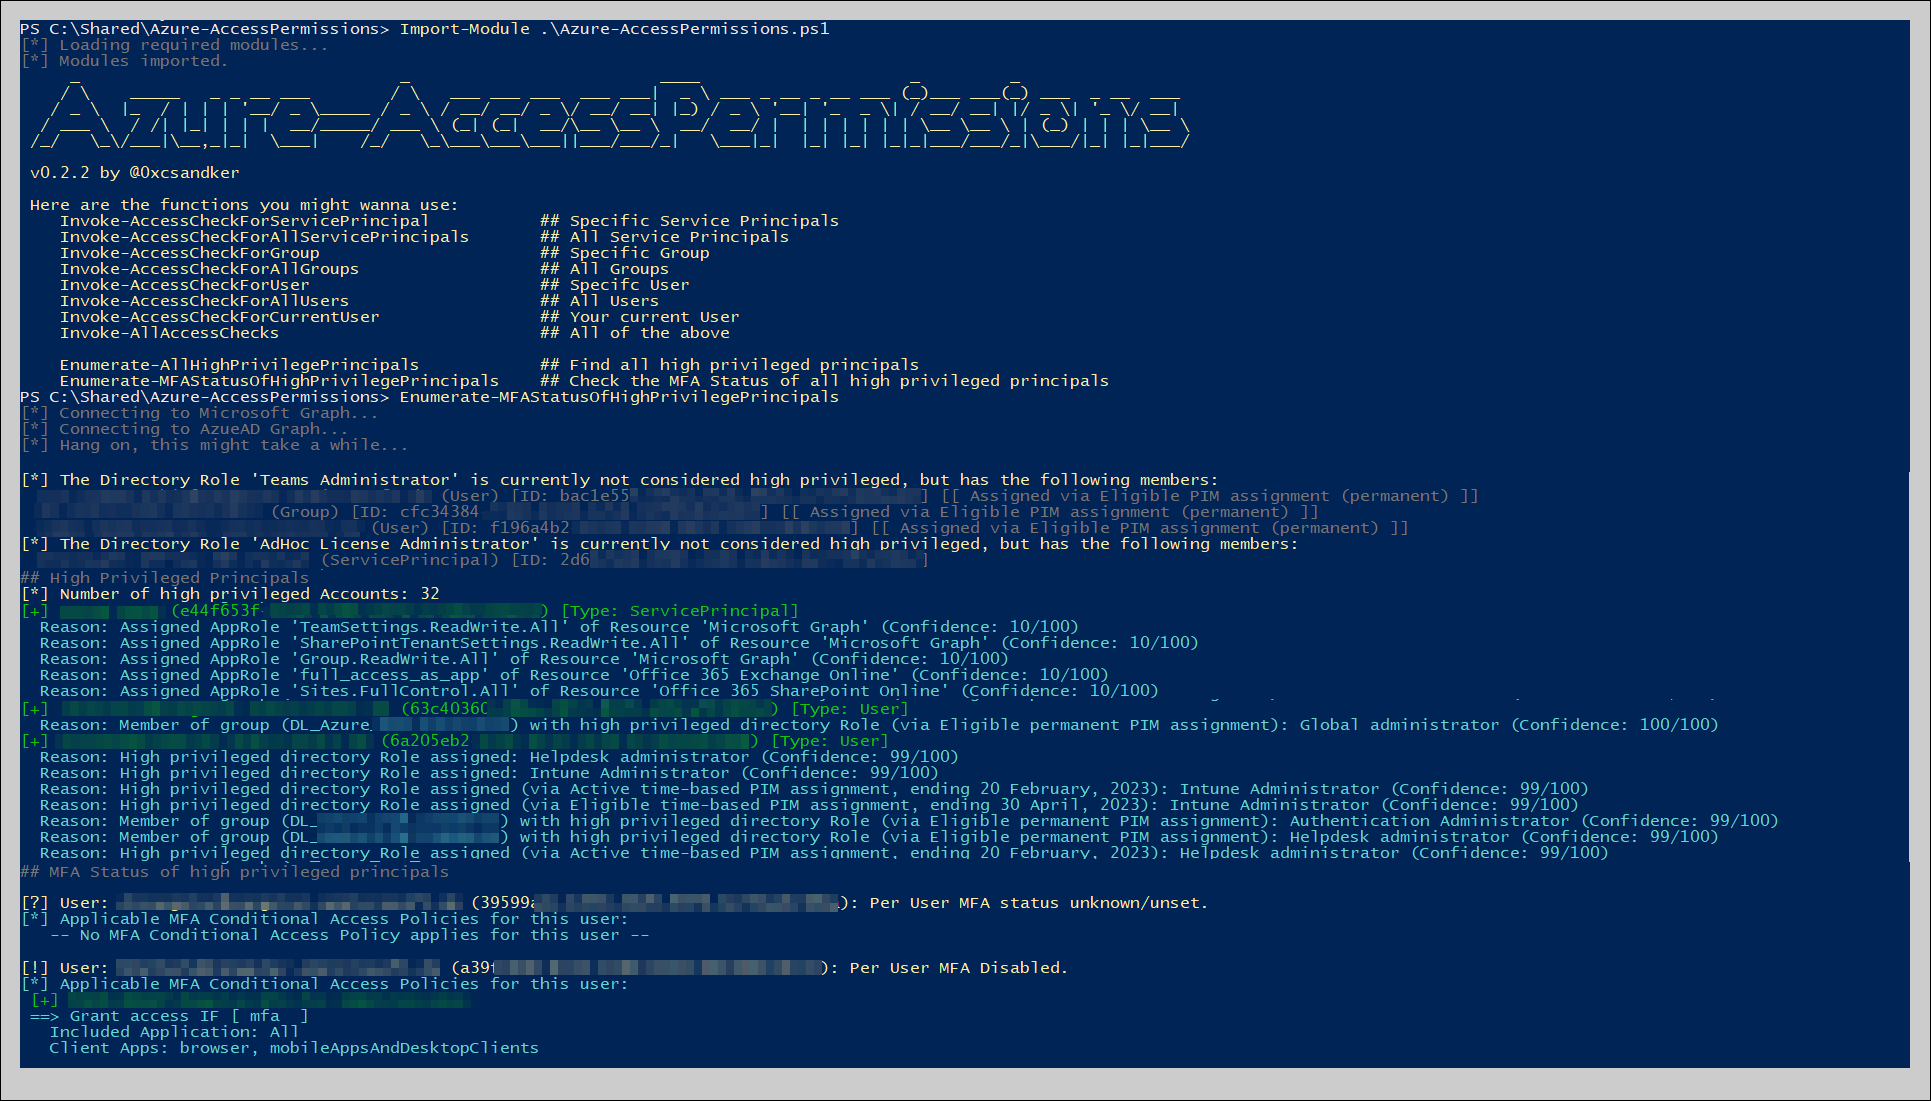
PowerShell script to enumerate Azure Active Directory access permissions, including role assignments, service principals, and privileged access…

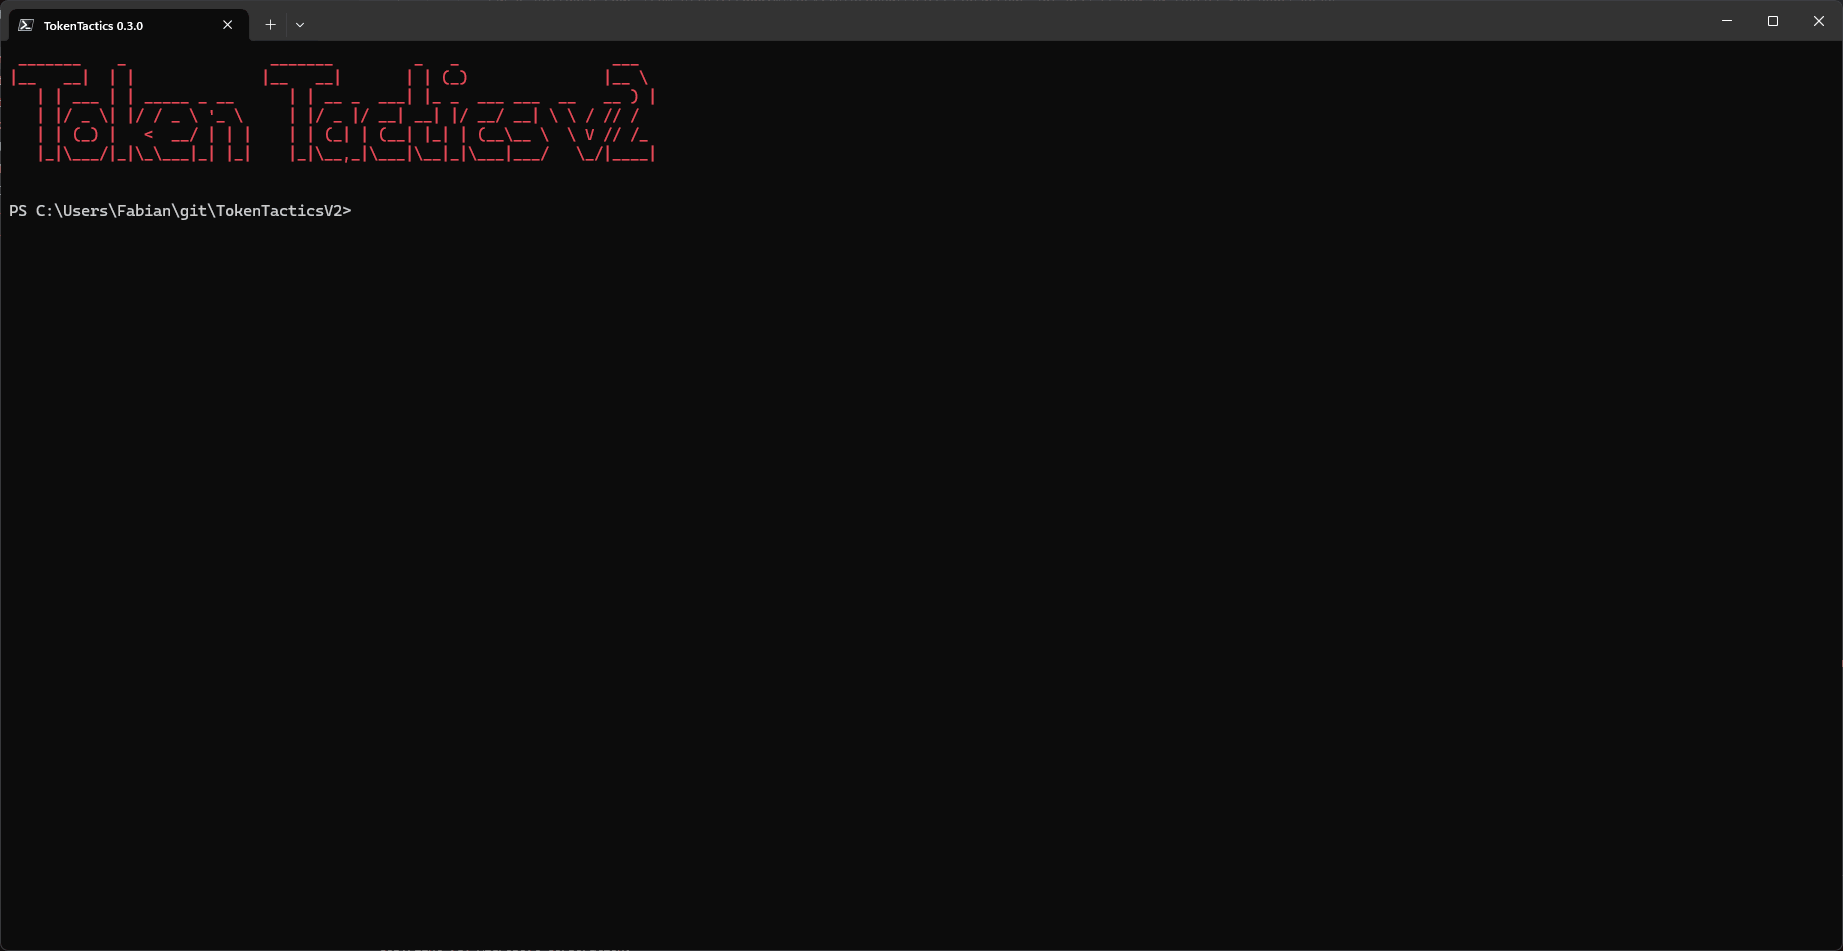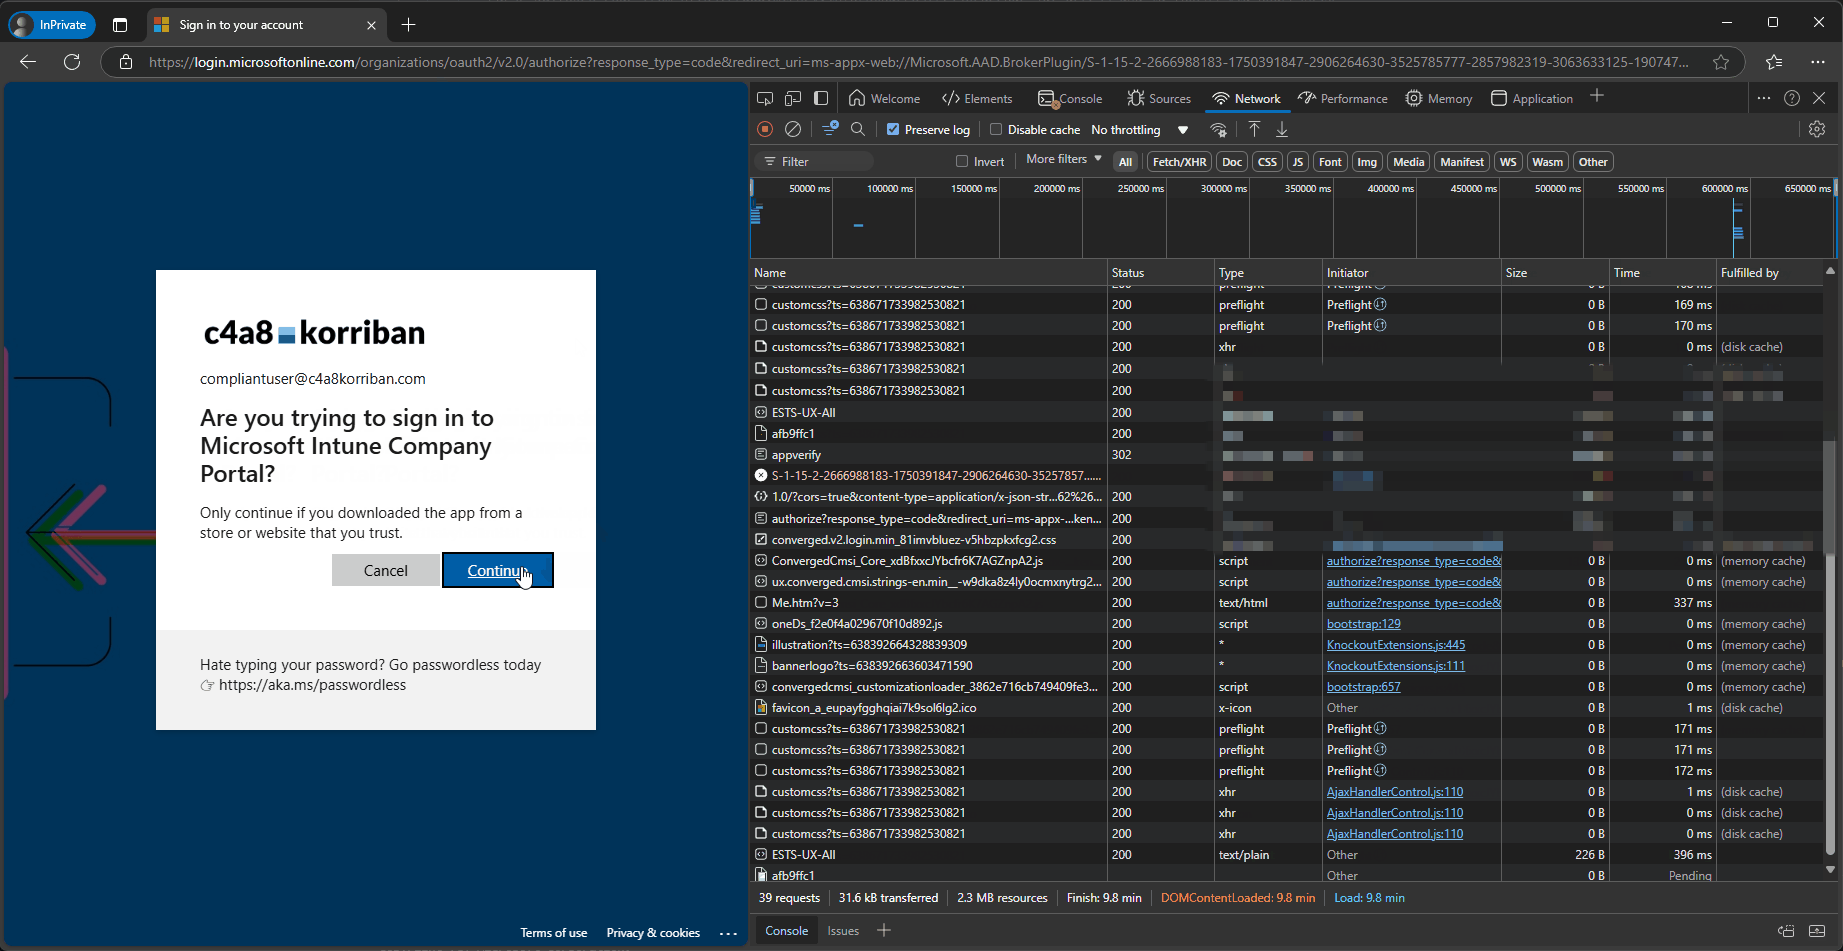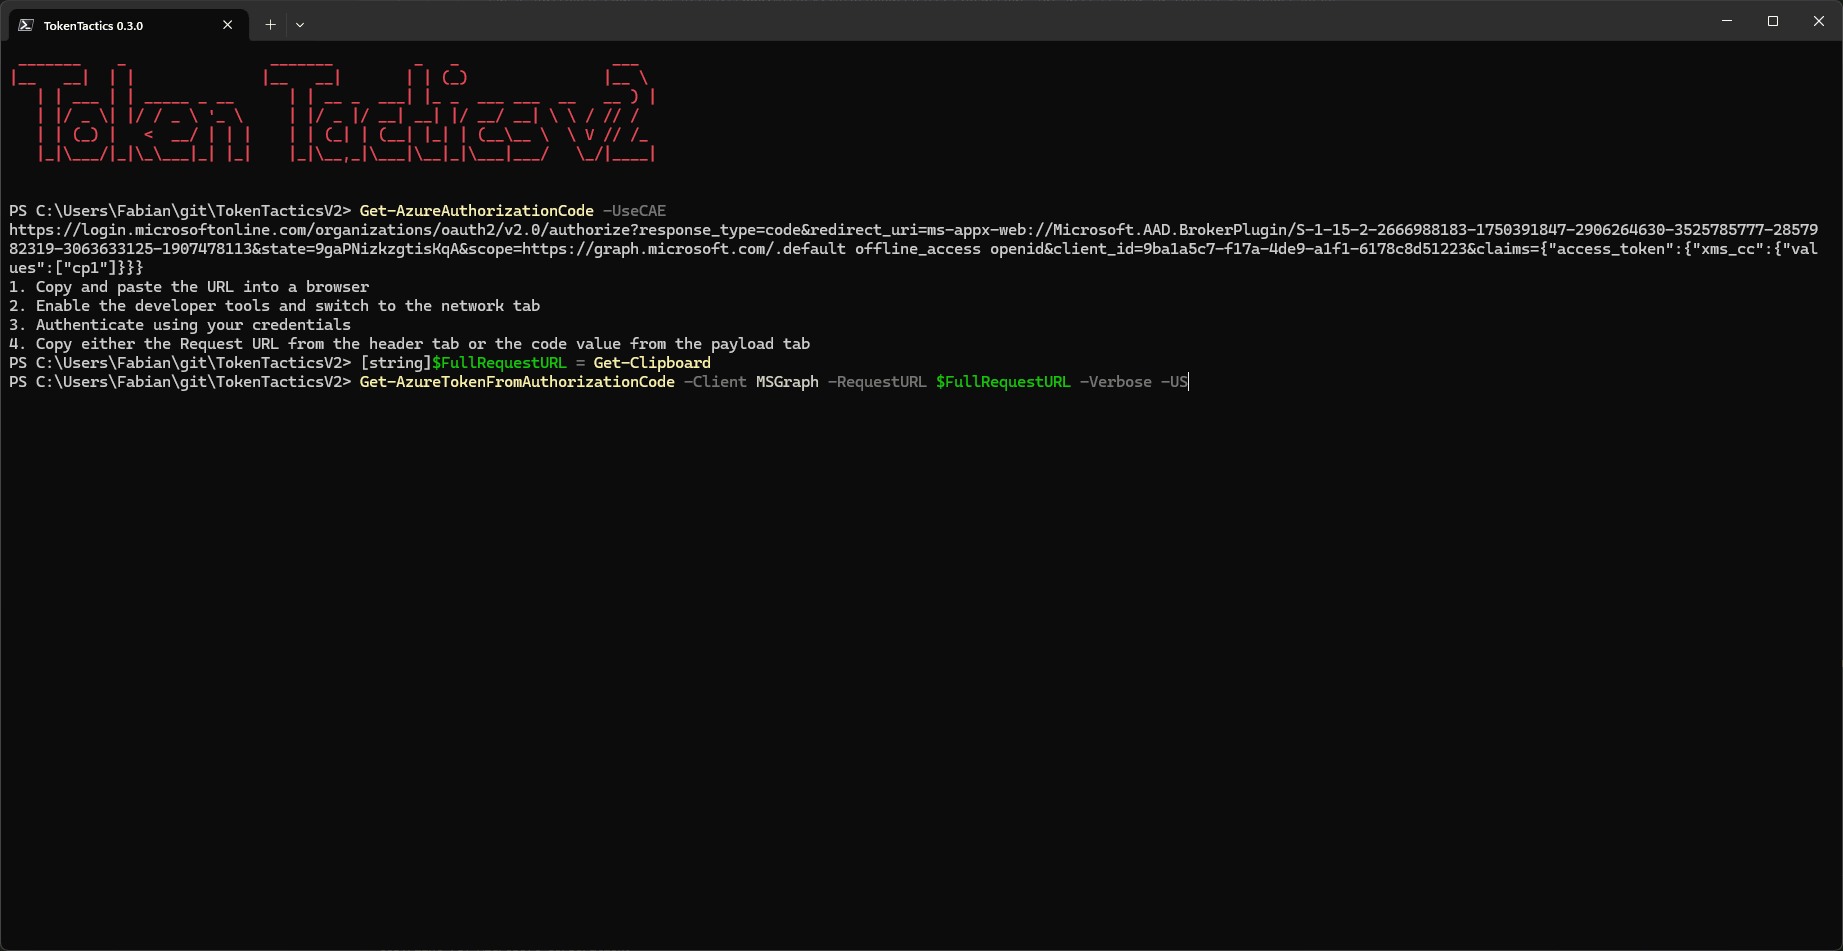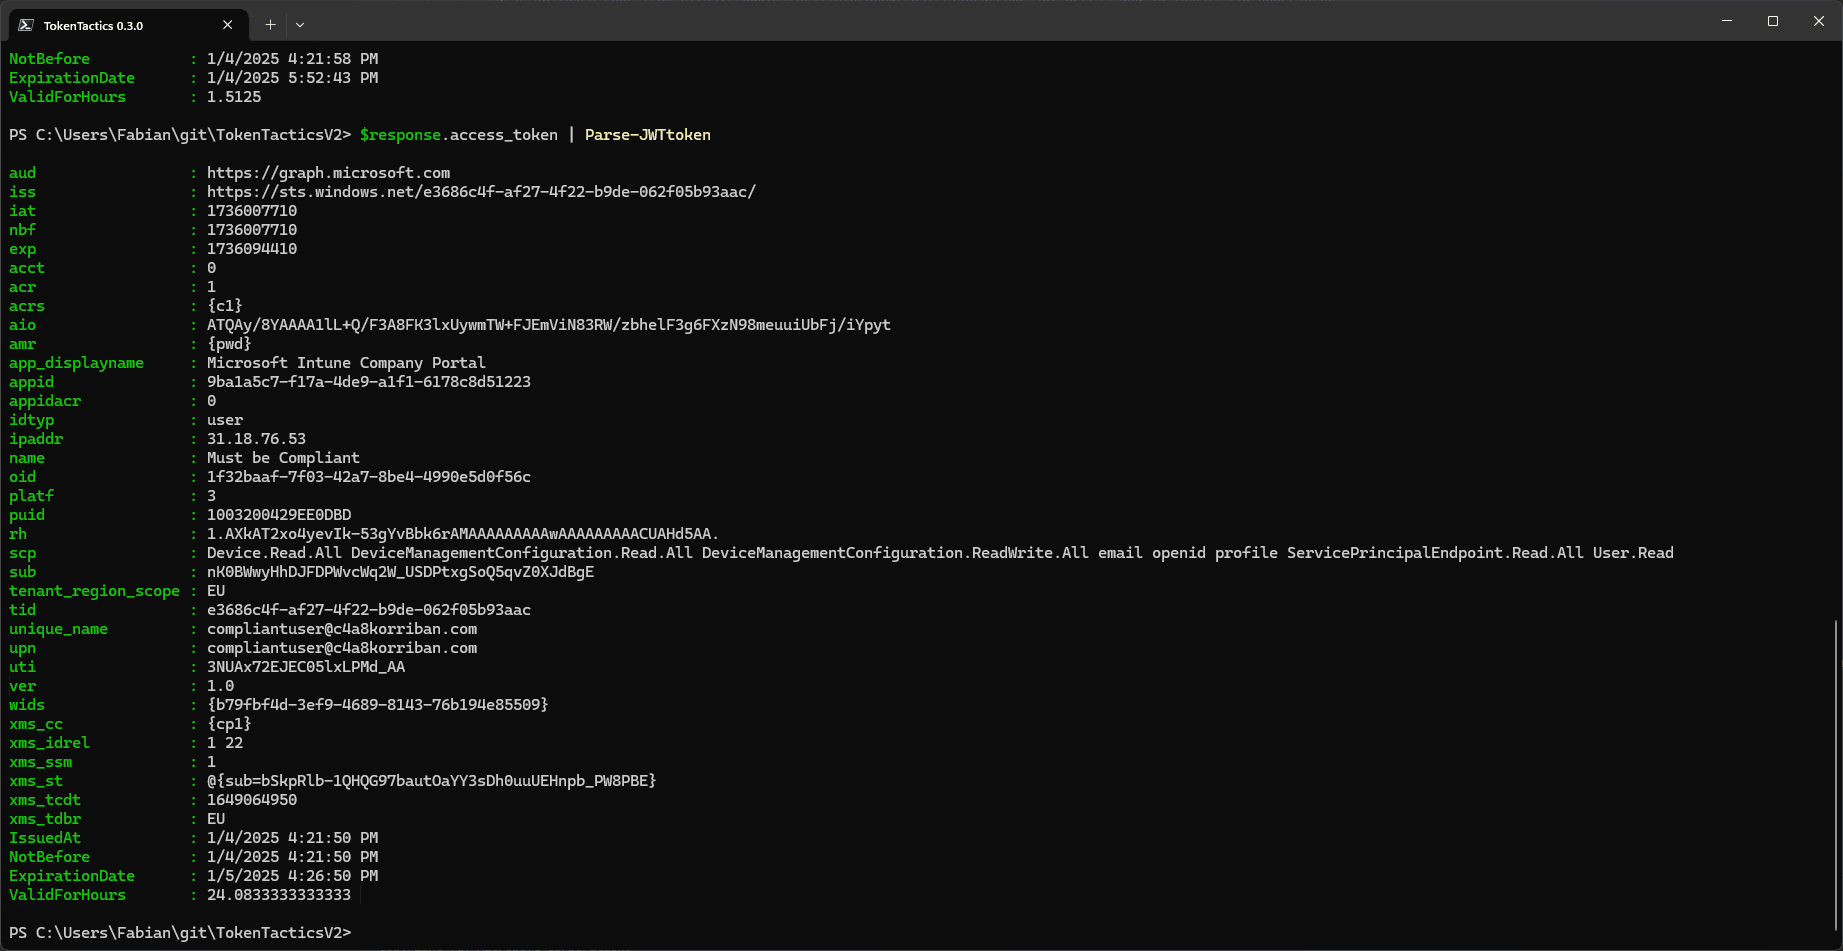
A fork of the great TokenTactics with support for CAE and token endpoint v2

Active Directory password filter featuring breached password checking and custom complexity rules


CyberArk Security Audit

Kerberos RC4 deprecation: detection, remediation and guidance (CVE-2026-20833)

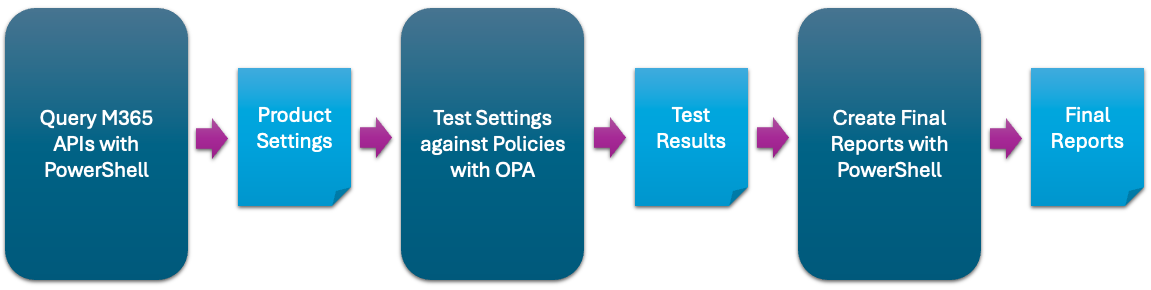
Automation to assess the state of your M365 tenant against CISA's baselines

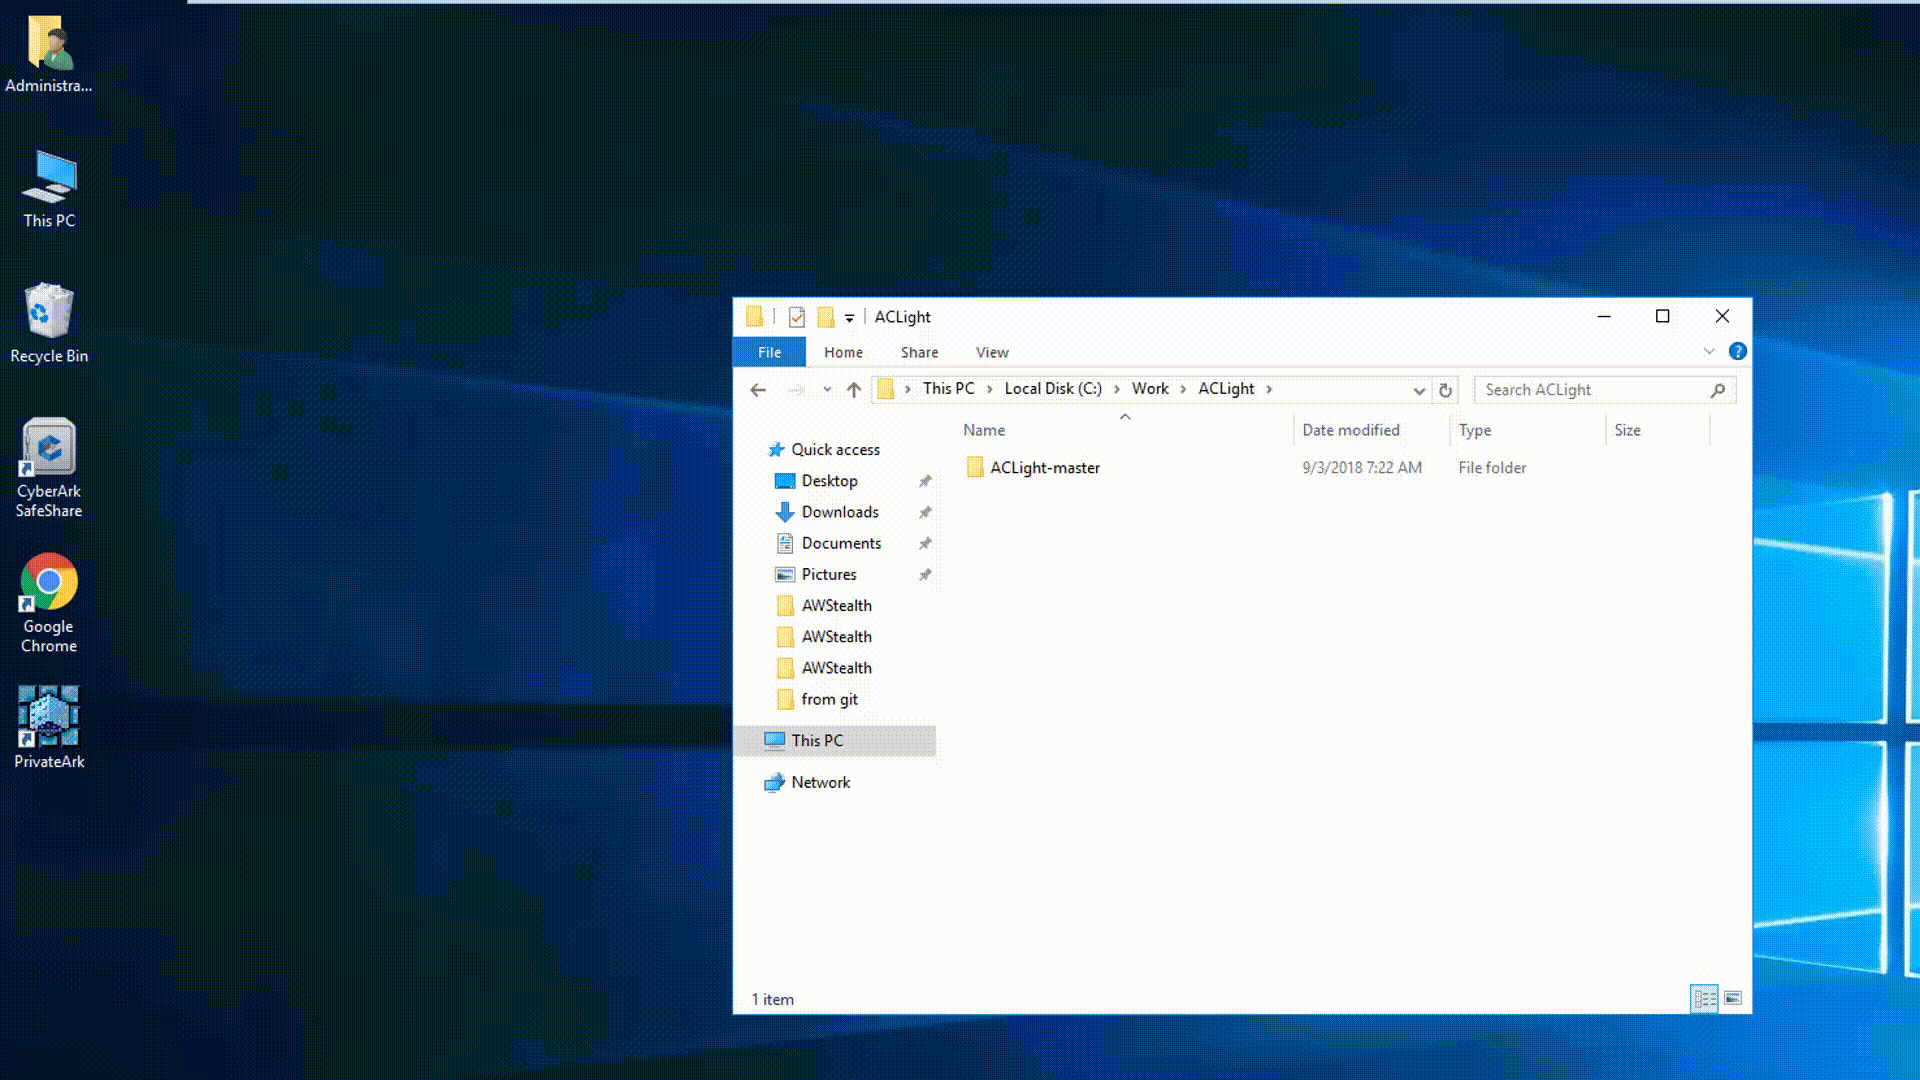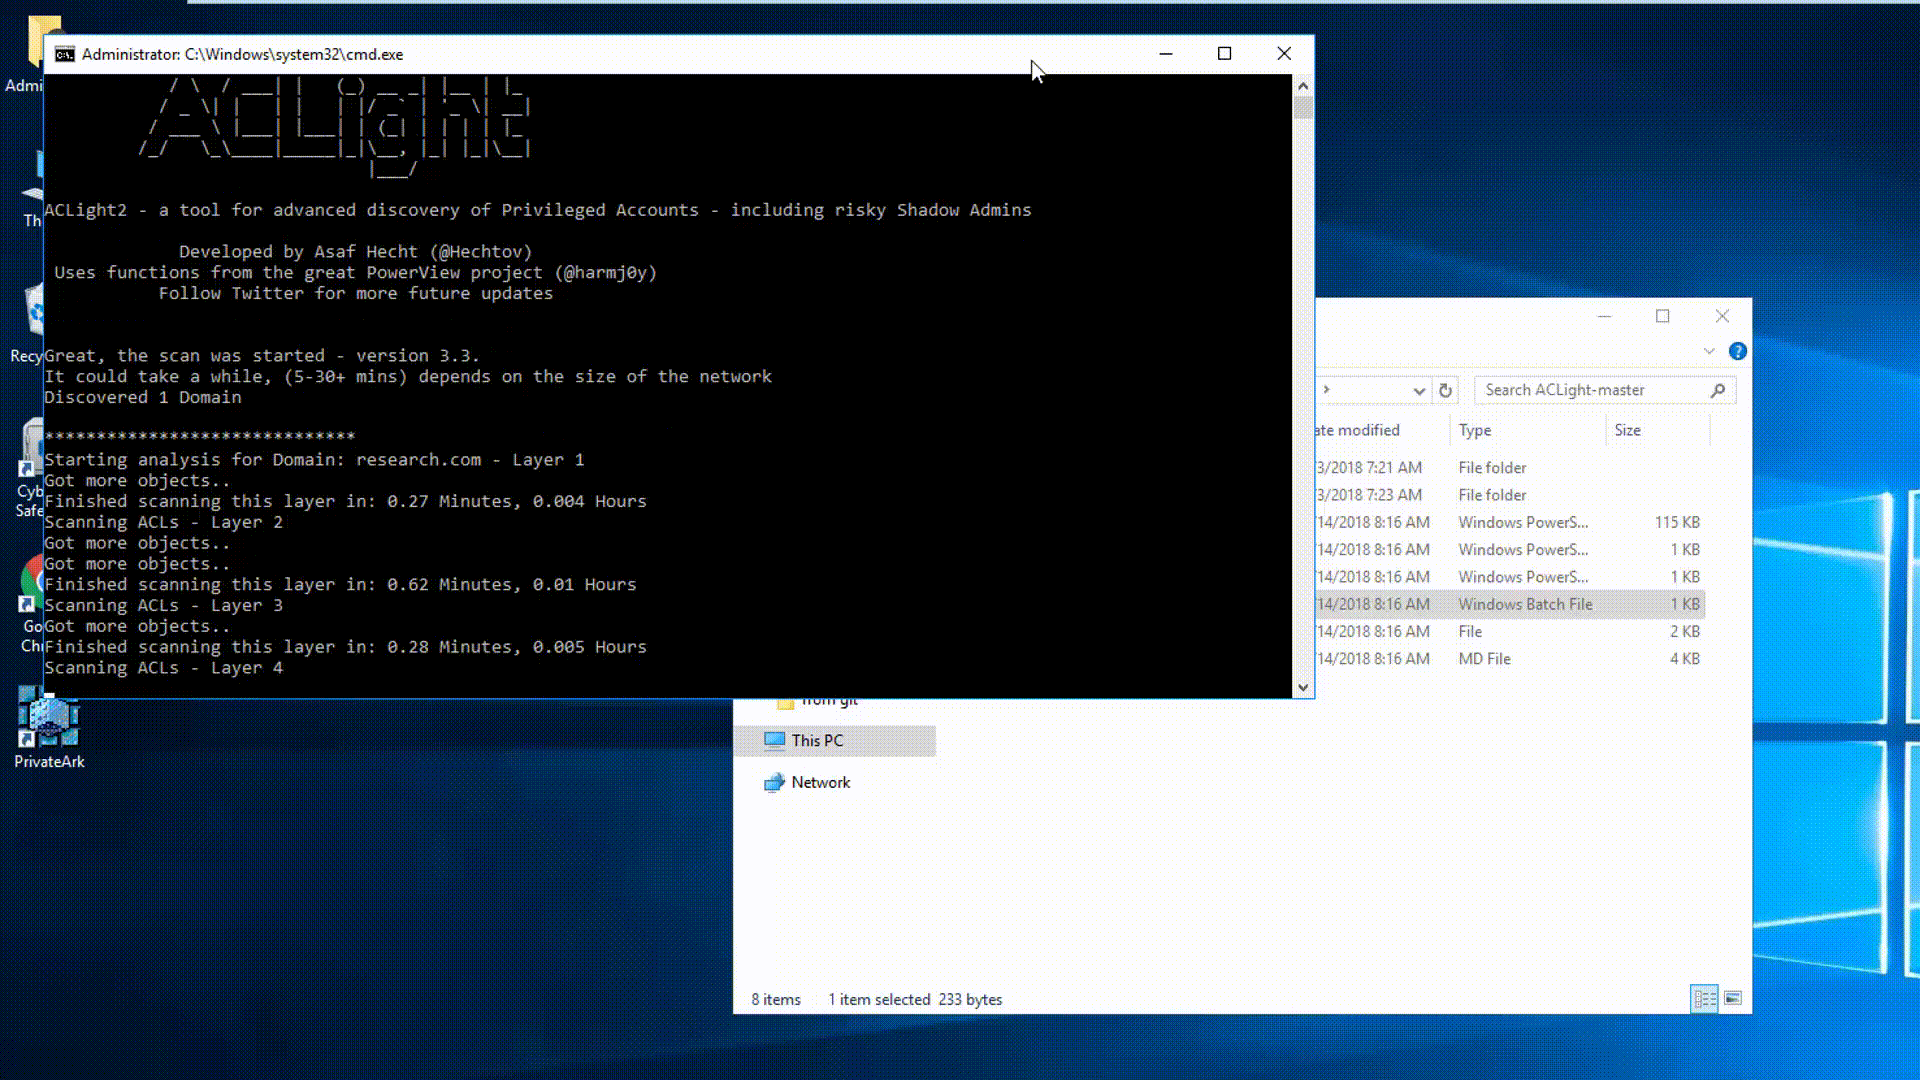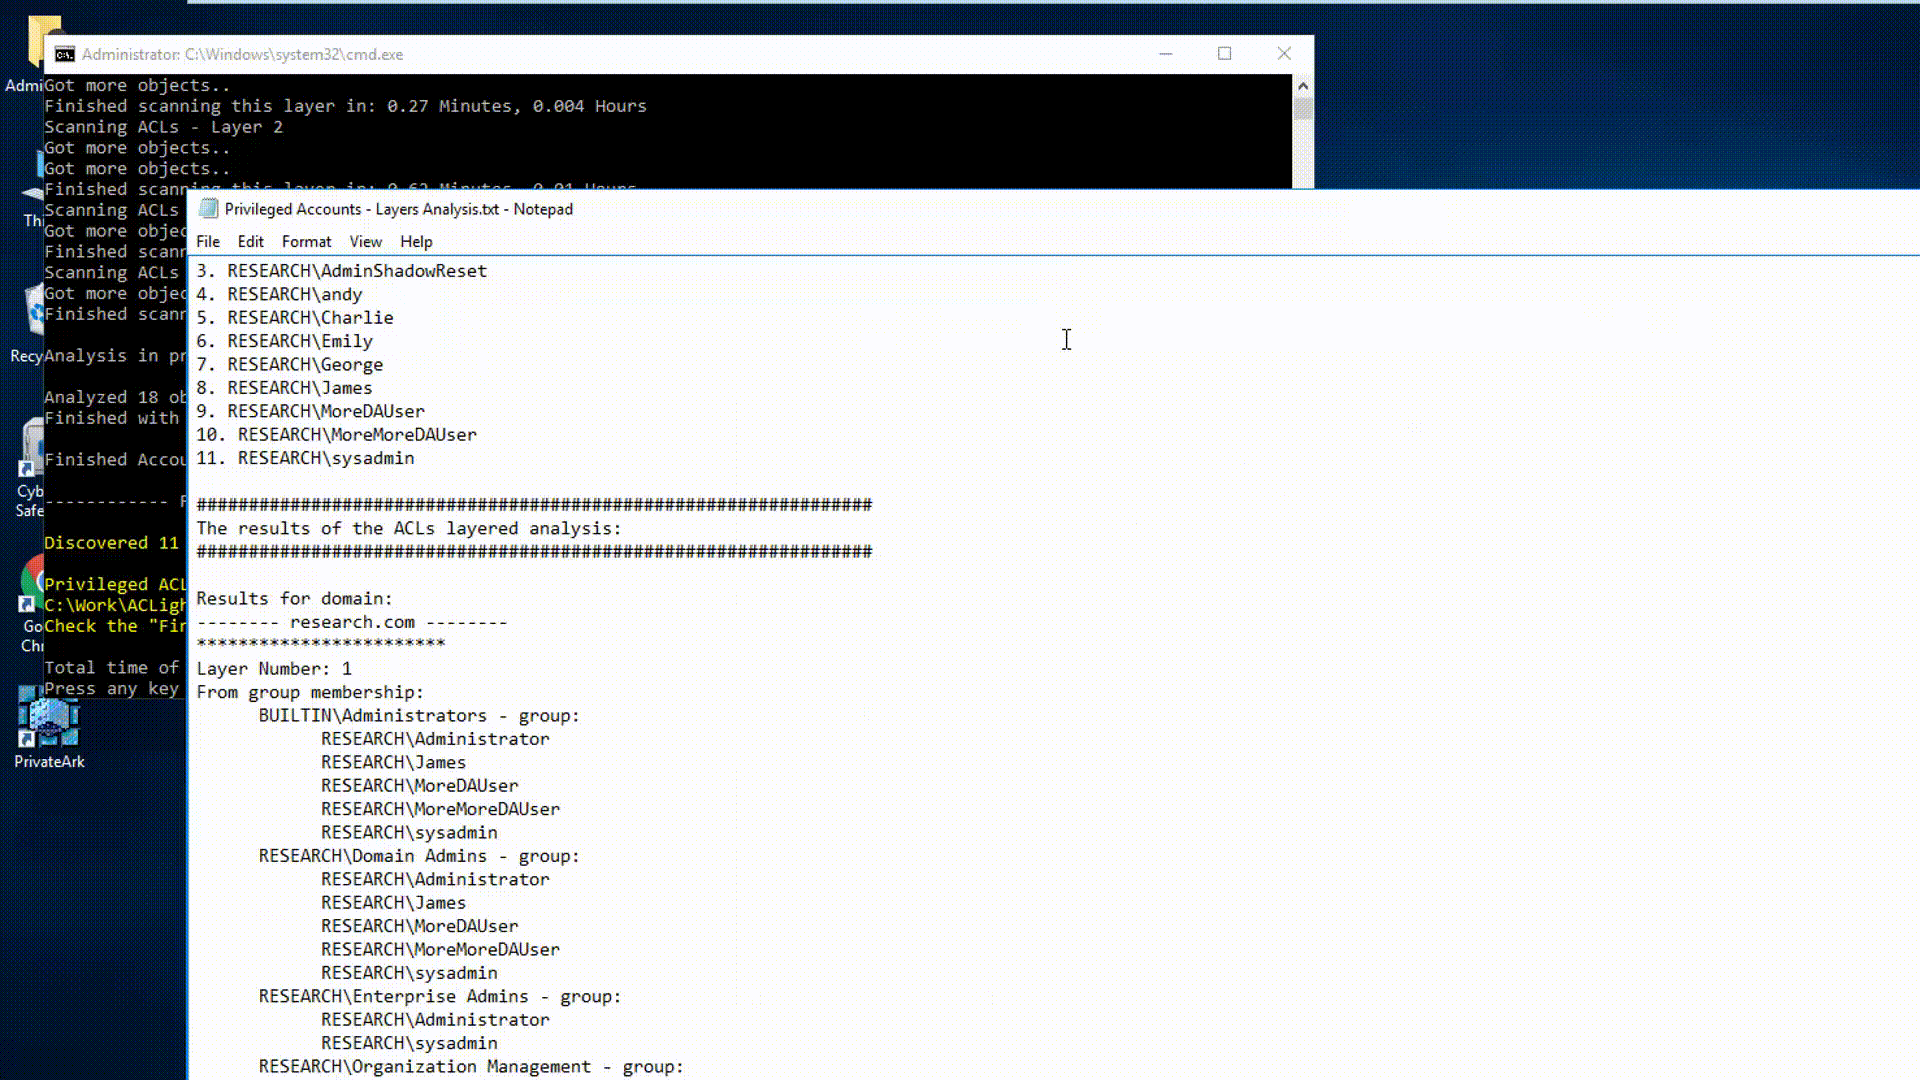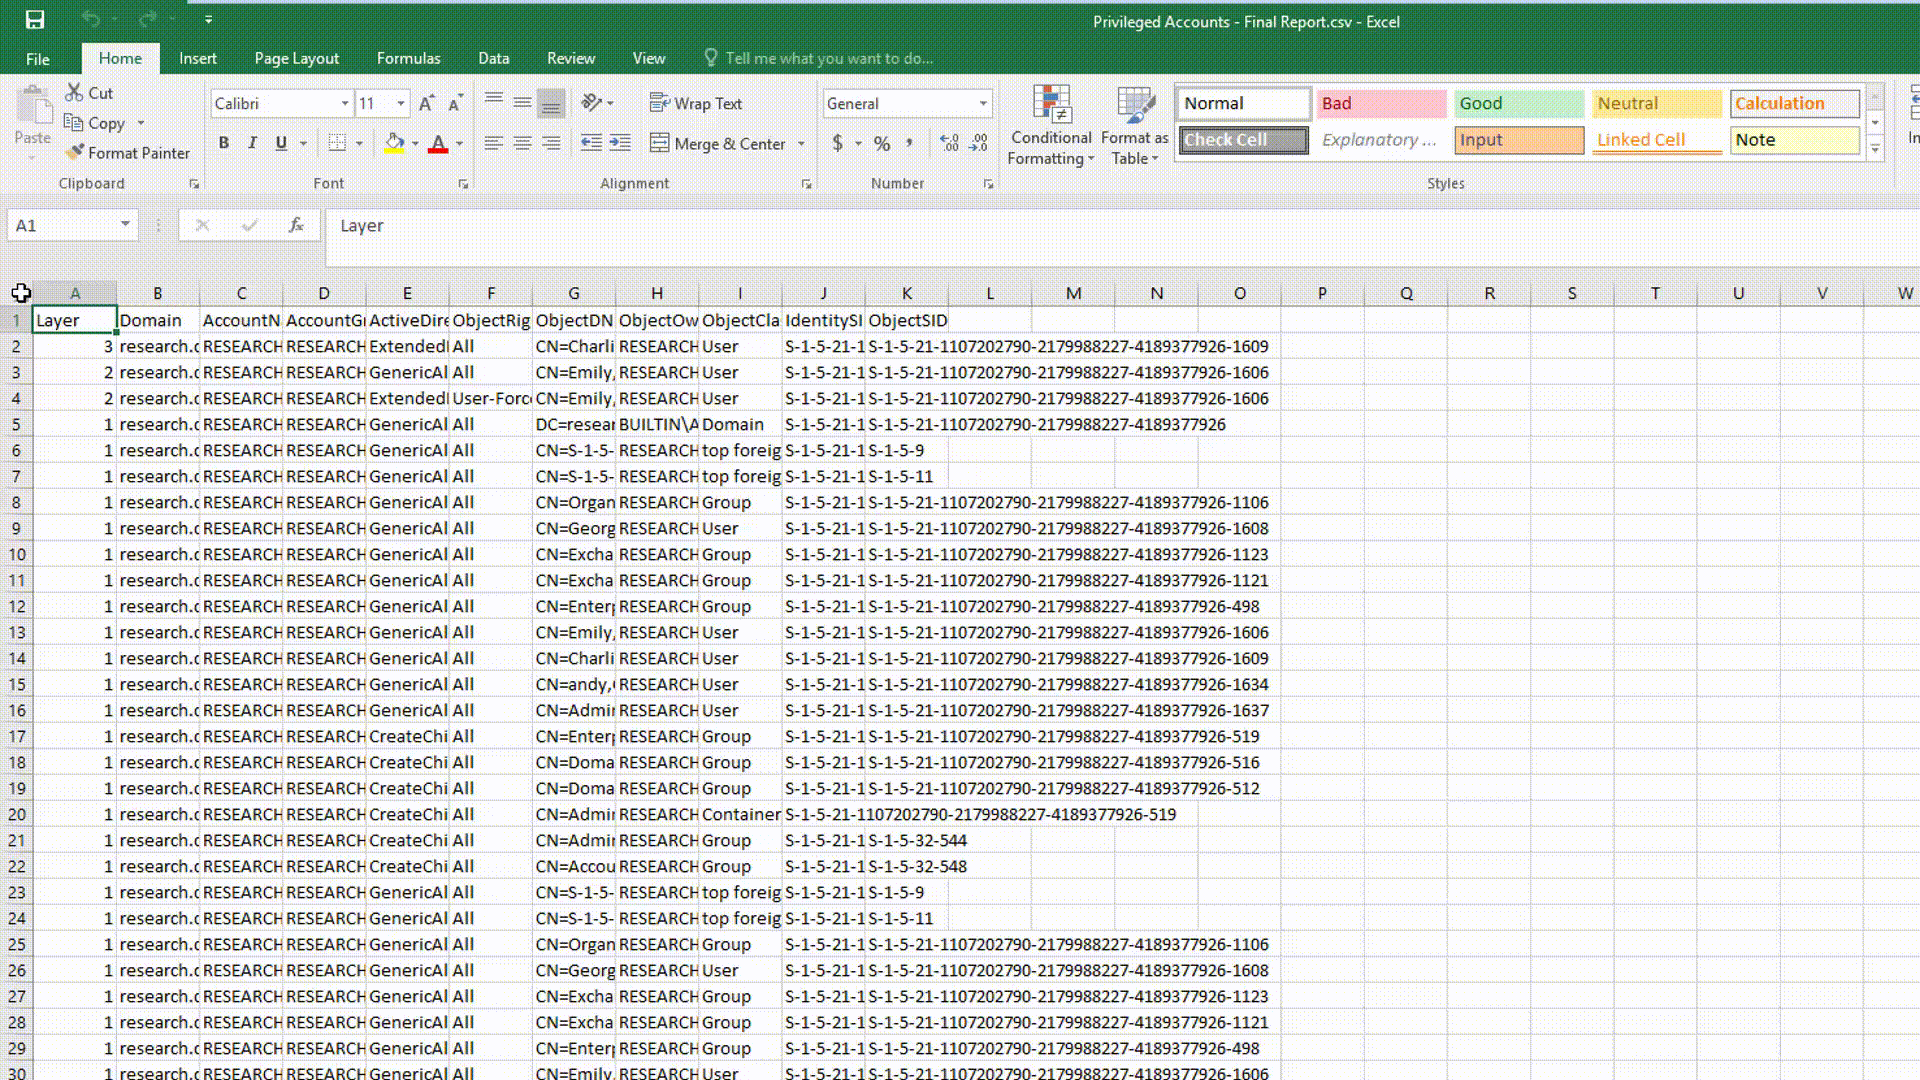
A script for advanced discovery of Privileged Accounts - includes Shadow Admins

SkyArk helps to discover, assess and secure the most privileged entities in Azure and AWS

Tooling for assessing an Azure AD tenant state and configuration

Protect your domain controllers against Zerologon (CVE-2020-1472).

MAAD Attack Framework - An attack tool for simple, fast & effective security testing of M365 & Entra ID (Azure AD).