

BloodHound
 specterops/bloodhound
Six Degrees of Domain Admin
defensive-toolsidentity-access-managementinformation-gathering+4
specterops/bloodhoundSix Degrees of Domain Admin
 dirkjanm/roadtools
A collection of Azure AD/Entra tools for offensive and defensive security purposes
 gerenios/aadinternals
PowerShell module for administering and auditing Azure AD and Office 365, enabling token manipulation, user enumeration, and security assessments of…
 pushsecurity/browser-identity-attacks-matrix
Offensive security drives defensive security. We're sharing a collection of SaaS attack techniques to help defenders understand the threats they…
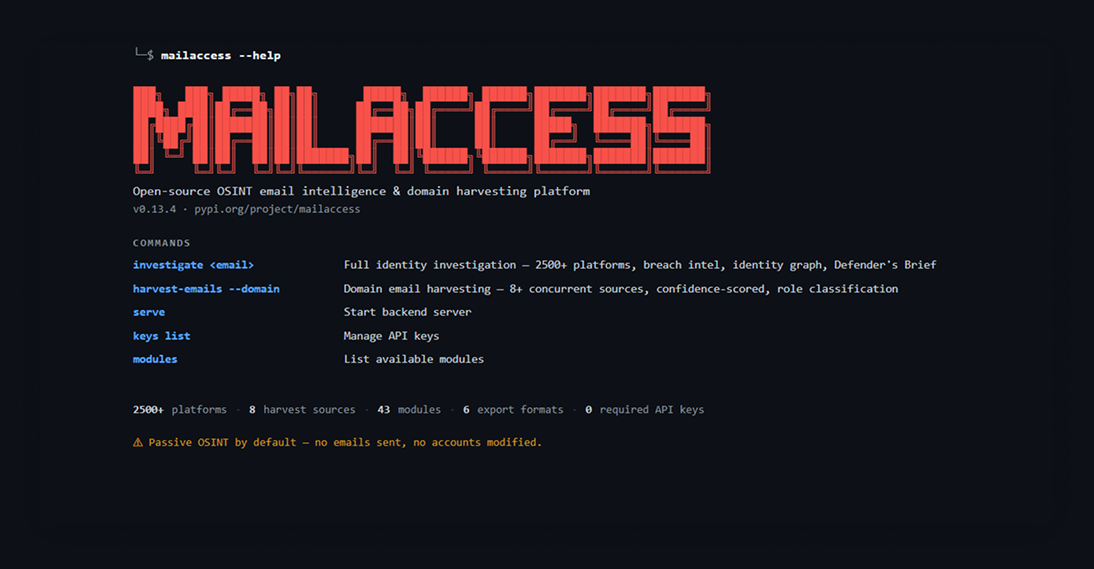 katrielmoses/mailaccess
Free email OSINT tool, 2500+ platforms, identity clustering, breach detection. No API keys required. pip install mailaccess
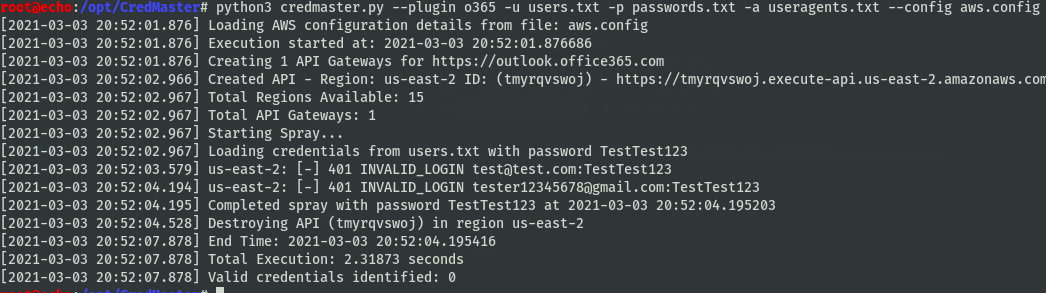 knavesec/credmaster
Refactored & improved CredKing password spraying tool, uses FireProx APIs to rotate IP addresses, stay anonymous, and beat throttling
 cyberark/skyark
SkyArk helps to discover, assess and secure the most privileged entities in Azure and AWS
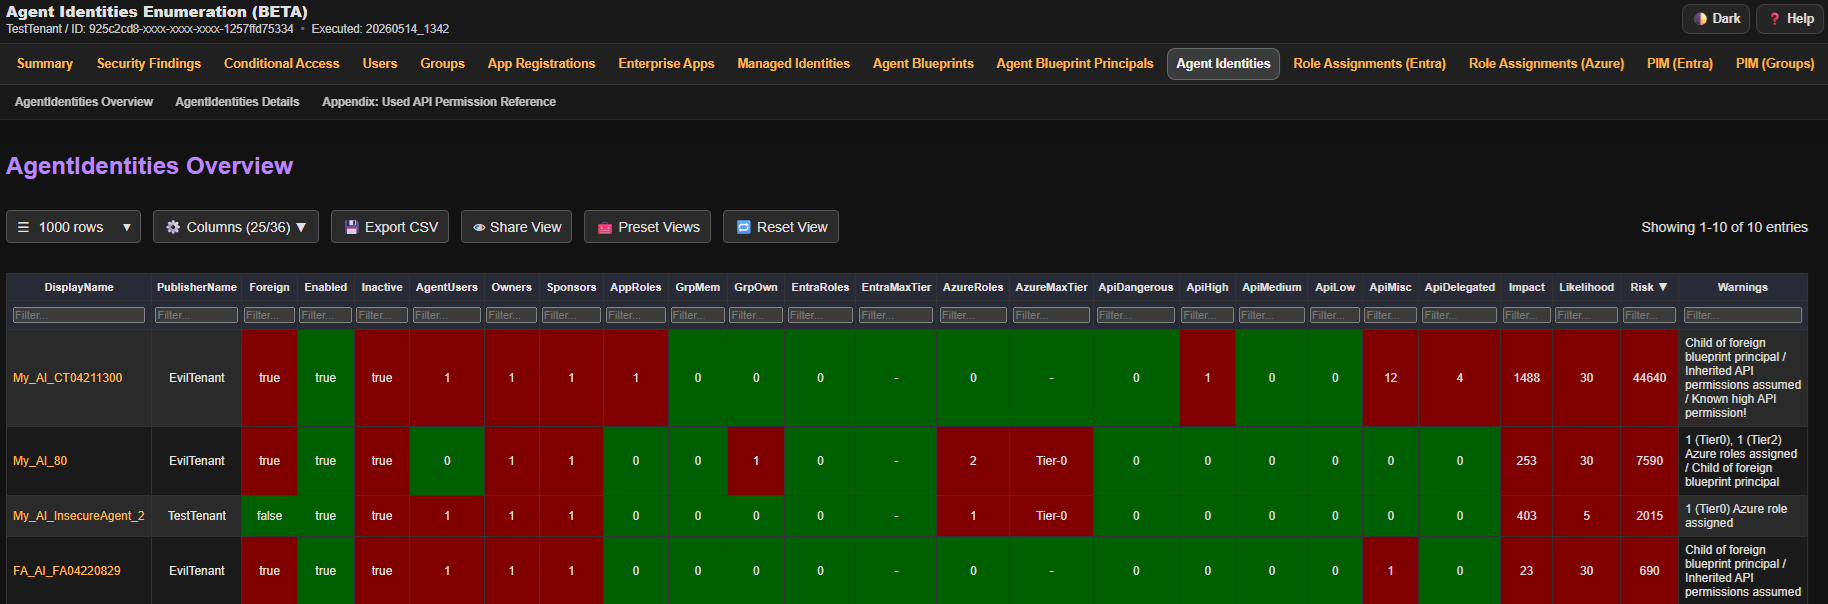 compasssecurity/entrafalcon
A lightweight PowerShell tool for assessing the security posture of Microsoft Entra ID environments. It helps identify privileged objects, risky…
 azuread/azureadassessment
Tooling for assessing an Azure AD tenant state and configuration
 franc-pentest/ldeep
In-depth ldap enumeration utility
 squidsec/bloodbash
Offline AD/Entra attack-path analyzer for SharpHound/AzureHound JSON. Surfaces prioritized privilege escalation, credential, and misconfiguration…
 rams3sh/aaia
AWS Identity and Access Management Visualizer and Anomaly Finder
 vectra-ai-research/maad-af
MAAD Attack Framework - An attack tool for simple, fast & effective security testing of M365 & Entra ID (Azure AD).
 logangoins/cable
.NET post-exploitation toolkit for Active Directory reconnaissance and exploitation
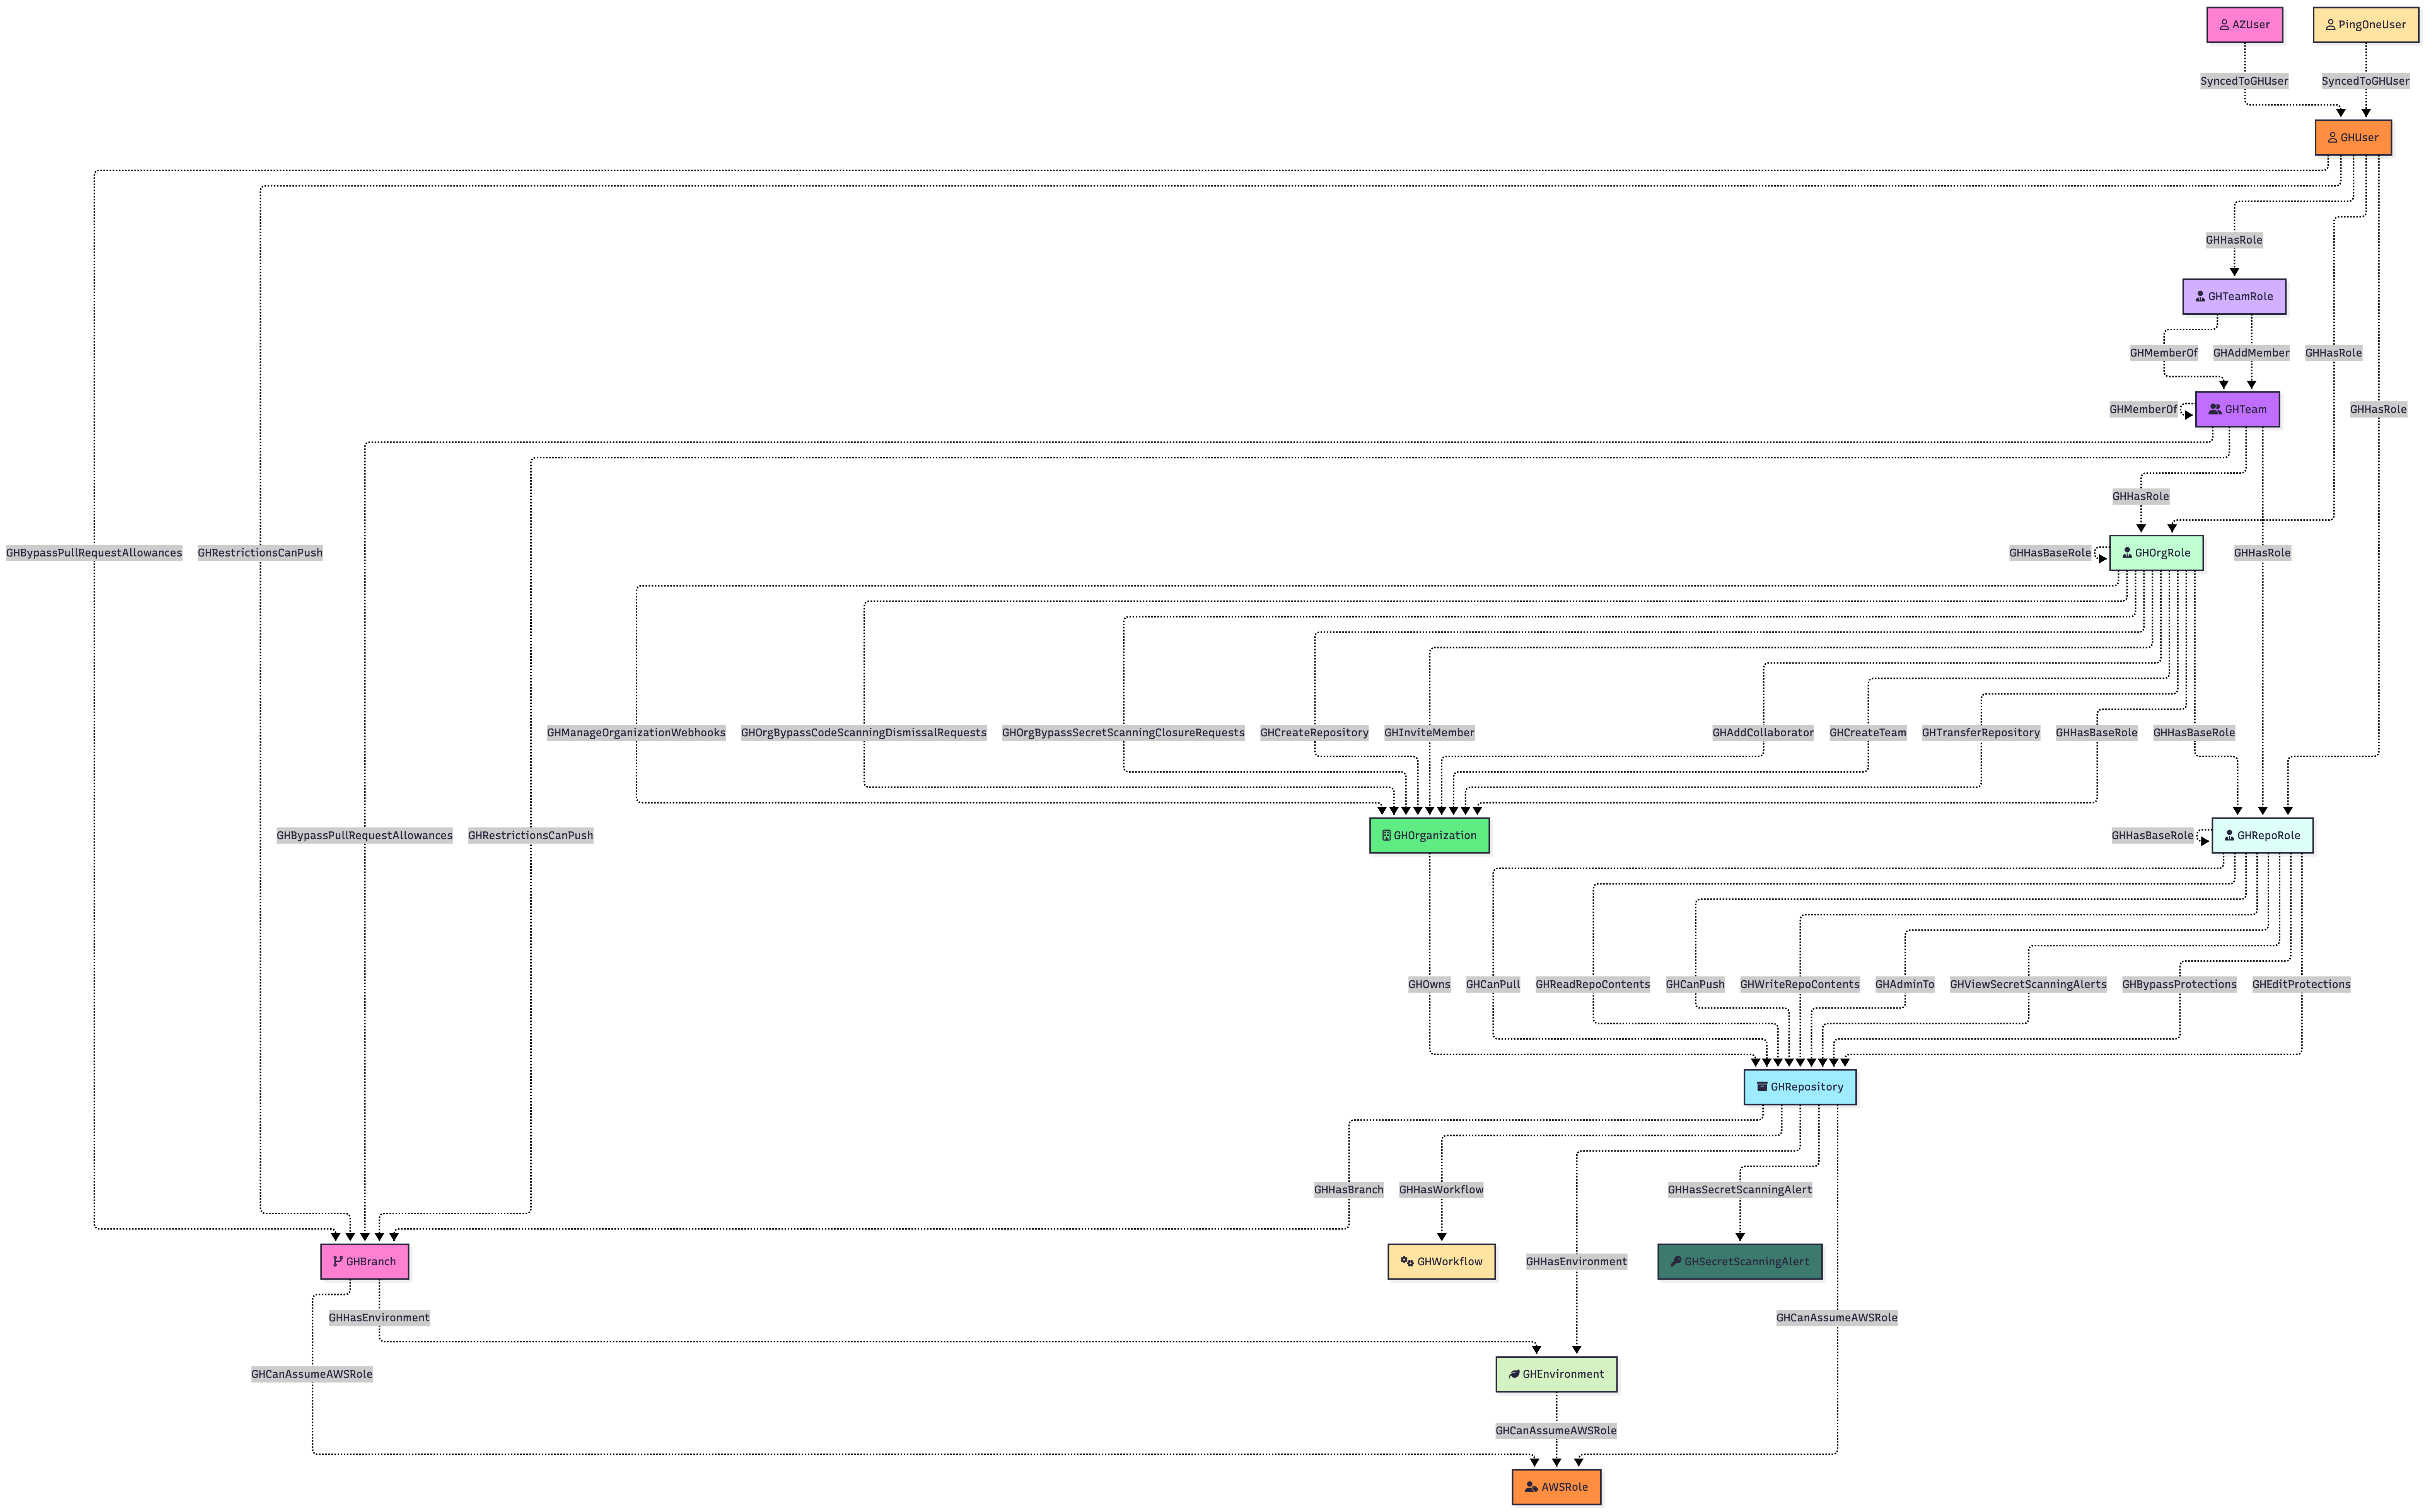 specterops/githound
BloodHound OpenGraph collector for GitHub that maps organization structure, permissions, and cross-cloud attack paths into a navigable graph for…
 logisek/evilmist
EvilMist is a collection of scripts and utilities designed to support cloud penetration testing & red teaming. The toolkit helps identify…
 redbyte1337/credspy
Entra ID user enumeration and auth method discovery via the public GetCredentialType API