
SkyArk
 cyberark/skyark
SkyArk helps to discover, assess and secure the most privileged entities in Azure and AWS
cloud-securityidentity-access-managementinformation-gathering+3
9141 year ago
cyberark/skyarkSkyArk helps to discover, assess and secure the most privileged entities in Azure and AWS
 gerenios/aadinternals
PowerShell module for administering and auditing Azure AD and Office 365, enabling token manipulation, user enumeration, and security assessments of…
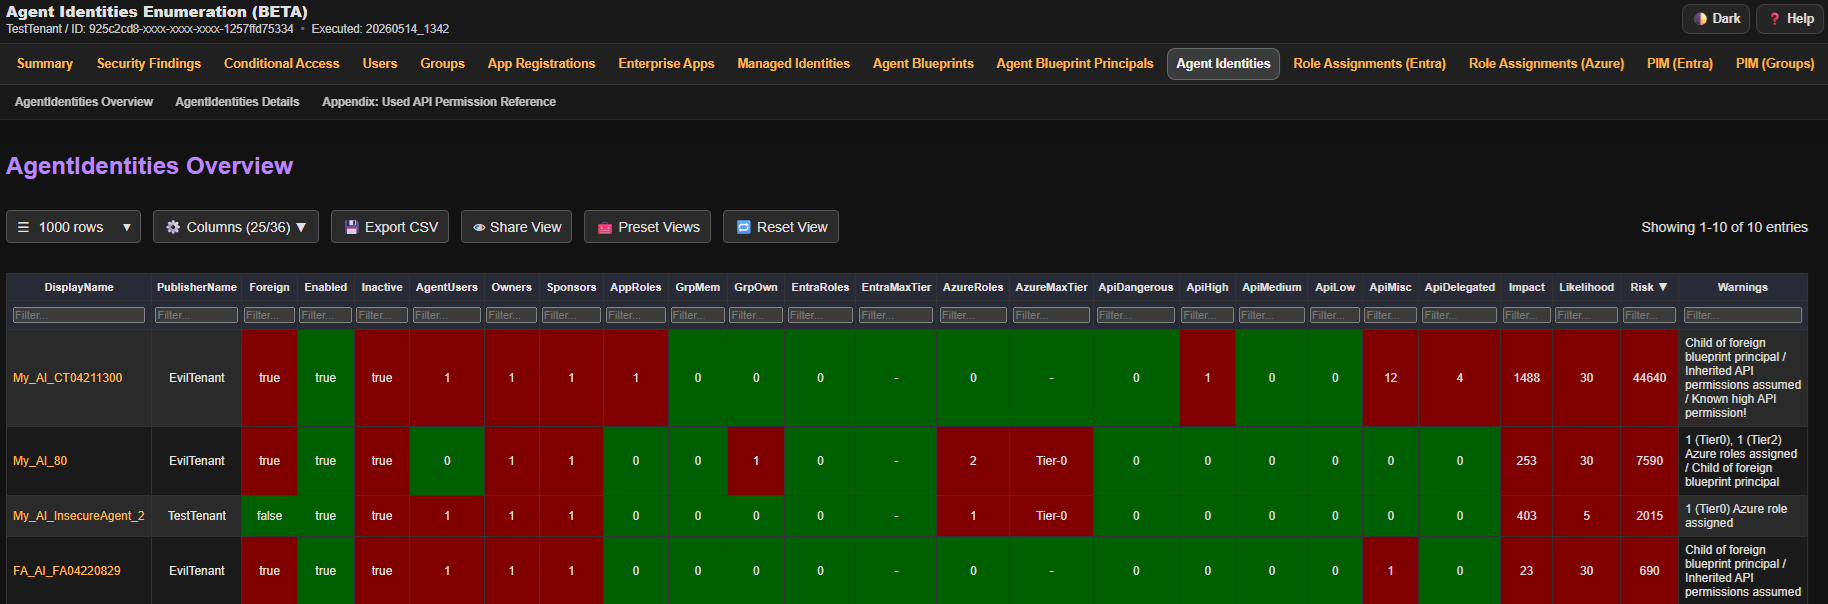 compasssecurity/entrafalcon
A lightweight PowerShell tool for assessing the security posture of Microsoft Entra ID environments. It helps identify privileged objects, risky…
 logisek/evilmist
EvilMist is a collection of scripts and utilities designed to support cloud penetration testing & red teaming. The toolkit helps identify…
 sap8899/reportly
AzureAD/EntraID user activity reporter for blue teams. Input a suspicious user and time frame to receive a detailed report of user info, actions, and…
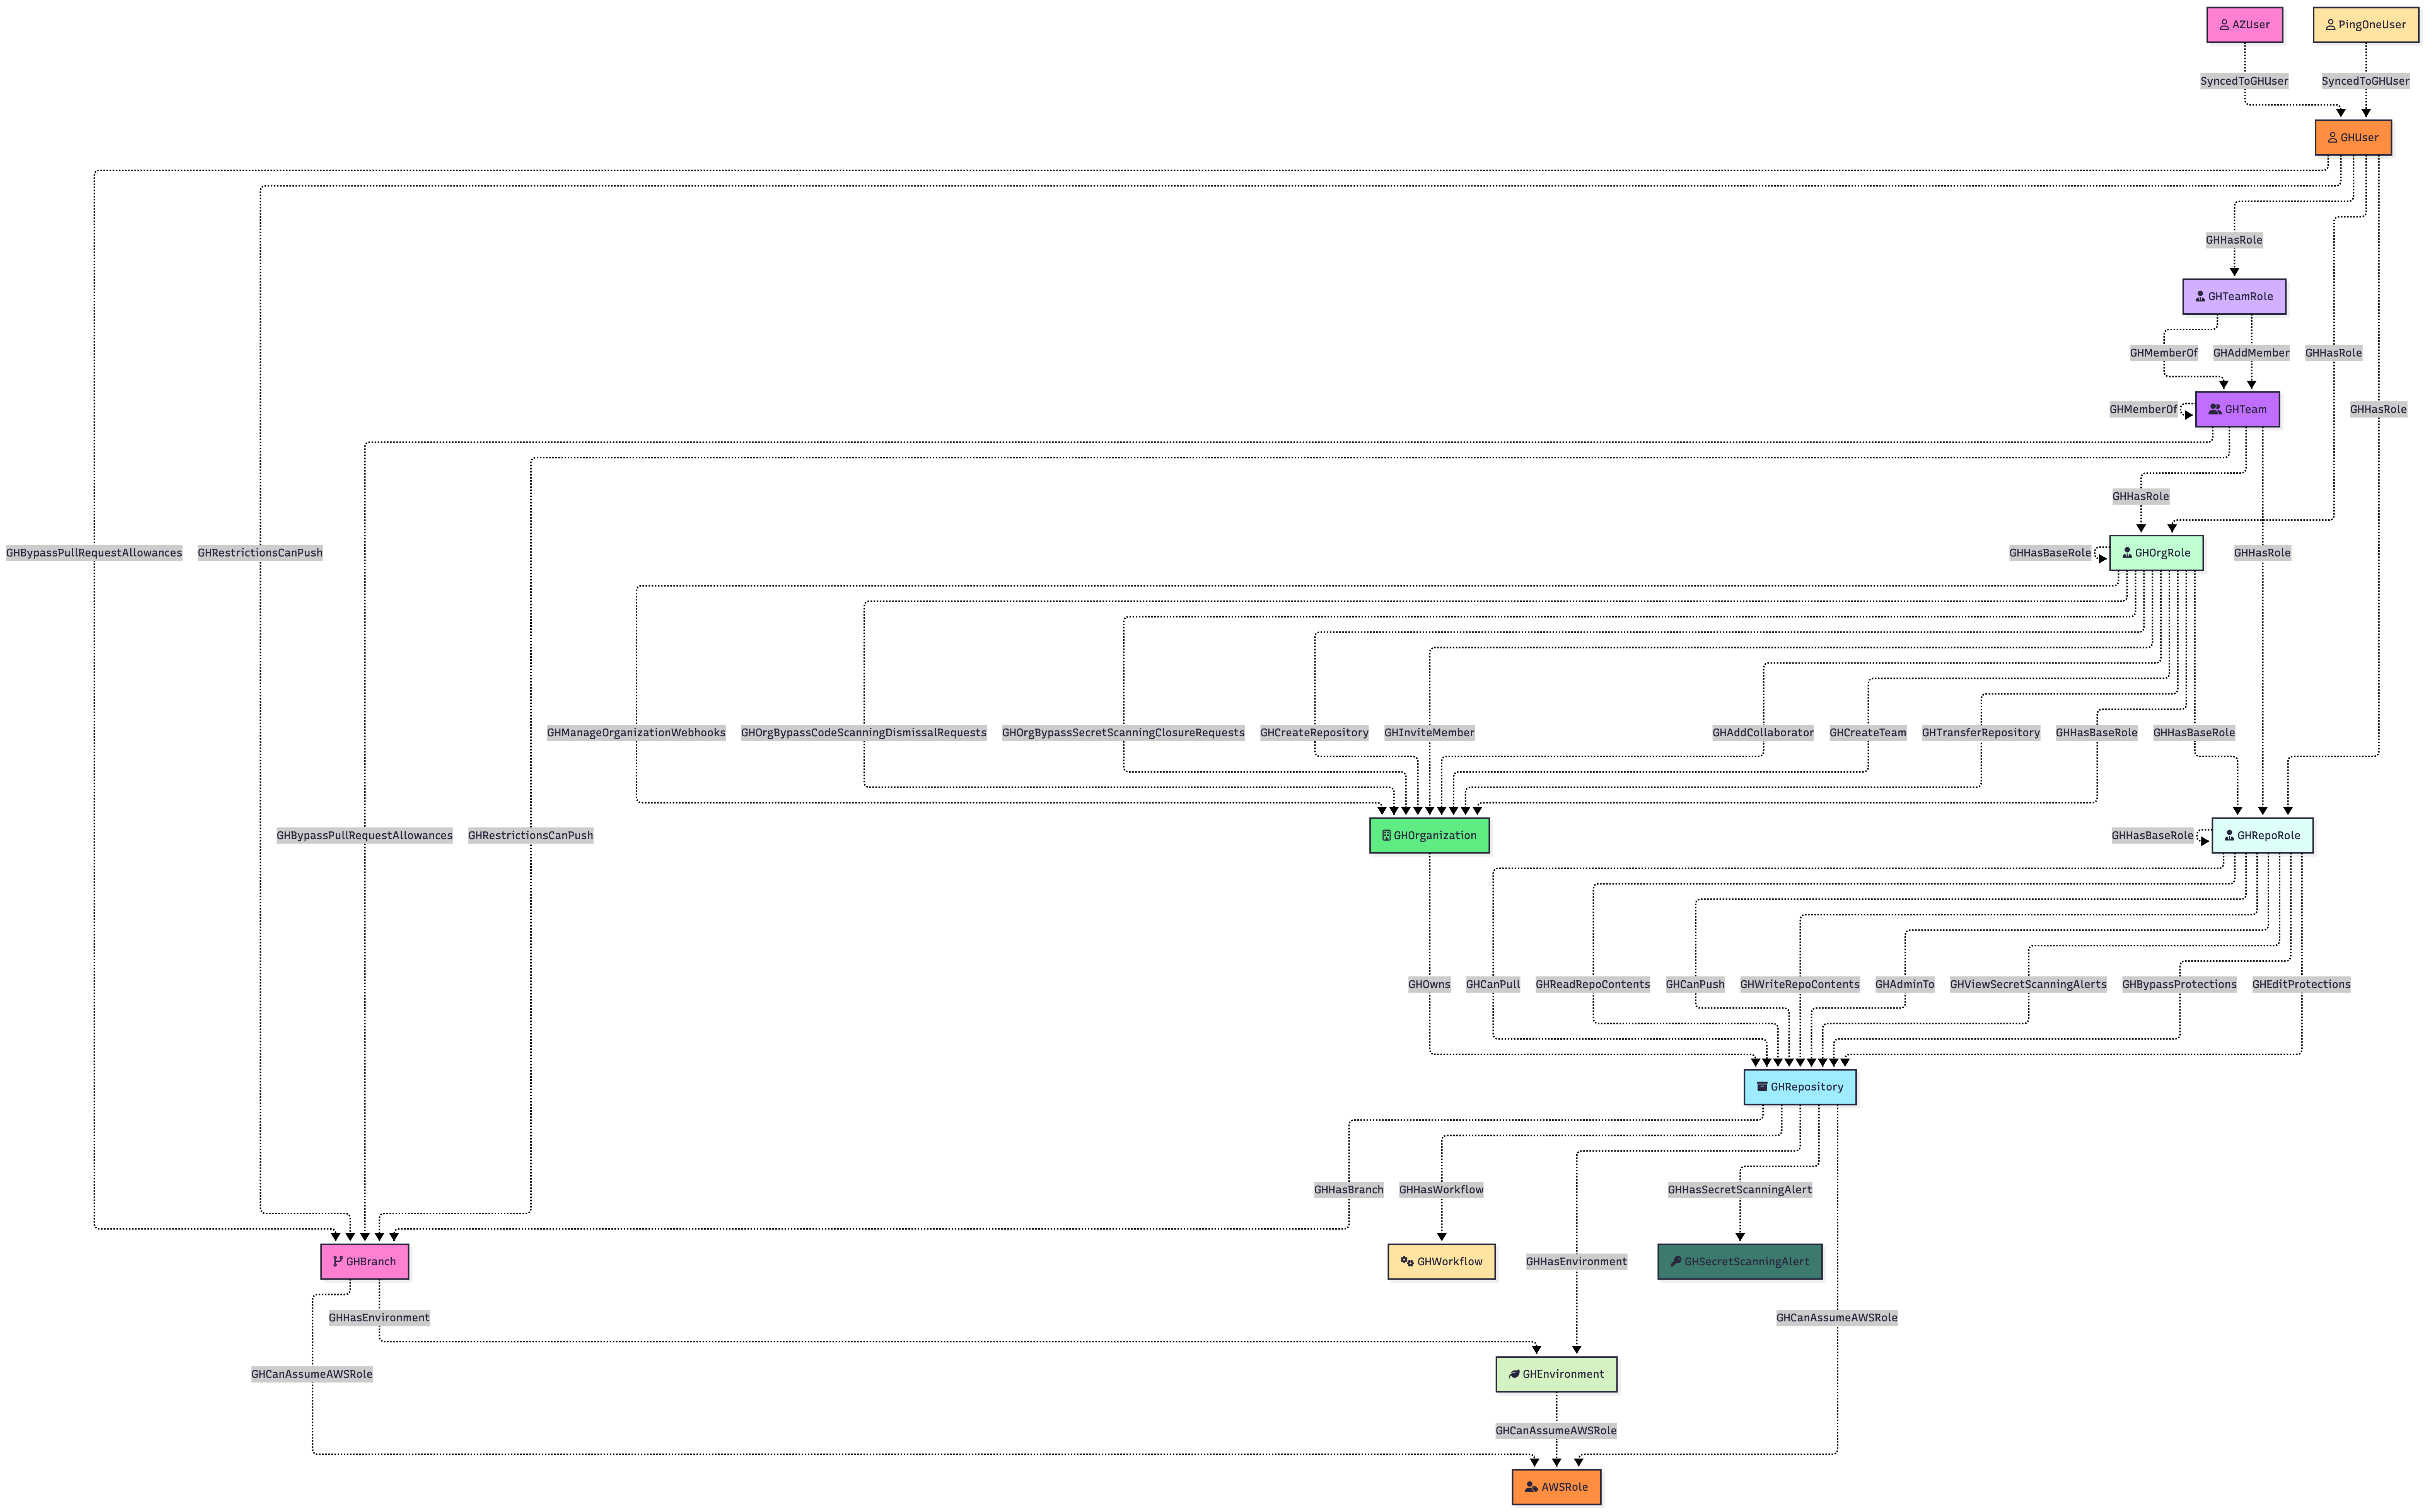 specterops/githound
BloodHound OpenGraph collector for GitHub that maps organization structure, permissions, and cross-cloud attack paths into a navigable graph for…
 redbyte1337/credspy
Entra ID user enumeration and auth method discovery via the public GetCredentialType API
 bishopfox/cirro
Creating attacks paths across management and data planes
 daddycocoaman/azbelt
AAD related enumeration in Nim
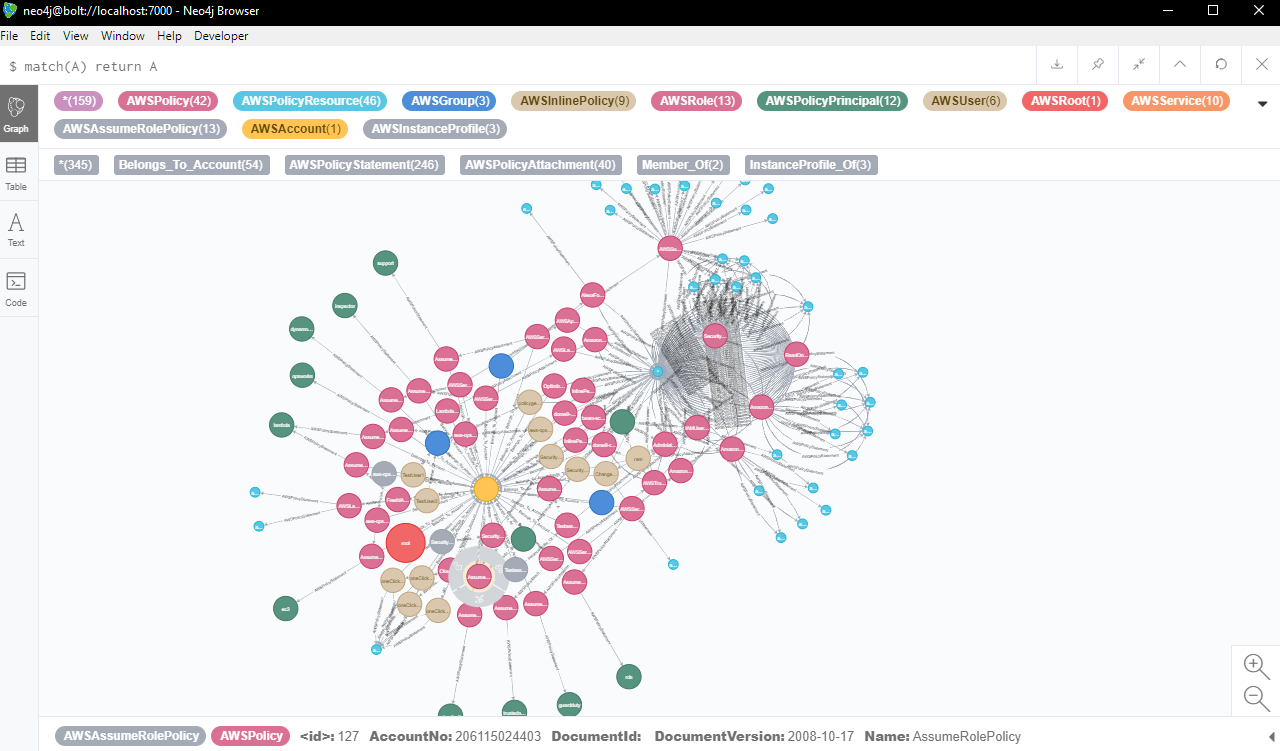 rams3sh/aaia
AWS Identity and Access Management Visualizer and Anomaly Finder
 andresriancho/enumerate-iam
Enumerate the permissions associated with AWS credential set
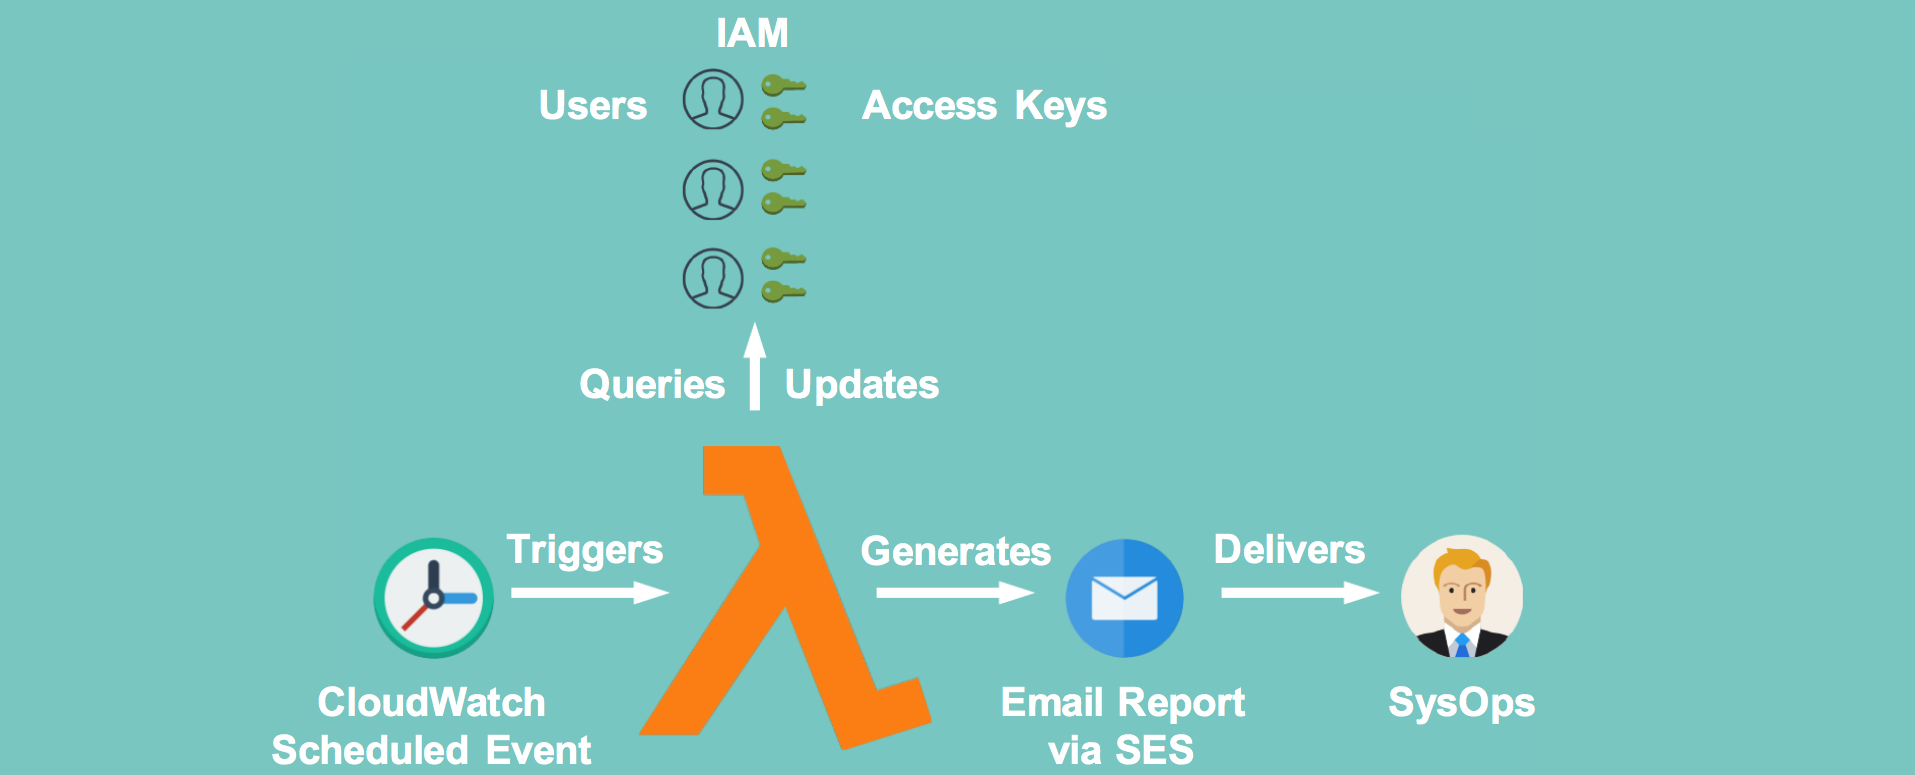 te-papa/aws-key-disabler
A small lambda script that will disable access keys older than a given amount of days.
 cyberark/skywrapper
SkyWrapper helps to discover suspicious creation forms and uses of temporary tokens in AWS
 netflix/repokid
AWS Least Privilege for Distributed, High-Velocity Deployment
 salesforce/cloudsplaining
Cloudsplaining is an AWS IAM Security Assessment tool that identifies violations of least privilege and generates a risk-prioritized report.
 eshlomo1/cloudsec
Master the art of cloud exploitation. A specialized resource for offensive security researchers and red teamers focused on weaponizing…
 rhinosecuritylabs/iamactionhunter
An AWS IAM policy statement parser and query tool.
 juanfont/headscale
An open source, self-hosted implementation of the Tailscale control server