
cloudflared
 cloudflare/cloudflared
Client for Cloudflare Tunnel enabling secure outbound-only connections to origins via Zero Trust architecture. Supports HTTP, WebSocket, SSH, and RDP…
api-securitycloud-infrastructure-securitycloud-security+3
15.2k
cloudflare/cloudflaredClient for Cloudflare Tunnel enabling secure outbound-only connections to origins via Zero Trust architecture. Supports HTTP, WebSocket, SSH, and RDP…
 g4bri-3l3/idwolf
Read-only Active Directory & Microsoft Entra ID hygiene auditor in pure PowerShell. Collect once, analyze offline: deterministic findings, attack…
 bastillion-io/bastillion
Bastillion gives you a clean, browser-based way to manage SSH access across all your systems—like a bastion host with a friendly dashboard.
 eshlomo1/cloudsec
Master the art of cloud exploitation. A specialized resource for offensive security researchers and red teamers focused on weaponizing…

 ritwick7/sudostamp
Approve sudo on a Linux workstation with a fingerprint on your Android phone. LAN only; the ECDSA key never leaves the phone's TEE and speaks the…
 ylianst/meshcentral
A complete web-based remote monitoring and management web site. Once setup you can install agents and perform remote desktop session to devices on…
 sap/macos-enterprise-privileges
This application gives Mac users in enterprise environments control over the administration of their machines by elevating their access level to…
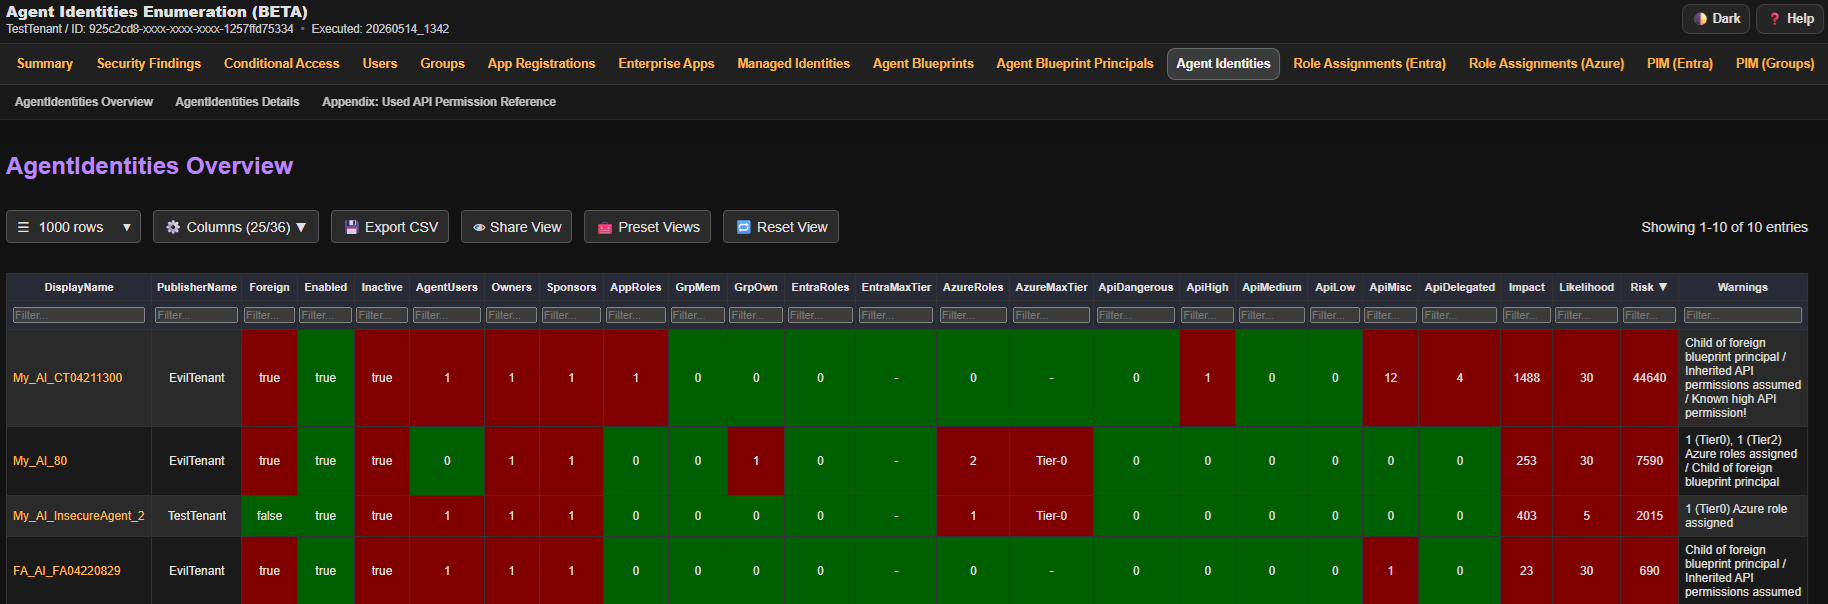 compasssecurity/entrafalcon
A lightweight PowerShell tool for assessing the security posture of Microsoft Entra ID environments. It helps identify privileged objects, risky…
 anthonyk2923/cve-2026-94609
Write-up and proof-of-concept for CVE-2026-94609, an authentik privilege-escalation flaw letting users with add_user_to_group join superuser groups…
 ustayready/thunderstorm
A collector and derivation engine. It maps your environment, evaluates effective permissions and trust, and writes a complete attack graph as a…
 ivanesk315/cve-2026-18963
Docker-based lab and Python exploit for CVE-2026-18963, a Keycloak reset-credentials flow bypass enabling account takeover via email verification…
 ricardojoserf/adduser-samr
Create local administrators in Windows using the SAMR API. In C#, Crystal, Python, Rust, Golang, Nim and Deno (Javascript)
 mvelazc0/badzure
BadZure automates the deployment of intentionally misconfigured Entra ID tenants and Azure subscriptions, populating them with diverse entities and…
 karitamw/printnightmare-detection-mitigation-lab
Sanitised Windows security lab demonstrating Active Directory administration, host and network detection, and layered mitigation of CVE-2021-34527.
 semperis/entragoat
A deliberately vulnerable Microsoft Entra ID environment. Learn identity security through hands-on, realistic attack challenges.
 stra-x/outoftune
Rogue device enrollment tool for Entra ID and Intune MDM. Automates device join, token acquisition, MDM enrollment, and OMA-DM checkin to extract…
 logisek/evilmist
EvilMist is a collection of scripts and utilities designed to support cloud penetration testing & red teaming. The toolkit helps identify…
 logisek/huntcyberark
CyberArk Security Audit