
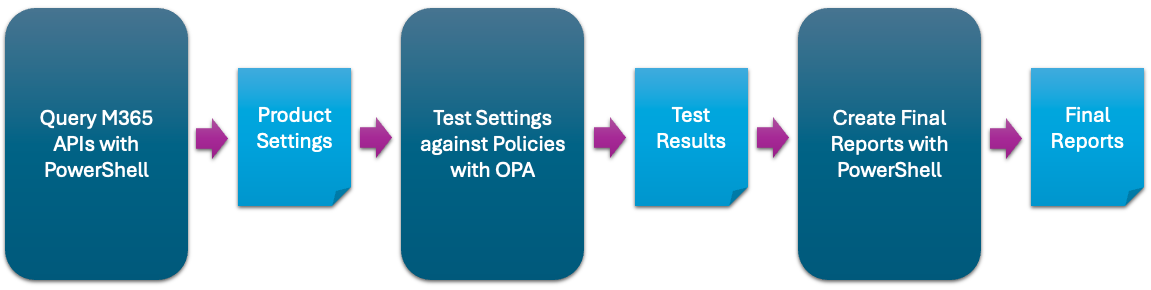
ScubaGear
 cisagov/scubagear
Automation to assess the state of your M365 tenant against CISA's baselines
cloud-securityconfiguration-auditingdefensive-tools+3
2.7k1 day ago
cisagov/scubagearAutomation to assess the state of your M365 tenant against CISA's baselines
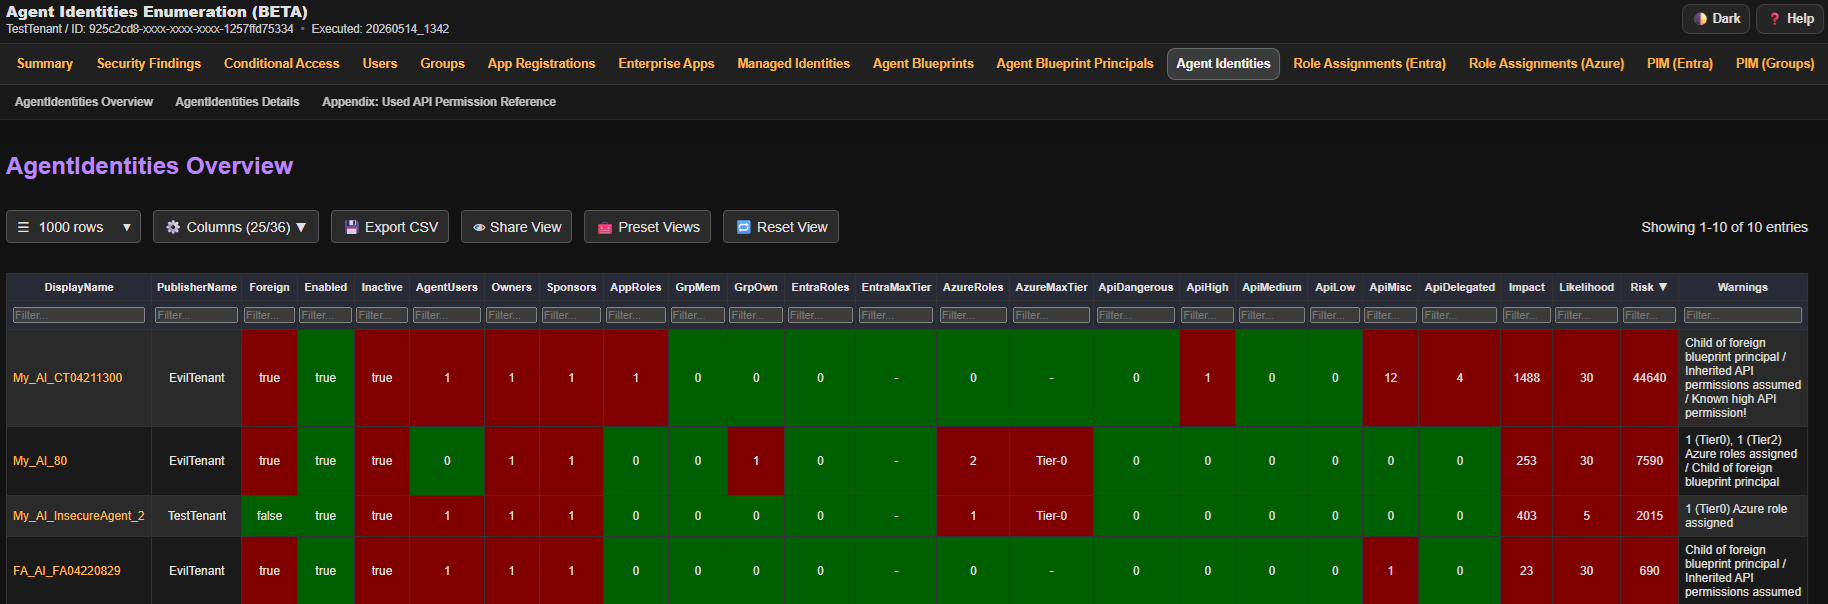 compasssecurity/entrafalcon
A lightweight PowerShell tool for assessing the security posture of Microsoft Entra ID environments. It helps identify privileged objects, risky…
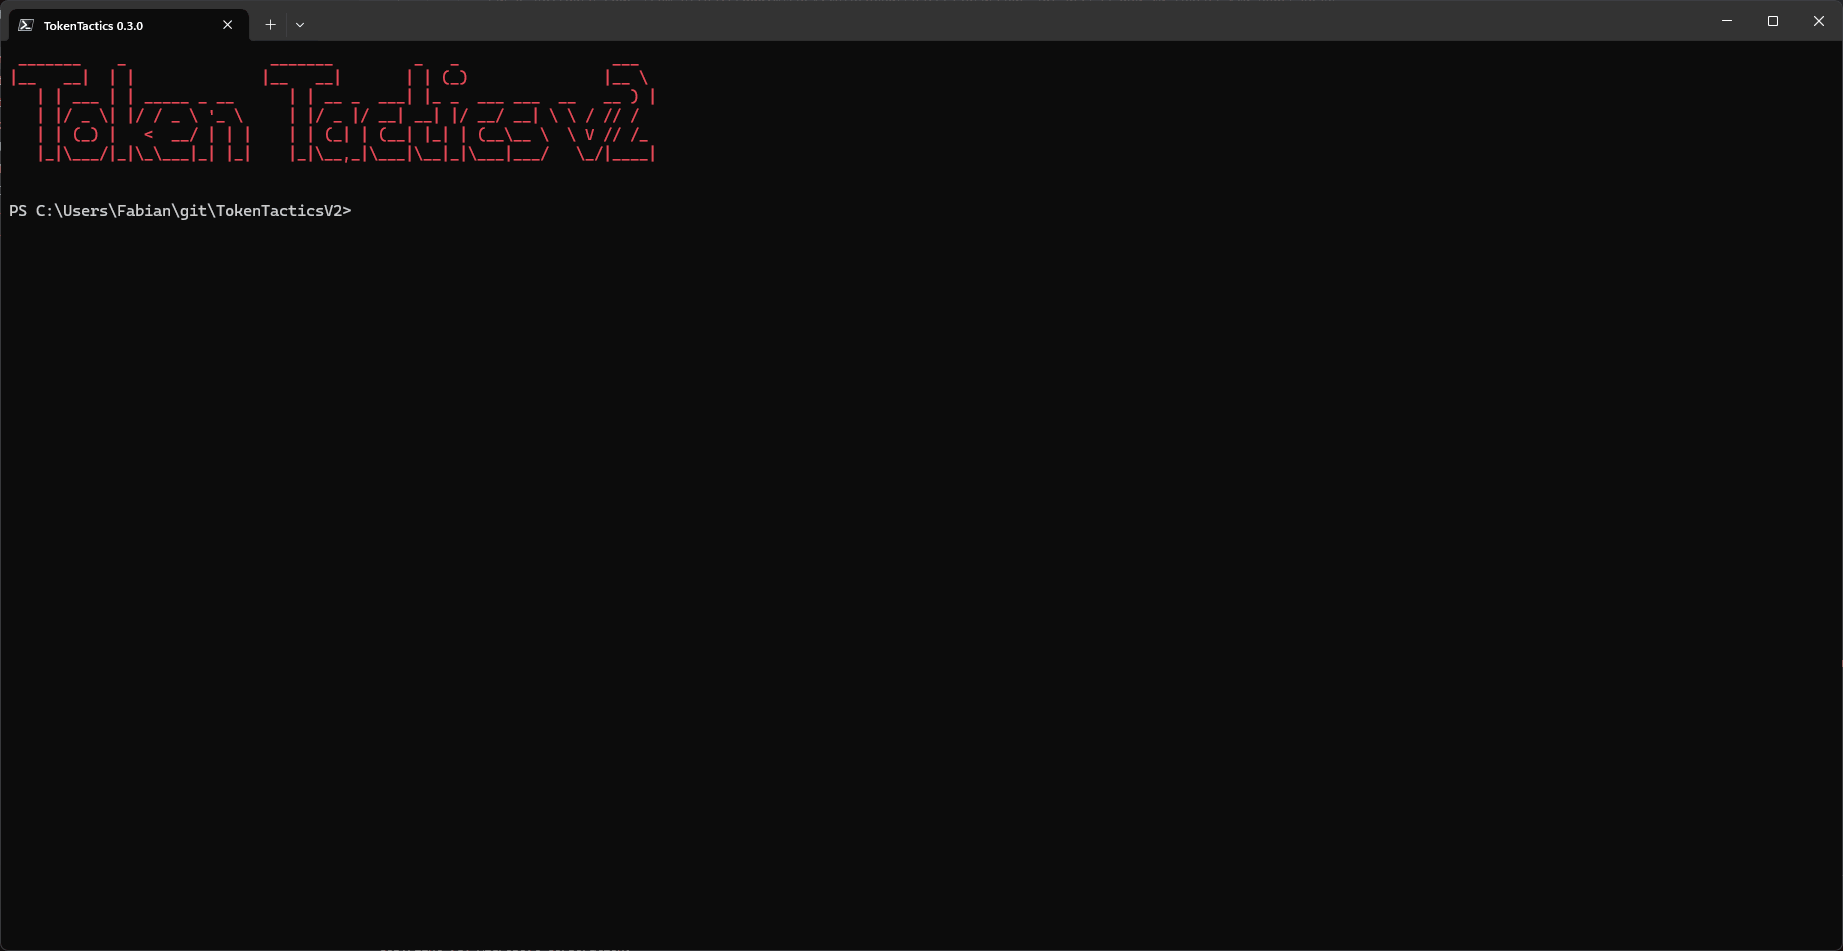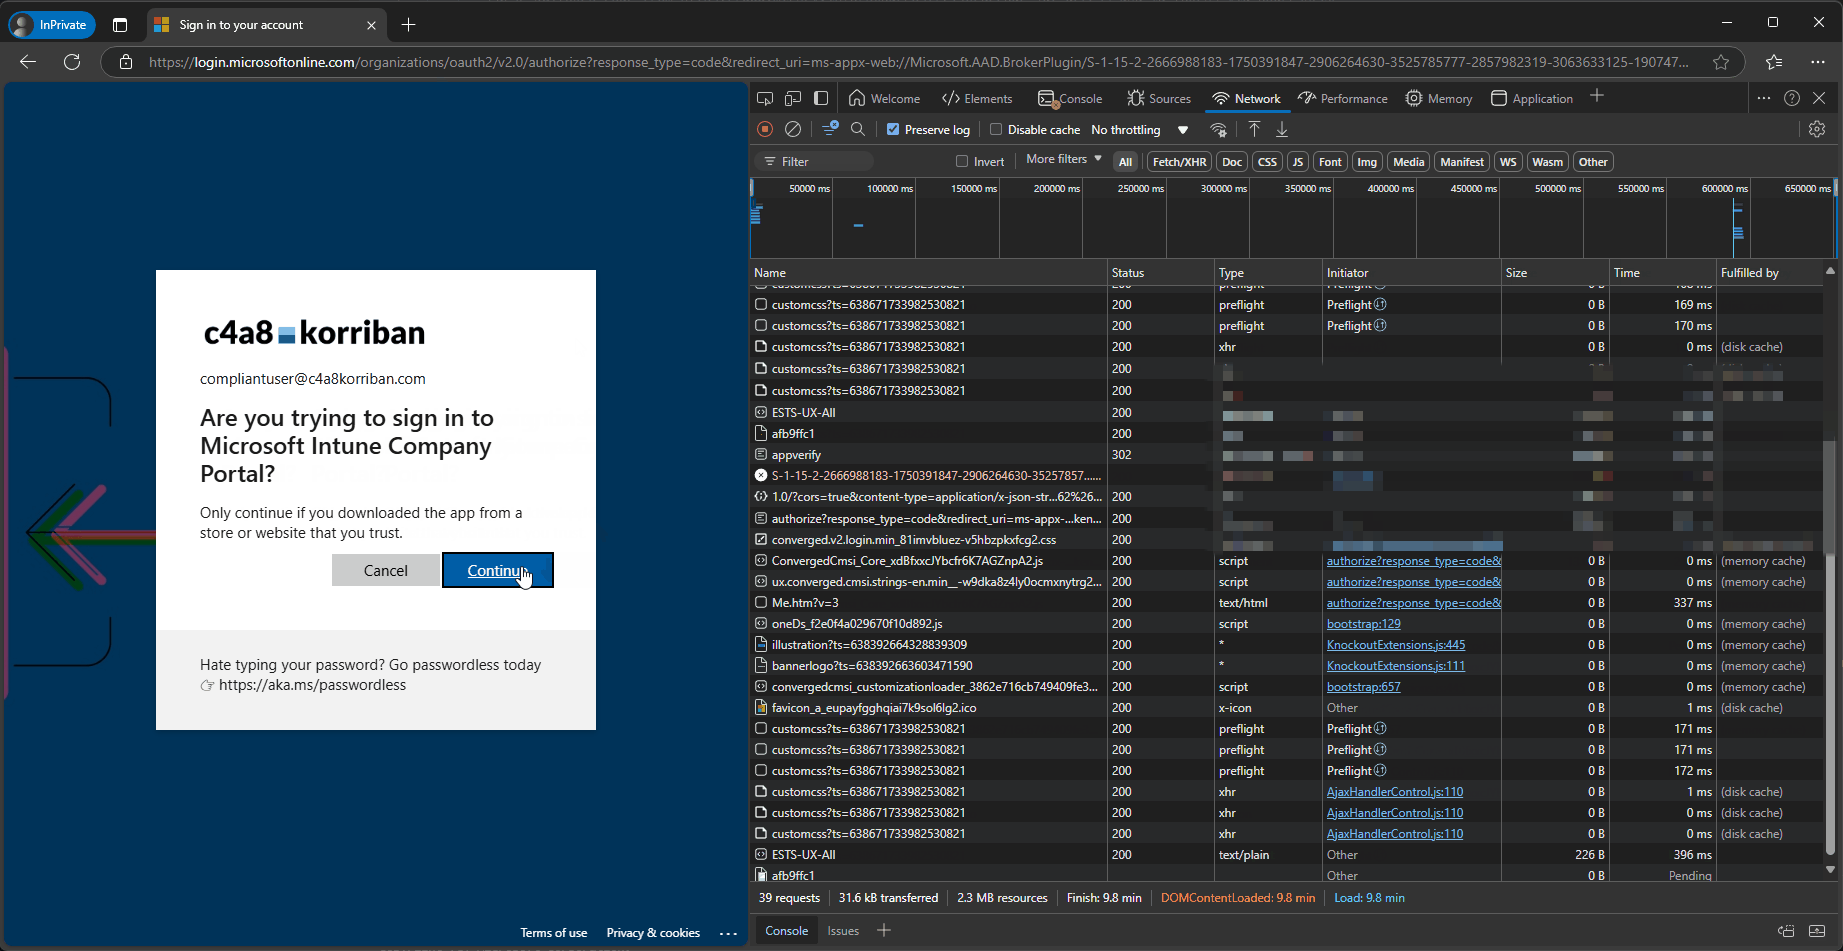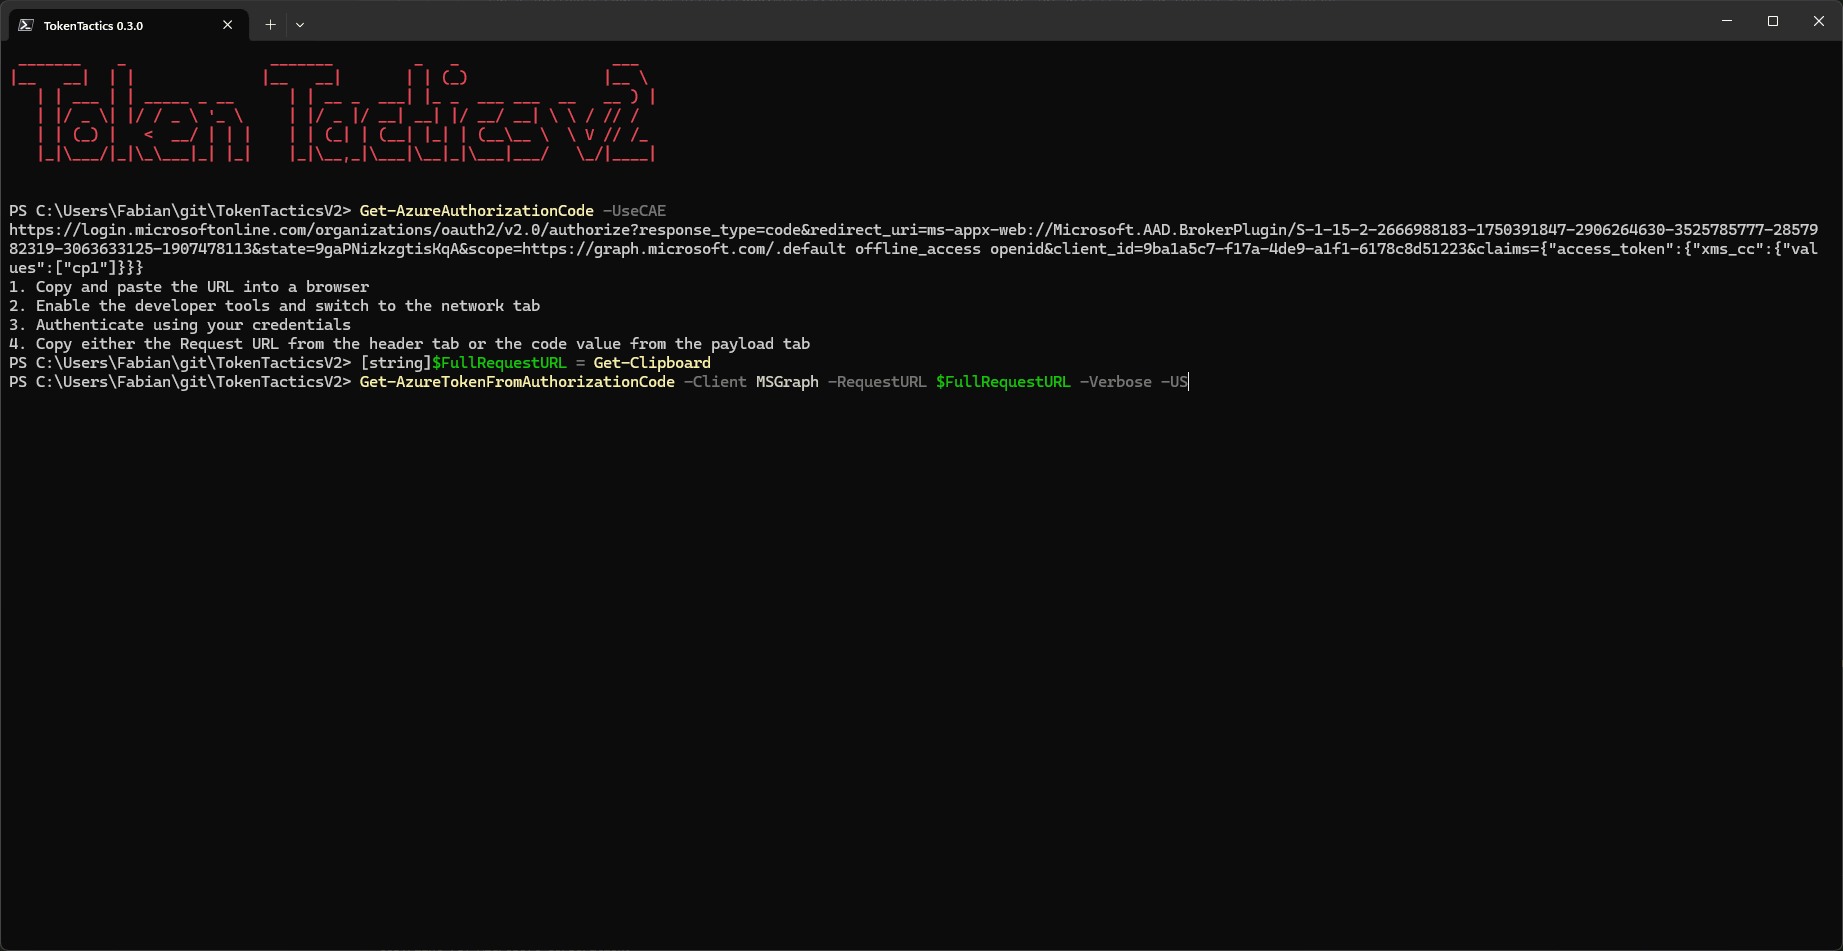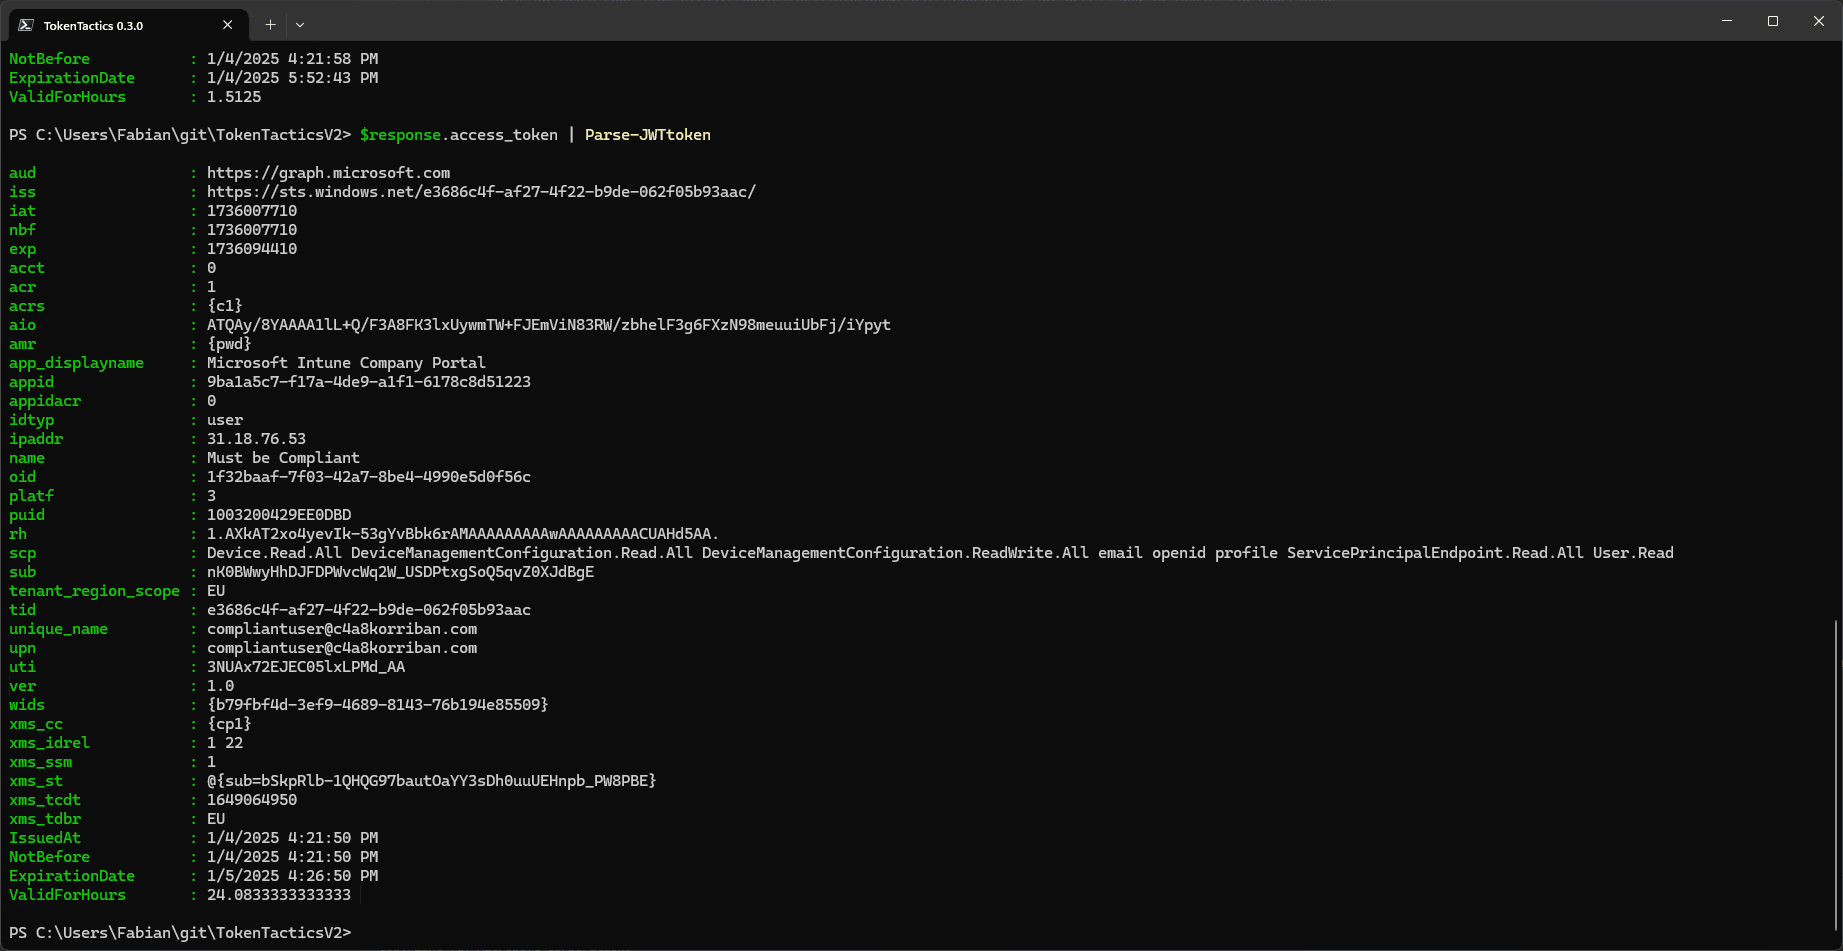 f-bader/tokentacticsv2
A fork of the great TokenTactics with support for CAE and token endpoint v2
 lithnet/ad-password-protection
Active Directory password filter featuring breached password checking and custom complexity rules
 offsecpierogi/azure
Bash and PowerShell scripts for Azure security assessments, covering IAM privilege escalation, container registry exploitation, Key Vault exposure,…
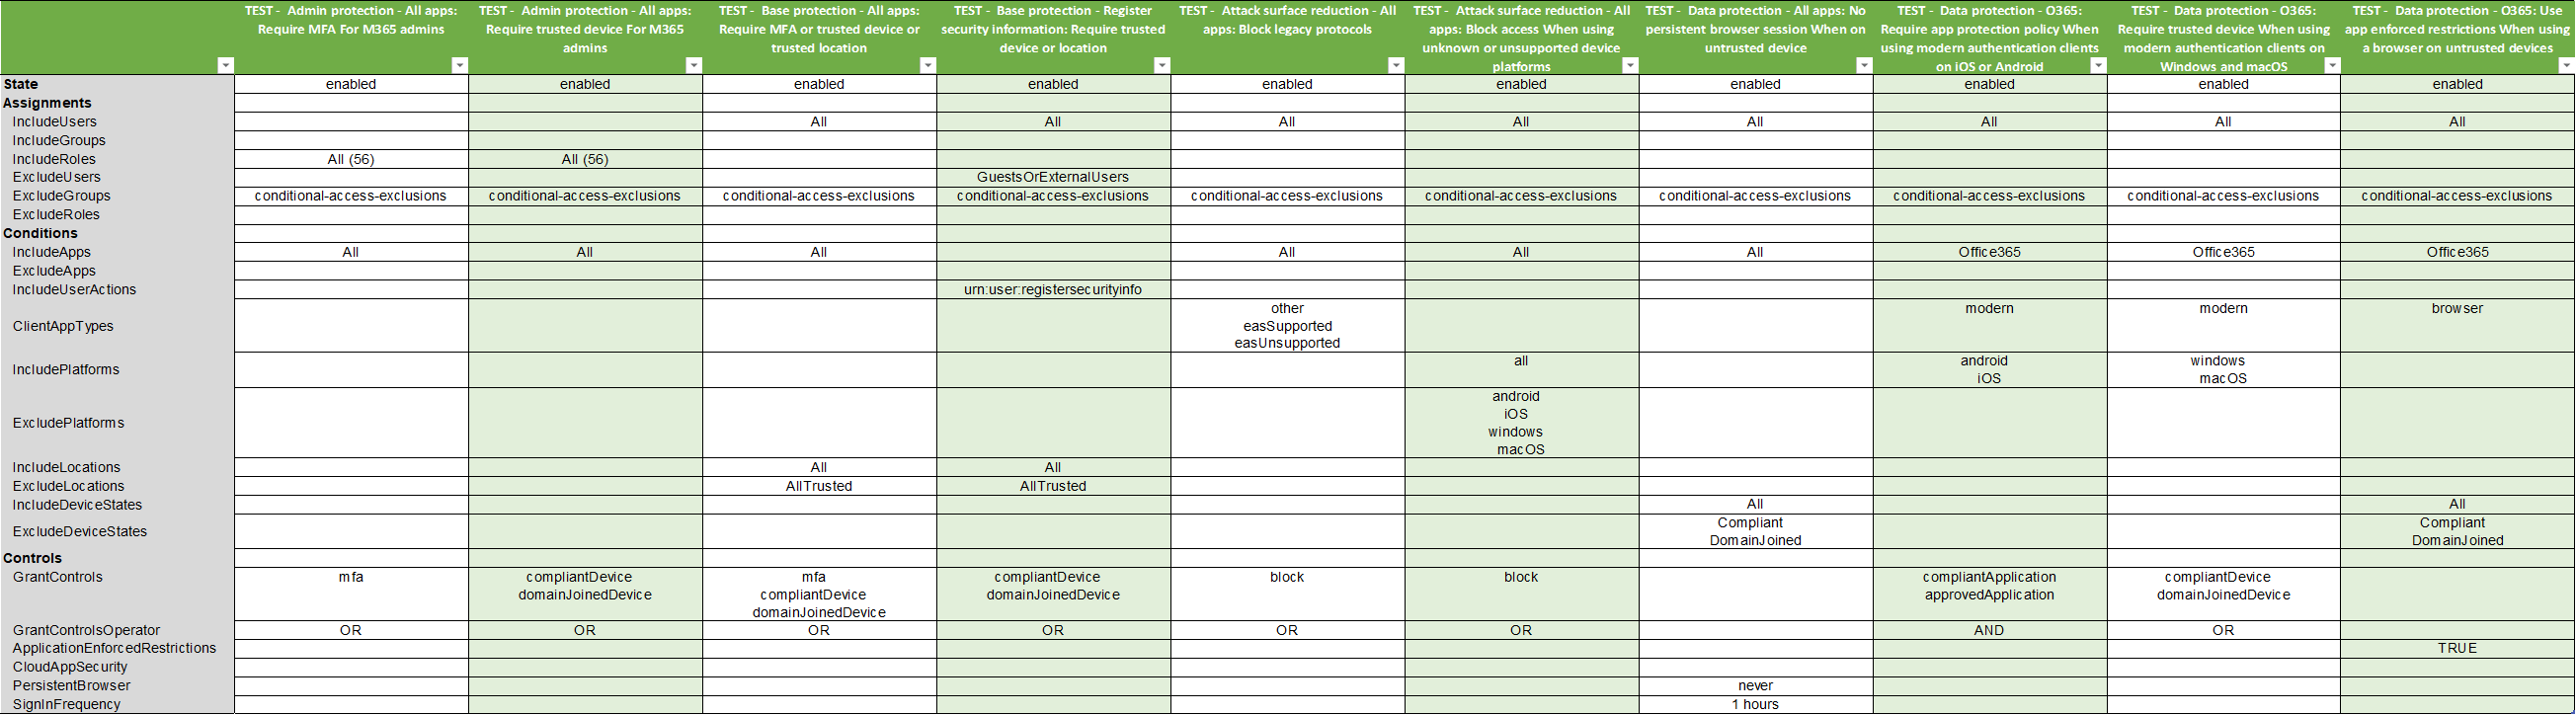 nicolonsky/conditionalaccessdocumentation
Microsoft Entra Conditional Access Documentation with PowerShell
 v-jfanca/cve-2026-20833-rc4-kerberos
Kerberos RC4 deprecation: detection, remediation and guidance (CVE-2026-20833)
 logisek/huntcyberark
CyberArk Security Audit
 vectra-ai-research/maad-af
MAAD Attack Framework - An attack tool for simple, fast & effective security testing of M365 & Entra ID (Azure AD).
 gerenios/aadinternals
PowerShell module for administering and auditing Azure AD and Office 365, enabling token manipulation, user enumeration, and security assessments of…
 cyberark/skyark
SkyArk helps to discover, assess and secure the most privileged entities in Azure and AWS
 azuread/azureadassessment
Tooling for assessing an Azure AD tenant state and configuration
 azuread/azure-ad-incident-response-powershell-module
The Azure Active Directory Incident Response PowerShell module provides a number of tools, developed by the Azure Active Directory Product Group in…
 mandiant/mandiant-azure-ad-investigator
Read-only PowerShell module for detecting UNC2452 and other threat actor artifacts in Azure AD, auditing federated domains, service principals,…
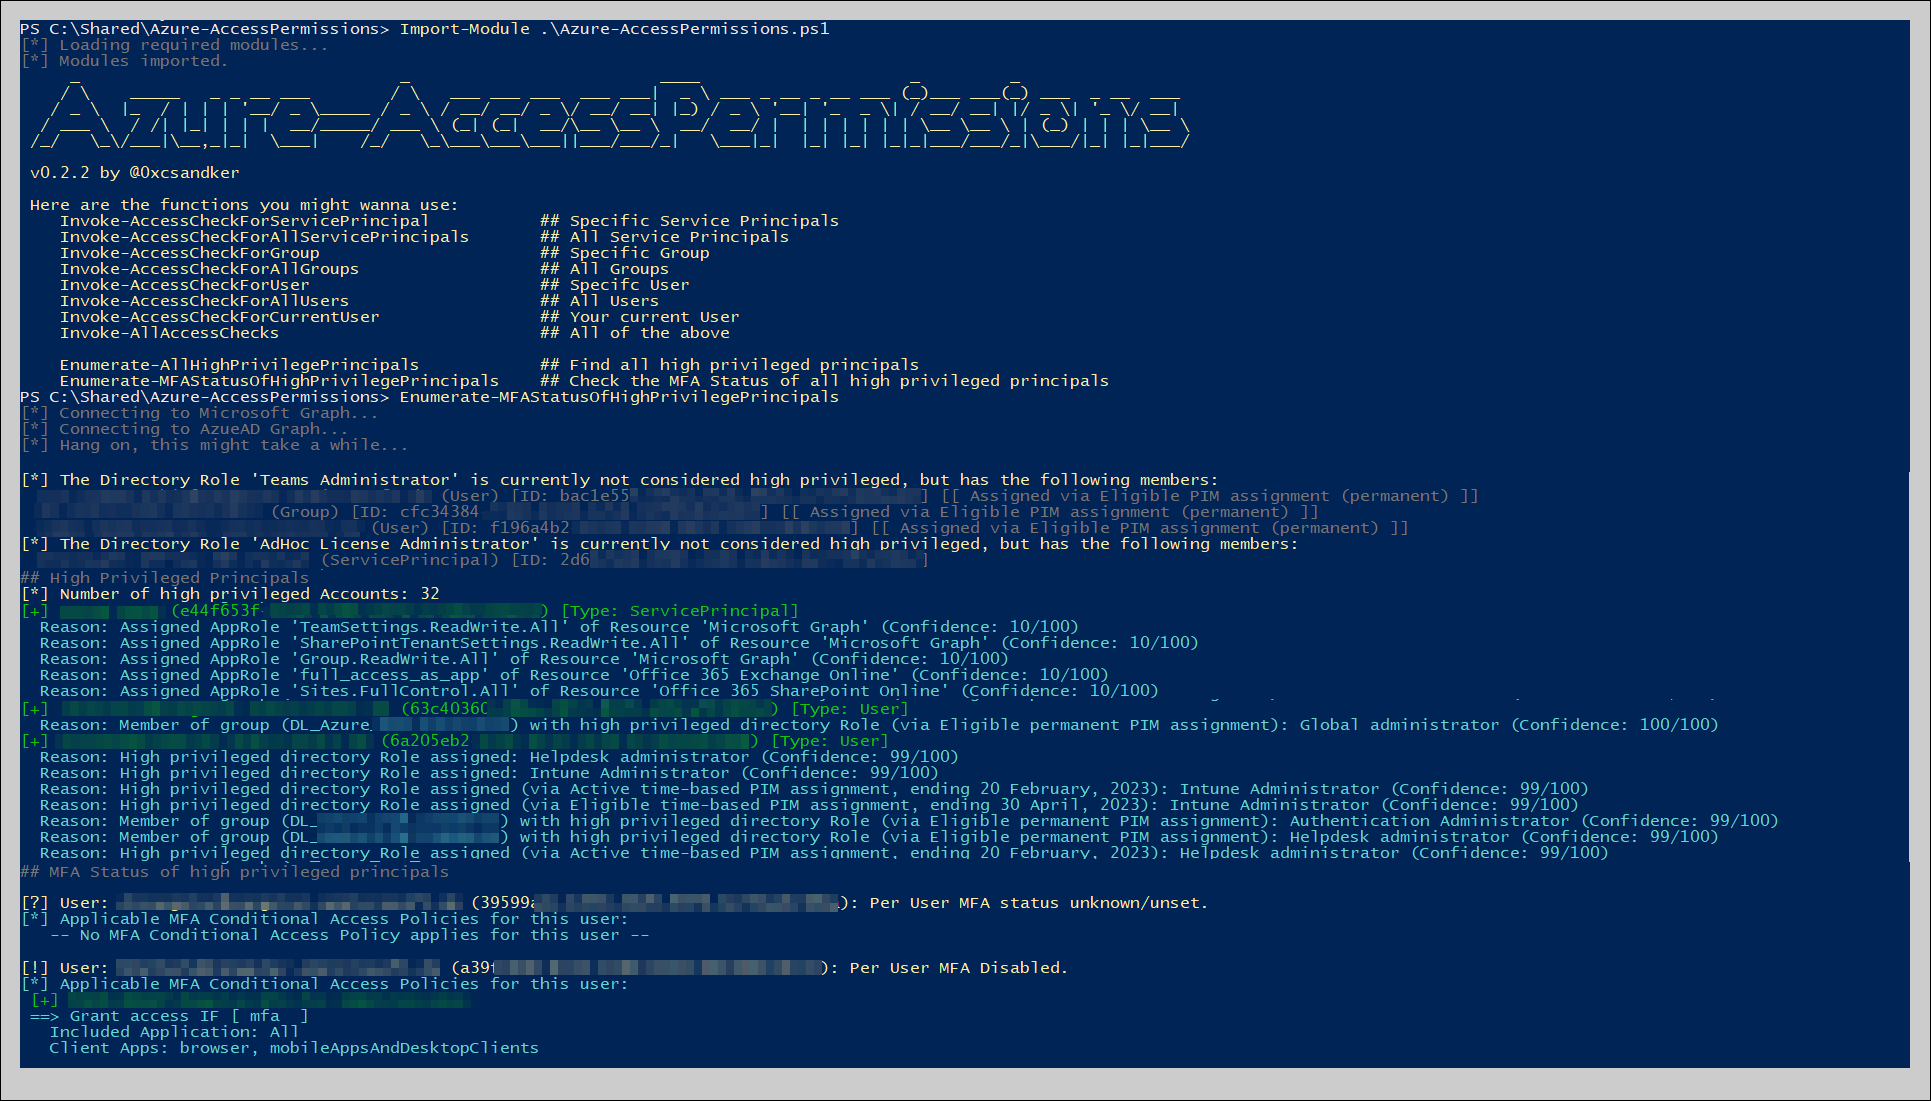 csandker/azure-accesspermissions
PowerShell script to enumerate Azure Active Directory access permissions, including role assignments, service principals, and privileged access…
 rhymeswithmogul/set-zerologonmitigation
Protect your domain controllers against Zerologon (CVE-2020-1472).
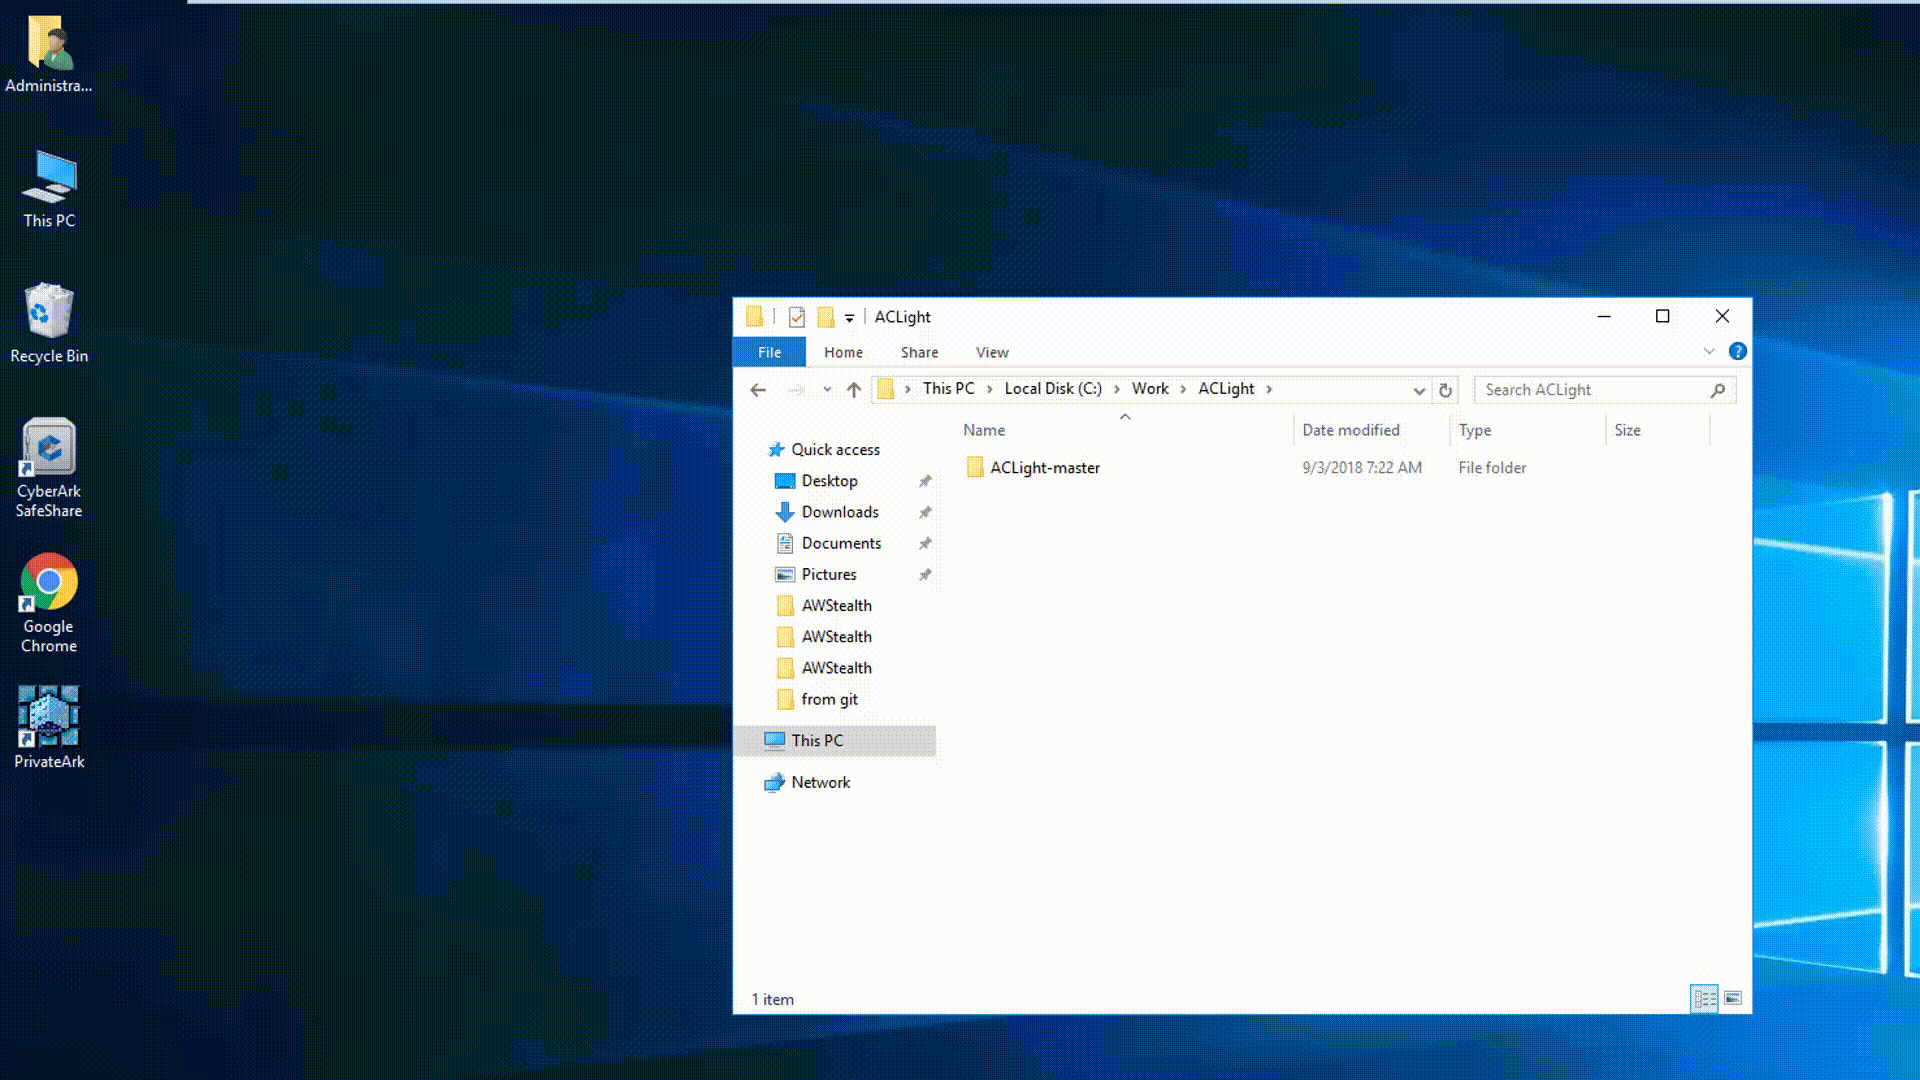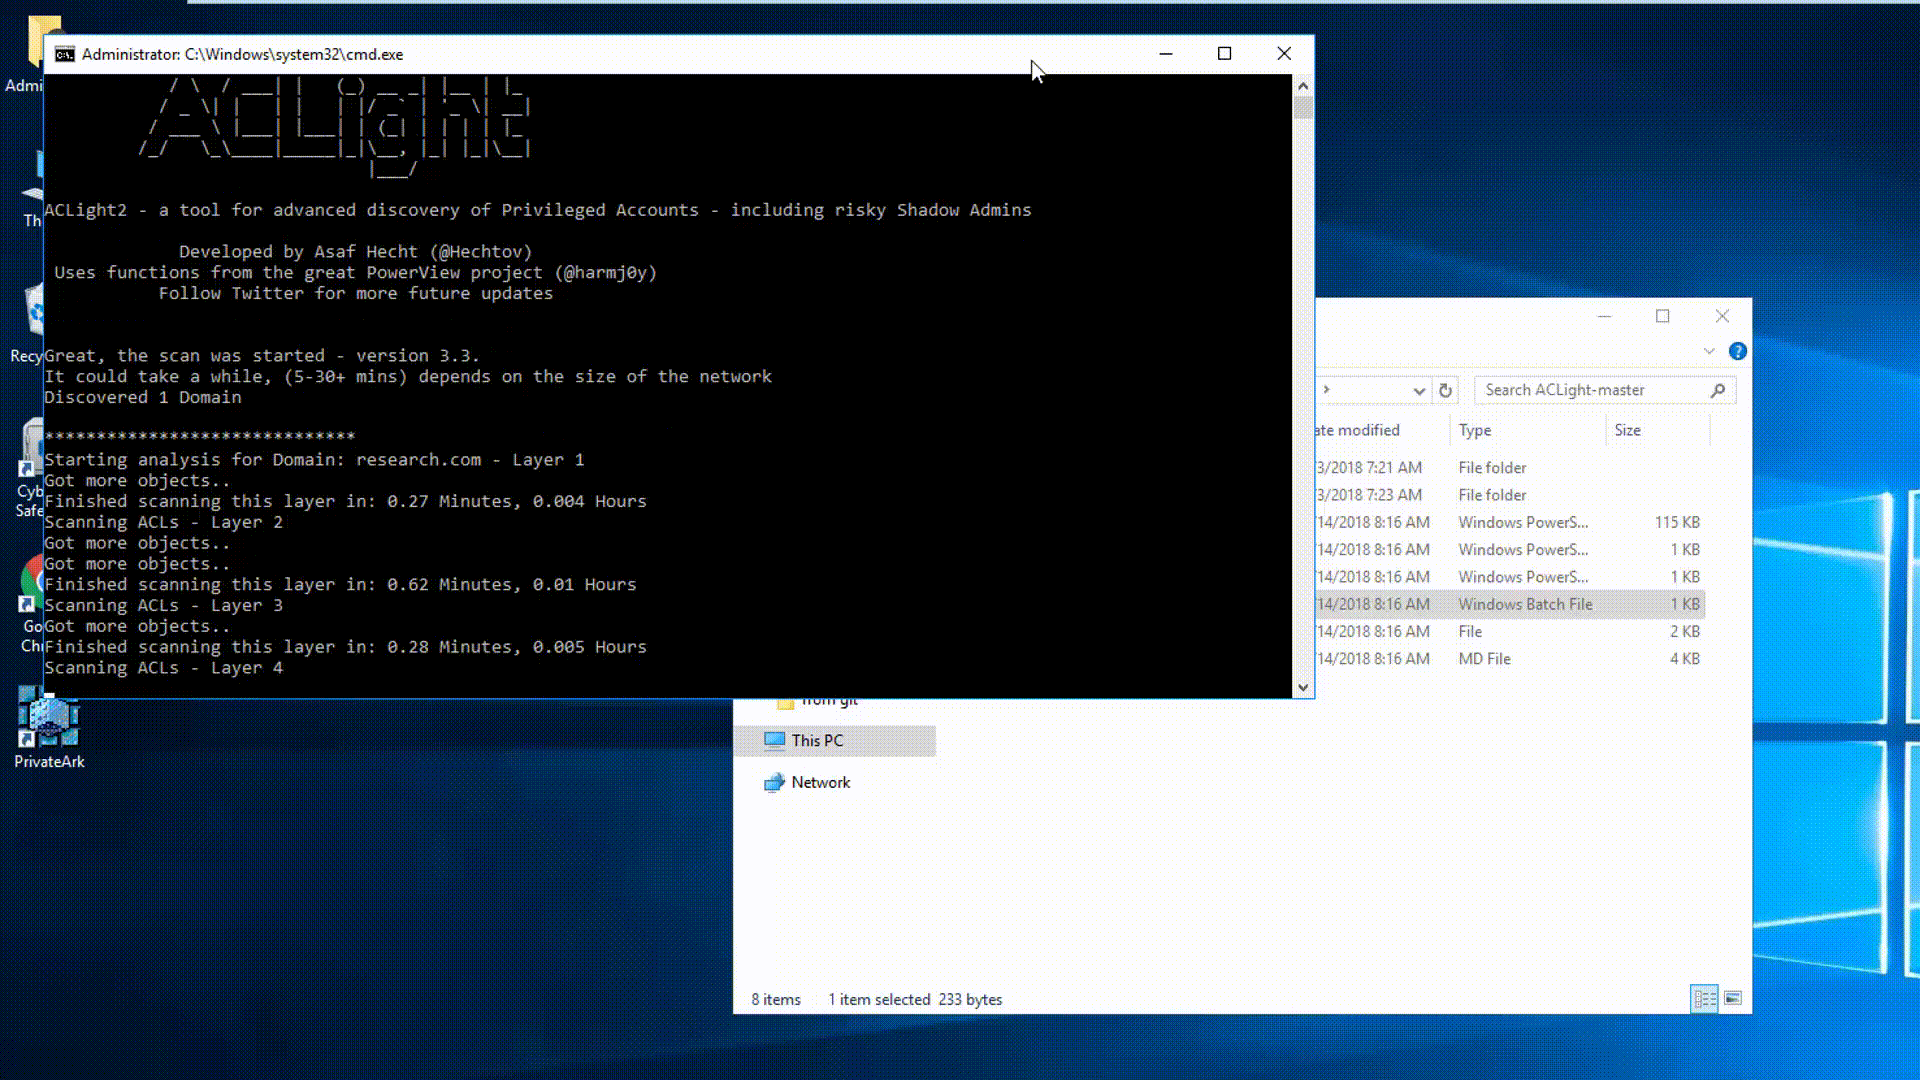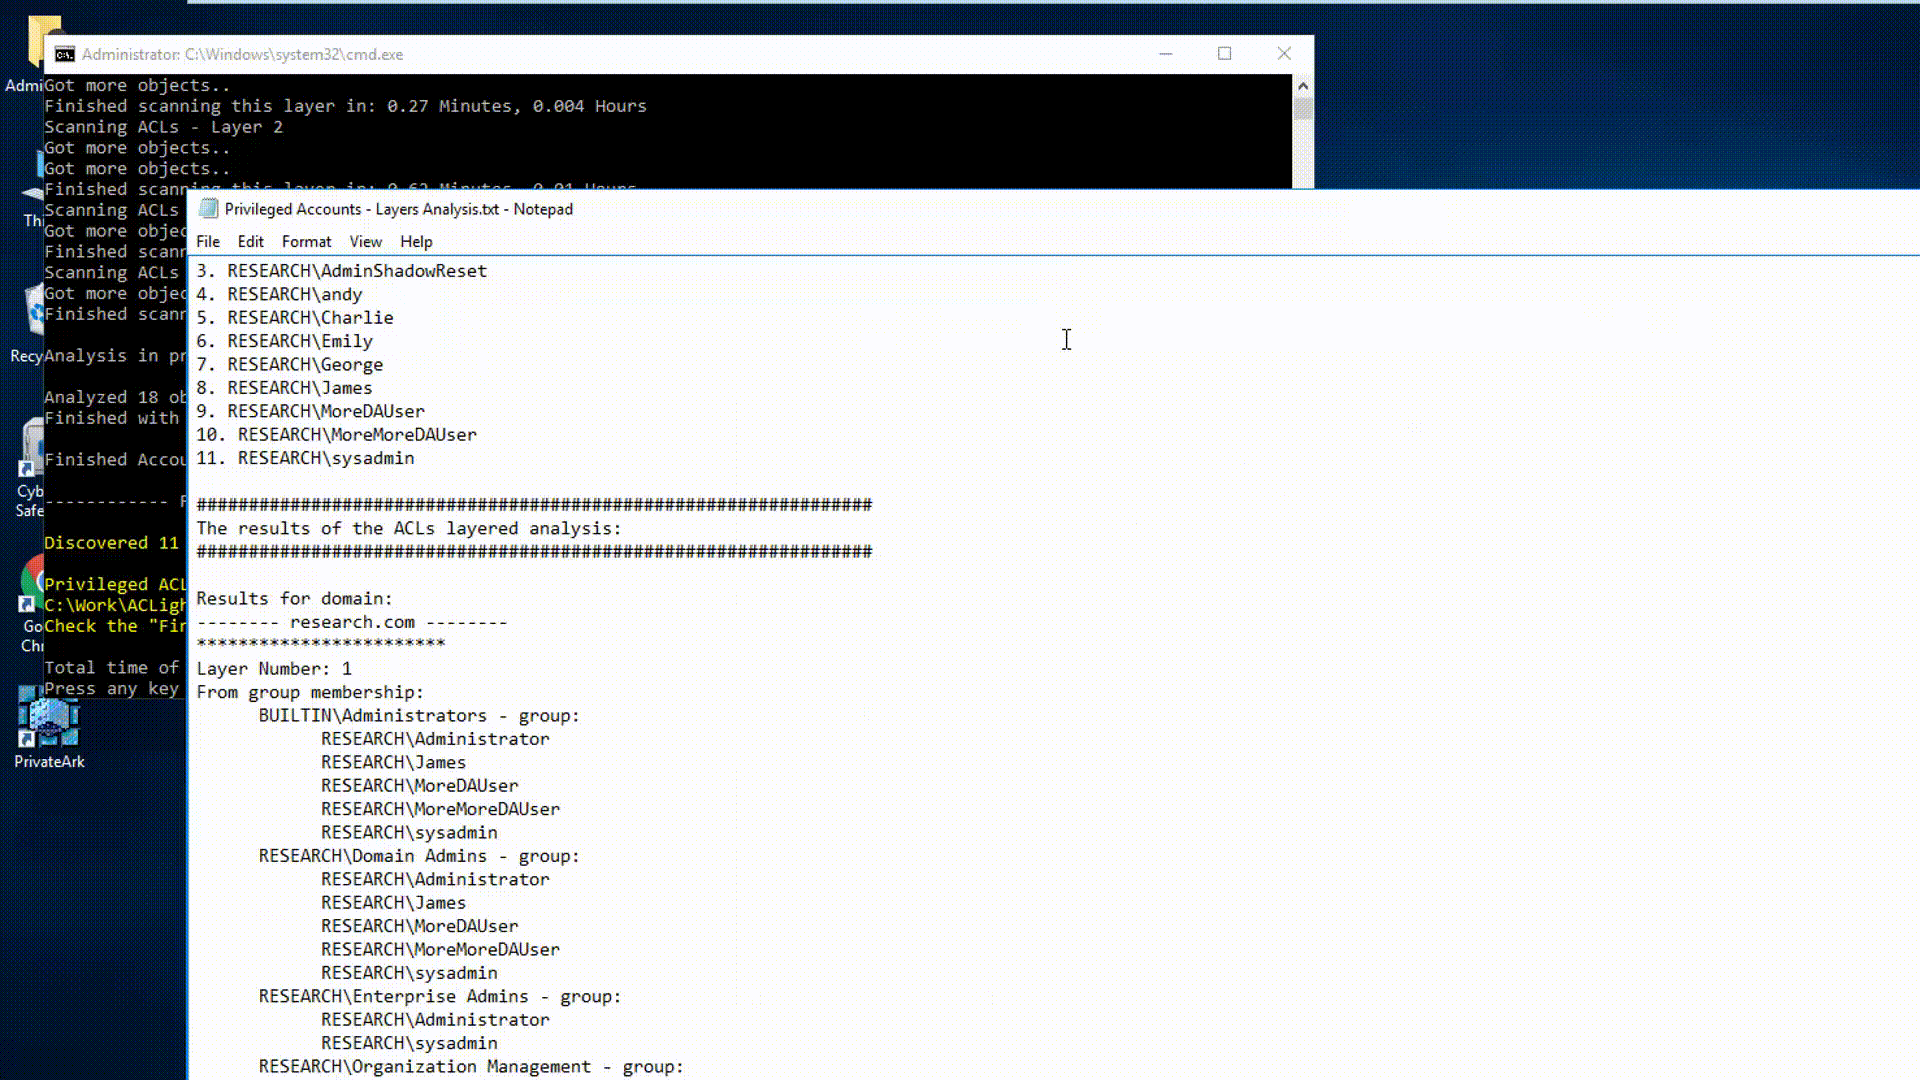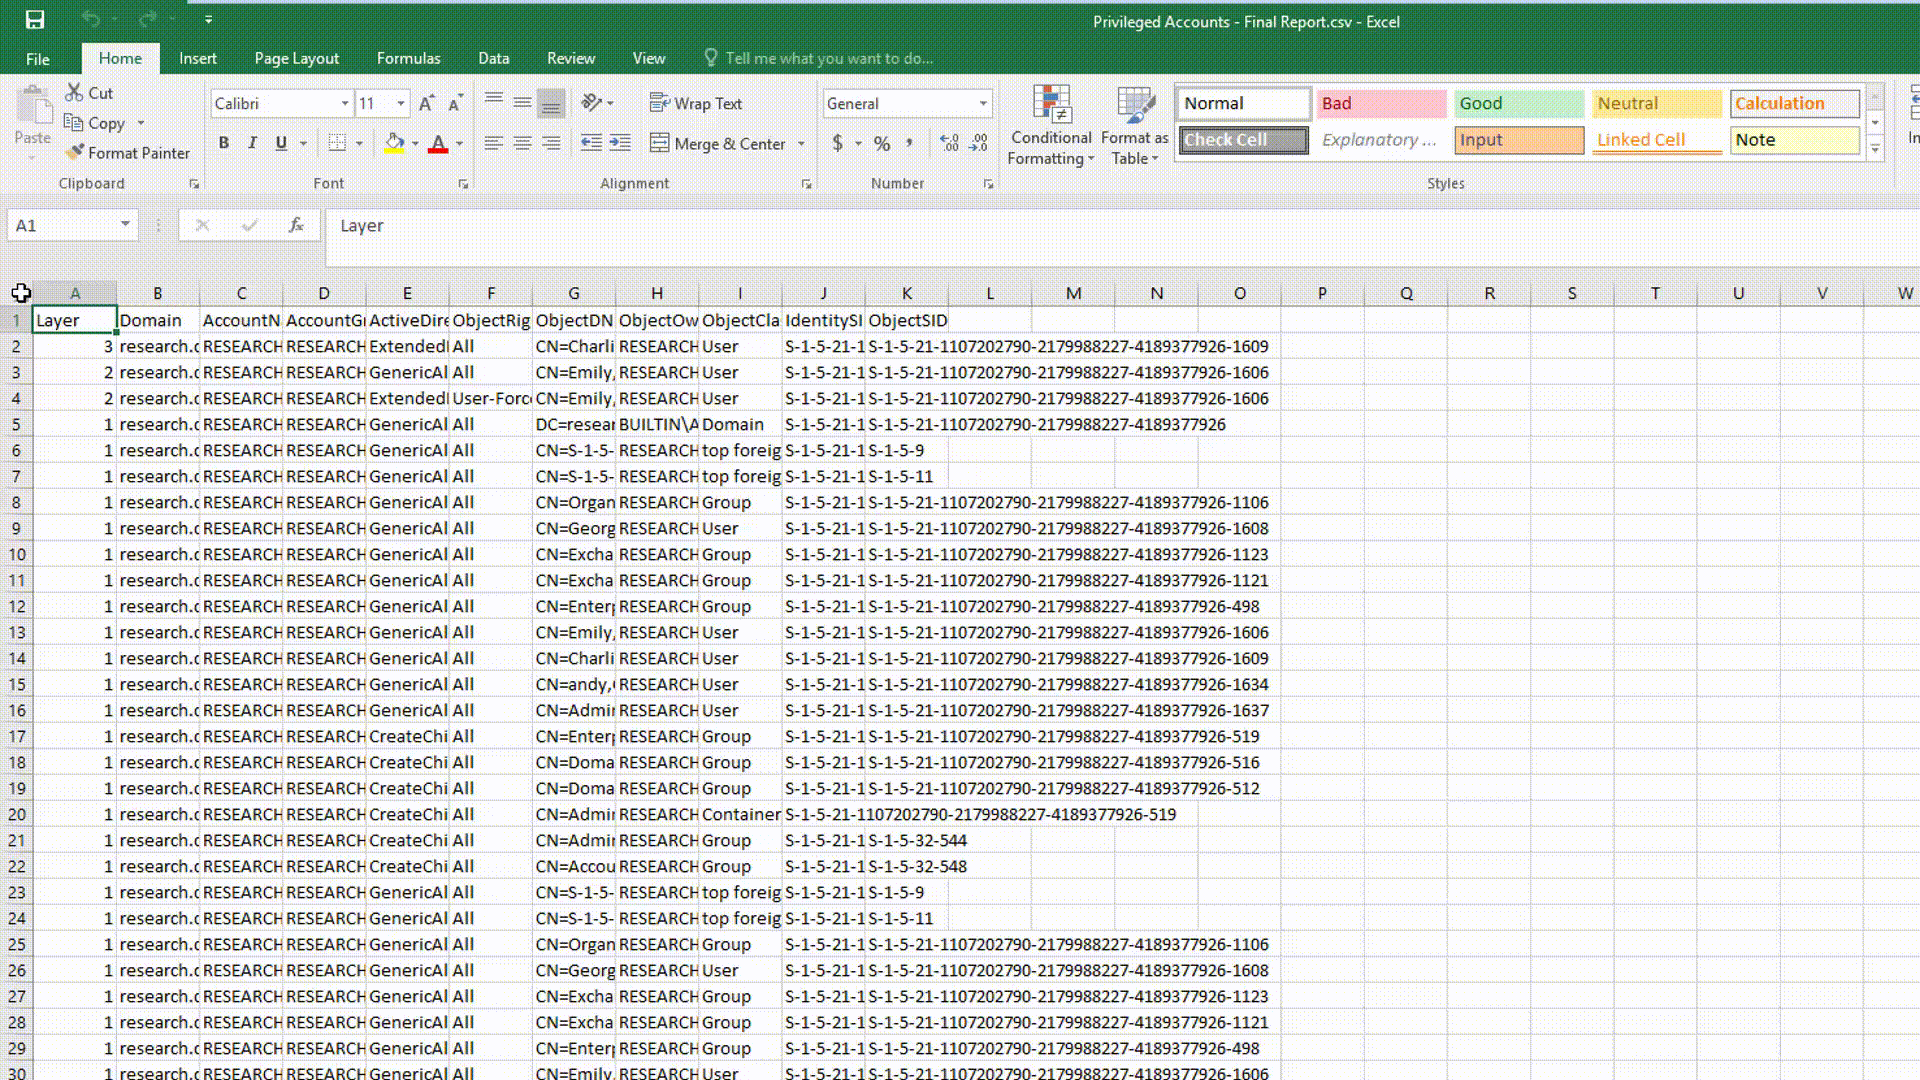 cyberark/aclight
A script for advanced discovery of Privileged Accounts - includes Shadow Admins