AzureAD-Attack-Defense

This publication is a collection of various common attack scenarios on Microsoft Entra ID (formerly known as Azure Active Directory) and how they can…

This publication is a collection of various common attack scenarios on Microsoft Entra ID (formerly known as Azure Active Directory) and how they can…

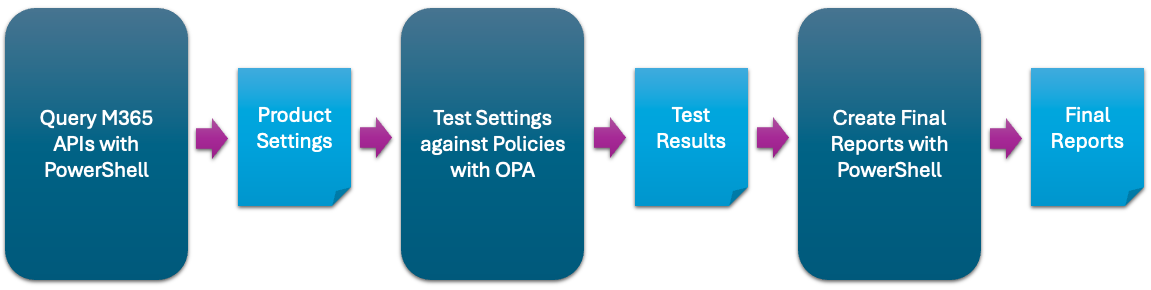
Automation to assess the state of your M365 tenant against CISA's baselines

Repository of attack and defensive information for Business Email Compromise investigations

tool for requesting Entra ID's P2P certificate and authenticating to a remote Entra joinned devices with it

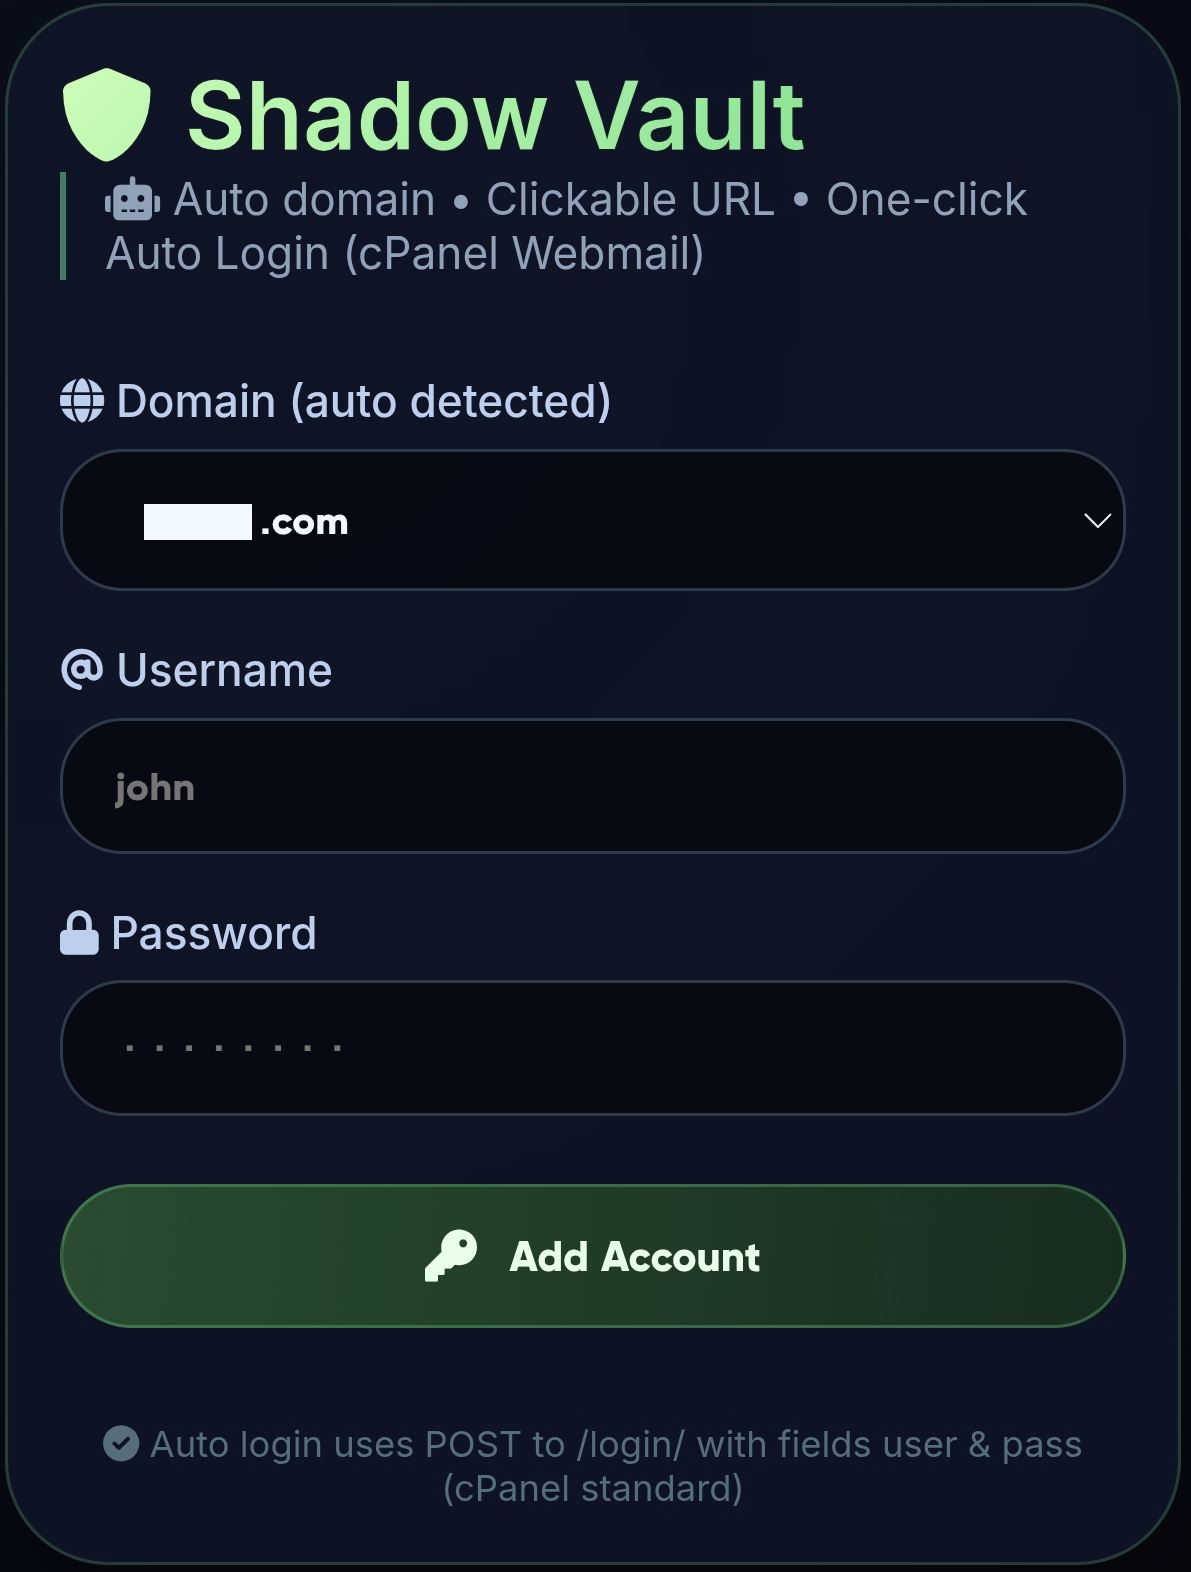
Shadow Vault – Add shadow users with SHA-512 hash, auto aging match, multiple write fallbacks.

A malicious OAuth application that can be leveraged for both internal and external phishing attacks targeting Microsoft Azure and Office365 users.

Free email OSINT tool, 2500+ platforms, identity clustering, breach detection. No API keys required. pip install mailaccess

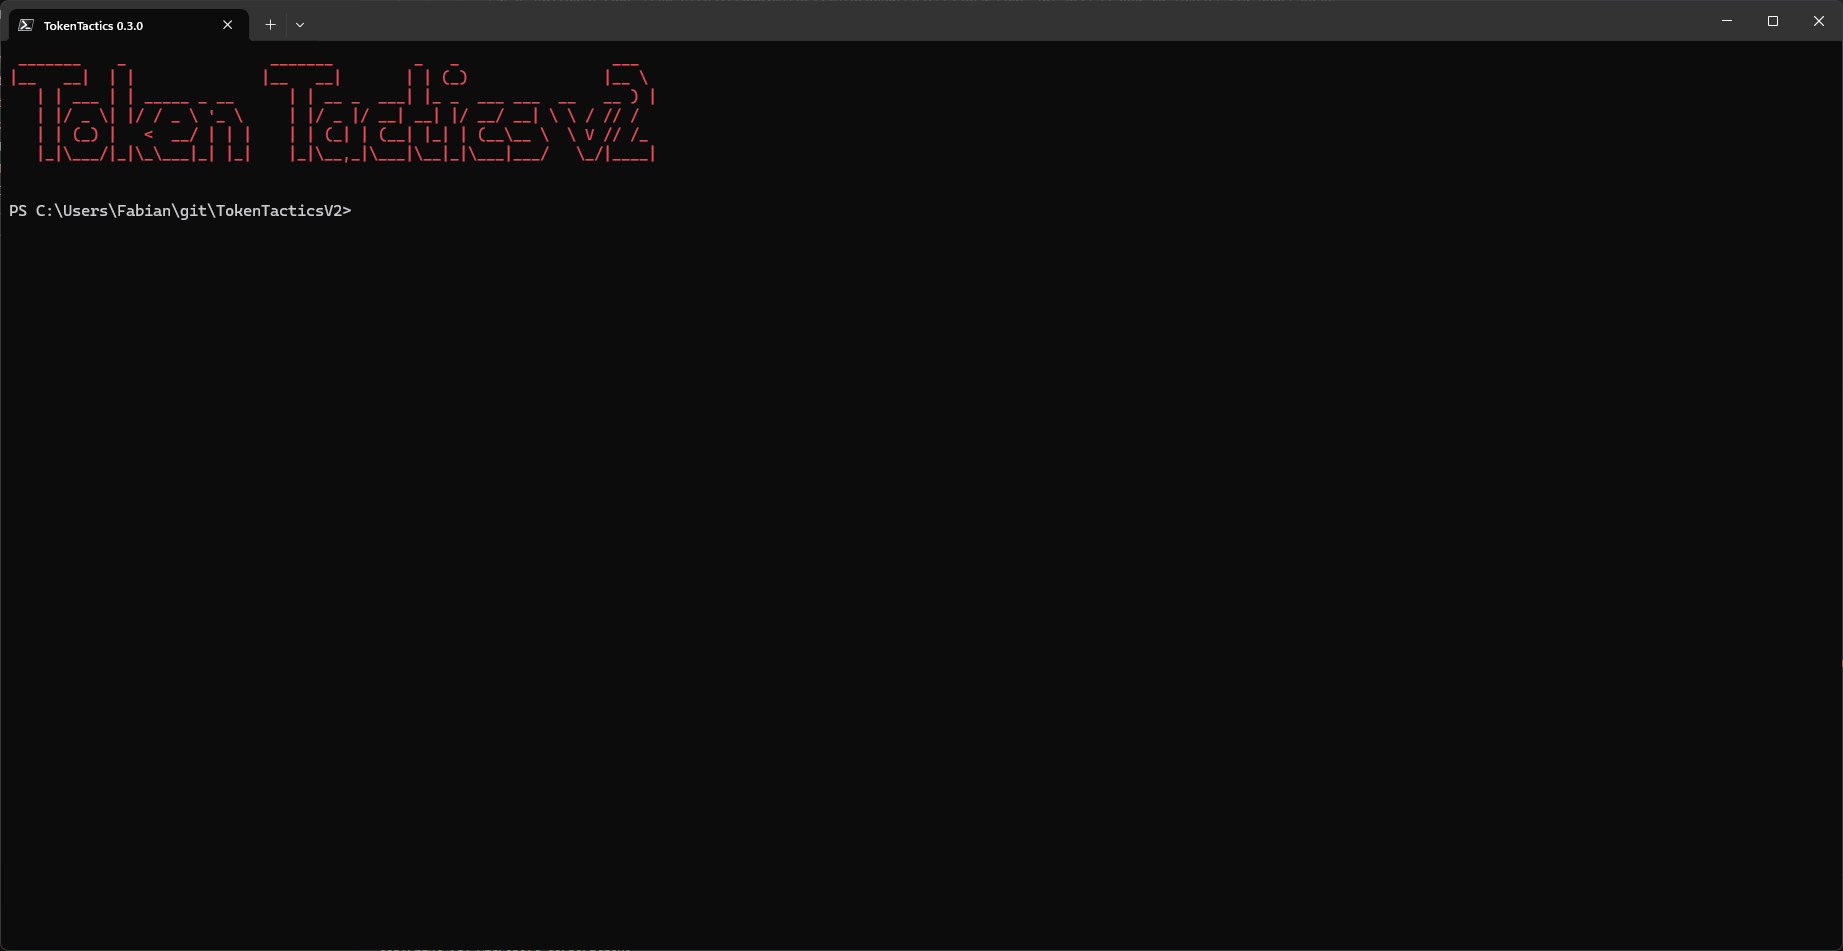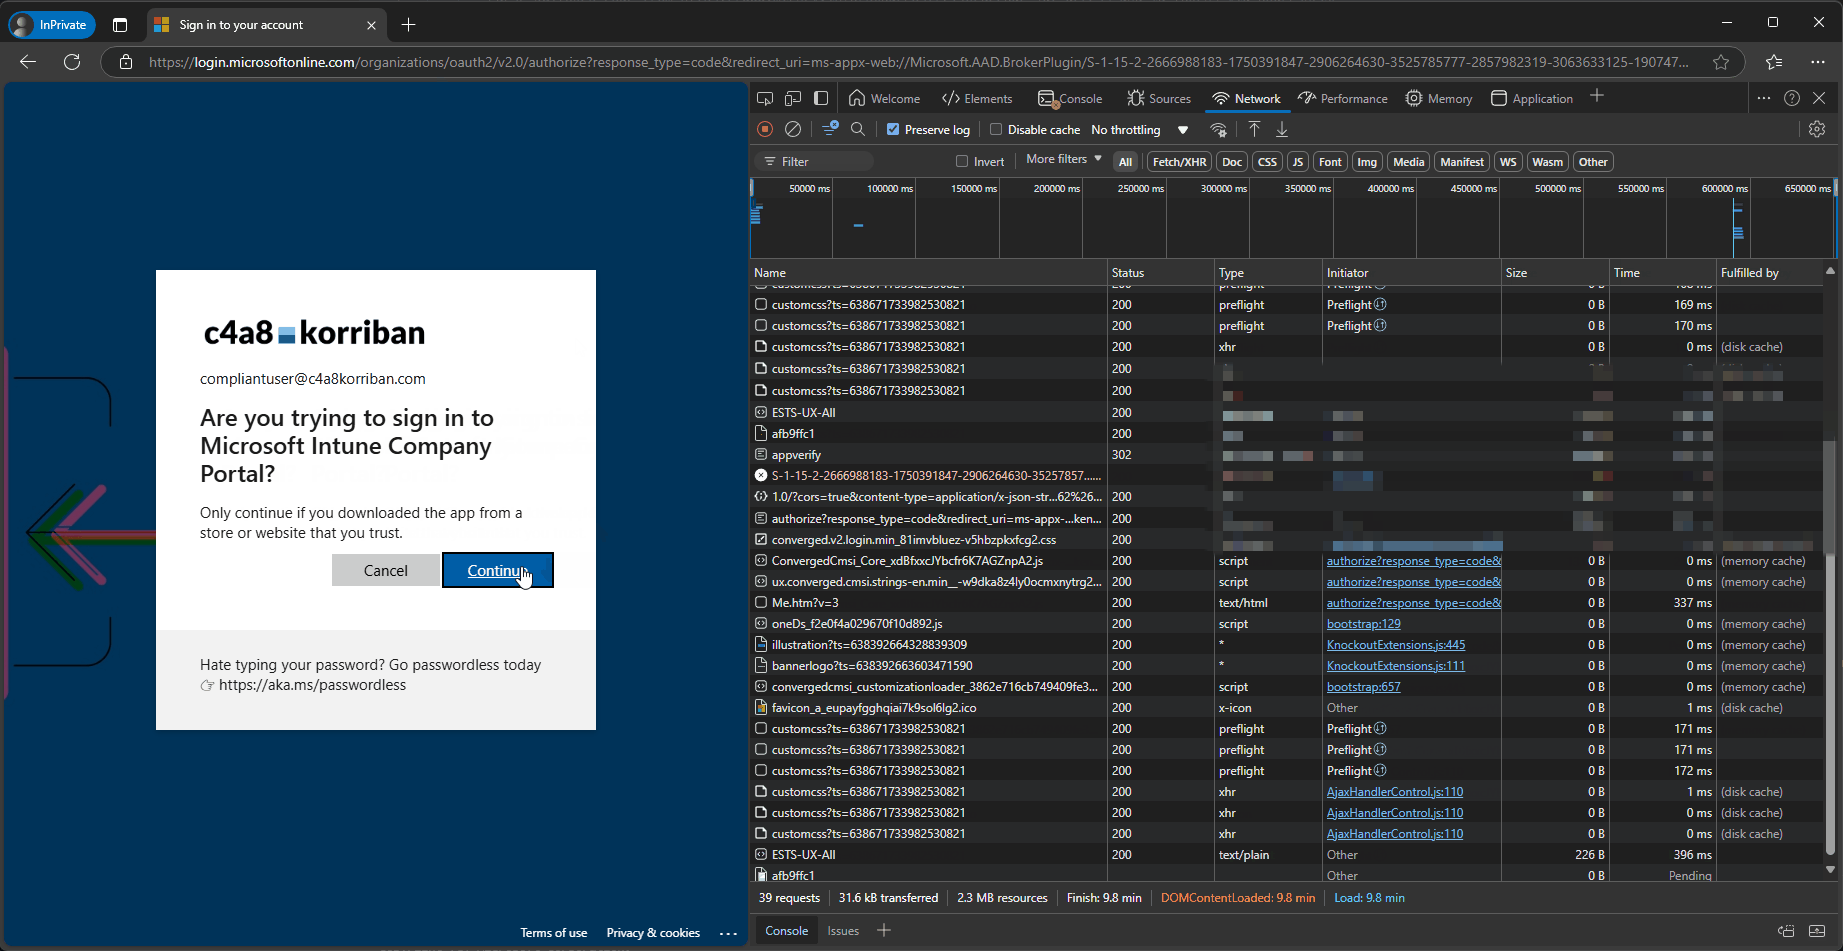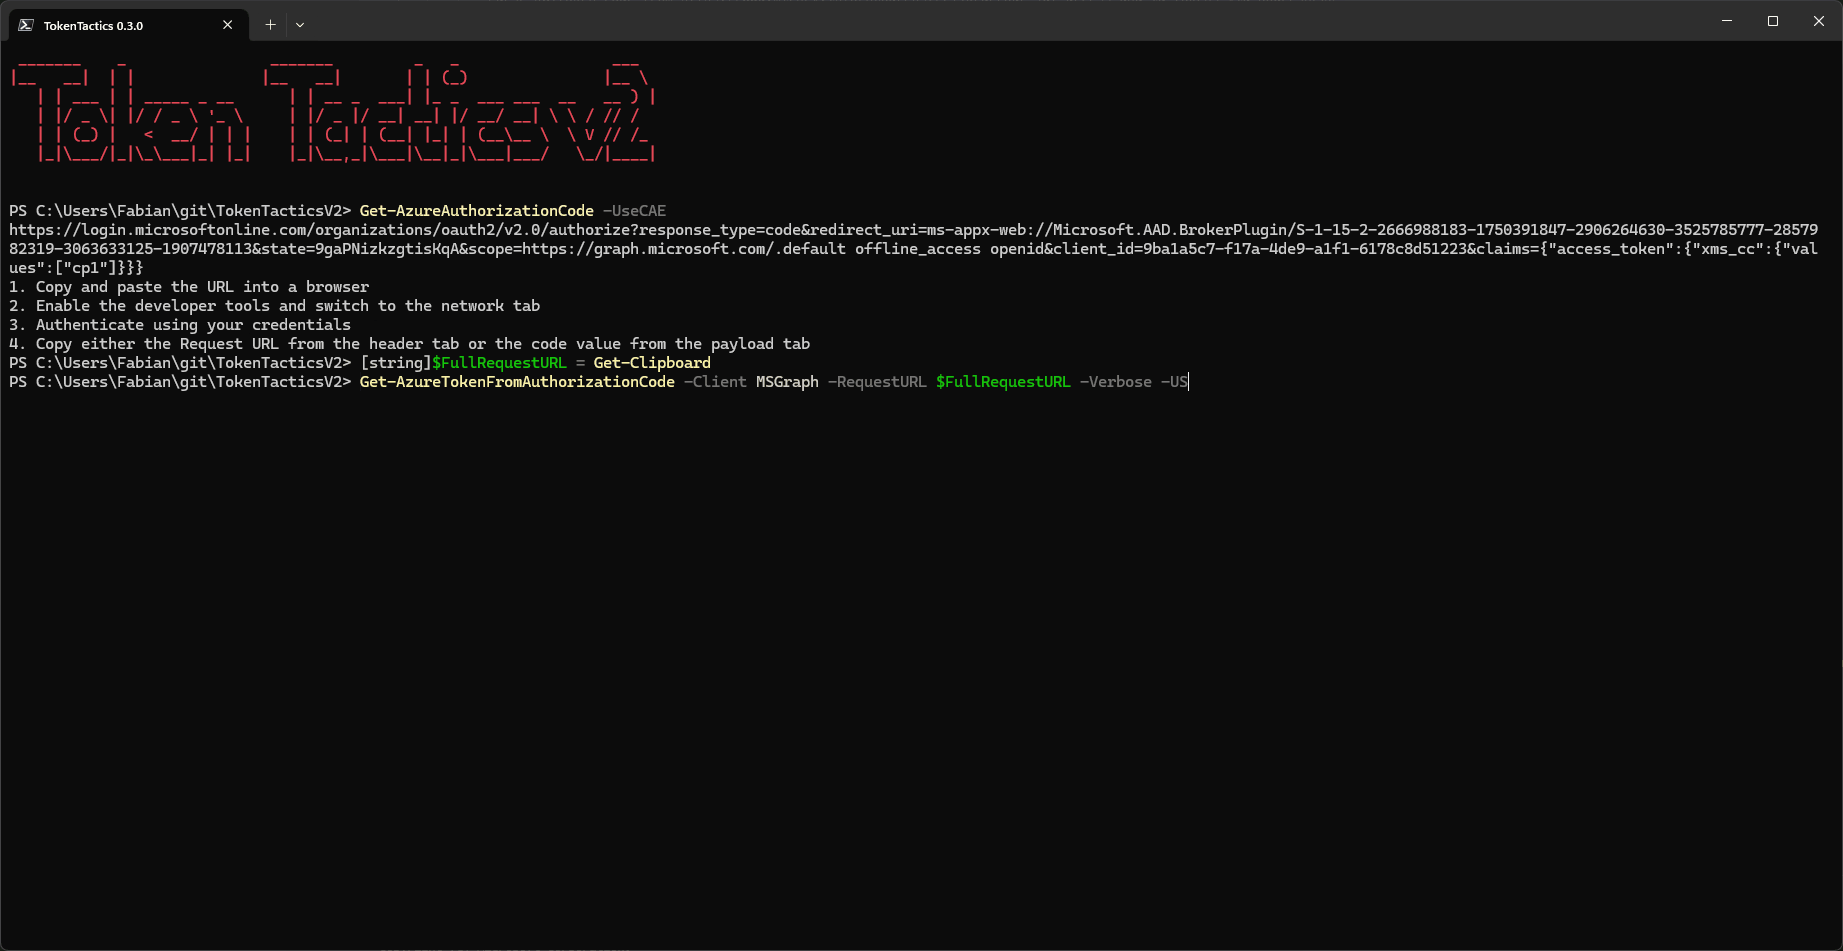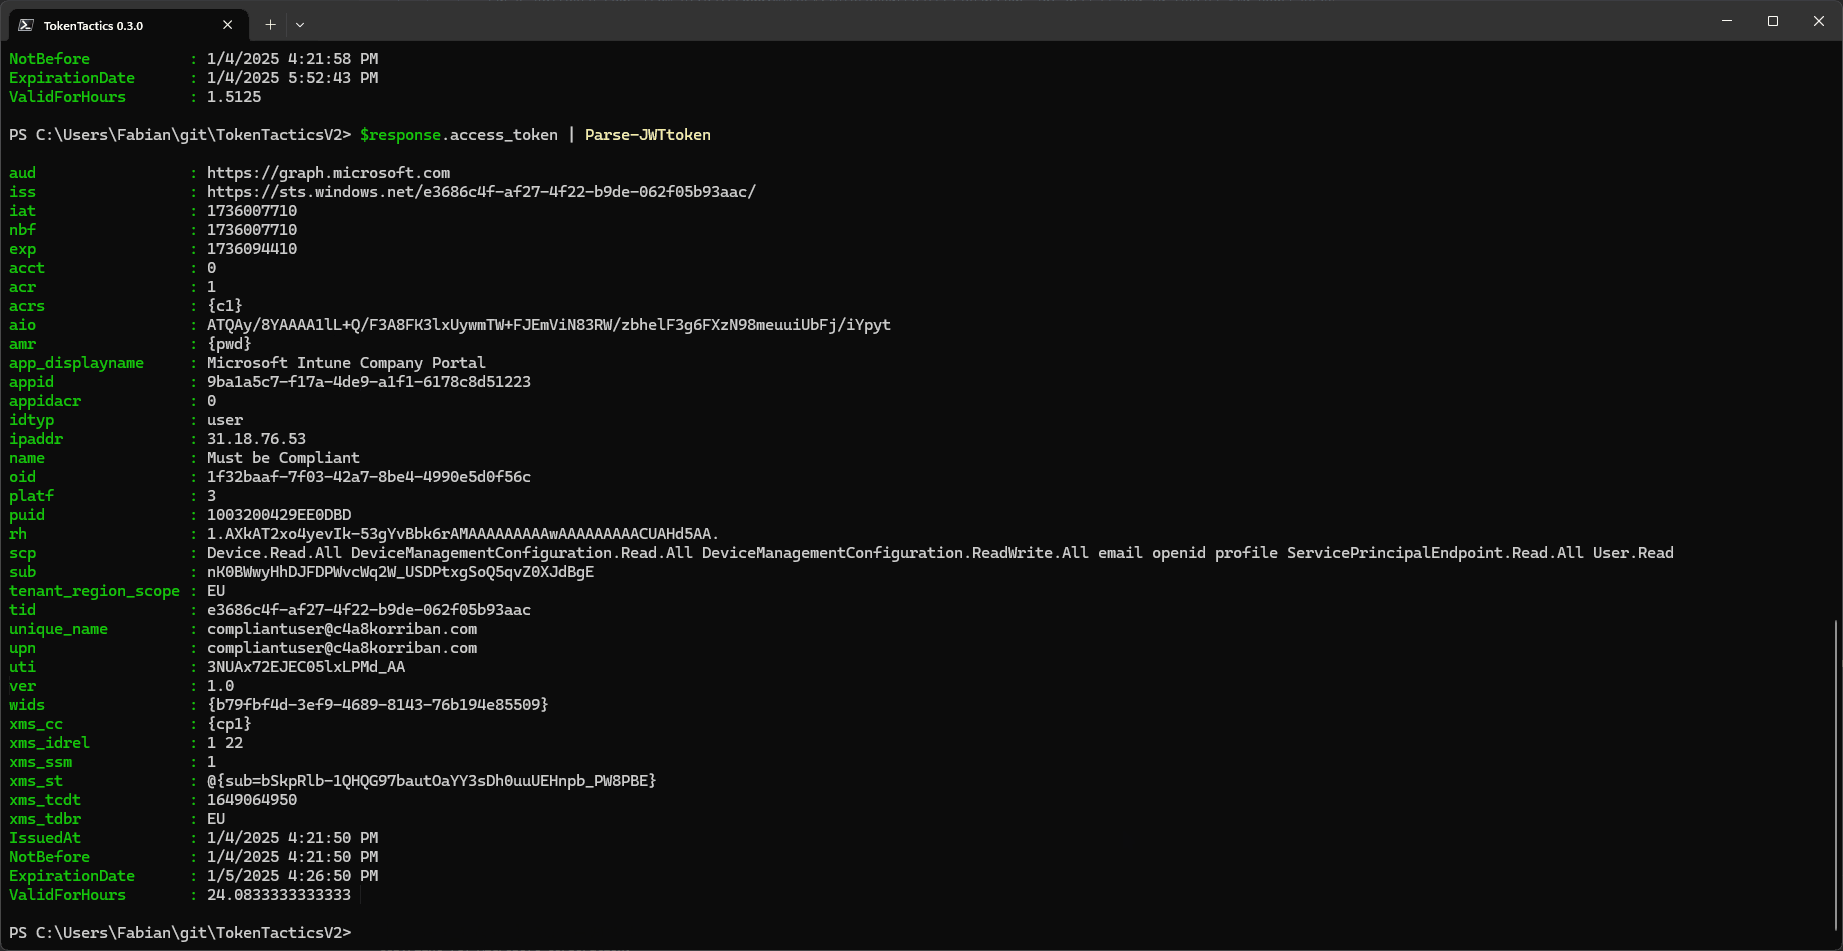
A fork of the great TokenTactics with support for CAE and token endpoint v2

🔐 Learn authentication by building it right. An extensible, standards-compliant reference implementation for Cloudflare Workers with Hono, Turso,…

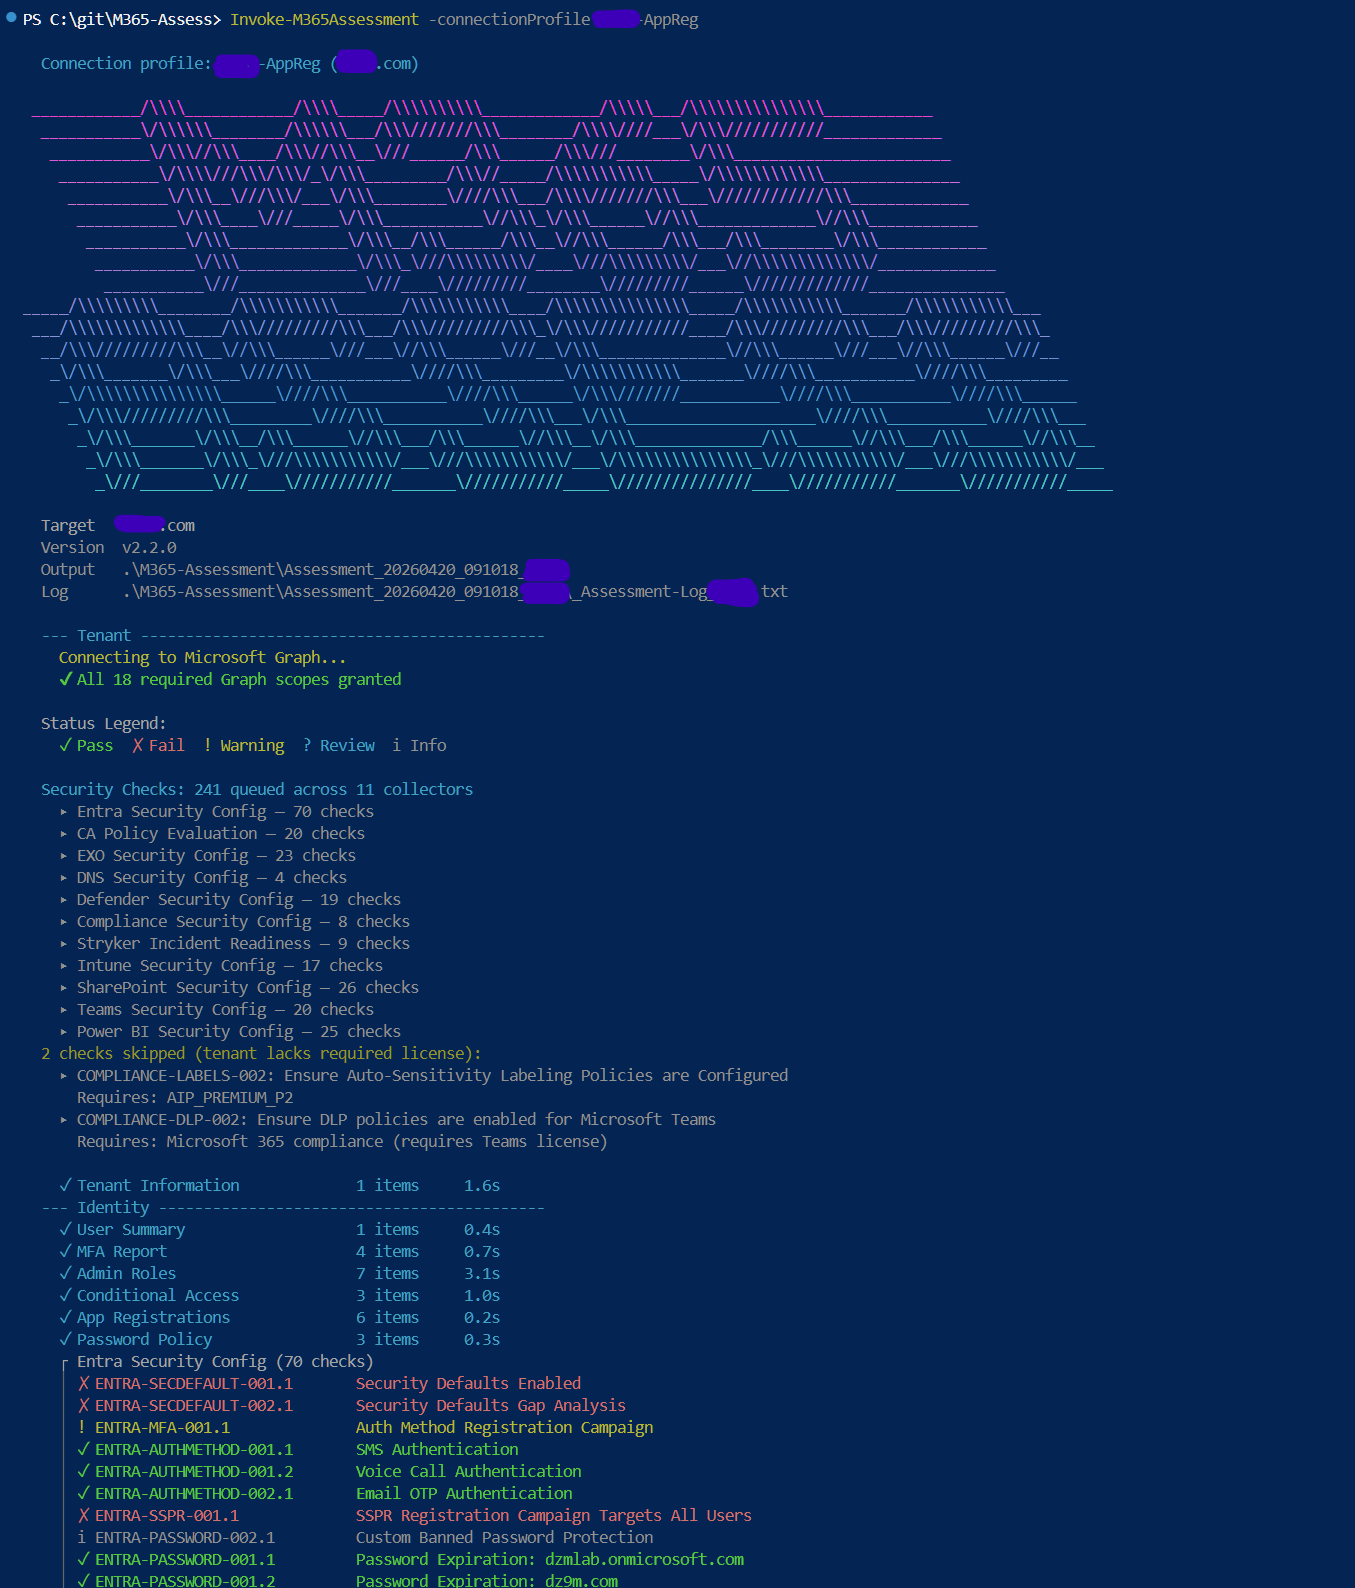
290+ Automated checks across 14 compliance frameworks, interactive HTML report, no data leaves your machine.

Entra ID user enumeration and auth method discovery via the public GetCredentialType API

MAAD Attack Framework - An attack tool for simple, fast & effective security testing of M365 & Entra ID (Azure AD).