gitea-cve-2026-116289-detection

Sigma detection rules, lab and findings for CVE-2026-116289 (Gitea public-only PAT to org Actions runner)

Sigma detection rules, lab and findings for CVE-2026-116289 (Gitea public-only PAT to org Actions runner)

Proof-of-concept for CVE-2026-11800: forges HS256 JWT assertions using Keycloak's IdP RSA public key DER bytes to mint tokens for federated users,…

Python PoC for CVE-2026-11800: forges HS256 JWT assertions signed with a Keycloak IdP public key to bypass authentication and impersonate federated…

Proof-of-concept and write-up for CVE-2026-123618: ABP Framework's external login provider path in the OpenIddict password grant bypasses 2FA,…

Recon tools and Sigma/KQL detections for testing whether VPN/SASE device trust can be transplanted after endpoint compromise, with conference slides.

Working PoC for CVE-2026-18963, an unauthenticated account takeover in Keycloak's forgot-password flow, plus a lab provisioning script and…

Python PoC and safe-check probe for the Keycloak reset-credentials bypass (CVE-2026-18963) enabling unauthenticated account takeover, with a…

🐾 Authority, not credentials, for AI agents: policy-approved actions, delegation that can only narrow, instant revocation, tamper-evident audit.

Java security framework providing authentication, authorization, cryptography, and session management APIs for securing applications from mobile to…

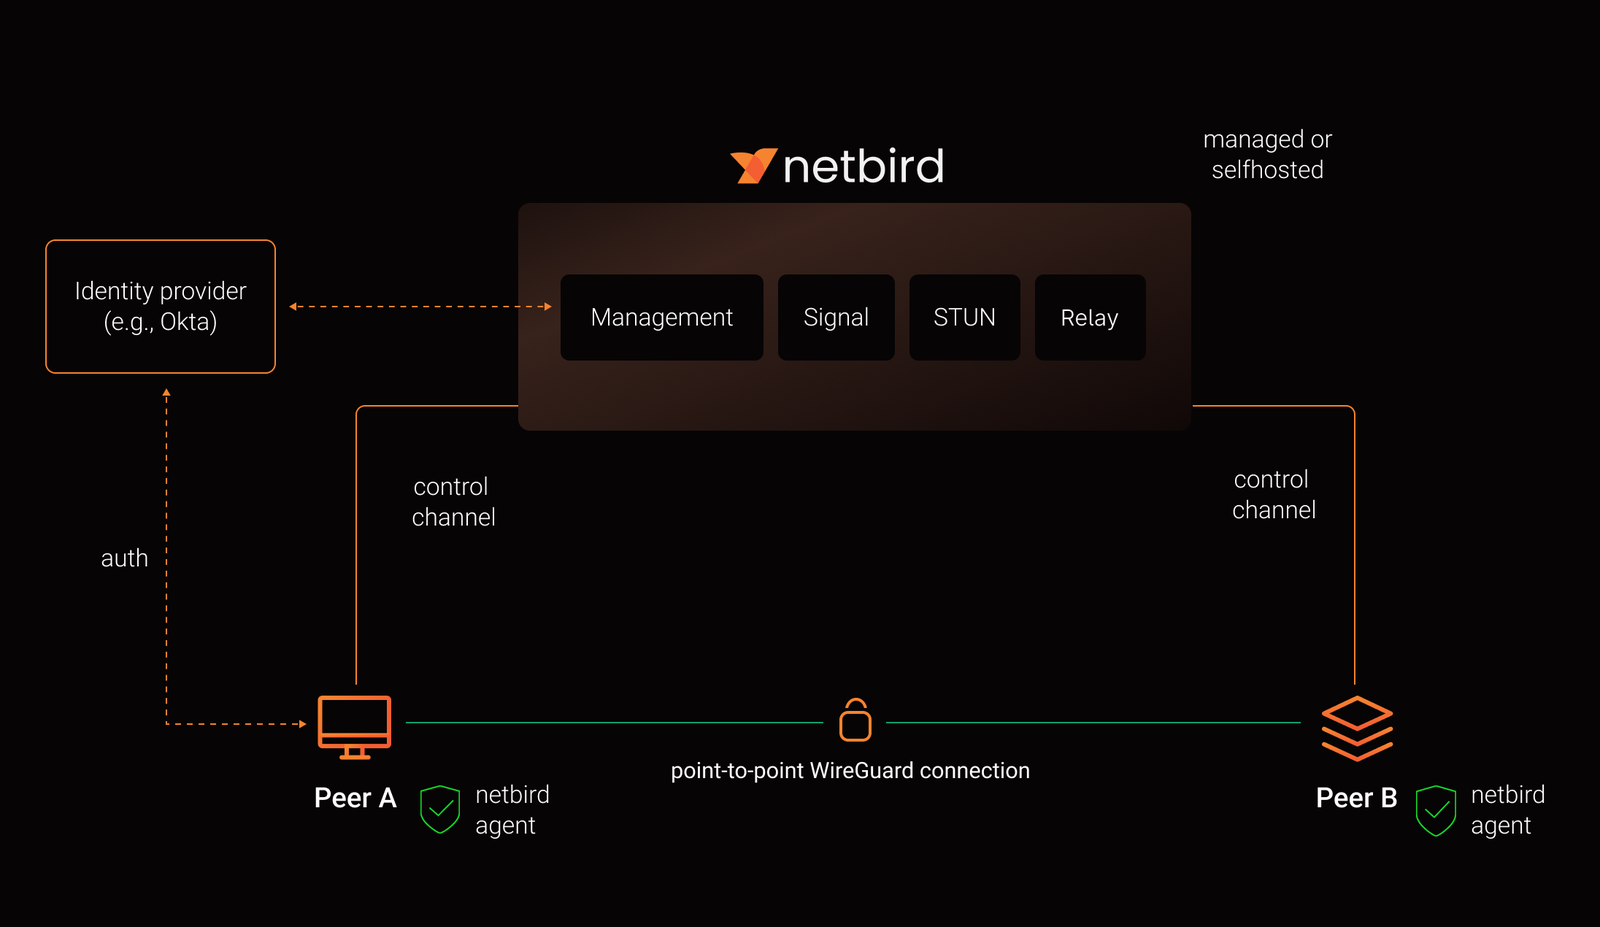
Identity-based Zero Trust networking platform that builds peer-to-peer WireGuard overlay networks with granular access policies, SSO/MFA, and…

A Loom security admin can change only the SSO issuer and keep a super-admin group mapping. Login then becomes super-admin, and an anonymous token…

Self-hosted, invite-only encrypted file sharing in Flask. Each file gets its own AES-256-GCM key, sealed with HPKE for every reader. Signed uploads,…

CVE-2026-80097 - Microsoft Authenticator Android Token Theft PoC & Exploit

Reproducible Docker lab + PoC: Keycloak manage-users -> realm-admin escalation via composite roles (CVE-2026-94000 variant). Validated on 26.8.1.

Benign, offline reproduction of CVE-2026-93355 — LiteLLM unverified-email JWT account takeover (runs LiteLLM's real code)

Loopback PoC for a Keycloak 26.8.1 SAML broker flaw: a percent-encoded duplicate SAMLResponse name bypasses redirect signature verification, allowing…

Keycloak 26.8.1 Medium 6.6 Remote authenticated auth leftover. A help-desk admin with manage-users can pin a pre-built composite of manage-realm onto…

Unofficial Bitwarden compatible server written in Rust, formerly known as bitwarden_rs