

TATS
 icemoonhsv/tats
Analyze and track OAuth 2.0, OIDC, and Microsoft Entra ID tokens from Burp, mitmproxy, or Chrome DevTools captures. Visualize token lifecycles,…
authenticationidentity-access-managementlog-analysis+2
7
icemoonhsv/tatsAnalyze and track OAuth 2.0, OIDC, and Microsoft Entra ID tokens from Burp, mitmproxy, or Chrome DevTools captures. Visualize token lifecycles,…
 squeeze440/tugtainer-poc
PoC — OIDC id_token accepted without signature/audience/expiry check in Tugtainer (GHSA-crjc-6vc7-xrfh, CVE-2026-87004, CVSS 8.1).
 ccob/pivert
Emulates NIST SP 800-73 PIV smart cards on Windows using a PFX certificate and private key, enabling smart-card authentication for RDP, Citrix, and…
 prof.shafiei/abdal-lockbox
Local-first encrypted password vault for Android with Master Password access, Recovery Key support, Autofill integration, and portable encrypted…
 manuelberrueta/flowanalyzer
FlowAnalyzer is a tool to help in testing and analyzing OAuth 2.0 Flows, including OpenID Connect (OIDC).
 logangoins/sharpsuccessor
SharpSuccessor is a .NET Proof of Concept (POC) for fully weaponizing Yuval Gordon’s (@YuG0rd) BadSuccessor attack from Akamai.
 synacktiv/captaincredz
CaptainCredz is a modular and discreet password-spraying tool.
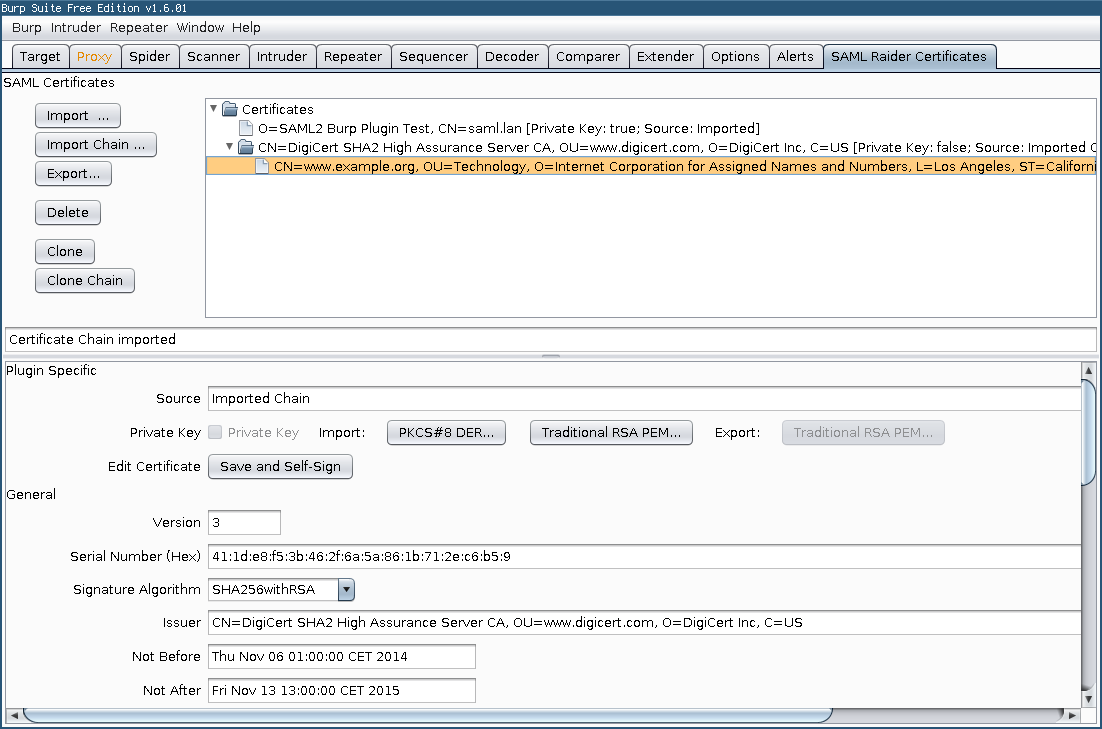 lindi2/samlraider
SAML2 Burp Extension
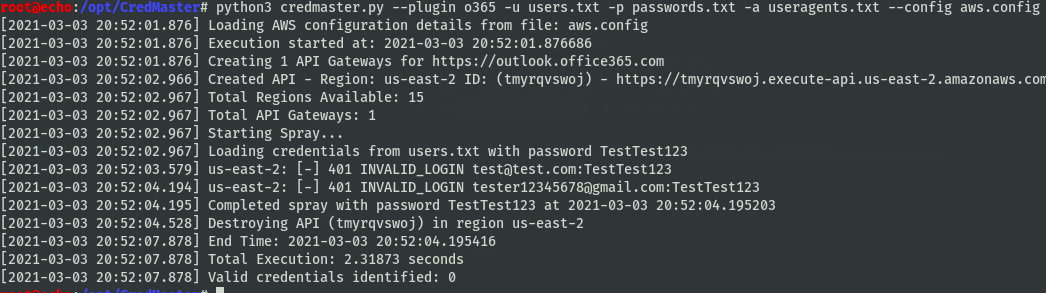 knavesec/credmaster
Refactored & improved CredKing password spraying tool, uses FireProx APIs to rotate IP addresses, stay anonymous, and beat throttling
 beemdevelopment/aegis
A free, secure and open source app for Android to manage your 2-step verification tokens.
 rockmelodies/blackash-cve-2025-41115
CVE-2025-41115
 notitssixtyn3in/cve-2025-4172025
Security advisory for CVE-2025-4172025: an authentication bypass vulnerability in Copilot enabling unauthorized account access, session hijacking,…
 secure-system/insular
Isolate your big brother apps https://secure-system.gitlab.io/Insular/
 honestcorrupt/phonepe-sensitive-data-exposure-cve-2025-5154
CVE-2025-5154: Proof-of-concept for unencrypted local storage of authentication tokens, PII, and KYC data in the PhonePe Android app, enabling…
 garrettfoster13/cve-2025-59501
CVE-2025-59501 POC code
 logisek/evilmist
EvilMist is a collection of scripts and utilities designed to support cloud penetration testing & red teaming. The toolkit helps identify…
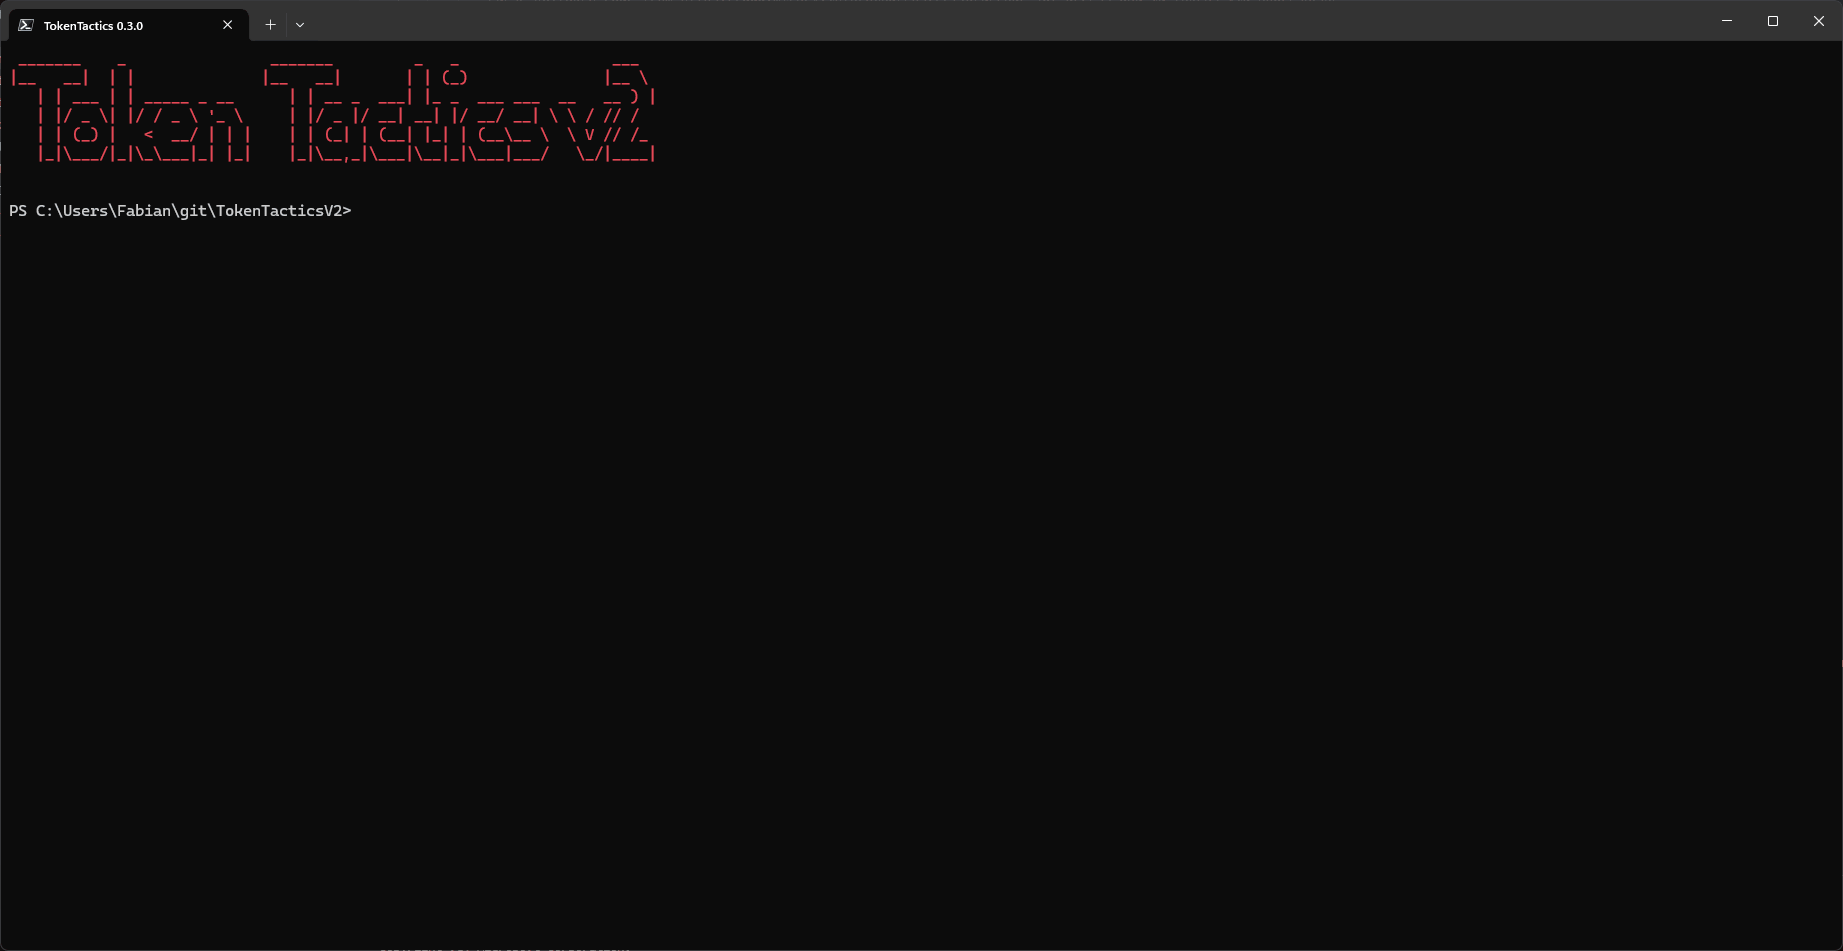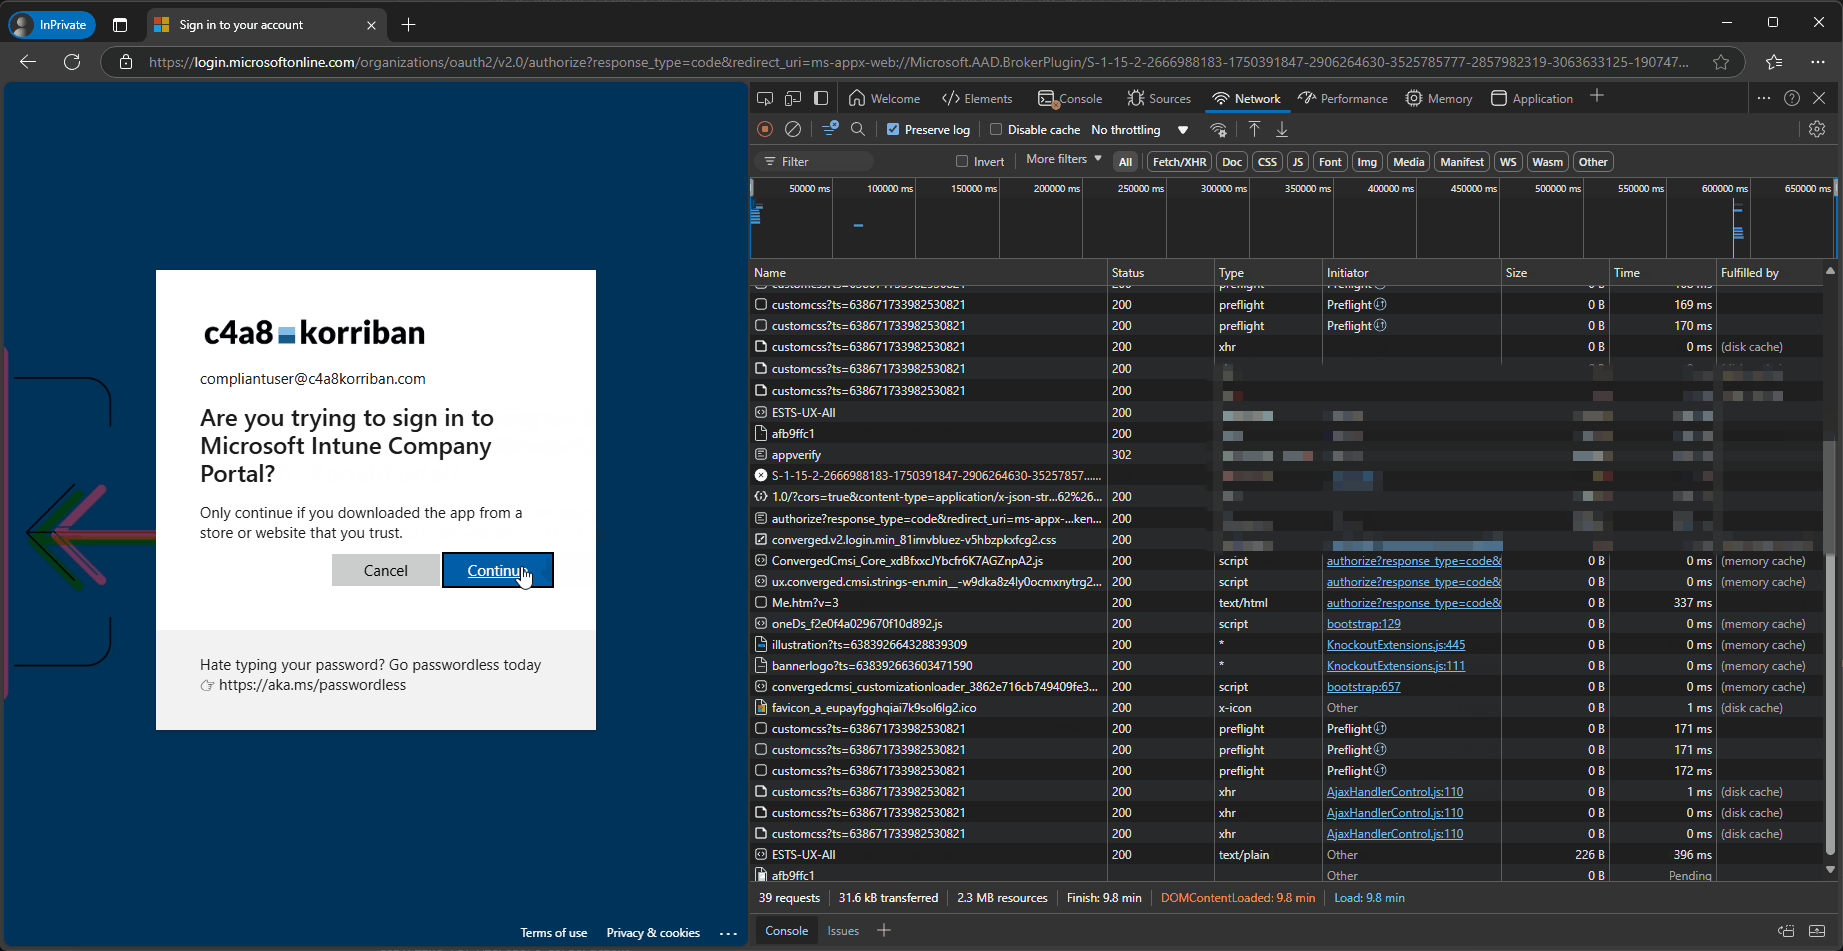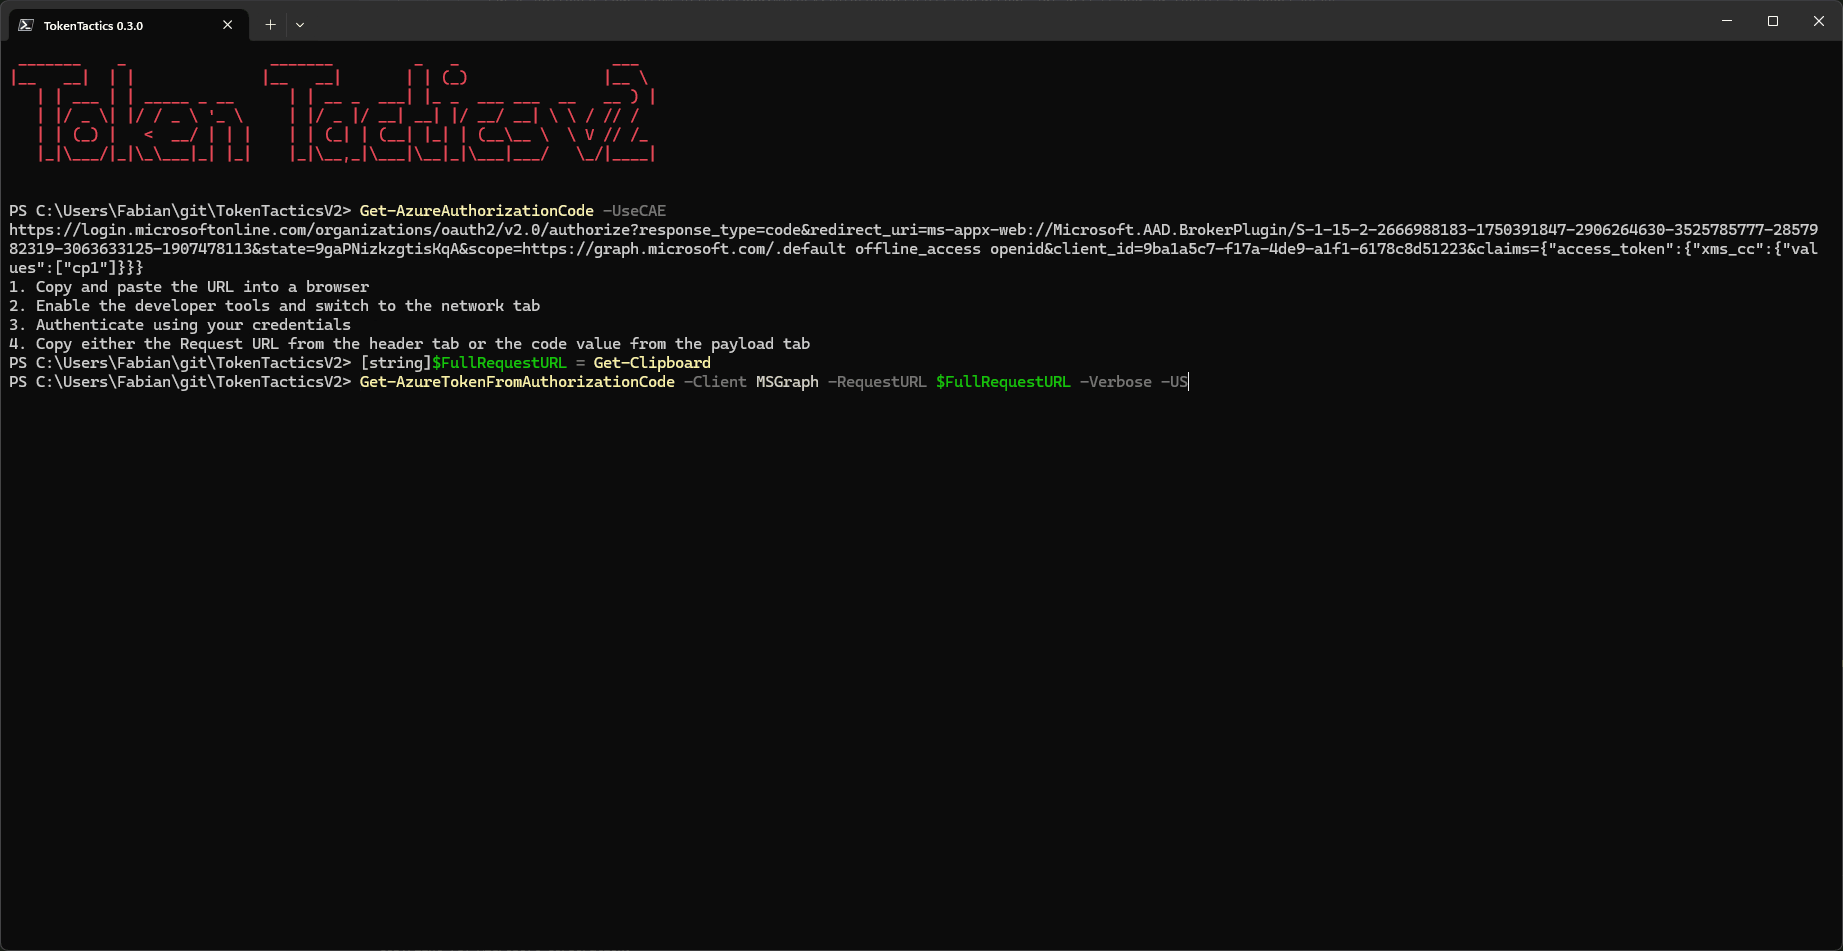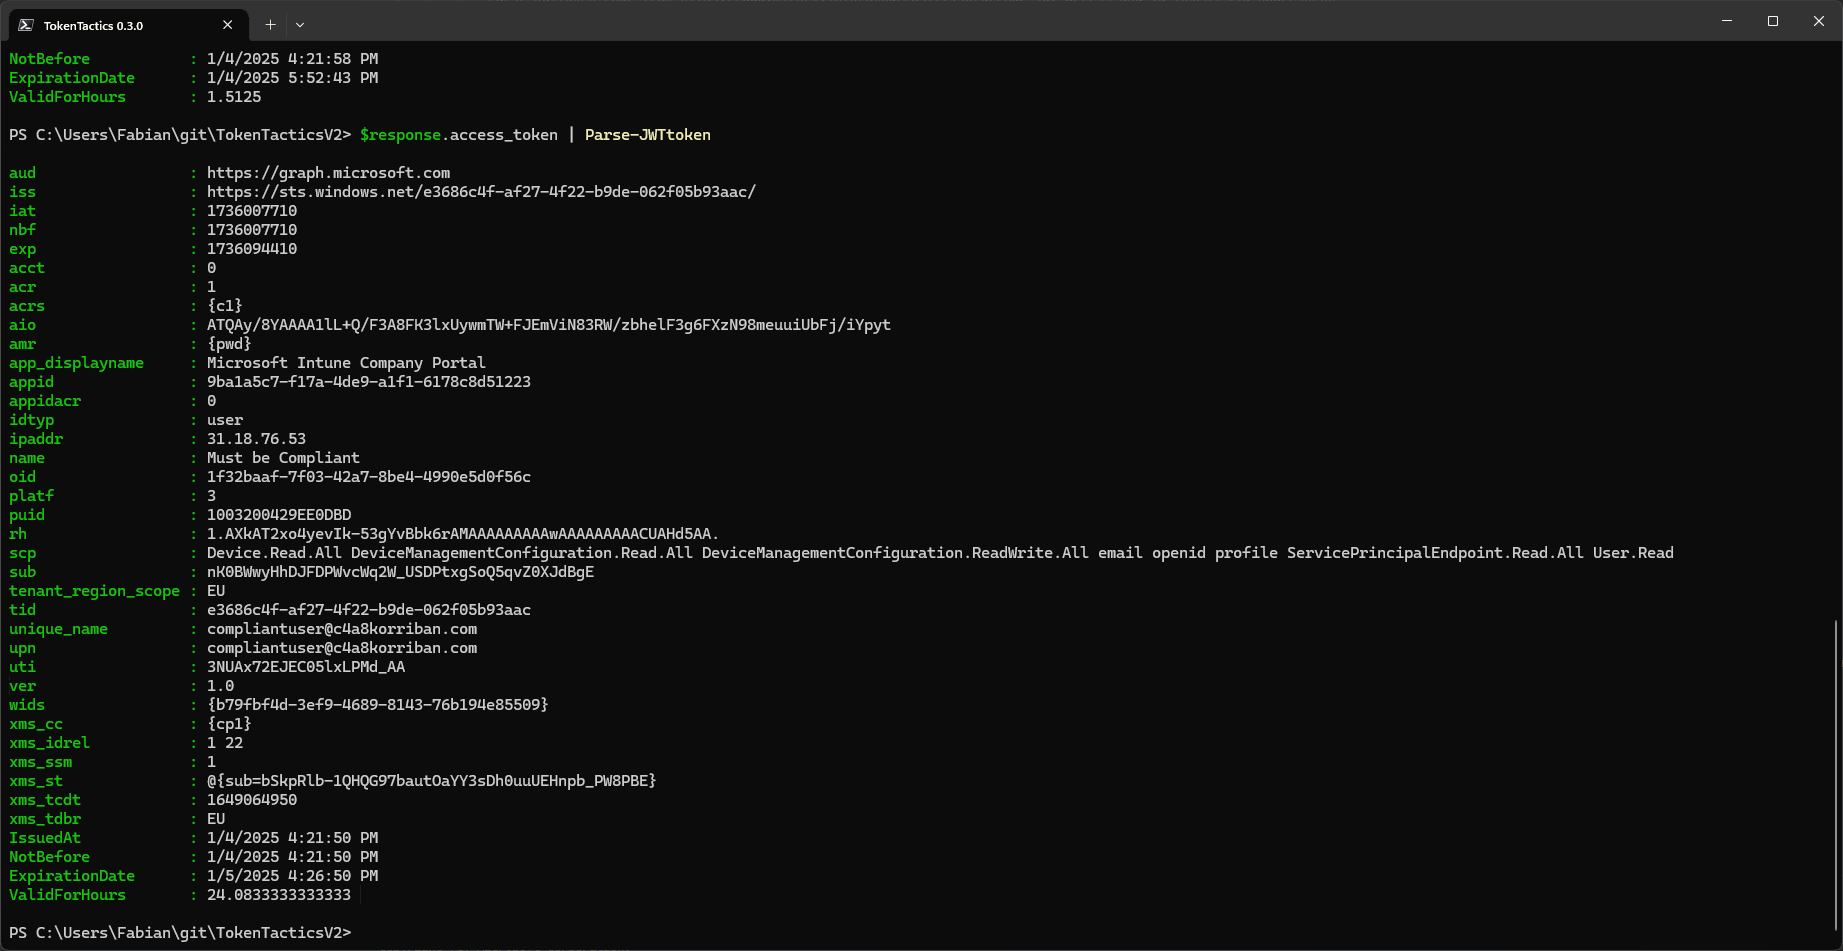 f-bader/tokentacticsv2
A fork of the great TokenTactics with support for CAE and token endpoint v2
 logisek/huntcyberark
CyberArk Security Audit