

 lkarlslund/hashmuncher
Grab NetNTLMv2 hashes using ETW with administrative rights on Windows 8.1 / Windows Server 2016 and later
 praetorian-inc/gladius
Automated Responder/secretsdump.py cracking
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
 theresafewconors/sooty
The SOC Analysts all-in-one CLI tool to automate and speed up workflow.
 ktzgraph/sarenka
OSINT tool - gets data from services like shodan, censys etc. in one app
 psypanda/hashid
Software to identify the different types of hashes -
 oalabs/hashdb
Assortment of hashing algorithms used in malware
 1an0rmus/tekdefense-automater
Automater - IP URL and MD5 OSINT Analysis
 joker25000/optiva-framework
Optiva-Framework 🔎 Web Application Scanner🕵️
 blackploit/hash-identifier
Software to identify the different types of hashes used to encrypt data and especially passwords
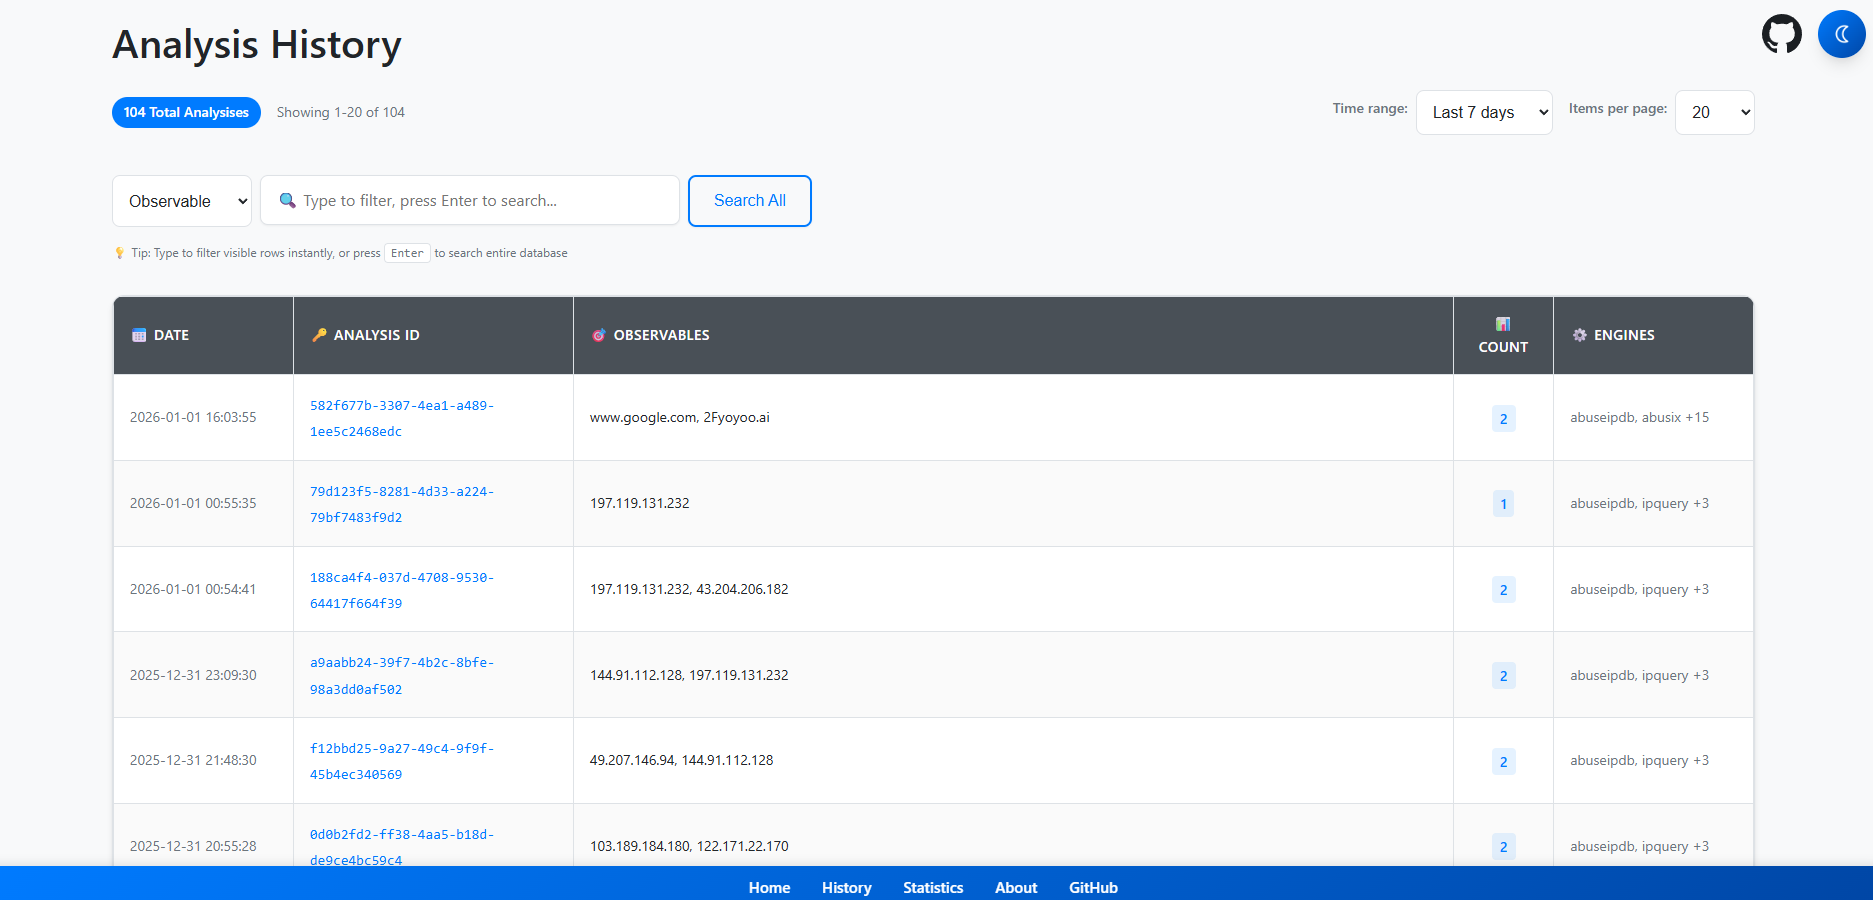 stanfrbd/cyberbro
A simple application that extracts your IoCs from garbage input and checks their reputation using multiple CTI services.
 c3rb3ru5d3d53c/binlex
A Binary Genetic Traits Lexer Framework
 badkeys/badkeys
Tool to find common vulnerabilities in cryptographic public keys