

dotnetfile
 pan-unit42/dotnetfile
Python library for parsing CLR/PE metadata in .NET assemblies, exposing streams and hash fingerprints to support malware analysis and threat hunting.
binary-analysisforensicshash-analysis+4
119
pan-unit42/dotnetfilePython library for parsing CLR/PE metadata in .NET assemblies, exposing streams and hash fingerprints to support malware analysis and threat hunting.
 idiom/pftriage
Python tool and library to help analyze files during malware triage and analysis.

 fin3ss3g0d/cve-2024-4956
Python utility for automating CVE-2024-4956 path traversal exploitation with mass file extraction, plus custom Hashcat module for cracking Apache…
 george0papasotiriou/cve-2026-22016-ipfs-cid-spoofing-via-multihash-length-extension
Python proof-of-concept demonstrating IPFS CID spoofing via multihash length extension, highlighting content-addressing verification flaws that can…
 star-sg/random-scripts
Collection of DFIR and OSINT Python scripts for parsing malicious LNK samples, extracting OLE objects from MHTML, and hashing favicons to hunt…
 ishaklaz/hash-eye
**HashEye** is a powerful Python CLI tool for instantly detecting and analyzing hash types. It provides detailed information about hash formats,…
 llcforge/cve-2026-124194
Python PoC for CVE-2026-124194: crafts Outlook .msg files with RTF INCLUDEPICTURE UNC paths to capture NetNTLMv2 hashes, with SMB server, relay, and…
 bee-san/ciphey
⚡ Automatically decrypt encryptions without knowing the key or cipher, decode encodings, and crack hashes ⚡
 neo23x0/loki
IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…
 theresafewconors/sooty
The SOC Analysts all-in-one CLI tool to automate and speed up workflow.
 nccgroup/redsnarf
RedSnarf is a pen-testing / red-teaming tool for Windows environments
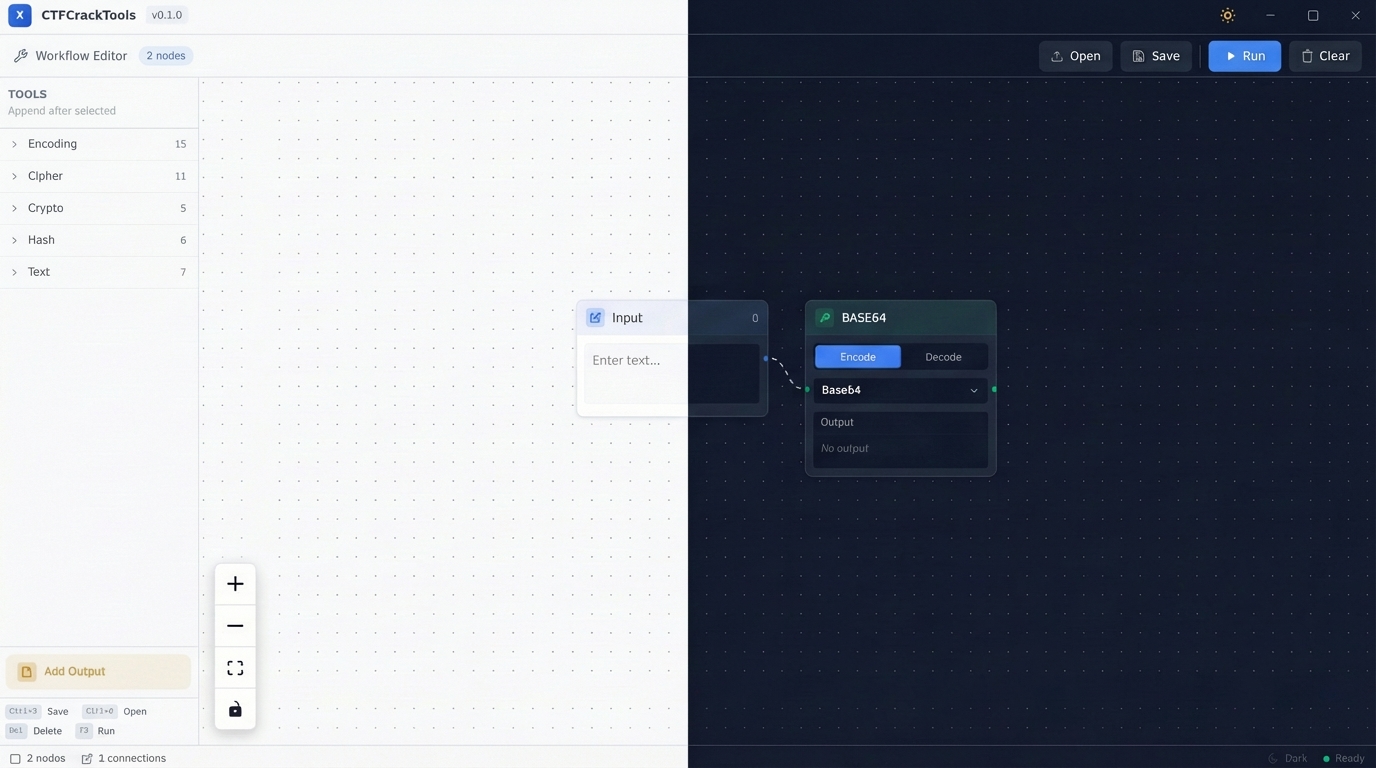 0chencc/ctfcracktools
The next-generation CTF Swiss Army Knife powered by Rust & Tauri. Features a visual node-based workflow and local AI intelligence for extreme…
 stanfrbd/cyberbro
A simple application that extracts your IoCs from garbage input and checks their reputation using multiple CTI services.

 davidbuchanan314/monomorph
MD5-Monomorphic Shellcode Packer - all payloads have the same MD5 hash
 bmaia/binwally
Binary and Directory tree comparison tool using Fuzzy Hashing