

unleashed-firmware
 darkflippers/unleashed-firmware
Custom firmware for Flipper Zero enabling Sub-GHz radio, NFC/RFID emulation, infrared, and BadUSB attack features for hardware security testing.
embedded-systems-securityfuzzinghardware-hacking+7
darkflippers/unleashed-firmwareCustom firmware for Flipper Zero enabling Sub-GHz radio, NFC/RFID emulation, infrared, and BadUSB attack features for hardware security testing.
 themalwareguardian/cve-2022-34302
Demonstrates CVE-2022-34302, a Secure Boot bypass via the New Horizon Datasys signed bootloader whose built-in custom PE/COFF loader executes…
 tnm/zclaw
Your personal AI assistant at all-in 888KiB (~35KB in app code). Running on an ESP32. GPIO, cron, custom tools, memory, and more.
 0xsamy/sweet-pineapple-builder
Build your own custom WiFi Pineapple Tetra firmware tailored to any based MIPS 24Kc architecture router. (WiFi Pineapple Tetra DIY)
 fahreddinaykut/sparkaltbatteryboard
Reverse-engineered I2C/SMBus battery interface board for DJI Spark, replacing OEM smart battery with standard 3S LiPo. Includes protocol analysis,…
 keowu/sjcam
Reverse engineering research and custom firmware for Allwinner V3-based IoT cameras, including firmware parsers, an AVIOCTRL client, and a…
 christophe.duvernois/usb-spy
Intercepts and analyzes USB Mass Storage traffic at the block and file level, emulates USB devices, and supports custom Python stubs for security…
 themalwareguardian/uefi-security-research-howyar-sysreturn-netcopy
Post CVE-2024-7344 analysis of Howyar SysReturn NetCopy - reverse engineering notes, vulnerable binaries, vendor correspondence, and proof-of-concept…
 gibmat/cve-2026-32606-poc
Proof-of-concept demonstrating bypass of TPM-bound LUKS disk encryption on Linux systems, extracting volume keys via custom root filesystem attack.
 oliviaholly/fusee-gelee
An implementation of the Fusee Gelee exploit (CVE-2018-6242) for the Nintendo Switch, along with a custom payload.
 leochen-coremind/vmpacker
ARM64 ELF Virtual Machine Protection System
 pietroborrello/customprocessingunit
The first analysis framework for CPU microcode
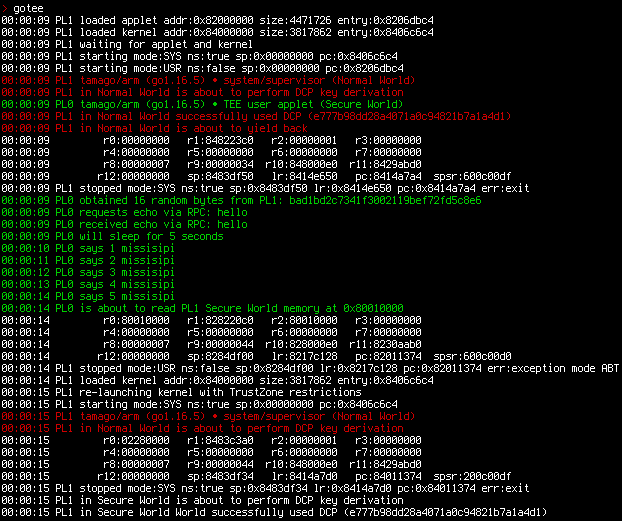 usbarmory/gotee
Go Trusted Execution Environment (TEE)
 nccgroup/the_automotive_threat_modeling_template
NCC Group Template for the Microsoft Threat Modeling Tool 2016 for Automotive Security
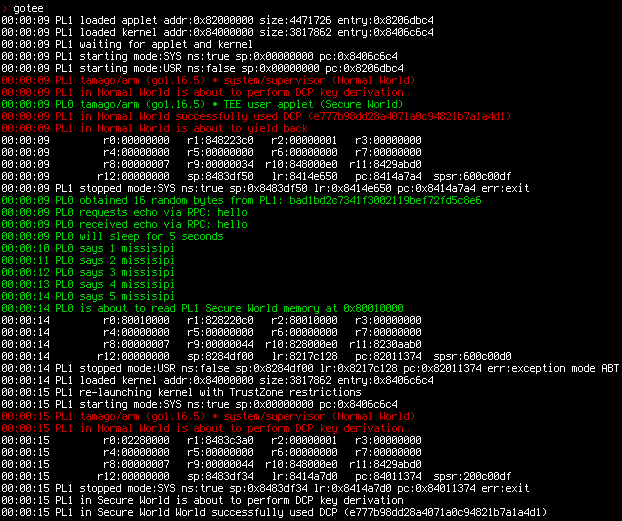 usbarmory/gotee-example
GoTEE - example application
 thegammasqueeze/bootloader_unlock_anbernic_t820
Bootloader unlock using CVE-2022-38694 for Anbernic Unisoc T820 devices
 themalwareguardian/cve-2026-79298
Research repository documenting CVE-2026-79298, an incomplete UEFI Secure Boot bypass remediation in Howyar SysReturn's IA-32 boot path, with reverse…
 freax13/cve-2023-20573-poc
Proof-of-concept demonstrating CVE-2023-20573: a hardware vulnerability in AMD SEV-SNP that allows exception reinjection suppression in KVM, enabling…