


 ox1111/cve-2022-32932
Technical analysis and proof-of-concept for CVE-2022-32932, a double fetch vulnerability in Apple's ANE kernel driver leading to out-of-bounds write…
 engrbilal992/deaddialect
A session-unique RISC-V ISA — every boot speaks a different dialect. Old binaries become invalid. Malware cannot persist.
 mytechnotalent/reverse-engineering
A FREE comprehensive reverse engineering tutorial covering x86, x64, 32-bit/64-bit ARM, 8-bit AVR and 32-bit RISC-V architectures.
 nfcgate/nfcgate
An NFC research toolkit application for Android
 cecio/usbvalve
Expose USB activity on the fly
 yasindce1998/barzakh
Ring -4 to Ring 0: offense-defense firmware research platform. We build the bootkits, then we catch them. Closed-loop. Zero trust in silicon.

 xe1phix/parrotlinux-public-kiosk-project
Systematic Linux kernel hardening project implementing KSPP-recommended settings, module blacklisting, and restricted environment configuration for…
 cecio/xenoboxx
Hardware Sandbox Toolkit
 aperikube/pwn-arm-nfc
ARM buffer overflow challenge exploiting NFC tag input on Raspberry Pi. Includes hardware assembly guide, server code, and flag retrieval for CTF and…
 h4rk3nz0/cve-2024-3912
Asus Router Arbitrary File Write to Remote Code Execution PoC - Fk Mirai

 qemu/qemu
Official QEMU mirror. Please see https://www.qemu.org/contribute/ for how to submit changes to QEMU. Pull Requests are disabled. Please only use…
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy


 gmh5225/awesome-game-security
Curated index of game security research: anti-cheat internals, DMA attacks, reverse engineering, kernel/mobile protections, and graphics API hooking…
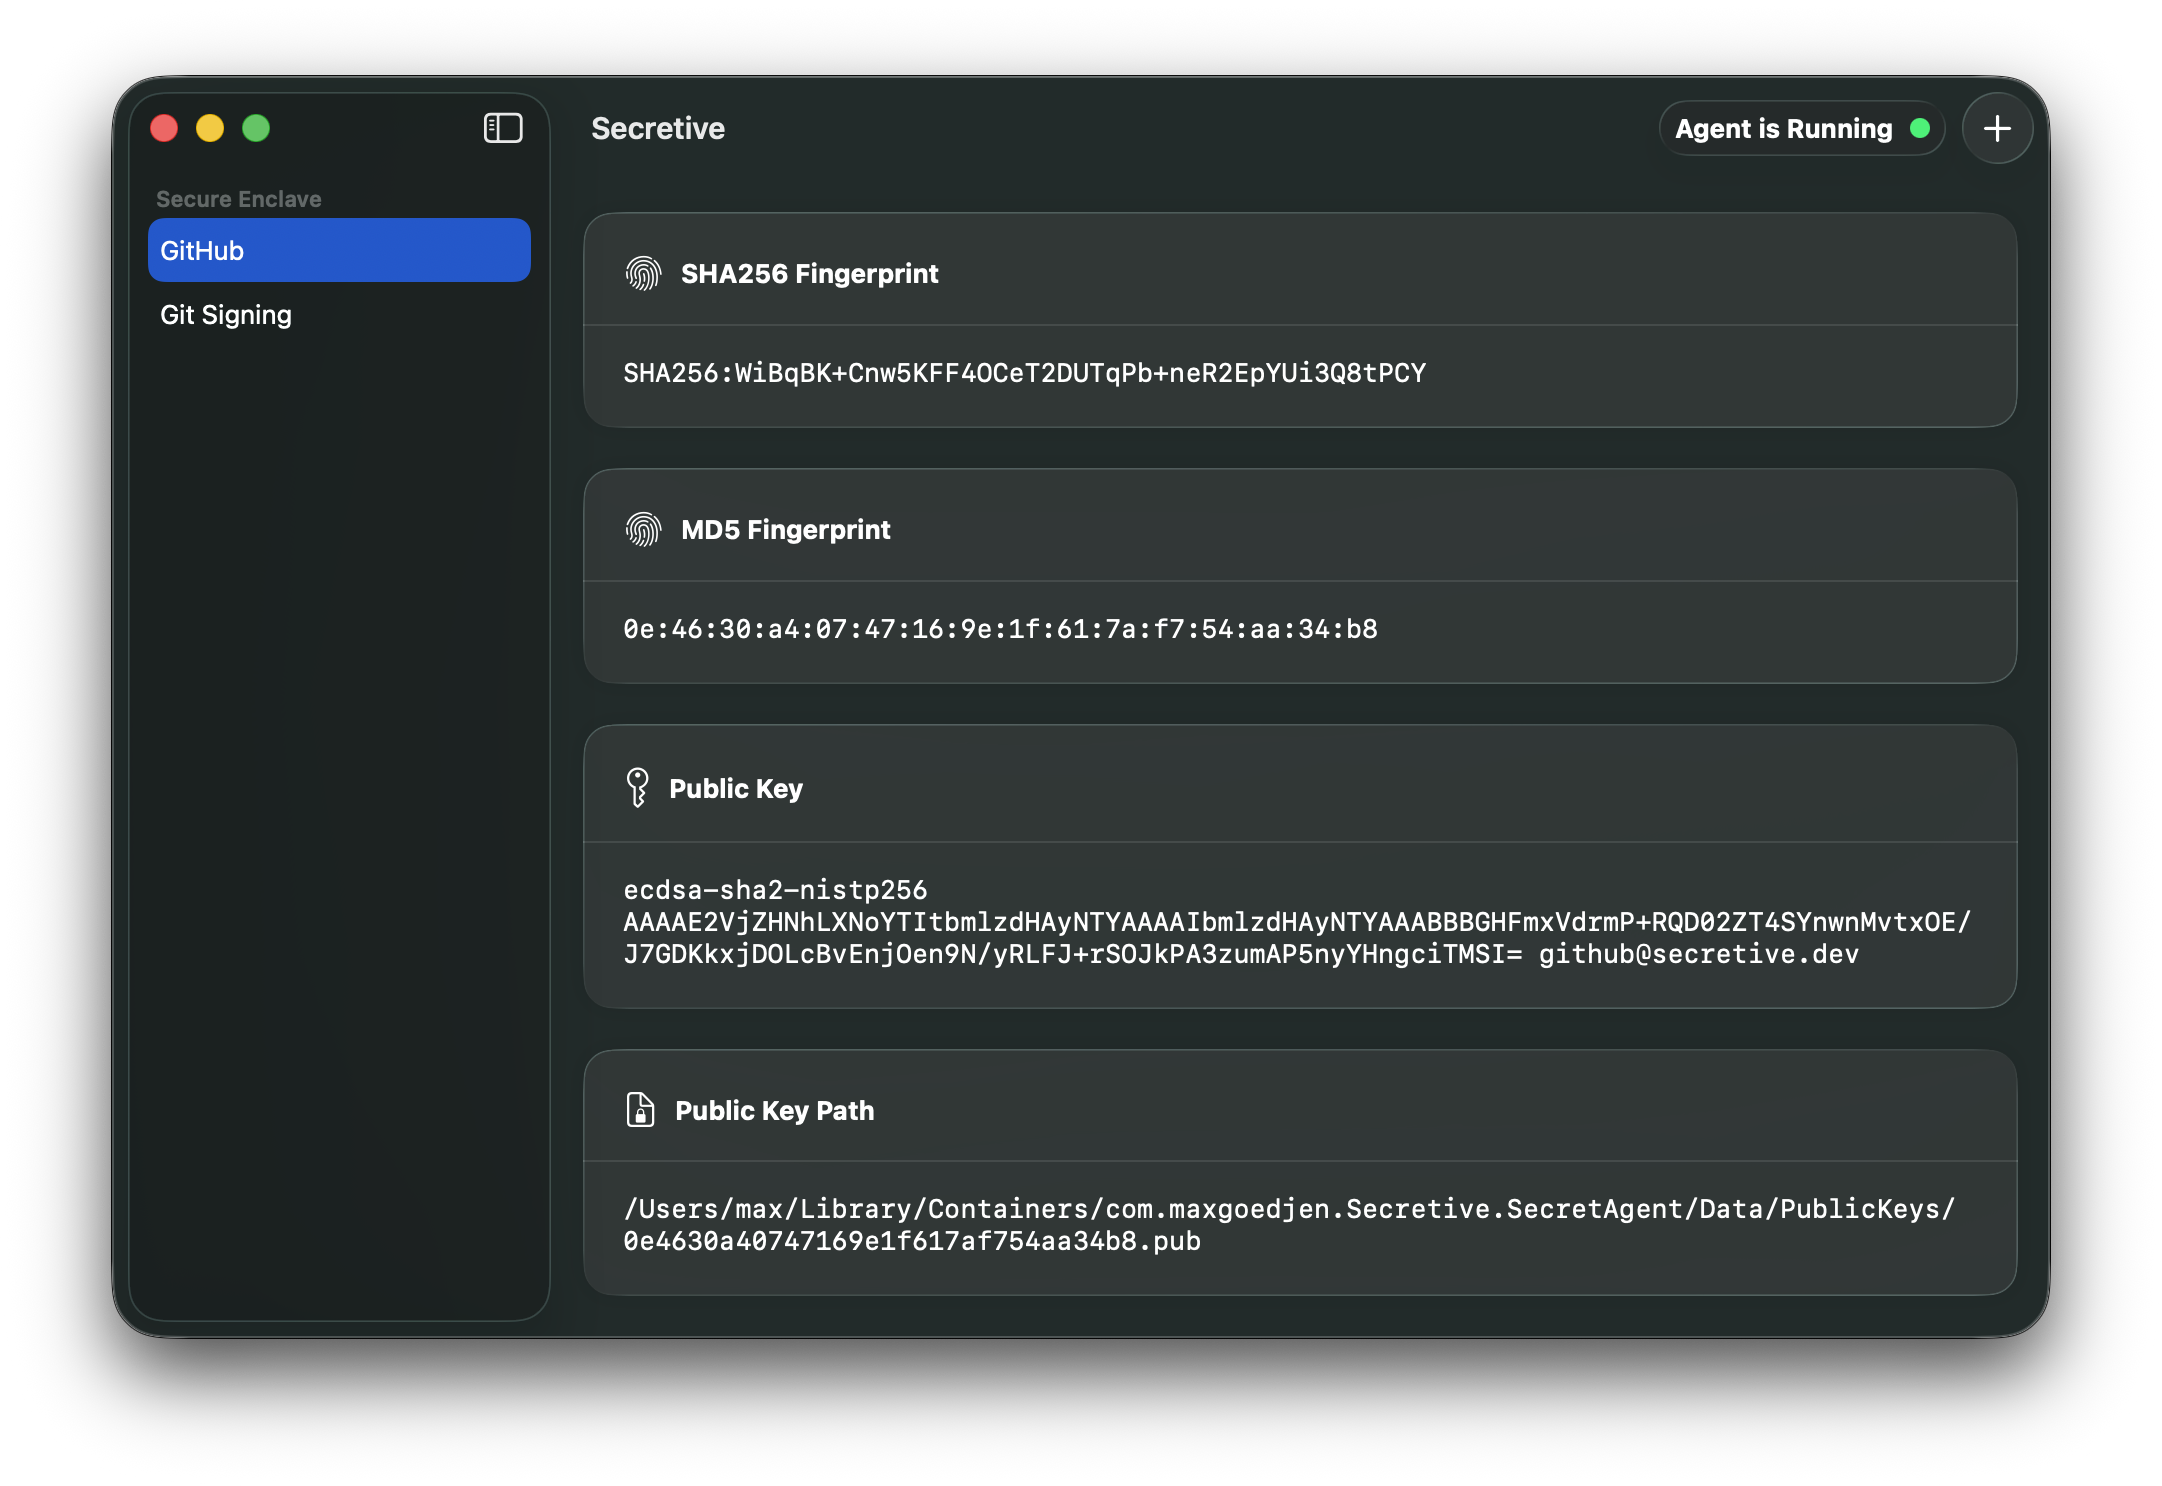 maxgoedjen/secretive
Protect your SSH keys with your Mac's Secure Enclave