bitlocker-bypass-research

BitLocker full-disk encryption bypass research using CVE-2023-21563 (BitPixie). Methodology, exploit chain, and defensive recommendations.

BitLocker full-disk encryption bypass research using CVE-2023-21563 (BitPixie). Methodology, exploit chain, and defensive recommendations.

Proof-of-concept demonstrating a firmware signature verification bypass in Phison S11 SSDs, allowing attackers to re-sign modified firmware by…

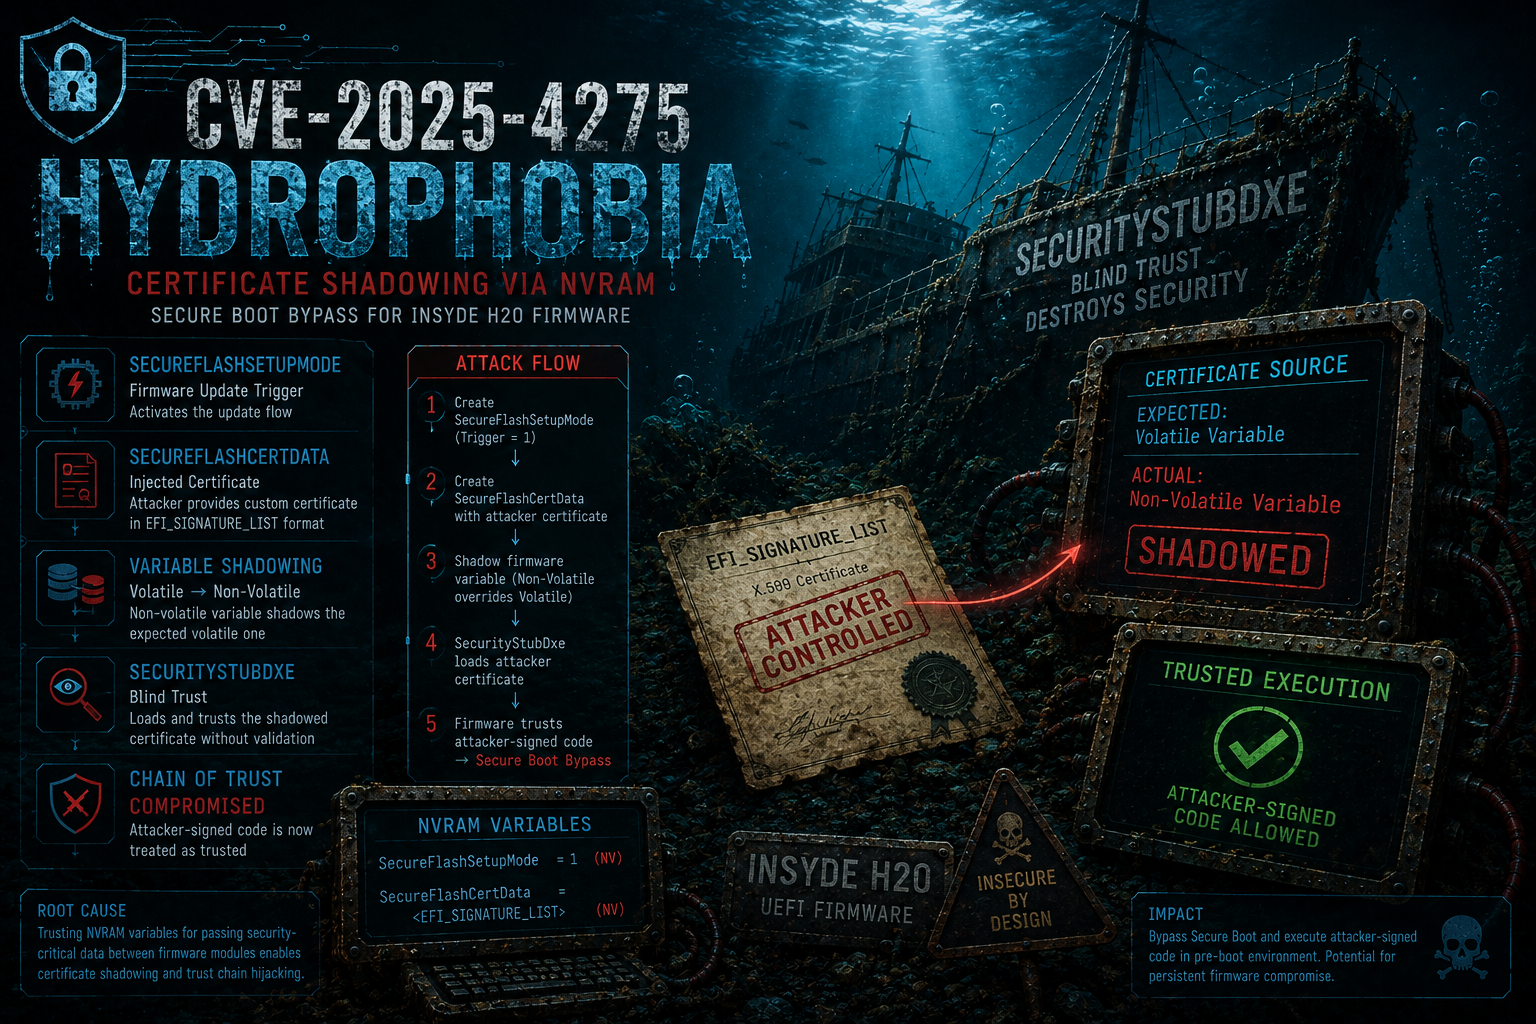
Analysis and exploitation of CVE-2025-4275 (Hydr0ph0bia), a Secure Boot trust-chain weakness where firmware variables are used to introduce…


Speculative Load Hazards Boost Rowhammer and Cache Attacks - CVE-2019-0162 -

Sources of Synacktiv's challenge for leHack 2026

对NETIS WF2409E路由器进行的一次完整硬件安全分析研究。通过对设备进行拆解分析、调试接口识别、固件提取等工作,记录了硬件分析的全过程、漏洞细节以及相应的安全建议,希望能帮助提高物联网设备的安全性。

Conceptual PoC for CVE-2025-54328, a critical zero-click stack buffer overflow in Samsung Exynos baseband firmware's SMS RP-DATA parser, enabling…

CVE Realtek SD card reader. CVE-2022-25477, CVE-2022-25478, CVE-2022-25479, CVE-2022-25480, CVE-2024-40432, CVE-2024-40431

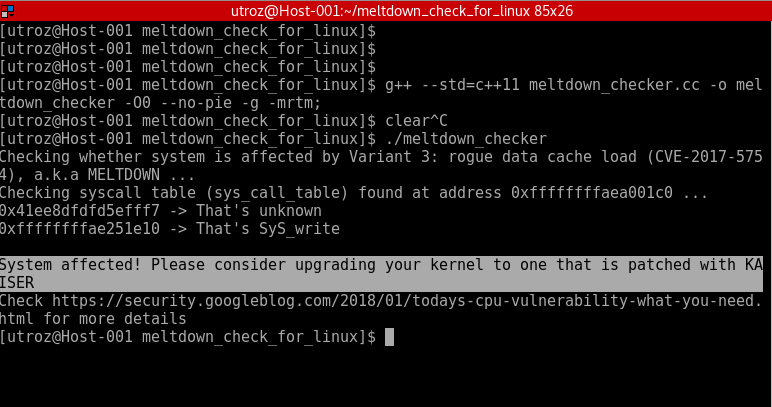
Proof-of-concept / Exploit / checks whether system is affected by Variant 3: rogue data cache load (CVE-2017-5754), a.k.a

Research and hands-on PoC of Spectre Variant 2 (CVE-2017-5715), a hardware side-channel vulnerability exploiting CPU speculative execution and branch…

GNU Radio out-of-tree (OOT) module for QRadioLink blocks.

Research on a temporal coherence vulnerability in Apple Silicon M-series chips, exploiting golden ratio harmonic clock frequencies to potentially…

Stack buffer overflow during cmdline parsing

ARM buffer overflow challenge exploiting NFC tag input on Raspberry Pi. Includes hardware assembly guide, server code, and flag retrieval for CTF and…

AVX-Based Timing Side Channel — ASLR Detection


Buffer Overflow Attack and Prevention for an FPGA Based Soft-Processor System - 7th International Conference on Innovation in Electronics and…