
draytek-arsenal
 infobyte/draytek-arsenal
Reverse Engineering and Observability toolkit for Draytek firewalls
binary-analysisembedded-systems-securityfirmware-analysis+5
54
infobyte/draytek-arsenalReverse Engineering and Observability toolkit for Draytek firewalls

 shinyquagsire23/cve-2020-12753-poc
A proof-of-concept for CVE-2020-12753
 0xsamy/sweet-pineapple-builder
Build your own custom WiFi Pineapple Tetra firmware tailored to any based MIPS 24Kc architecture router. (WiFi Pineapple Tetra DIY)
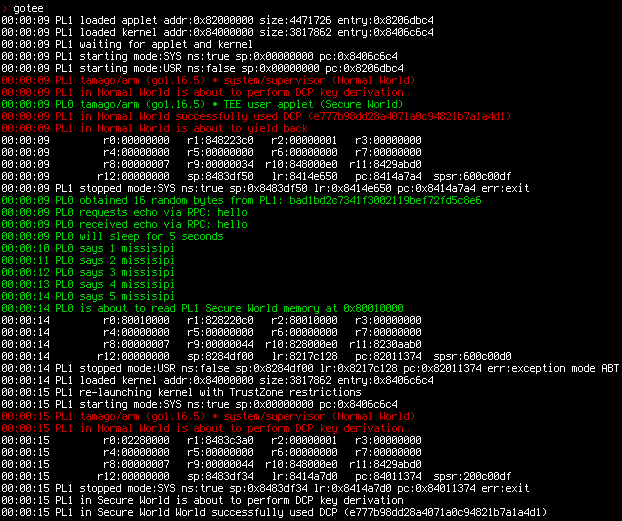 usbarmory/gotee-example
GoTEE - example application
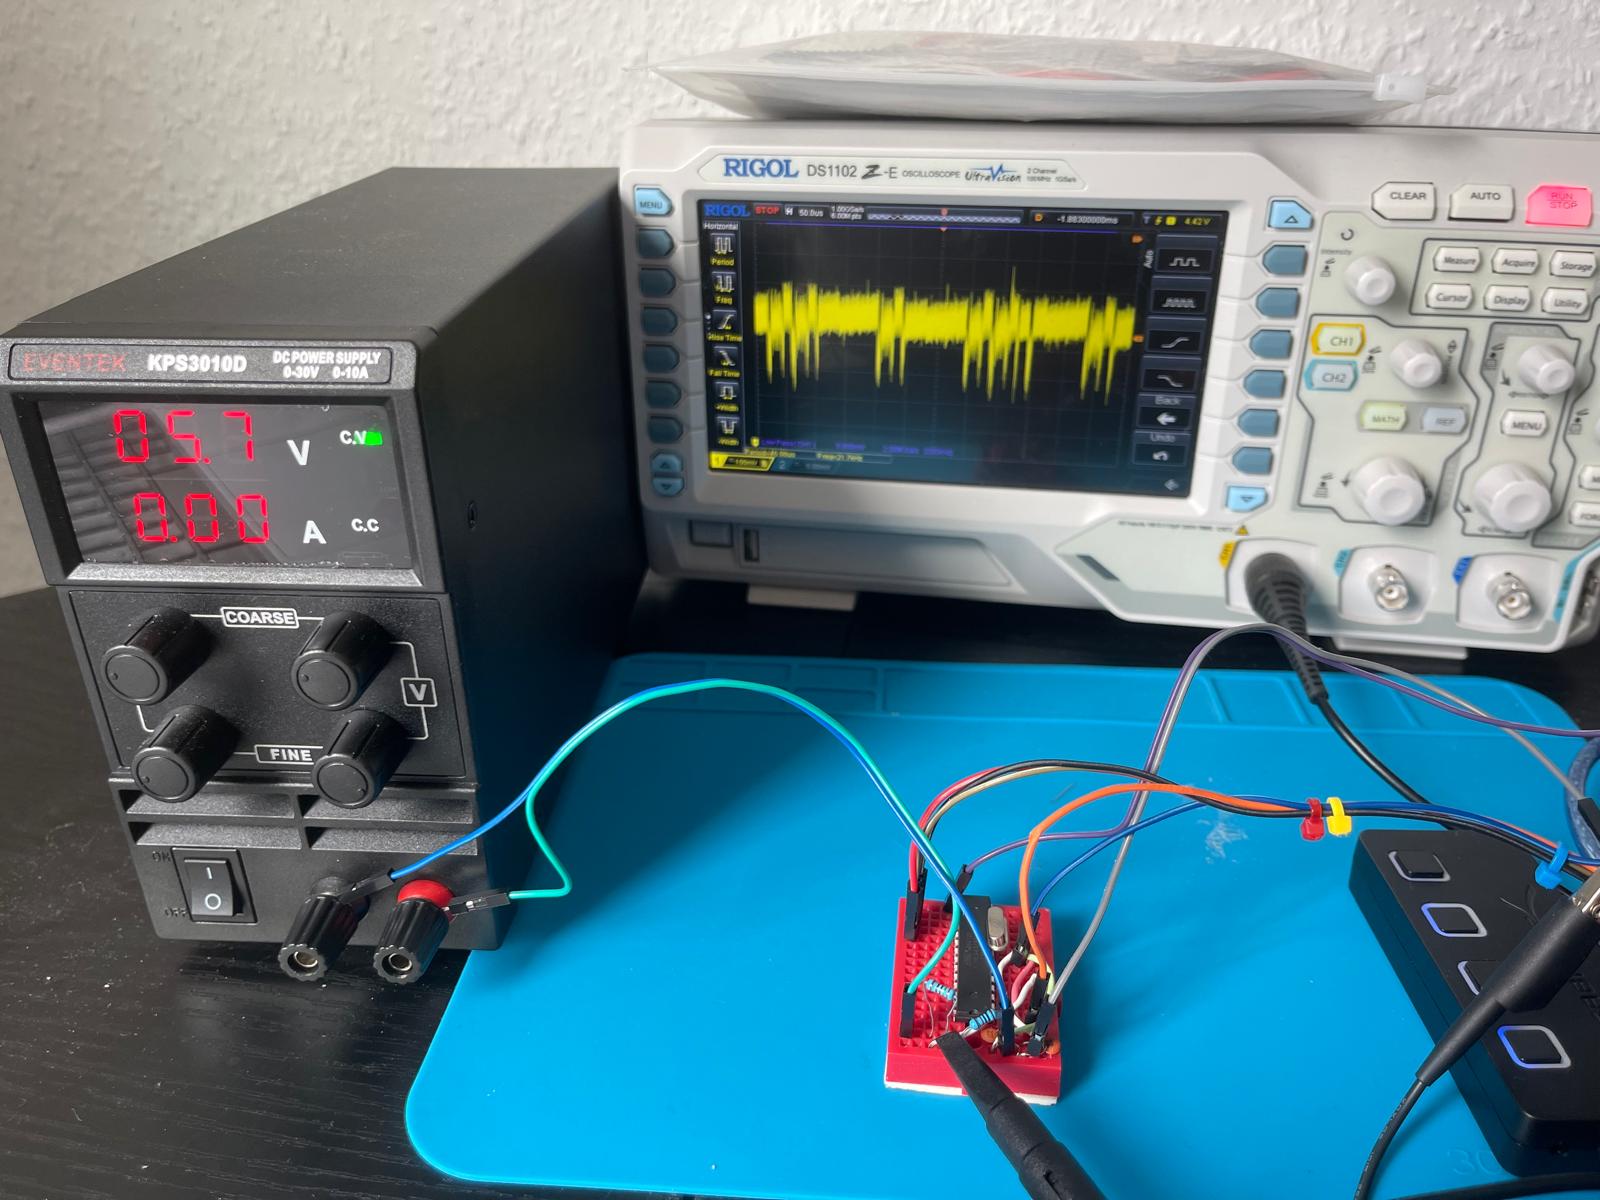 lord-feistel/power_analysis
Proof-of-concept demonstrating a power analysis side-channel attack against a vulnerable RSA implementation on Arduino (Atmega328P), with detailed…
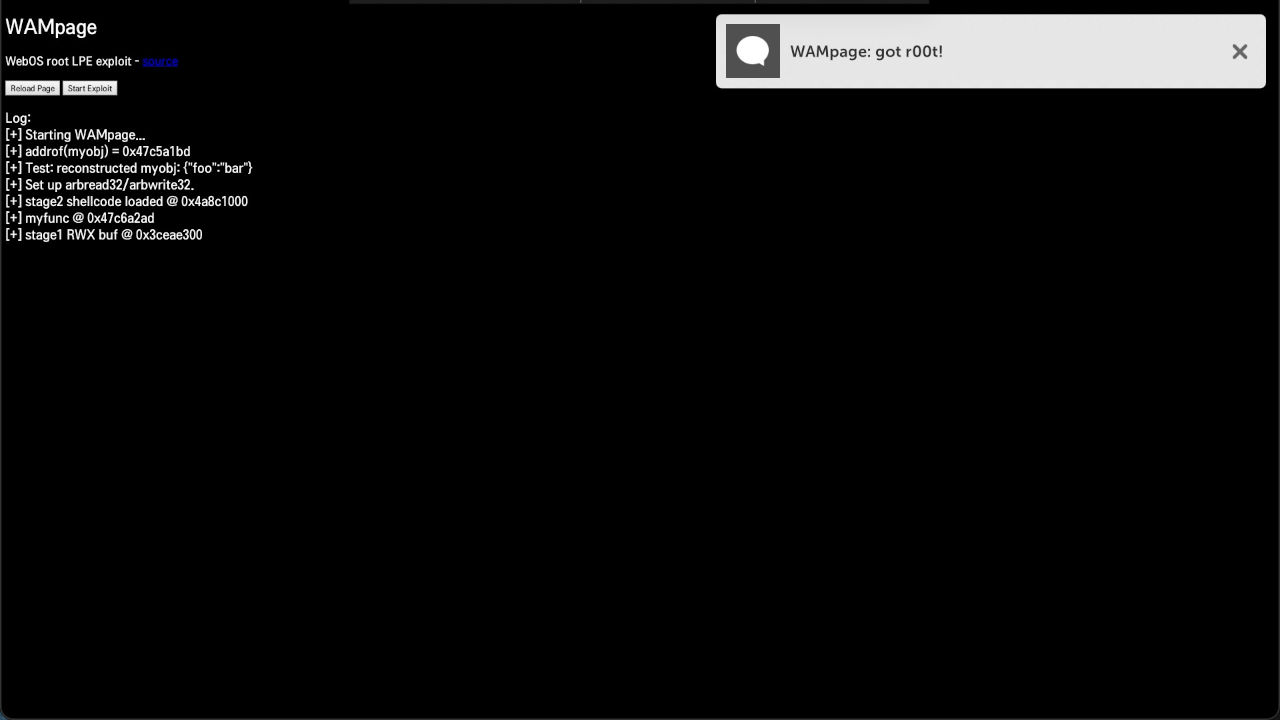 davidbuchanan314/wampage
WAMpage - A WebOS root LPE exploit chain (CVE-2022-23731)
 cunninglogic/pixeldump_cve-2016-8462
Pixel bootlaoder exploit for reading flash storage
 synacktiv/yealink_tools
Reverse engineering scripts designed for extracting Yealink VOIP upgrade files
 geeoon/fault-injection-finder
Automatically find and execute fault injection attacks
 userlandkernel/usbusted
Research on Apple's USB protocols
 embedi/smm_usbrt_poc
CVE-2017-5721 Proof-of-Concept
 ntgabrielgomes/cve-2023-20564
Proof-of-concept exploit for CVE-2023-20564 demonstrating arbitrary physical memory read/write via AMD Ryzen Master Driver IOCTL handlers, enabling…
 r3n3r0/cve-2026-20700
PoC demonstrating dyld as a PAC signing oracle via hand-crafted Mach-O chained fixups on arm64e, achieving controlled PAC-valid pointer writes and…
 416rehman/asus-bsitf-0-day-poc
PoC for CVE-2026-13585
 szymonh/inspector-gadget
CVE-2021-39685 Description and sample exploit for Linux USB Gadget overflow vulnerability
 dest-3/cve-2023-46012
LINKSYS AC1900 EA7500v3 IGD UPnP Stack Buffer Overflow Remote Code Execution Vulnerability
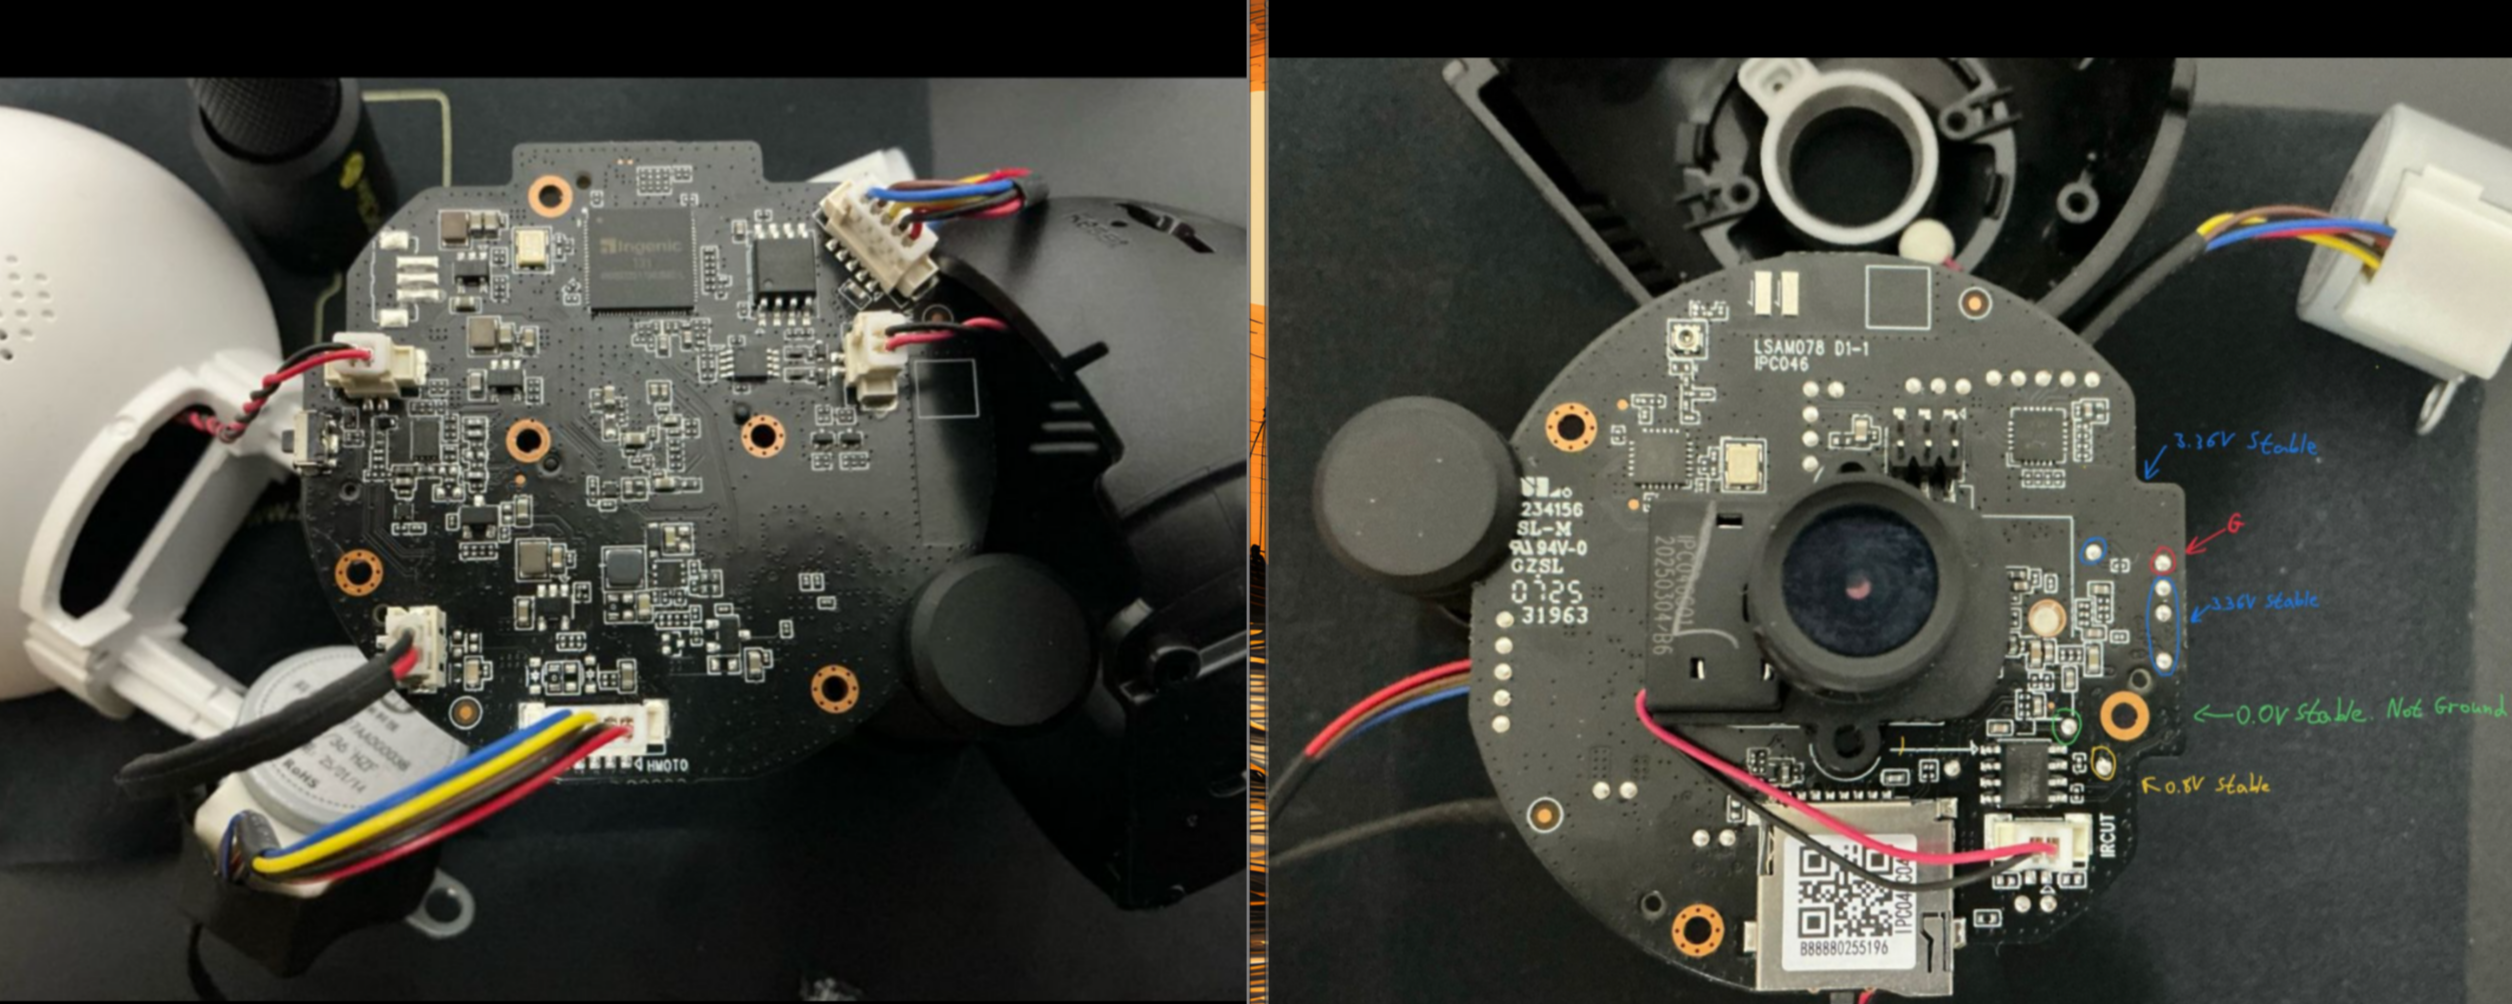 h3xdum/xiaomi-c200-firmware-analysis
From UART to Root: Breaking Into the Xiaomi C200 via U-Boot