

spidump
 wrongbaud/spidump
Tool for reconstructing SPI flash images via logic analyzer captures
digital-forensicsembedded-systems-securityfirmware-analysis+7
46 days ago
wrongbaud/spidumpTool for reconstructing SPI flash images via logic analyzer captures
 yellowkeybitlocker-cve/yellowkey-bitlocker-cve-2026-45585
YellowKey BitLocker recovery audits CVE-2026-45585: yellowkey github, TPM, recovery key backup. Windows 10/11 CLI GUI, portable audit tool for…

 renich/genclave
Centralized, TPM 2.0 hardware-backed cryptographic identity enclave and multi-protocol bridge for Linux (FIDO2/CTAP2 WebAuthn Passkeys, OpenSSH…
 egorrsp/cve-2020-15368-asrdrv103-research
Reverse engineering research of ASRock AsrDrv103.sys (CVE-2020-15368), covering its driver interface, encrypted request protocol, and privileged…
 pentoo/pentoo-overlay
Gentoo overlay for security tools as well as the heart of the Pentoo Livecd
 jiegec/loongbleed
Proof-of-concept demonstrating a microarchitectural data leak in Loongson LA464/LA664 processors via undefined upper bits of LASX vector registers,…
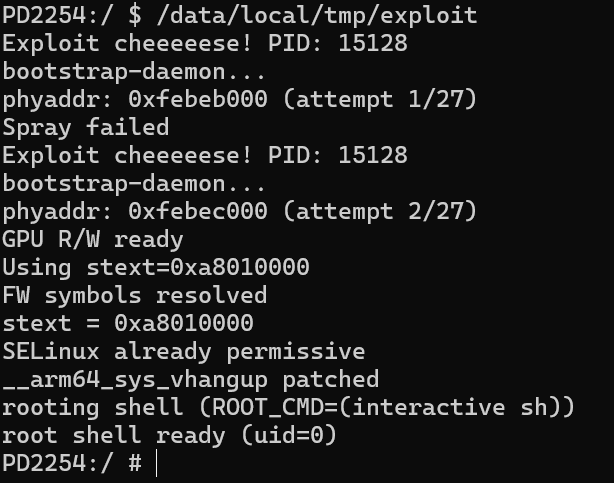 xianwan1314/cve-2025-21479-iqoo11pro
CVE-2025-21479 (Qualcomm Adreno GPU) reproduction notes for vivo iQOO 11 Pro (PD2254) - authorized research
 ramenfast/zenfone9-root
Temporary root (uid 0) on a bootloader-locked ASUS Zenfone 9 via CVE-2025-21479 + a perf-based physical-address leak. GPLv3.
 wqsv/throttlestoppoc
CVE-2025-7771: Arbitrary physical memory and I/O port read/write via ThrottleStop driver
 bmax121/kernelpatch
Patching and hooking the Linux kernel with only a stripped Linux kernel image.
 eiln/ane
Reverse engineered Linux kernel driver and userspace library for the Apple Neural Engine (ANE), enabling hardware access and analysis on Linux…
 themalwareguardian/cve-2022-34301
Demonstrates CVE-2022-34301 Secure Boot bypass via Eurosoft signed UEFI Shell (esdiags.efi), using the mm command to nullify gSecurity2 and load…
 themalwareguardian/cve-2022-34302
Demonstrates CVE-2022-34302, a Secure Boot bypass via the New Horizon Datasys signed bootloader whose built-in custom PE/COFF loader executes…
 themalwareguardian/cve-2022-34303
Demonstrates CVE-2022-34303 Secure Boot bypass via CryptoPro signed UEFI Shell, using the mm command to nullify gSecurity2 and load unsigned UEFI…
 gmh5225/disk-spoofer
Kernel driver based disk size and sector query spoofing program, can evade Windows WMIC query.
 gmh5225/driver-hwid-btbd-modified
Modified btbd HWID spoofer kernel driver that can be manually mapped to evade anti-cheat detection on Windows 1909.
 abdul-kalam2000/retbleed-speculative-execution-poc
Reproduction of the Retbleed (CVE-2022-29900/29901) micro-architectural attack in gem5. RSB underflow, Flush+Reload side-channel leak, and a verified…
 themalwareguardian/cve-2026-79298
Research repository documenting CVE-2026-79298, an incomplete UEFI Secure Boot bypass remediation in Howyar SysReturn's IA-32 boot path, with reverse…