
cheese
 zhuowei/cheese
CVE-2025-21479 proof-of-concept, I think
android-securitybinary-exploitationembedded-systems-security+7
zhuowei/cheeseCVE-2025-21479 proof-of-concept, I think
 kristof-mattei/gardyn-hack
CVE-2025-29628, CVE-2025-29629, CVE-2025-29630, CVE-2025-29631
 jgoyd/ios-attack-chain-cve-2025-31200-cve-2025-31201
CVE-2025-31200 is a zero-day, zero-click RCE in iOS CoreAudio’s AudioConverterService, triggered by a malicious audio file via iMessage/SMS.…
 tobss8/gigabyte-h510m-k-v2-bios-smm-reverse-engineering-cve-2025-7026-7027-7028-7029-research
Static reverse-engineering of a GIGABYTE H510M K V2 (`H510MKV2.F3`) BIOS image: full UEFI firmware-volume extraction analysis of the PI-spec SMM Core…
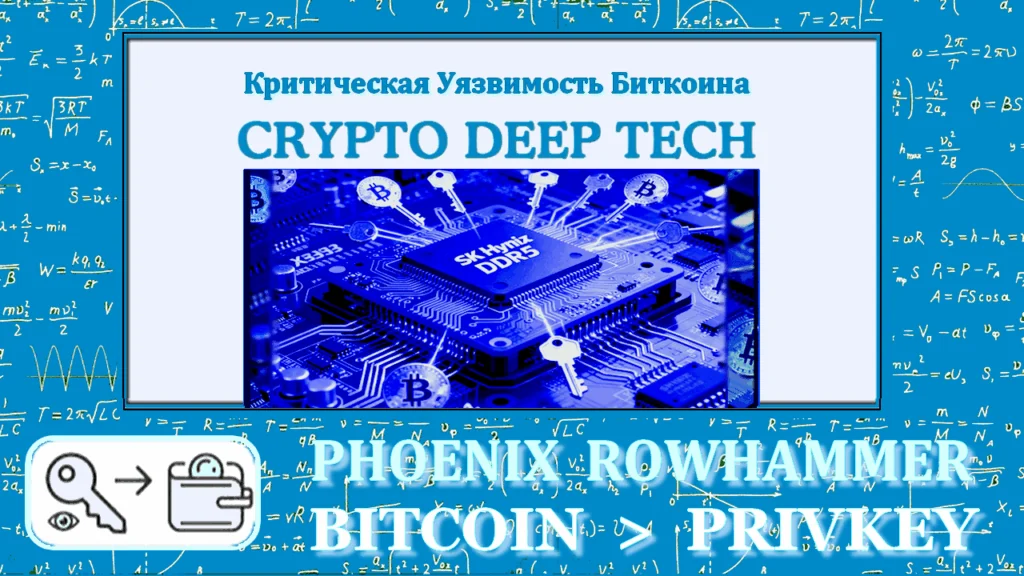 demining/phoenix-rowhammer-attack-cve-2025-6202
Phoenix Rowhammer Attack: Systemic Risk of Bitcoin Wallet Private Key Compromise in Global Blockchain Infrastructure Due to a Critical SK Hynix DDR5…
 themalwareguardian/cve-2025-4275
Analysis and exploitation of CVE-2025-4275 (Hydr0ph0bia), a Secure Boot trust-chain weakness where firmware variables are used to introduce…
 mselbrede/gardyn
CVE-2025-29628, CVE-2025-29629, CVE-2025-29630, CVE-2025-29631
 abhijithaj/dorset_smartlock_vulnerability
This repository is for Dorset_SmartLock_vulnerability. CVE-2025-25650 is suggested by MITRE which is yet to confirm.
 veereshgadige/aziot-cctv-cve-2025-50777
CVE-2025-50777: Root Access and Plaintext Credential Exposure in AZIOT Smart CCTV
 masjadaan/cve-2025-29338
Technical advisory and proof-of-concept for a stack-based buffer overflow (CWE-121) in the NXP moal.ko Wi-Fi kernel driver, enabling local kernel…
 analyticeth/chronomaly-webos
CVE-2025-38352 kernel exploit for LG webOS Smart TVs (ARM64). Achieves persistent root on real consumer hardware with novel exploitation techniques.…
 zgsnj123/cve-2025-45467
Proof-of-concept exploit for CVE-2025-45467, demonstrating remote code execution on Unitree Go1 robotic dogs via insecure MD5-based firmware…
 goldenticketlabs/cve-2025-52413
repo for CVE-2025-52413
 yashodhanvivek/agatsa-easytouch-plus---cve-2025-56019
This report is for CVE-2025-56019 reserved for Easytouch+product for BLE authentication vulnerability assigned to Discoverer Yashodhan Vivek Mandke.…
 hunt-benito/samsung-exynos-sms-stack-overflow-cve-2025-54328-critical-zero-click-baseband-rce
Conceptual PoC for CVE-2025-54328, a critical zero-click stack buffer overflow in Samsung Exynos baseband firmware's SMS RP-DATA parser, enabling…
 c-sprinks/bitlocker-bypass-research
BitLocker full-disk encryption bypass research using CVE-2023-21563 (BitPixie). Methodology, exploit chain, and defensive recommendations.
 jdbonfils/poc_cve-2025-48507
Proof of Concept of CVE-2025-48507. The security flaw can be leveraged by Non-Secure software (e.g., Linux) to break Trust Zone and gain access to…