CVE-2025-69821-Beat-XP-Vega-Smartwatch-Security-Assessment

A security assessment of the Beat XP VEGA Smartwatch (Firmware RB303ATV006229) focused on Bluetooth Low Energy (BLE) connectivity revealed a design…

A security assessment of the Beat XP VEGA Smartwatch (Firmware RB303ATV006229) focused on Bluetooth Low Energy (BLE) connectivity revealed a design…

Detailed CVE-2026-8697 writeup with POC exploit for a login rate-limit bypass on TP-Link Archer C64 routers via a debug SSH service, enabling…

Proof-of-concept exploit for iOS Bluetooth stack vulnerabilities CVE-2018-4327 and CVE-2018-4330, enabling ARM PC register control on iPhone 6S via…

Documentation of CVE-2025-51643: physical SPI flash extraction on Meitrack T366G-L GPS tracker enabling firmware dump, plaintext credential…

This vulnerability impacts device availability and reliable operation of Atomberg Erica Smart Fan(Firmware Version 1.0.36). The issue arises due to a…

CAWODOG is a proof-of-concept project demonstrating how to protect Python-based AI models deployed on offline industrial machines. Across three…

Kankun Smart Socket Hijacker and Sniffer. The kankun smart socket and its mobile app use a hardcoded AES 256 bit key to encrypt and decrypt…

Simulates a Bluetooth keyboard to exploit CVE-2023-45866, injecting keystrokes via DuckyScript on vulnerable Android, iOS, macOS, and Linux devices…

Remote Code Execution (RCE) proof of concept on a enphase solar inverter

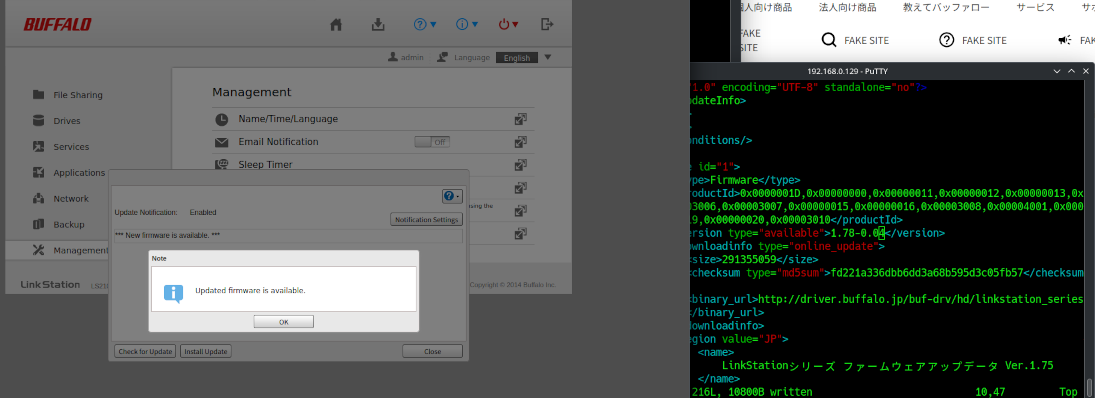
Firmware Update Server Verification Vulnerability on Buffalo LS210D Version 1.78-0.03

Proof-of-concept exploit for CVE-2024-27619 causing denial of service on D-Link DIR-3040/3060 routers via FTP memory exhaustion without…

Single Go binary for Bluetooth Low Energy security testing on Linux/BlueZ: scan, enumerate GATT, read/write/notify, fuzz characteristics, and run…

iPhone 11 emulated on QEMU

PS5 Exploit Web Server on a Raspberry Pi Powered by the PS5's USB Port

Proof of concept for arbitrary OS command execution on Guangzhou/V-SOL 1GE ONU devices (CVE-2020-8958)

APOLOGEE is a Python script and Metasploit module that enumerates a hidden directory on Siemens APOGEE PXC BACnet Automation Controllers (all…

Proof-of-concept exploit for CVE-2026-1668 in TP-Link switch firmware, delivering a MIPS payload that yields a root shell on vulnerable devices.

Unauthenticated arbitrary file upload on Honeywell PD45 web admin (firmware F10.19.010040–before F10.22.030745) leading to RCE. Python check/exploit…