
pyFlipper
 wh00hw/pyflipper
Flipper Zero Python CLI Wrapper
bluetooth-securityhardware-hackinghardware-iot-security+6
442
wh00hw/pyflipperFlipper Zero Python CLI Wrapper
 rebilibin/ghostlock-oppo-watch3pro
Complete exploit research for CVE-2026-43499 (GhostLock) on OPPO Watch 3 Pro, including kernel UAF analysis, disassembly, and exploit chain…
 redzrush101/zte-blade-v40-vita-unlock
Unlocking the ZTE Blade V40 Vita (P606F02 / Unisoc UMS9230 / UFS) bootloader via CVE-2022-38694 - Linux scripts, the FBE post-unlock hang fix, and…
 w00t3k/awesome-cellular-hacking
Awesome-Cellular-Hacking
 rfidresearchgroup/proxmark3
Hardware tool for RFID analysis, emulation, and penetration testing. Supports 125kHz, 13.56MHz protocols (MIFARE, iClass, ISO14443/15693) with key…
 secluso/core
A privacy-preserving Raspberry Pi home security camera that uses advanced end-to-end encryption.
 furrtek/precir
Open-source hardware and software toolkit for reverse-engineering and communicating with infrared-based electronic shelf labels. Includes custom…
 owasp/iot-security-verification-standard-isvs
OWASP IoT Security Verification Standard (ISVS)
 nccgroup/ble-replay
BLE-Replay is a Bluetooth Low Energy (BLE) peripheral assessment tool
 seemoo-lab/fitness-app
BLE-based Fitbit research tool for authentication replay, encrypted activity dump decryption, memory/firmware extraction, and custom firmware…
 omerporze/brokentooth
POC for CVE-2018-4327
 alkersan/om-research
Documenting Osmo Mobile BLE protocol
 e-gleba/world_conqueror_4_ru
Translated strings for World Conqueror 4 (RU)
 zhubaohe123/ghostlock-kit
One-click root kit for vivo iQOO Neo9S Pro (MT6989) exploiting CVE-2026-43499 futex PI UAF via MCAST transport, with scripts and analysis docs.
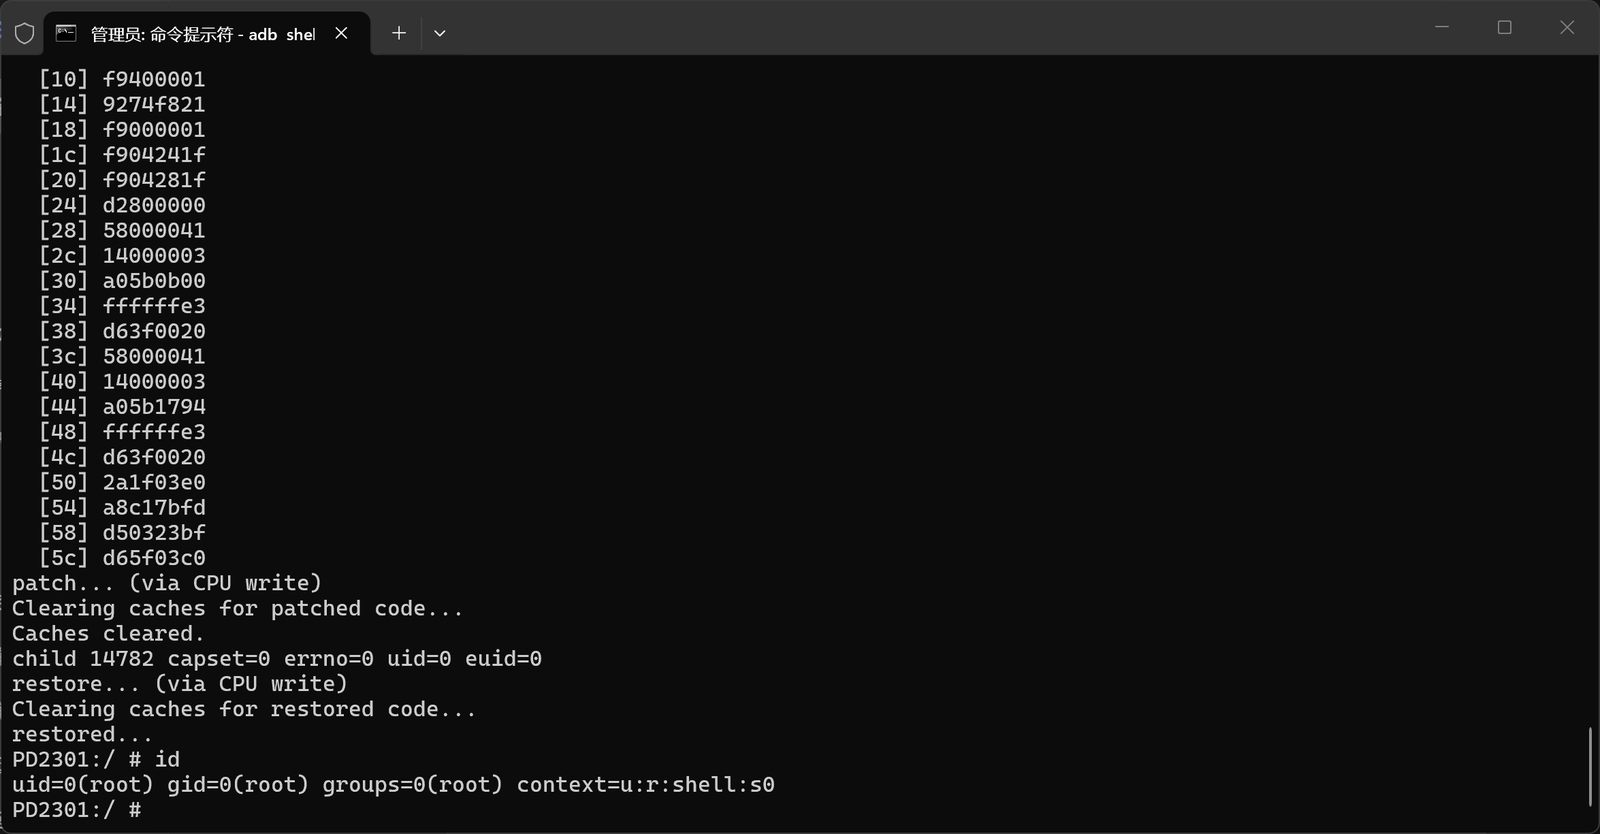 qingizi7/cve-2025-21479_iqooneo8
Local root exploit for CVE-2025-21479 (Adreno KGSL) on iQOO Neo8 (SM8475) - physical memory r/w, disables SELinux, spawns root shell
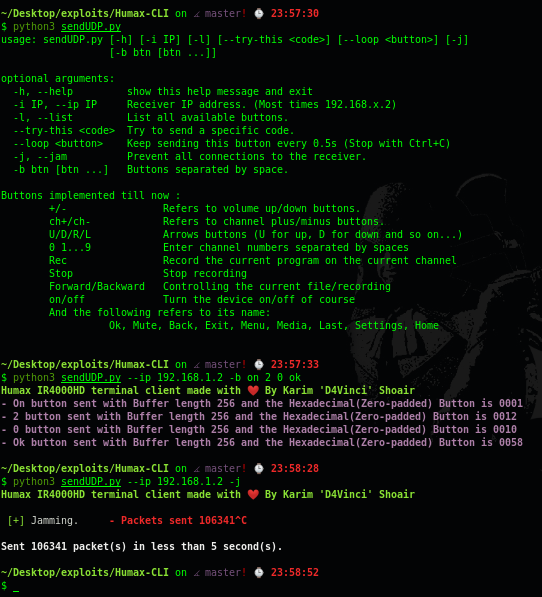 d4vinci/humax-cli
An unofficial Humax IR4000HD terminal client with enhanced features.
 joshuapassos/cmf-watch-pro-2-ble-protocol
Reverse-engineered BLE protocol for the CMF Watch Pro 2, documenting GATT layout, AES-128-CBC encrypted command frames, authentication handshake, and…
 alk601/root-my-galaxy
KSU installer for supported Samsung Galaxy firmware with CVE-2026-43499