cve-2026-43499-firetv-sheldonp-writeup

Security research write-up on exploiting CVE-2026-43499 on the Amazon Fire TV Stick 3rd Gen (sheldonp), from temporary root to bootloader unlock.

Security research write-up on exploiting CVE-2026-43499 on the Amazon Fire TV Stick 3rd Gen (sheldonp), from temporary root to bootloader unlock.

One-click root kit for vivo iQOO Neo9S Pro (MT6989) exploiting CVE-2026-43499 futex PI UAF via MCAST transport, with scripts and analysis docs.

A collection of vulnerabilities & exploits against modern GCS

PoC skeleton for CVE-2021-28664, a Mali kbase GPU driver use-after-free, demonstrating a kernel arbitrary physical memory read/write primitive on…

Reverse engineered Linux kernel driver and userspace library for the Apple Neural Engine (ANE), enabling hardware access and analysis on Linux…

Technical writeup analyzing CVE-2024-20154, a stack-based buffer overflow in MediaTek MT6769 NB-IoT baseband firmware, covering reverse engineering…

Firmware-specific temporary root exploit for Toshiba/Amazon Fire TV (hazel) using CVE-2026-43499. Implements ARM32 futex-PI UAF, kernel address leak,…

Ghidra plugin that automates UEFI firmware analysis by identifying known GUIDs, protocols, SMI handlers, and interrupt functions, with headless…

rt26cx21x64.sys exploit (Realtek PCIe GbE/2.5GbE/5GbE family)

Security research on a consumer IP camera built on the Fullhan FH8626V100 SoC (model AJL30PG0803).

Simulates a Bluetooth keyboard to exploit CVE-2023-45866, injecting keystrokes via DuckyScript on vulnerable Android, iOS, macOS, and Linux devices…

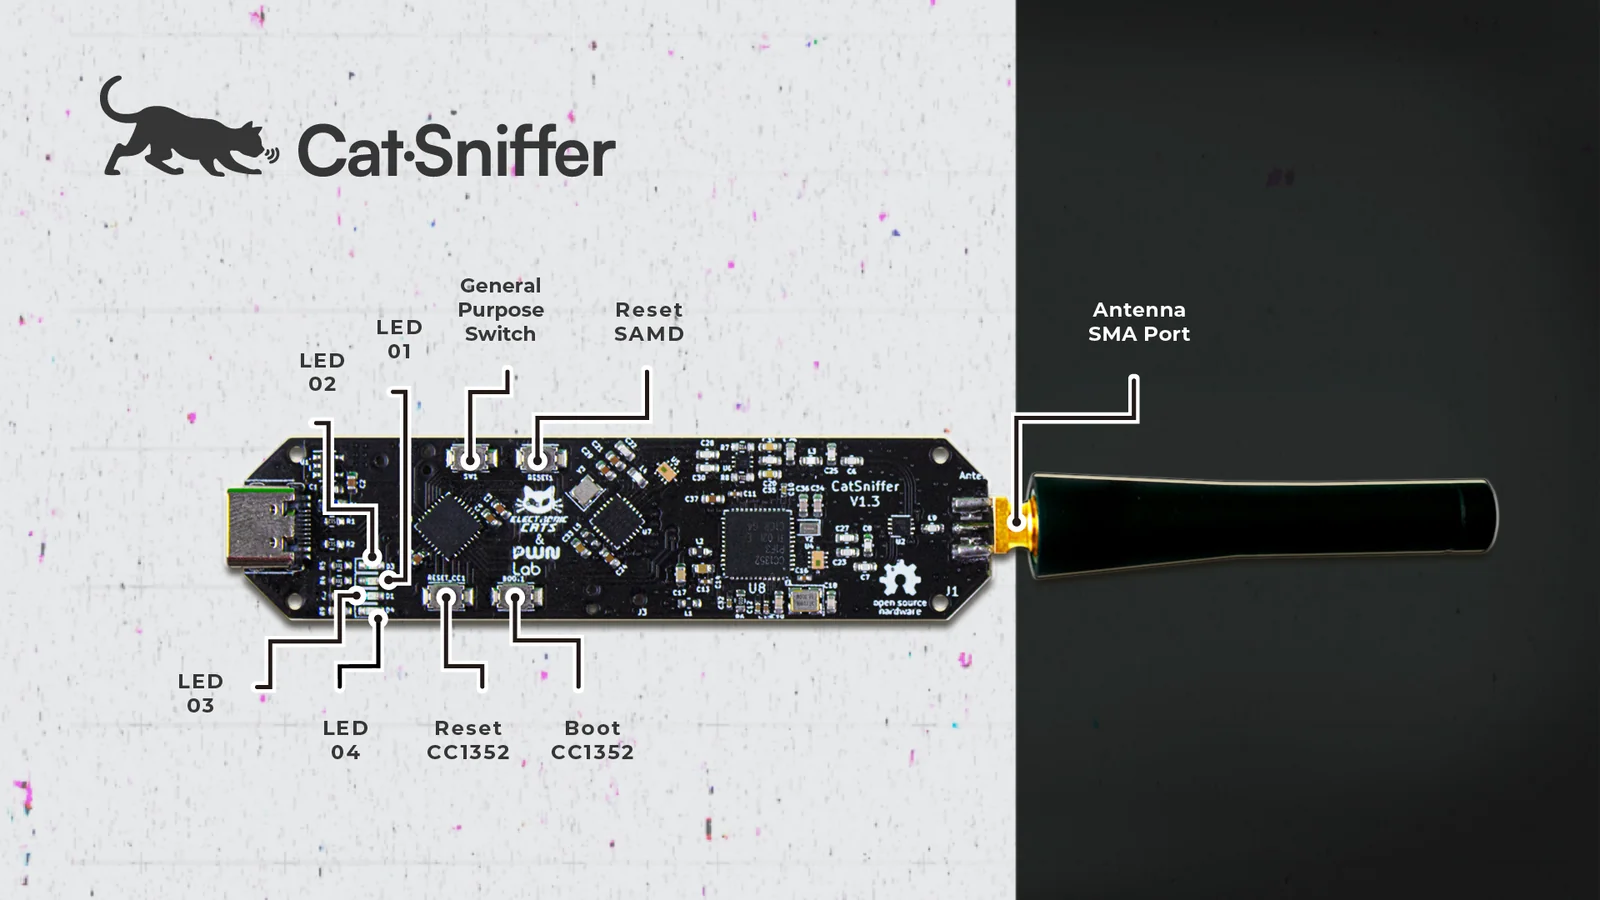
Firmware repository for CatSniffer, a multi-protocol IoT security research board supporting BLE, Zigbee, Sub-1 GHz, and more, with version-specific…

Proof-of-concept for NVIDIA GreenSection memory corruption 0day, demonstrating out-of-bounds write via shared memory section, enabling cross-user…

Your ONVIF and RTSP camera companion for discovering and hacking real-world security cameras 🎥

Research tools for MouseJack vulnerabilities in nRF24L01 wireless devices, including device discovery, packet sniffing, network mapping, and firmware…

LoRaWAN session cracker - A PoC for exploiting weak or shared Application Keys

Set your radio to 148.500 MHz, select FM, USB, or CW mode, and set the squelch to 0 or 1. Then, extend your radio's antenna toward the monitor's HDMI…

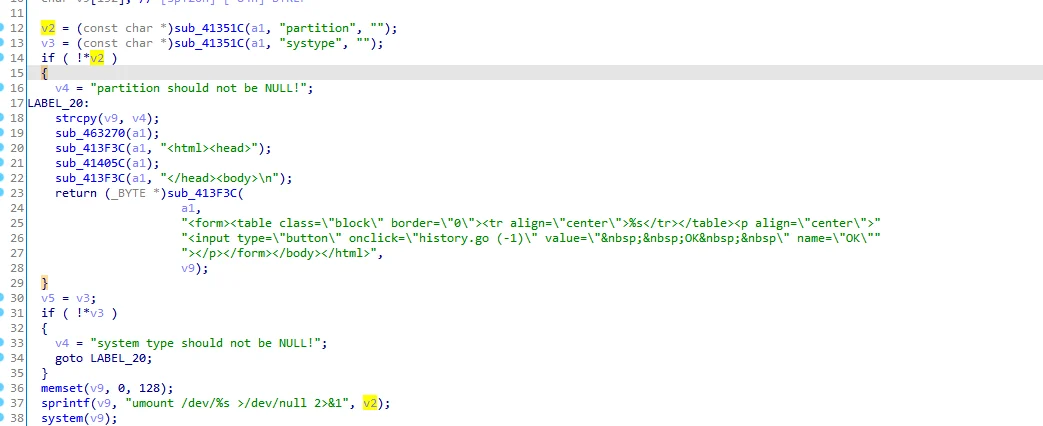
Proof-of-concept exploit for D-Link DIR-825M stack buffer overflow and command injection in /boafrm/formDiskFormat, enabling remote code execution as…