
unleashed-firmware
Custom firmware for Flipper Zero enabling Sub-GHz radio, NFC/RFID emulation, infrared, and BadUSB attack features for hardware security testing.

Custom firmware for Flipper Zero enabling Sub-GHz radio, NFC/RFID emulation, infrared, and BadUSB attack features for hardware security testing.

A suite of WiFi/Bluetooth offensive and defensive tools for the ESP32

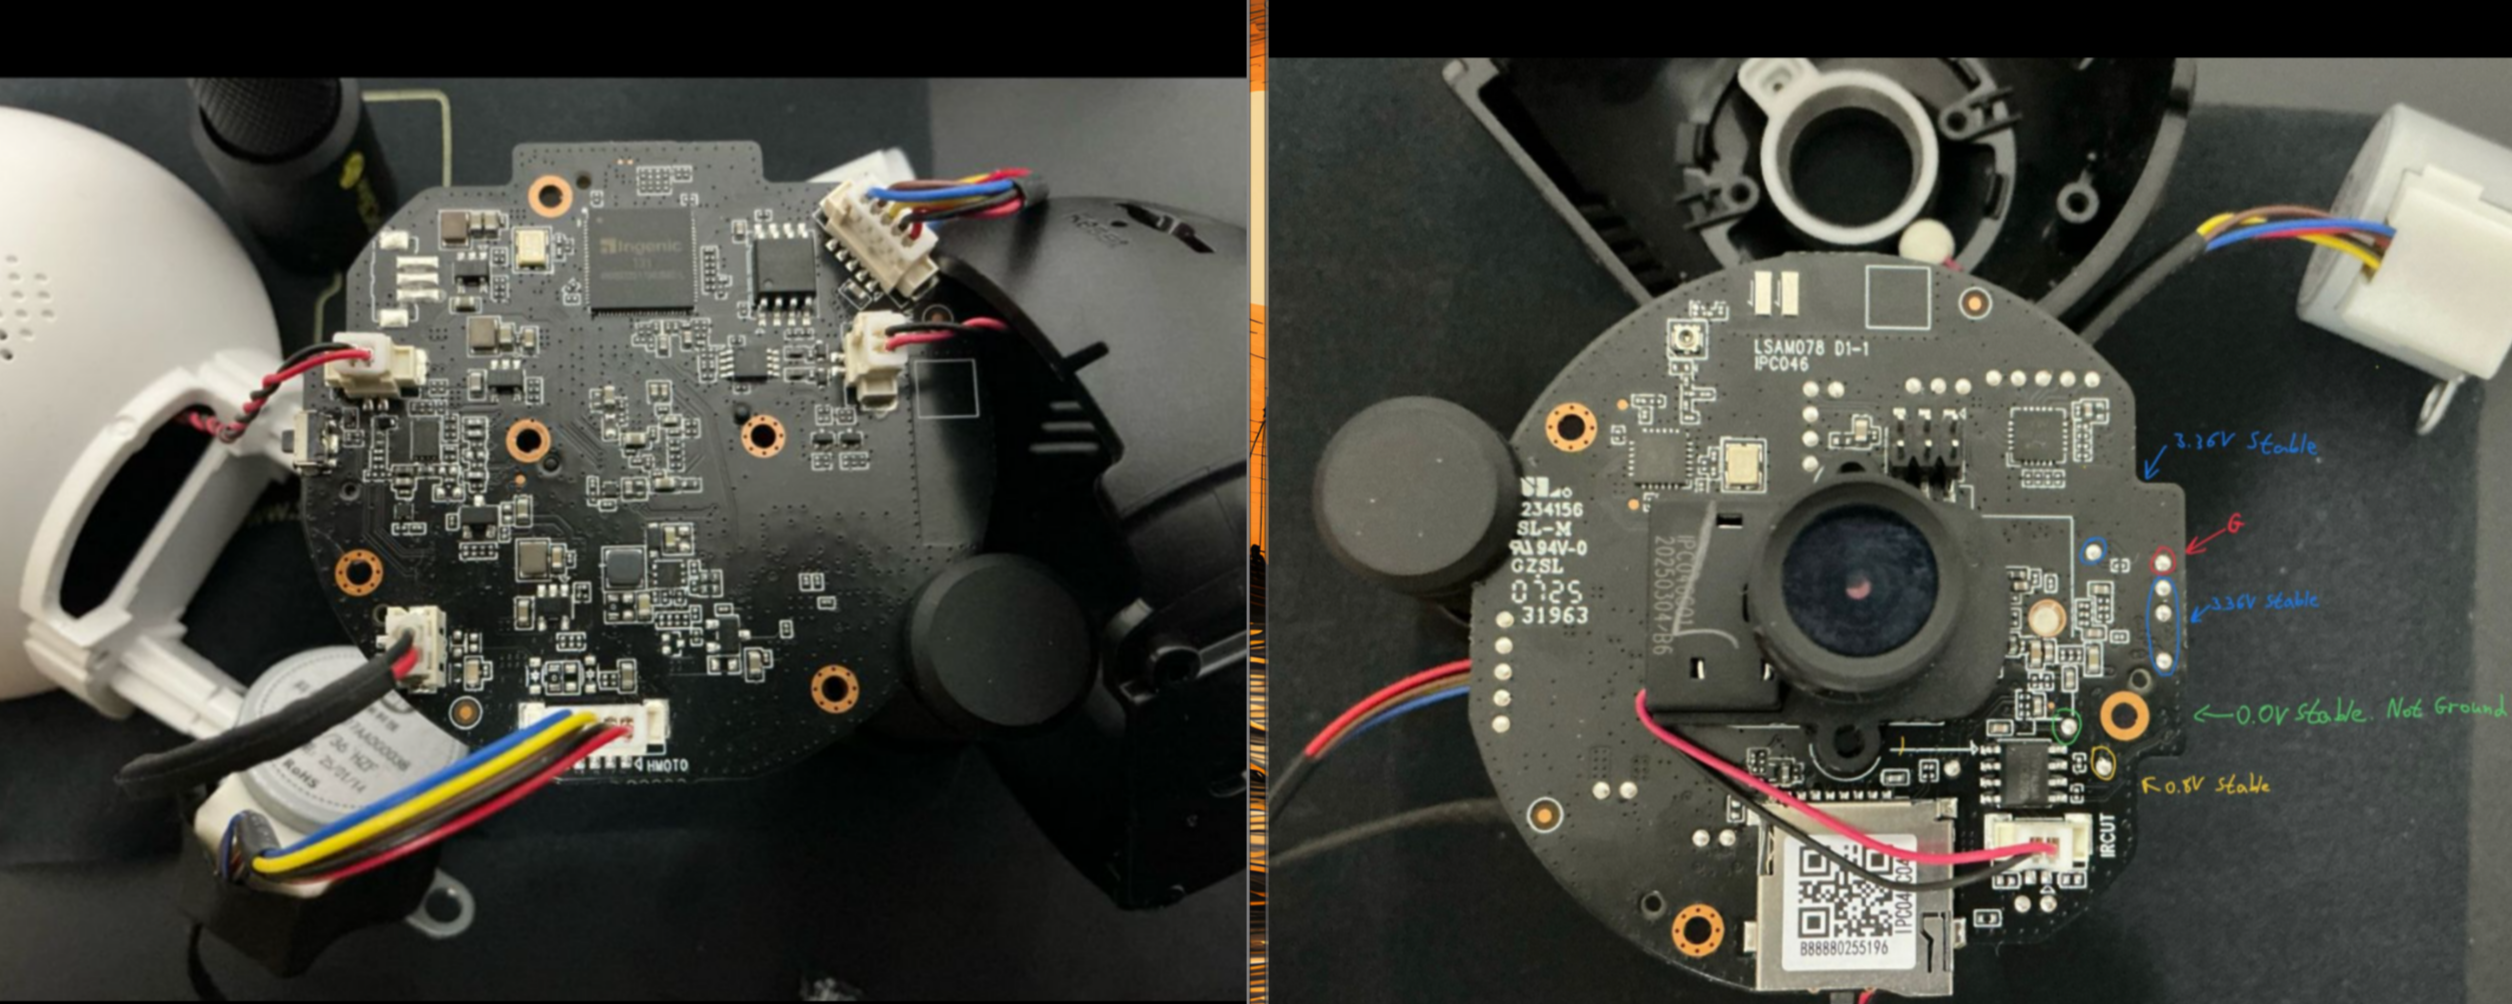
From UART to Root: Breaking Into the Xiaomi C200 via U-Boot

Flipper Zero firmware source code

EMBA - The firmware security analyzer

Portable NFC/RFID security tool for emulating and cloning contactless smartcards, reading tags, sniffing RF traffic, and recovering Mifare access…

Spoofing the Windows 10 HDD/diskdrive serialnumber from kernel without hooking

Attacks for $5 or less using Arduino

Red Team Toolkit - A curated list of tools that are commonly used in the field for Physical Security, Red Teaming, and Tactical Covert Entry.

Mifare Classic Plus - Hardnested Attack Implementation for SCL3711 LibNFC USB reader

Offline nested attack tool that recovers MIFARE Classic authentication keys using known default or user-supplied keys for assessing NFC/RFID card…

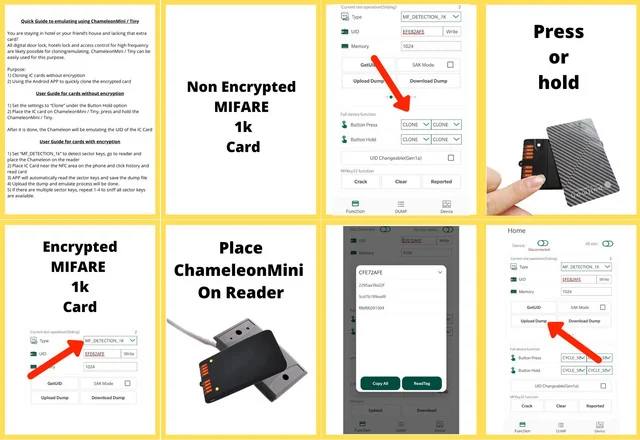
The new generation chameleon based on NRF52840 makes the performance of card emulation more stable. And gave the chameleon the ability to read,…

Hardware tool for RFID analysis, emulation, and penetration testing. Supports 125kHz, 13.56MHz protocols (MIFARE, iClass, ISO14443/15693) with key…

A Curated list of Security Resources for all connected things

Platform independent Near Field Communication (NFC) library

Unlocking _everything_ on the CPU with DRAM scrambling

Simple Windows and Linux keystroke injection tool that exfiltrates stored WiFi data (SSID and password).