
ajpfuzzer
 doyensec/ajpfuzzer
A command-line fuzzer for the Apache JServ Protocol (ajp13)
fuzzingpenetration-testingvulnerability-analysis+1
doyensec/ajpfuzzerA command-line fuzzer for the Apache JServ Protocol (ajp13)
 xmendez/wfuzz
Modular web fuzzer for automated security testing. Injects payloads into any HTTP request field to discover vulnerabilities, brute-force parameters,…
 jtpereyda/boofuzz
A fork and successor of the Sulley Fuzzing Framework
 portswigger/turbo-intruder
High-speed Burp Suite extension for sending large volumes of HTTP requests with a custom stack, Python-based attack configuration, and advanced…
 0xsobky/hackvault
A container repository for my public web hacks!
 khalilbijjou/wafninja
WAFNinja is a tool which contains two functions to attack Web Application Firewalls.
 p0dalirius/coercer
A python script to automatically coerce a Windows server to authenticate on an arbitrary machine through 12 methods.
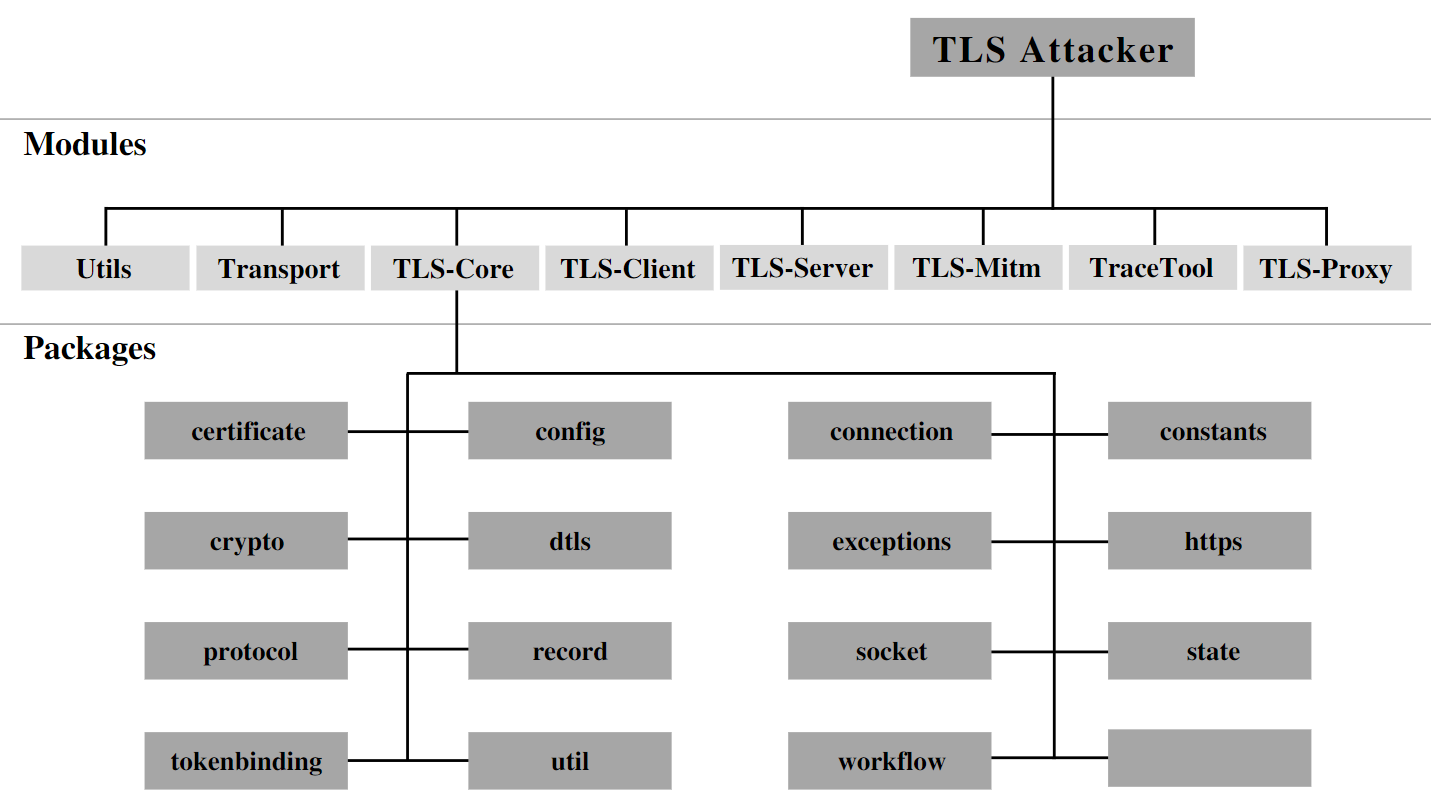 tls-attacker/tls-attacker
Java-based framework for systematic fuzzing and analysis of TLS libraries. Enables arbitrary protocol message crafting, modification, and testing of…
 flock4h/freeway
WiFi Penetration Testing & Auditing Tool
 schutzwerk/canalyzat0r
Security analysis toolkit for proprietary car protocols
 416rehman/deepzero
Find zero-days while you sleep. DeepZero is an automated vulnerability research framework that parses, decompiles, and analyzes thousands of Windows…
 nccgroup/fuzzowski
the Network Protocol Fuzzer that we will want to use.
 cisco-talos/mutiny-fuzzer
Network protocol fuzzer that replays PCAP traffic through a mutational engine (Radamsa) to quickly discover vulnerabilities in target hosts via…
 kamorin/dhcpig
DHCP exhaustion script written in python using scapy network library
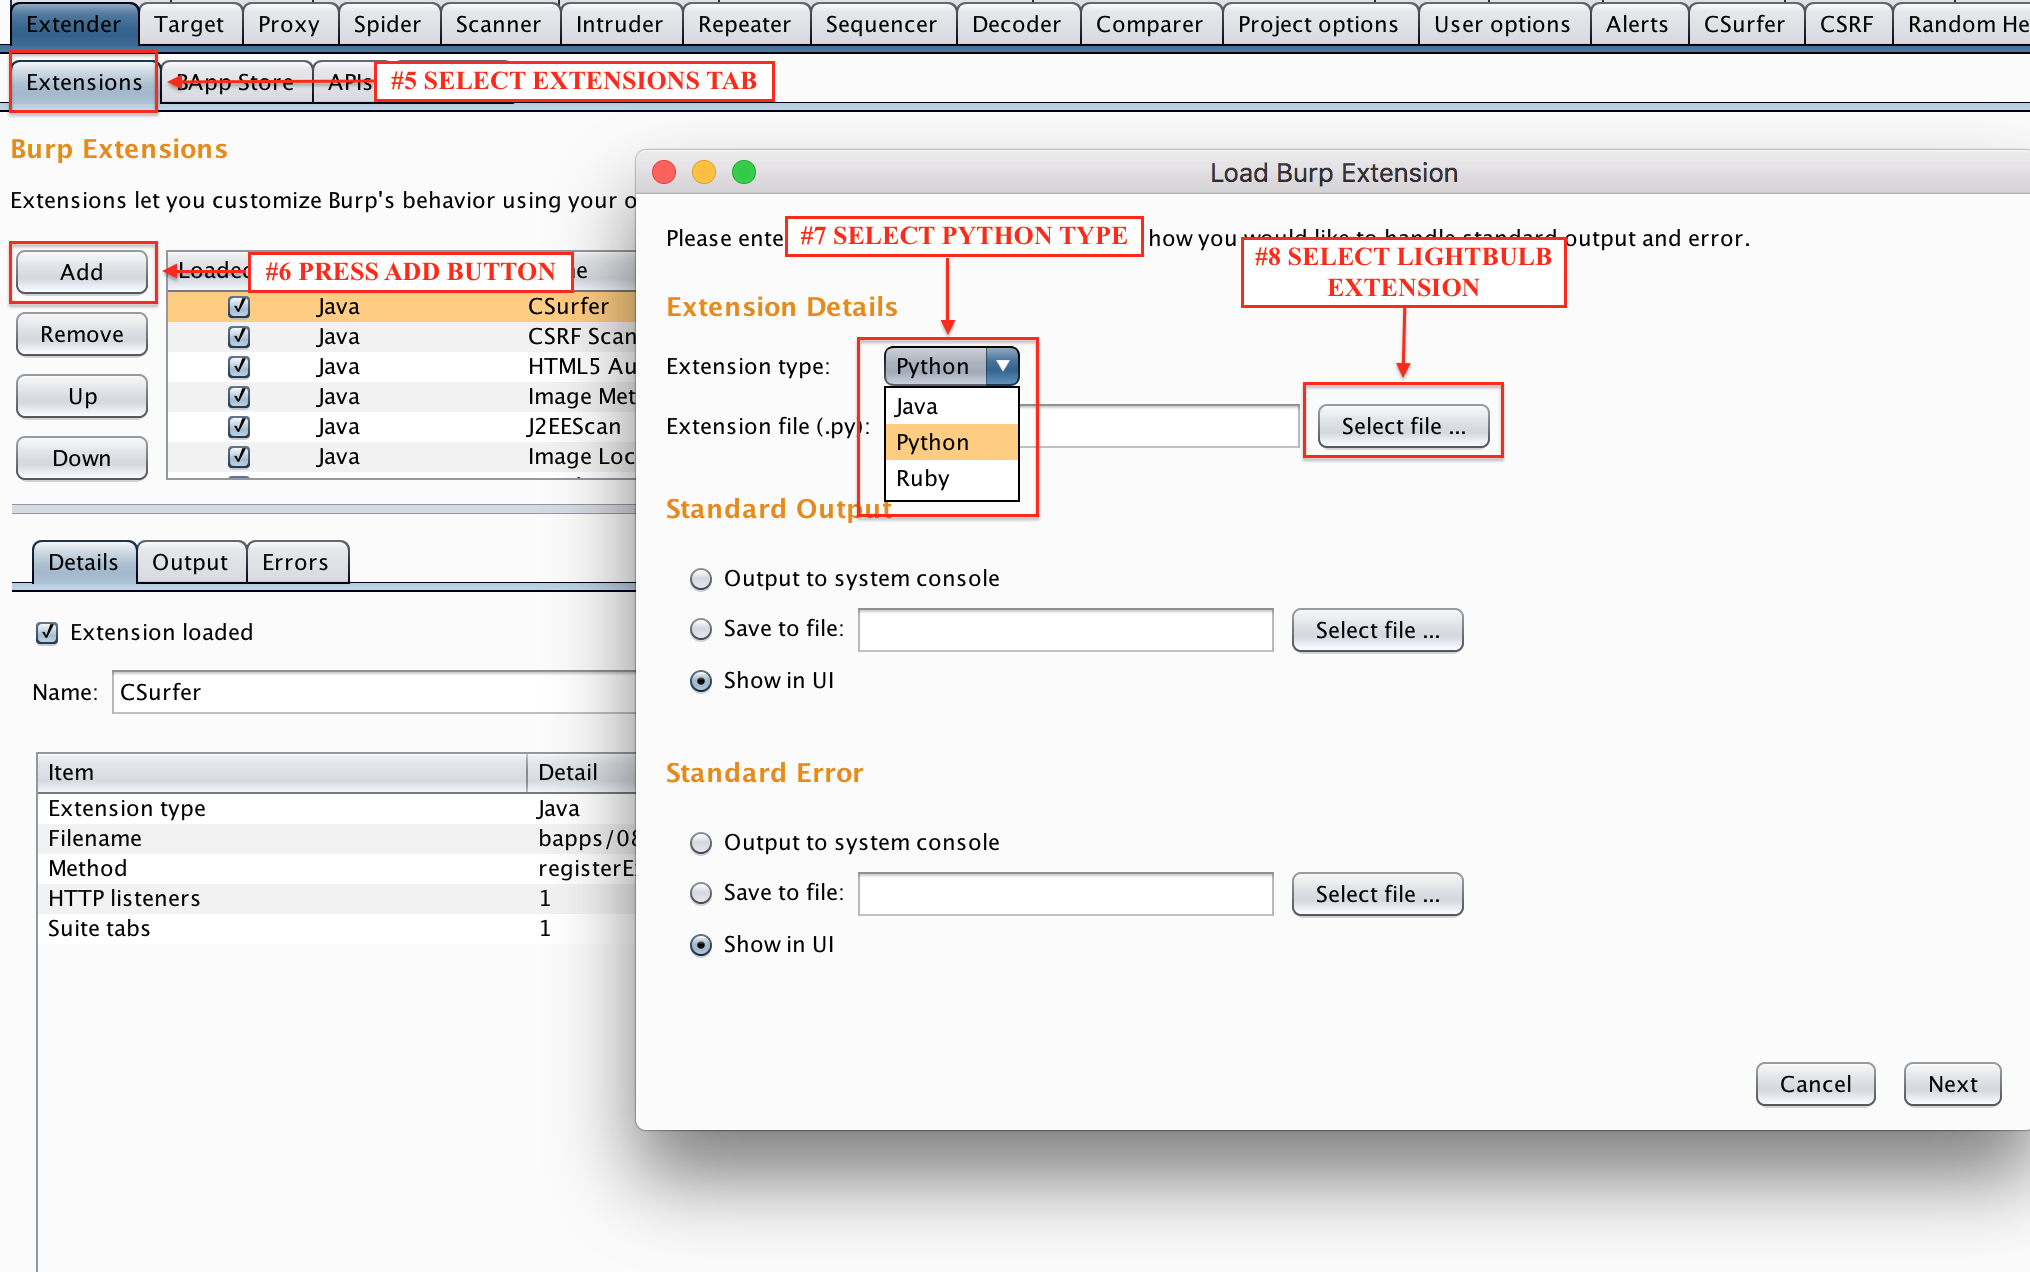 lightbulb-framework/lightbulb-framework
Tools for auditing WAFS
 fcavallarin/htcap
htcap is a web application scanner able to crawl single page application (SPA) recursively by intercepting ajax calls and DOM changes.
 rub-nds/ws-attacker
WS-Attacker is a modular framework for web services penetration testing. It is developed by the Chair of Network and Data Security, Ruhr University…
 dzonerzy/gowapt
Go Web Application Penetration Test