SSTImap
 vladko312/sstimap
Automatic SSTI detection tool with interactive interface
code-analysiscommand-and-controldynamic-code-analysis+6
vladko312/sstimapAutomatic SSTI detection tool with interactive interface
 enessar/libpng_oss-fuzz
Security research project on fuzzing libpng with OSS-Fuzz. Includes seed corpus analysis, custom read/write fuzzers, and a proof-of-concept exploit…
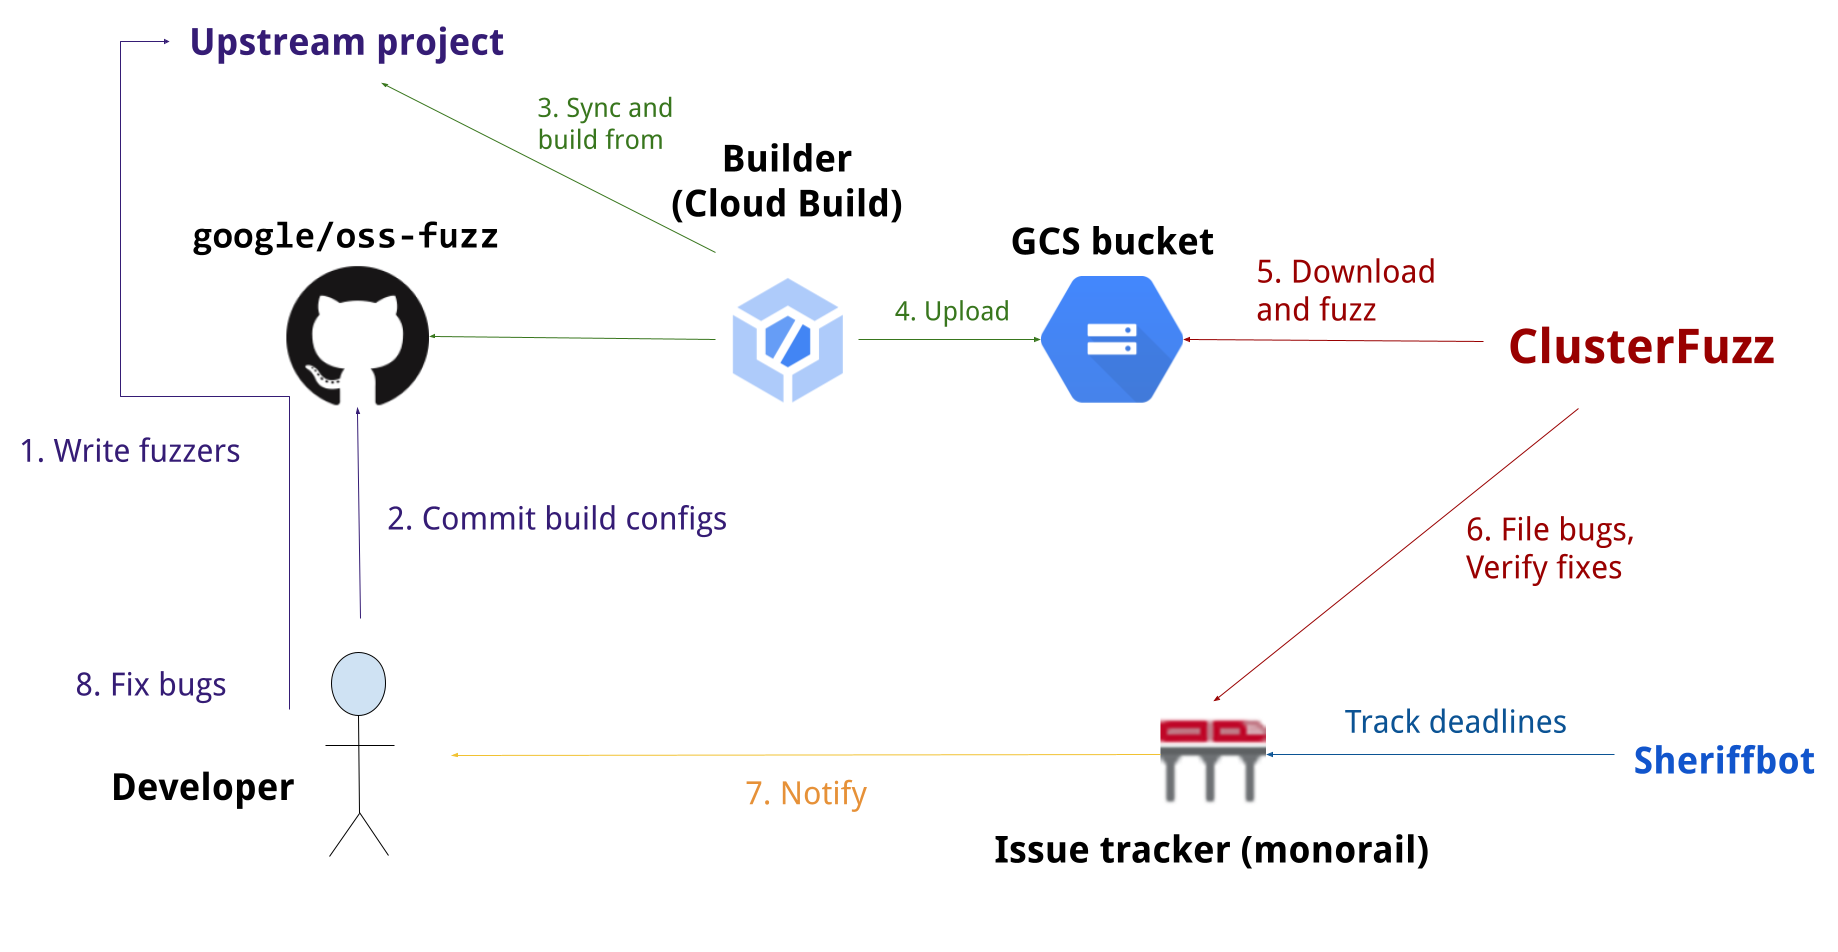 google/oss-fuzz
OSS-Fuzz - continuous fuzzing for open source software.
 kudelskisecurity/cdf
Automated differential fuzzing tool for cryptographic software that detects implementation errors, compliance failures, and side-channel leaks…
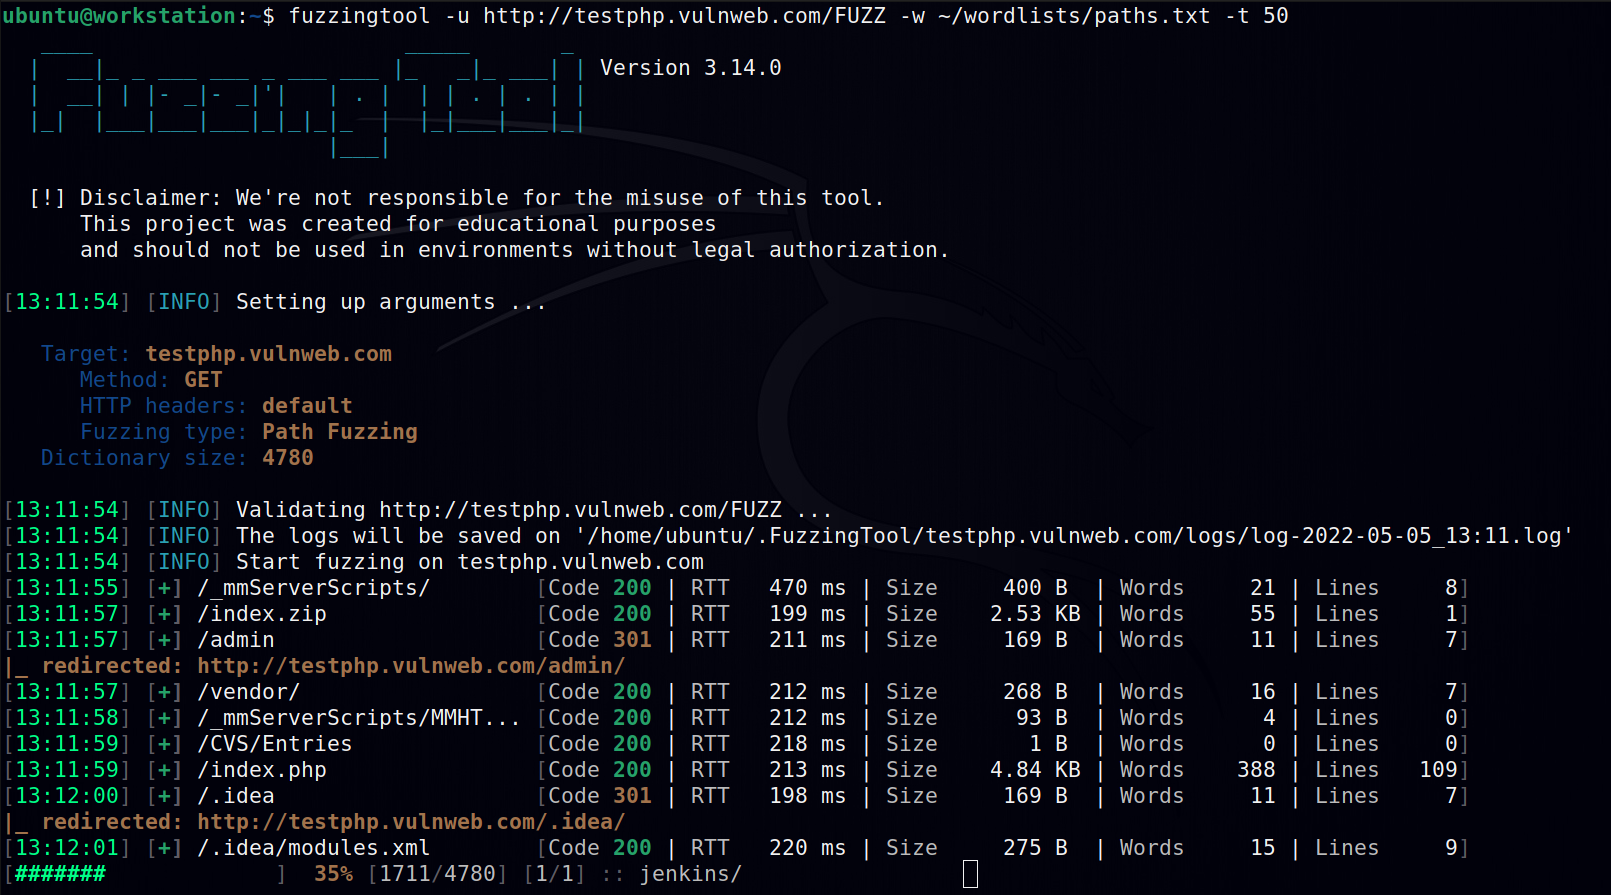 nescau-ufla/fuzzingtool
Software for fuzzing, used on web application pentestings.
 ntop/ndpi
Open Source Deep Packet Inspection Software Toolkit
 google/honggfuzz
Security oriented software fuzzer. Supports evolutionary, feedback-driven fuzzing based on code coverage (SW and HW based)
 google/silifuzz
Fuzzes CPU implementations by generating test inputs from software proxies, then executes them on real hardware to detect microarchitecture defects…
 team-atlanta/aixcc-afc-atlantis
Automated cyber reasoning system that discovers and analyzes software vulnerabilities through fuzzing, binary analysis, and program reasoning for…
 cclabsinc/rfcrack
A Software Defined Radio Attack Tool
 schutzwerk/canalyzat0r
Security analysis toolkit for proprietary car protocols
 wireghoul/dotdotpwn
DotDotPwn - The Directory Traversal Fuzzer
 feliam/cve-2013-2729
Python-based exploit generator for Adobe Reader BMP/RLE heap corruption (CVE-2013-2729). Demonstrates arbitrary code execution via malicious BMP…
 kevinbackhouse/djvulibre-poc-cve-2025-53367
Proof-of-concept exploit for CVE-2025-53367, a vulnerability in the DjVuLibre library. Demonstrates exploitation of a memory corruption bug in DjVu…
 googleprojectzero/brokentype
TrueType and OpenType font fuzzing toolset
 jopohl/urh
Universal Radio Hacker: Investigate Wireless Protocols Like A Boss
 microsoft/onefuzz
A self-hosted Fuzzing-As-A-Service platform