
wssip
 nccgroup/wssip
Application for capturing, modifying and sending custom WebSocket data from client to server and vice versa.
fuzzingpenetration-testingweb-proxies-interception+1
4508 years ago
nccgroup/wssipApplication for capturing, modifying and sending custom WebSocket data from client to server and vice versa.
 libnet/nemesis
A command-line network packet crafting and injection utility
 nxenon/h2spacex
HTTP/2 Last Frame Synchronization (also known as Single Packet Attack) low Level Library / Tool based on Scapy + Exploit Timing Attacks
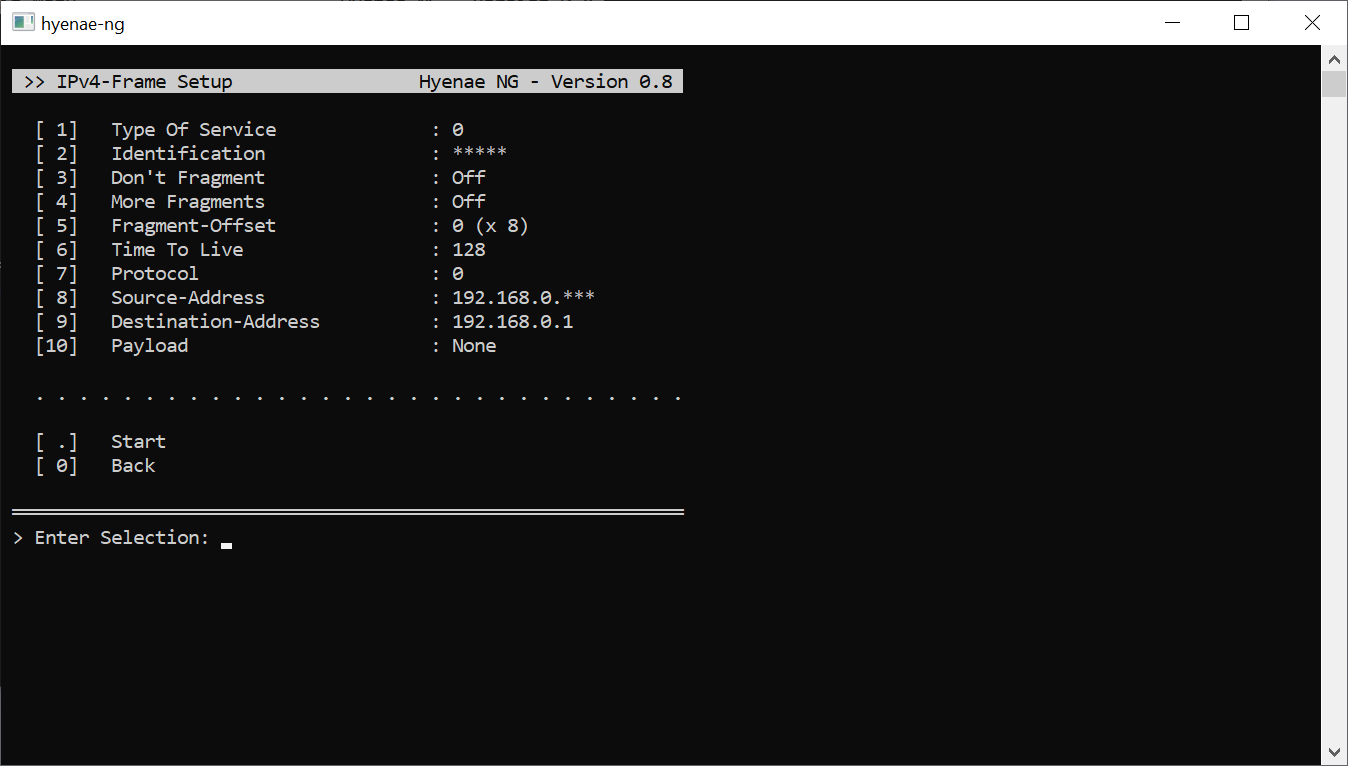 r-richter/hyenae-ng
Cross-platform network packet generator with full layer spoofing, pattern-based address randomization, and flood detection evasion for stress-testing…
 halit/isip
Interactive sip toolkit for packet manipulations, sniffing, man in the middle attacks, fuzzing, simulating of dos attacks.

 s0md3v/arjun
HTTP parameter discovery tool that finds valid query parameters for URL endpoints using a large dictionary, supporting GET/POST/JSON/XML requests,…
 ignitetechnologies/burpsuite-for-pentester
This cheatsheet is built for the Bug Bounty Hunters and penetration testers in order to help them hunt the vulnerabilities from P4 to P1 solely and…
 devanshbatham/paramspider
Mining URLs from dark corners of Web Archives for bug hunting/fuzzing/further probing
 reversenseorg/dexcalibur
[Official] Android reverse engineering tool focused on dynamic instrumentation automation leveraging Frida. It disassembles dex, analyzes it…
 sunblaze-ucb/exploitgym
ExploitGym is a large-scale, realistic benchmark built from real-world vulnerabilities designed to evaluate AI agents' ability to develop exploits.
 owasp/offat
Automated API security testing tool that generates tests from OpenAPI specs, fuzzes inputs, and checks for OWASP API Top 10 vulnerabilities including…
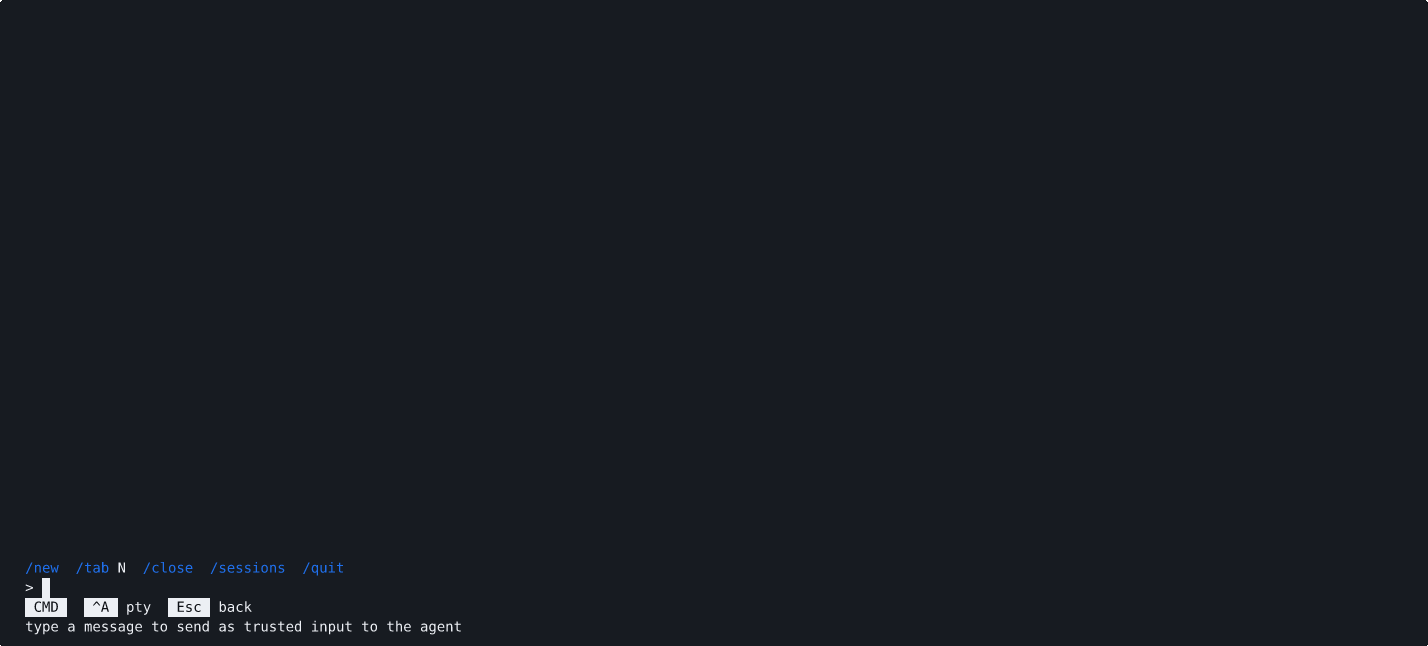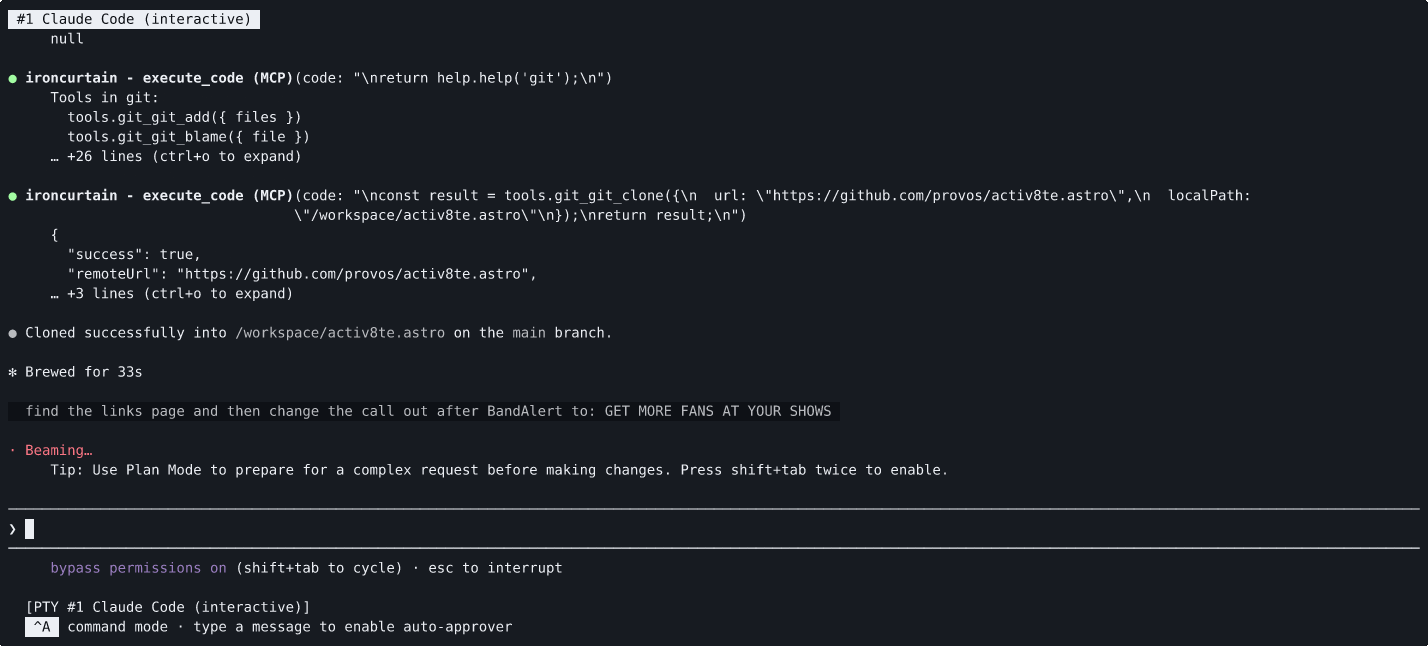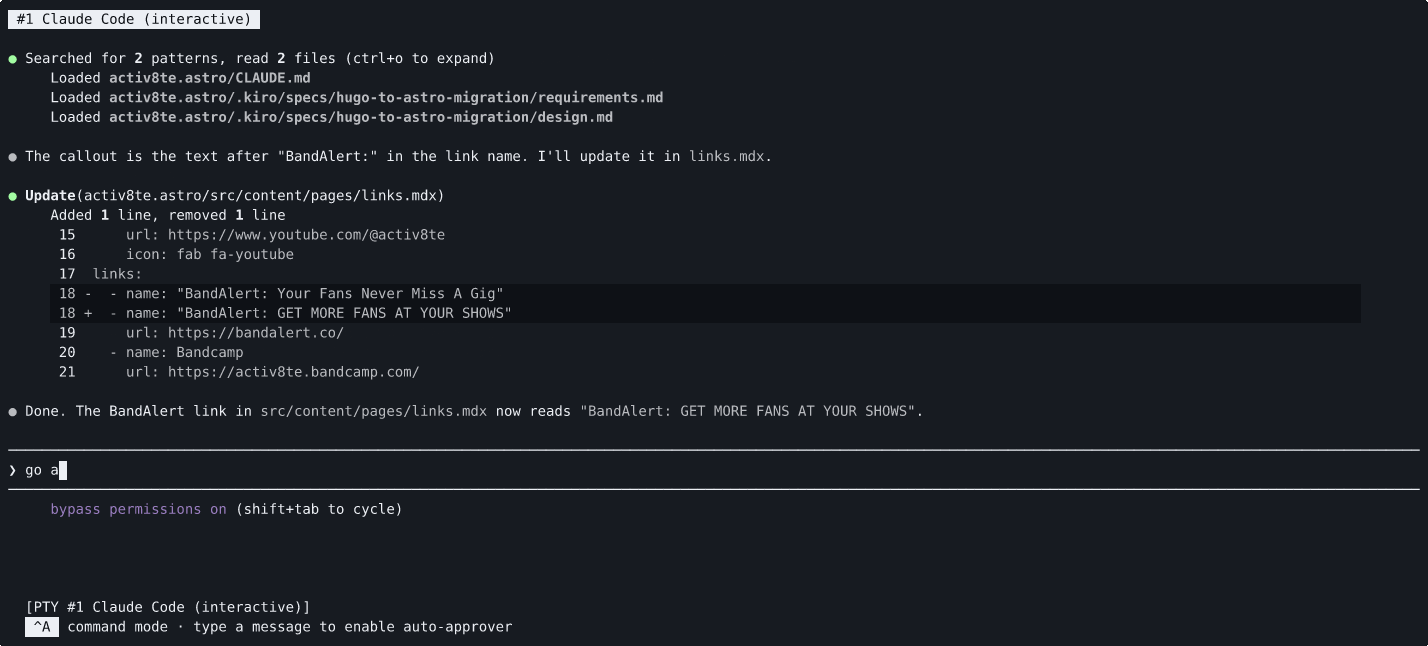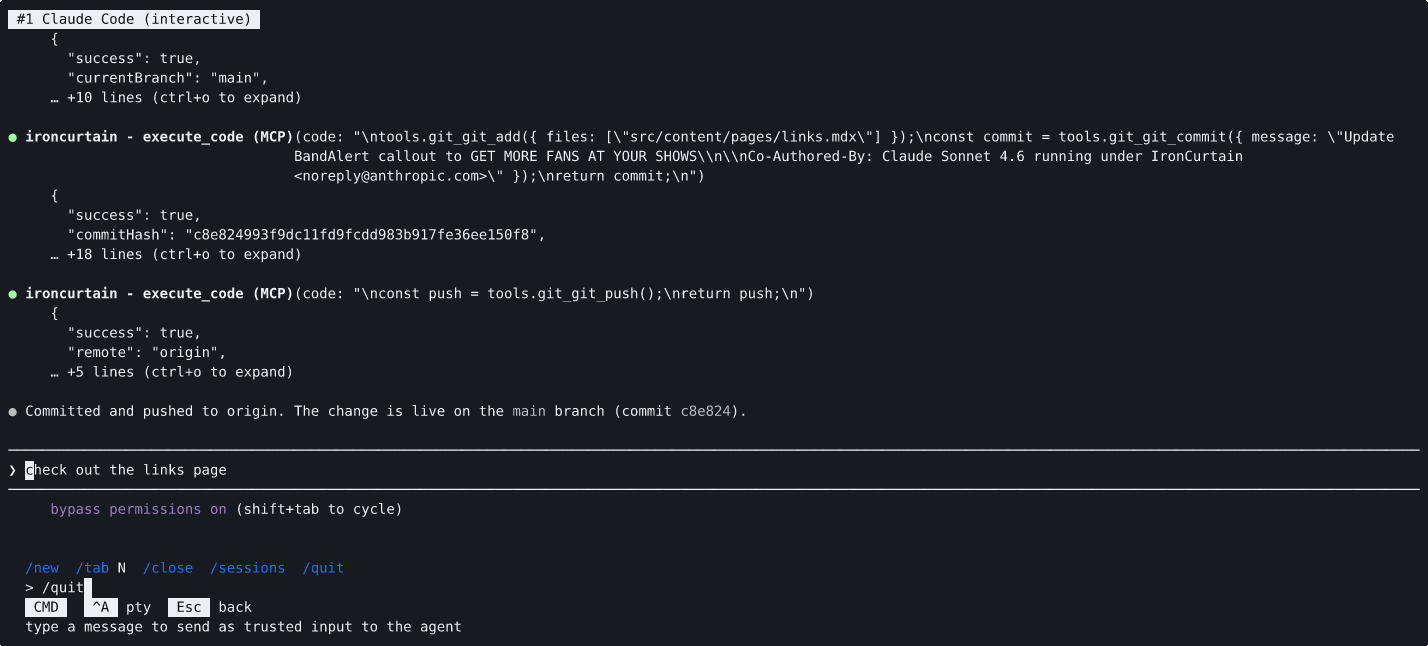 provos/ironcurtain
A secure* runtime for autonomous AI agents. Policy from plain-English constitutions. (*https://ironcurtain.dev)
 google/silifuzz
Fuzzes CPU implementations by generating test inputs from software proxies, then executes them on real hardware to detect microarchitecture defects…
 overspace-labs/caa
BurpSuite plugin for HTTP packet analysis and fuzzing dictionary generation. Extracts parameters, paths, and files from requests, counts frequency,…
 netzob/netzob
Open-source toolkit for reverse engineering, modeling, and fuzzing communication protocols. Infers message formats and state machines from network…
 hackerhouse-opensource/exploits
exploits and proof-of-concept vulnerability demonstration files from the team at Hacker House