

 henshin/filebuster
An extremely fast and flexible web fuzzer
 pedrib/poc
Advisories, proof of concept files and exploits that have been made public by @pedrib.
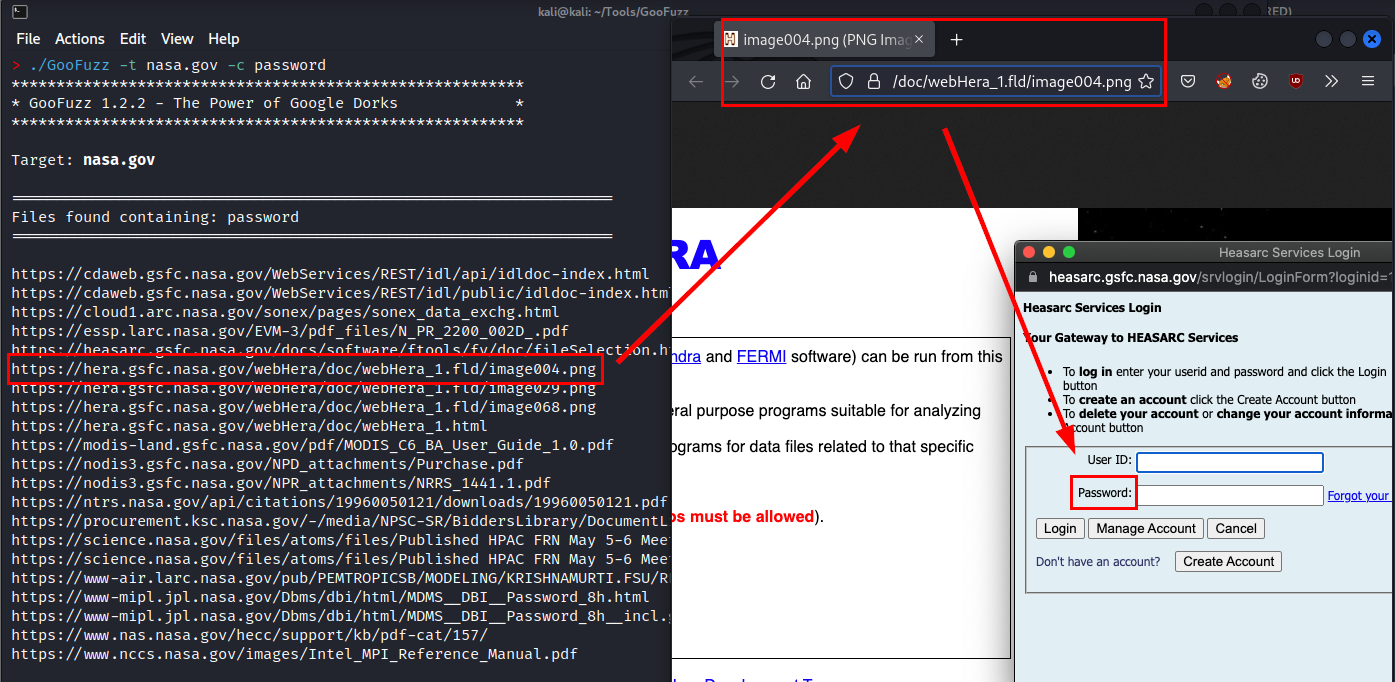 m3n0sd0n4ld/goofuzz
Bash-based fuzzing tool that leverages Google Dorking for stealthy enumeration of directories, files, subdomains, and parameters without direct…
 overspace-labs/caa
BurpSuite plugin for HTTP packet analysis and fuzzing dictionary generation. Extracts parameters, paths, and files from requests, counts frequency,…
 netzob/netzob
Open-source toolkit for reverse engineering, modeling, and fuzzing communication protocols. Infers message formats and state machines from network…
 hackerhouse-opensource/exploits
exploits and proof-of-concept vulnerability demonstration files from the team at Hacker House
 musana/fuzzuli
Domain-aware URL fuzzer that dynamically generates wordlists to discover exposed backup and sensitive files on web servers.
 rapiddns/afuzz
Automated web path fuzzing tool that detects hidden directories, files, and endpoints using intelligent language detection, blacklist/whitelist…
 liamg/scout
🔭 Lightweight URL fuzzer and spider: Discover a web server's undisclosed files, directories and VHOSTs
 cytopia/urlbuster
Powerful mutable web directory fuzzer to bruteforce existing and/or hidden files or directories.
 jhftss/ida2obj
Static binary instrumentation tool that dumps COFF object files from executables, enabling code/data insertion at any location for black-box fuzzing…
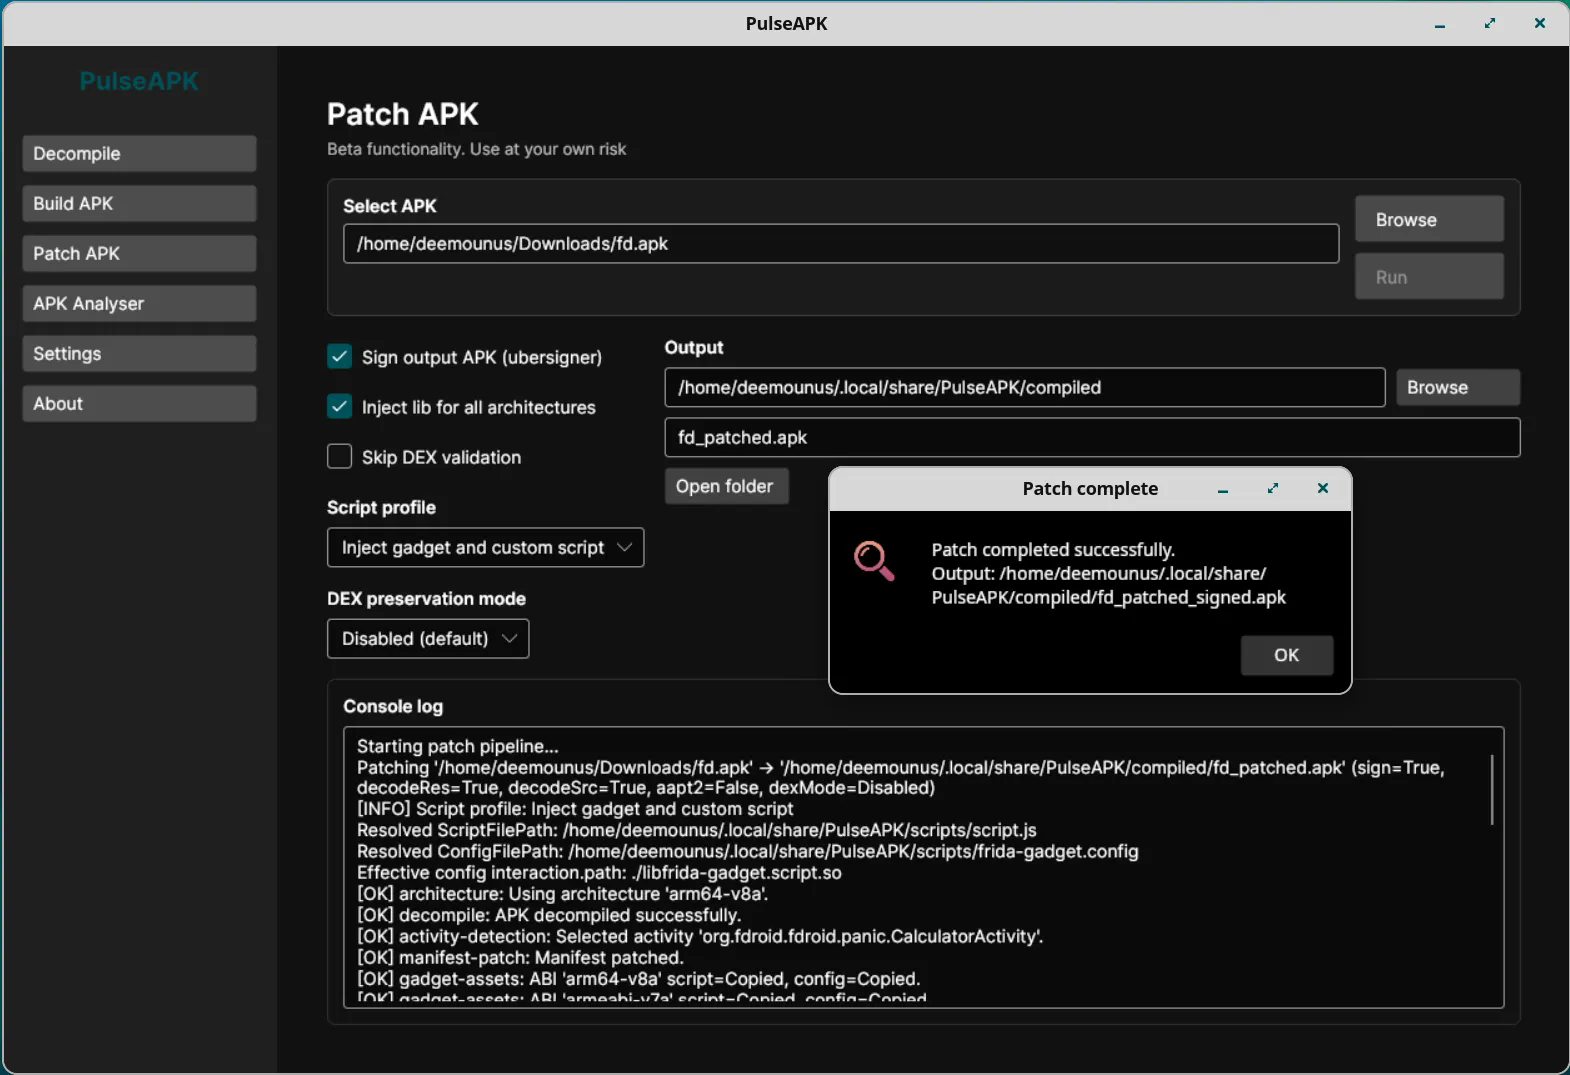 deemoun/pulseapk-core
PulseAPK Core: Cross-Platform tool for working with APK files: Decompilation, Analysis, Building
 tismayil/fastfuz-chrome-ext
Chrome extension for fast web fuzzing to discover hidden files and directories during penetration testing and vulnerability analysis.
 halcy0nic/cves-for-picoc-3.2.2
Reproduction files for CVE-2022-44312 through CVE-2022-44321
 zunak/cve-2024-22641
Proof-of-concept for CVE-2024-22641: ReDoS vulnerability in TCPDF <=6.7.4 triggered by crafted SVG files, demonstrating regex backtrack limit…
 mohitsinghpapola/cve-2023-20052
Fixed Docker build for CVE-2023-20052 ClamAV XXE exploit. Resolves OpenSSL 3.0 compilation errors using Ubuntu 18.04 with OpenSSL 1.0 for…
 cyhe50/cve-2025-54874-poc
Proof-of-concept demonstrating a memory leak in OpenJPEG 2.5.1 via crafted JP2 files, triggering opj_read_header failure and heap leak, with valgrind…