
fpicker
 ttdennis/fpicker
Frida-based in-process fuzzing suite with AFL++ proxy, standalone active/passive modes, and shared memory communication for high-performance…
binary-analysisdynamic-analysis-sandboxingexploitation+2
298
ttdennis/fpickerFrida-based in-process fuzzing suite with AFL++ proxy, standalone active/passive modes, and shared memory communication for high-performance…
 google/honggfuzz
Security oriented software fuzzer. Supports evolutionary, feedback-driven fuzzing based on code coverage (SW and HW based)
 cloudflare/filterforge
Tool for solving BPF filters and crafting packets based on these.
 hackinglz/maps_scanner
MAPS cloud scanner and response parser for Microsoft Defender research.
 themalwareguardian/cve-2003-0264
Classic stack-based buffer overflow in SLMail 5.1 showing how early mail servers could be compromised through oversized SMTP and POP3 commands.
 jgs-developer/cve-2025-5548
Stack-based buffer overflow exploit for FreeFloat FTP Server, demonstrating reverse engineering, EIP control, and shellcode execution for educational…
 aflplusplus/aflplusplus
AFL++ is a state-of-the-art fuzzer, and #1 in benchmarks. It was originally based on AFL. Today it comes with qemu 5.1, collision-free coverage,…
 alberto-galindo/cve-2025-5548
Security research and reproduction of CVE-2025-5548: A stack-based buffer overflow in FreeFloat FTP Server 1.0. Includes binary analysis, crash…
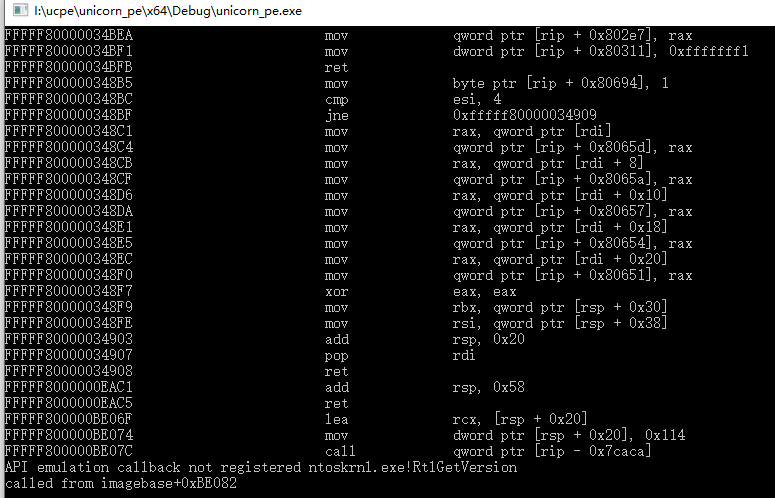 hzqst/unicorn_pe
Emulates Windows PE execution using Unicorn engine for malware analysis, unpacking packed binaries, and decrypting VMProtect strings and imports.
 angorafuzzer/angora
Coverage-guided fuzzer that uses taint tracking and scalar optimization to solve path constraints without symbolic execution, improving branch…
 unicorn-engine/unicorn
Unicorn CPU emulator framework (ARM, AArch64, M68K, Mips, Sparc, PowerPC, RiscV, S390x, TriCore, X86)
 quarkslab/rewind
Snapshot-based coverage-guided windows kernel fuzzer
 tezeb/accfly
Disclosure of Accfly camera vulnerabilities: CVE-2020-25782, CVE-2020-25783, CVE-2020-25784, CVE-2020-25785.
 benmevic/cve-2025-22457
Altay takımı haftalık sunumu için yaptığım cve-2025-22457 zafiyeti demo uygulaması
 themalwareguardian/cve-2017-14980
Stack-based buffer overflow in Sync Breeze Enterprise 10.0.28 reachable through the /login handler, demonstrating how unchecked input length can…
 themalwareguardian/cve-2002-1120
Classic stack-based buffer overflow in Savant Web Server 3.1 demonstrating early-2000s remote memory corruption through a crafted HTTP request.
 iamescri/cve-2025-5548-freefloat-ftp-buffer-overflow
Laboratorio de análisis y explotación de la vulnerabilidad CVE-2025-5548 en FreeFloat FTP Server 1.0
 veridiff/veridiff
Dynamic branch-divergence finder for native code -- traces two Frida executions and finds the exact instruction where they diverge.