
ReconHound
 s_r_e_e_r_a_j/reconhound
ReconHound is a Python-based web reconnaissance tool designed for penetration testers, bug bounty hunters, and ethical hackers. It supports directory…
fuzzinginformation-gatheringpenetration-testing+3
1
s_r_e_e_r_a_j/reconhoundReconHound is a Python-based web reconnaissance tool designed for penetration testers, bug bounty hunters, and ethical hackers. It supports directory…
 xmendez/wfuzz
Modular web fuzzer for automated security testing. Injects payloads into any HTTP request field to discover vulnerabilities, brute-force parameters,…
 flock4h/freeway
WiFi Penetration Testing & Auditing Tool
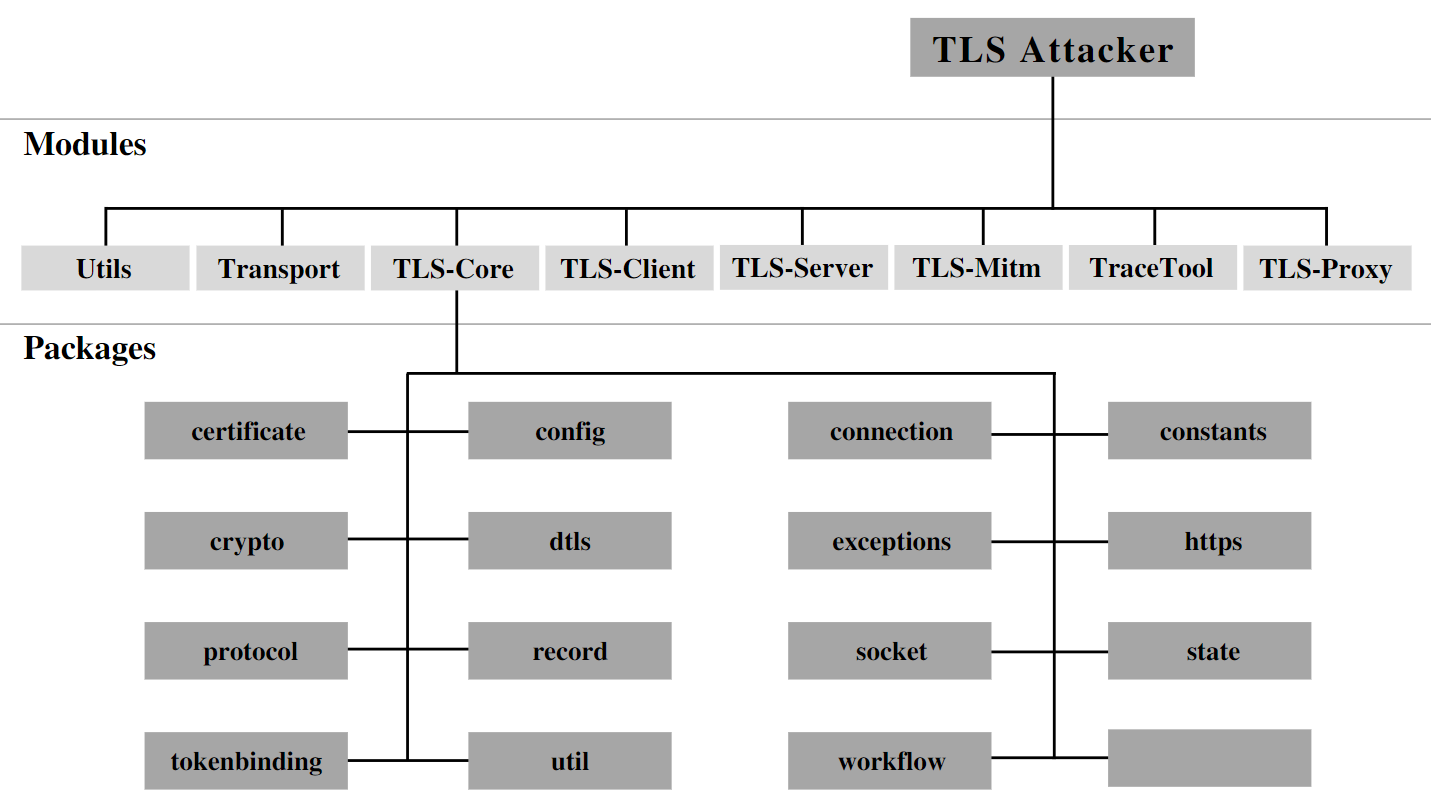 tls-attacker/tls-attacker
Java-based framework for systematic fuzzing and analysis of TLS libraries. Enables arbitrary protocol message crafting, modification, and testing of…
 rub-nds/ws-attacker
WS-Attacker is a modular framework for web services penetration testing. It is developed by the Chair of Network and Data Security, Ruhr University…
 dzonerzy/gowapt
Go Web Application Penetration Test
 redsection/pfuzz
Modular WAF bypass fuzzer with multi-threading, request manipulation, and payload encoding for red team web application testing.
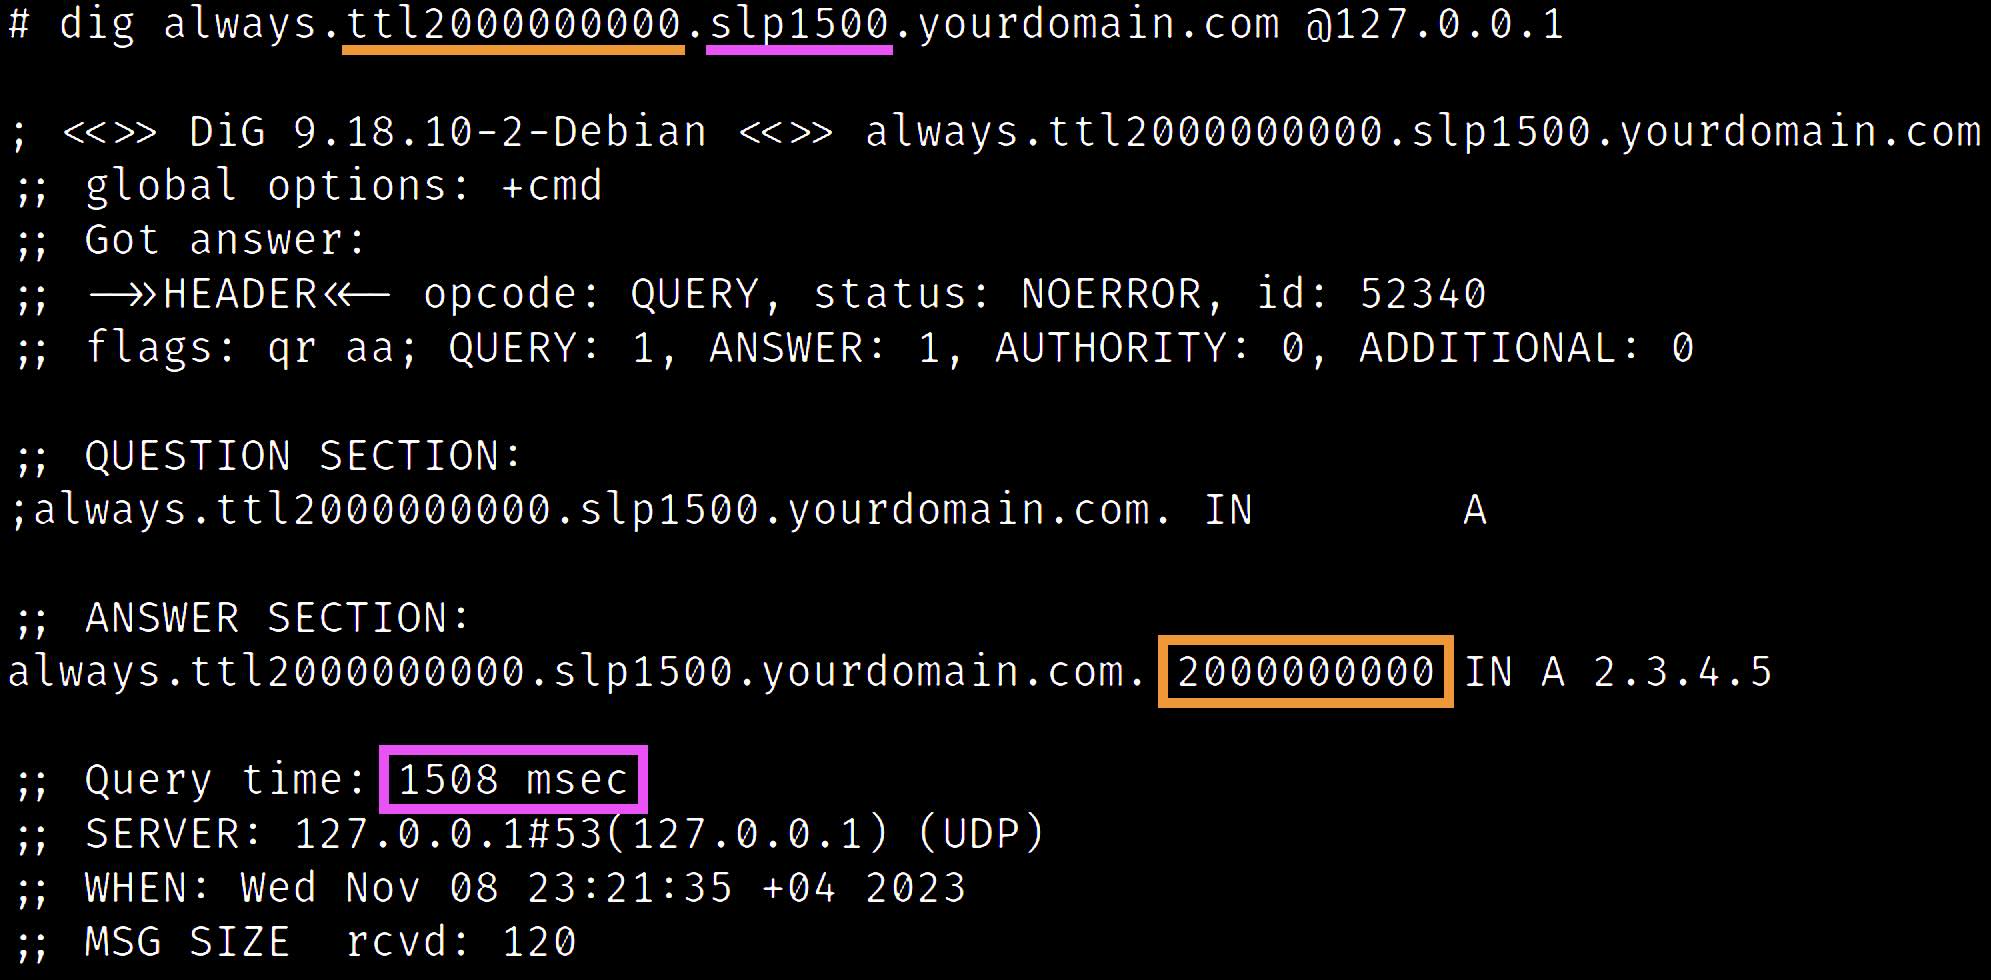 oryxlabs/polardns
PolarDNS is a specialized authoritative DNS server suitable for penetration testing and vulnerability research.
 vitaliy-grigoriev/protocol-analyzer
Fuzz testing framework for network protocols.
 tismayil/fastfuz-chrome-ext
Chrome extension for fast web fuzzing to discover hidden files and directories during penetration testing and vulnerability analysis.
 cappricio-securities/crlfi-scanner
CRLFISCANNER is a lightweight and powerful CLI tool designed for bug bounty hunters and penetration testers to automatically detect CRLF injection…
 retocode/golang-cve-2023-44487
Testing resources and attacker tool for CVE-2023-44487 (HTTP/2 Rapid Reset) to evaluate server resilience across Go, gRPC, reverse proxy, and nginx…
 redcrazyghost/cve-2026-42945
Go-based exploit tool for CVE-2026-42945 (nginx HTTP/2) with detection, crash probing, command execution, and reverse shell capabilities for…
 pentdebra/scadashutdowntool
SCADA Security Testing tool
 khalilbijjou/wafninja
WAFNinja is a tool which contains two functions to attack Web Application Firewalls.
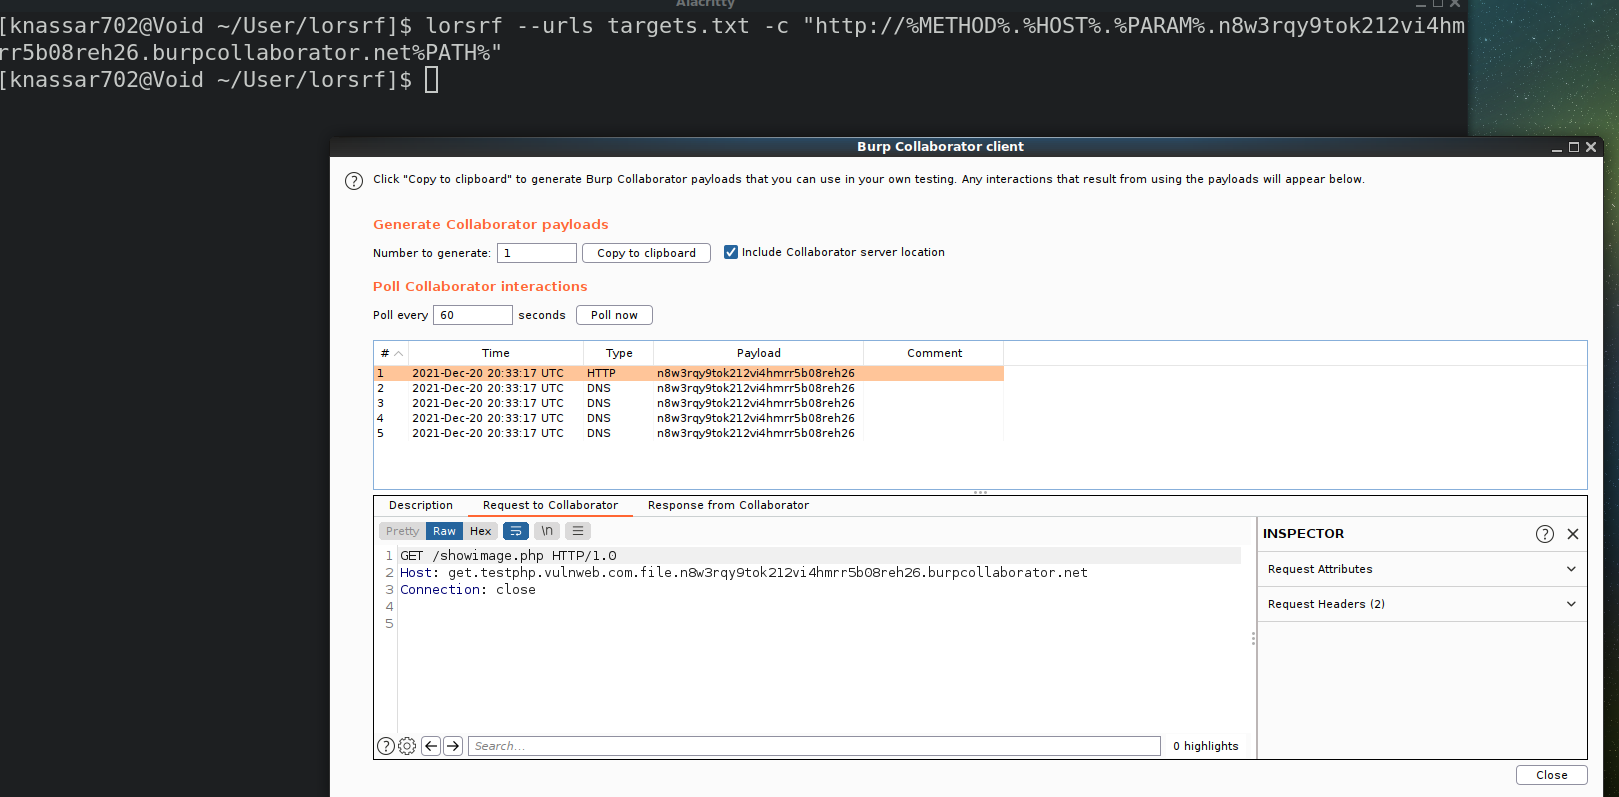 mindpatch/lorsrf
Fast CLI tool to find the parameters that can be used to find SSRF or Out-of-band resource load :artificial_satellite: :crab:
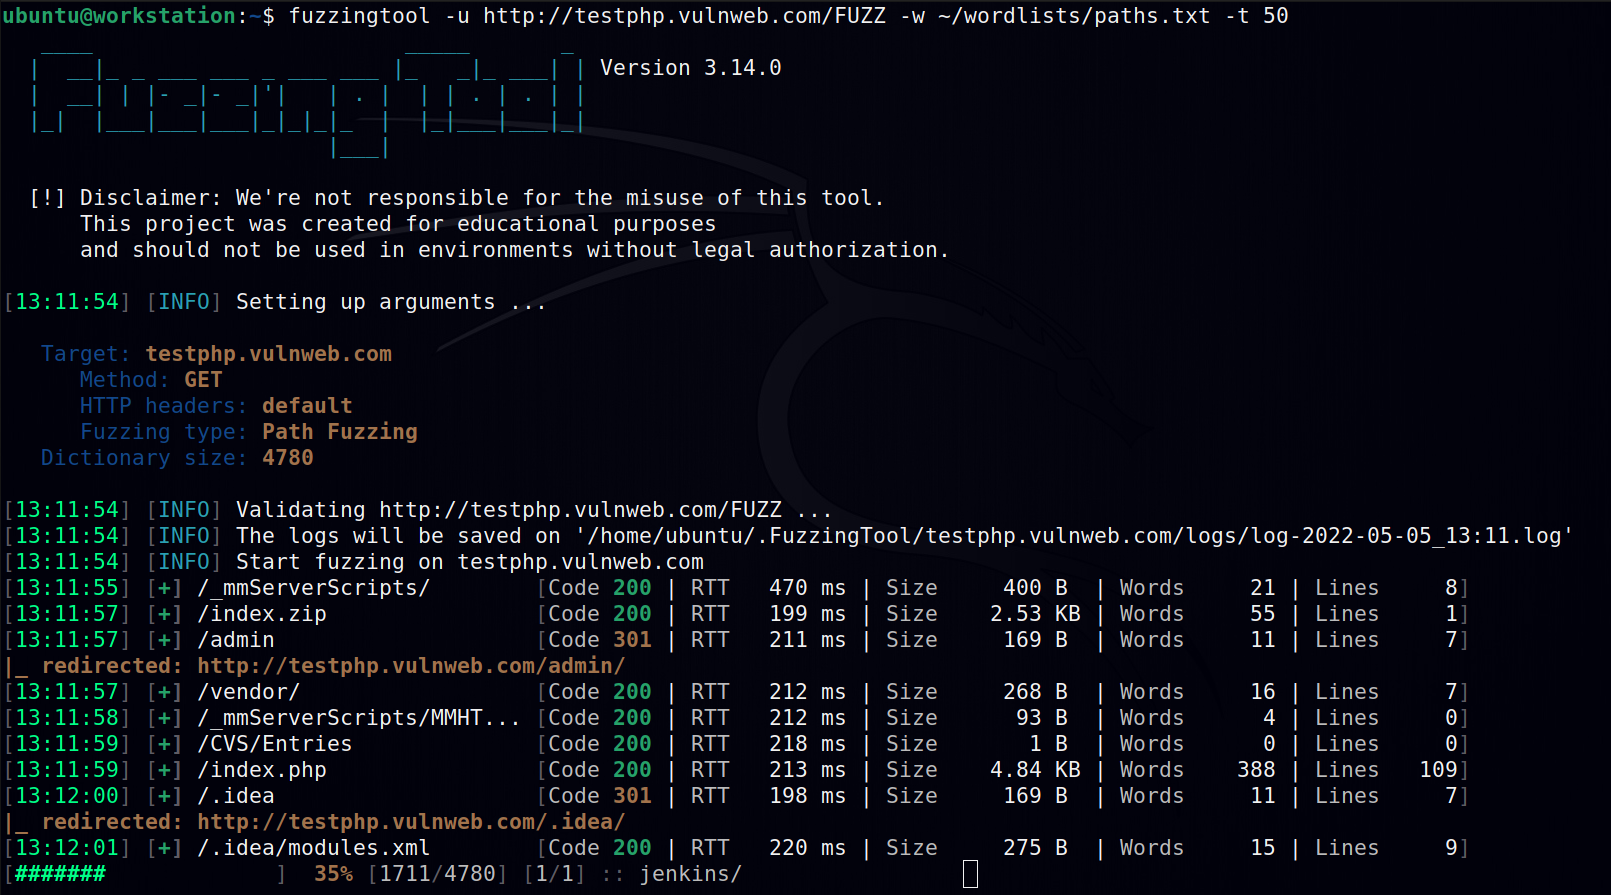 nescau-ufla/fuzzingtool
Software for fuzzing, used on web application pentestings.