


 google/honggfuzz
Security oriented software fuzzer. Supports evolutionary, feedback-driven fuzzing based on code coverage (SW and HW based)
 danmcinerney/xsscrapy
XSS spider - 66/66 wavsep XSS detected
 vladko312/sstimap
Automatic SSTI detection tool with interactive interface
 rust-fuzz/cargo-fuzz
Cargo subcommand for coverage-guided Rust fuzzing with libFuzzer: create and run fuzz targets, minimize failures and corpora, and report coverage.
 narfindustries/http-garden
Differential testing framework for HTTP implementations
 google/oss-fuzz-gen
LLM powered fuzzing via OSS-Fuzz.
 angorafuzzer/angora
Coverage-guided fuzzer that uses taint tracking and scalar optimization to solve path constraints without symbolic execution, improving branch…
 trailofbits/polytracker
An LLVM-based instrumentation tool for universal taint tracking, dataflow analysis, and tracing.
 google/buzzer
eBPF fuzzer toolchain for generating random eBPF programs and validating kernel verifier/runtime behavior. Supports coverage-guided fuzzing and…
 gbrindisi/xsssniper
An automatic XSS discovery tool
 hackmanit/tinja
TInjA is a CLI tool for testing web pages for template injection vulnerabilities and supports 44 of the most relevant template engines for eight…
 nccgroup/dibf
Windows NT ioctl bruteforcer and modular fuzzer
 r00tkitsmm/pishi
Pishi is a code coverage tool like kcov for macOS.
 tca-iscas/cooper-ndss-2022
A tool for effective testing the binding layer of scripting languages
 dvyukov/centipede
Distributed coverage-guided fuzzing engine compatible with libFuzzer targets; scales to thousands of concurrent jobs, uses sanitizers and corpus…
 momalab/icsfuzz
Instrumented fuzzer for PLC-based ICS control applications, targeting Codesys runtime on Wago controllers to uncover memory corruption and…
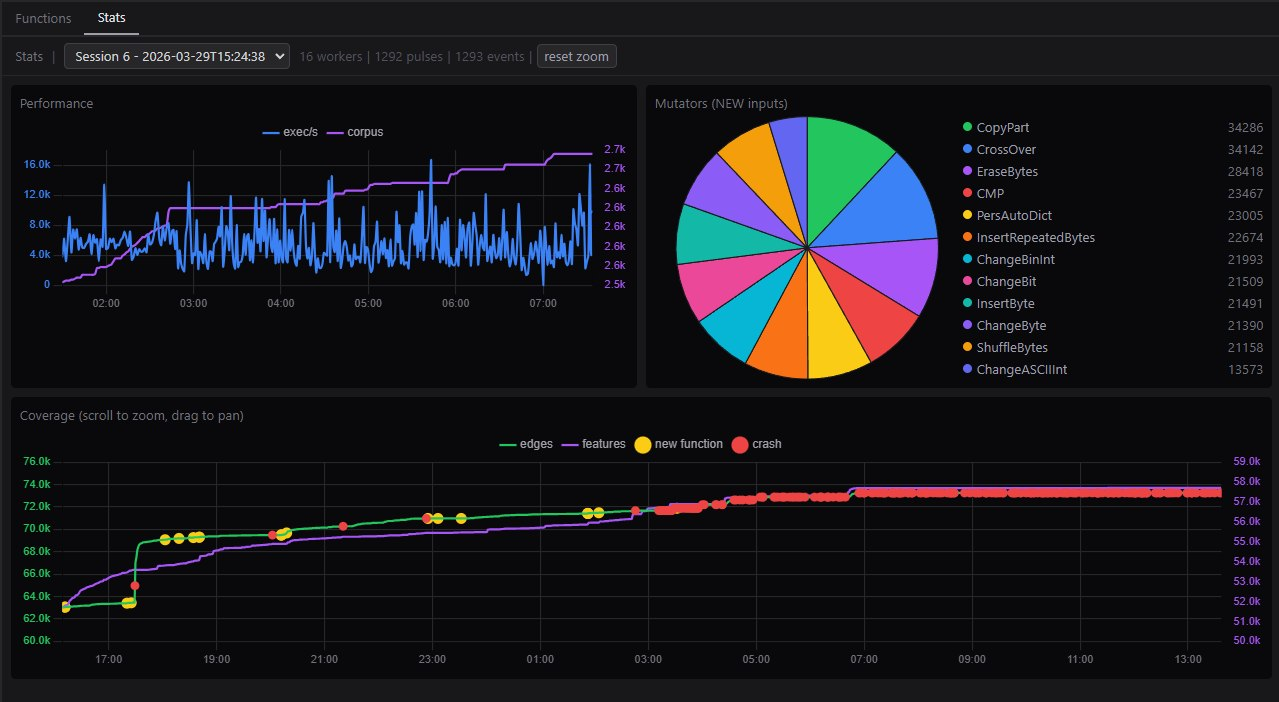 0xbigshaq/apatchy
Fuzzing Framework for Modules in Apache HTTPD Server