

vigolium
 vigolium/vigolium
Vigolium - High-fidelity vulnerability scanner fusing agentic AI with native speed, modularity, and precision
ai-securityapi-security-testingauthentication+9
1.1k3 days ago
vigolium/vigoliumVigolium - High-fidelity vulnerability scanner fusing agentic AI with native speed, modularity, and precision
 endava/cats
Automated REST API fuzzer and negative testing tool for OpenAPI endpoints. Generates, runs, and reports thousands of self-healing tests with no…
 albinowax/activescanplusplus
Burp Suite extension that extends active and passive scanning with checks for host header attacks, XXE, expression language injection, shellshock and…
 chrislockard/api_wordlist
A wordlist of API names for web application assessments
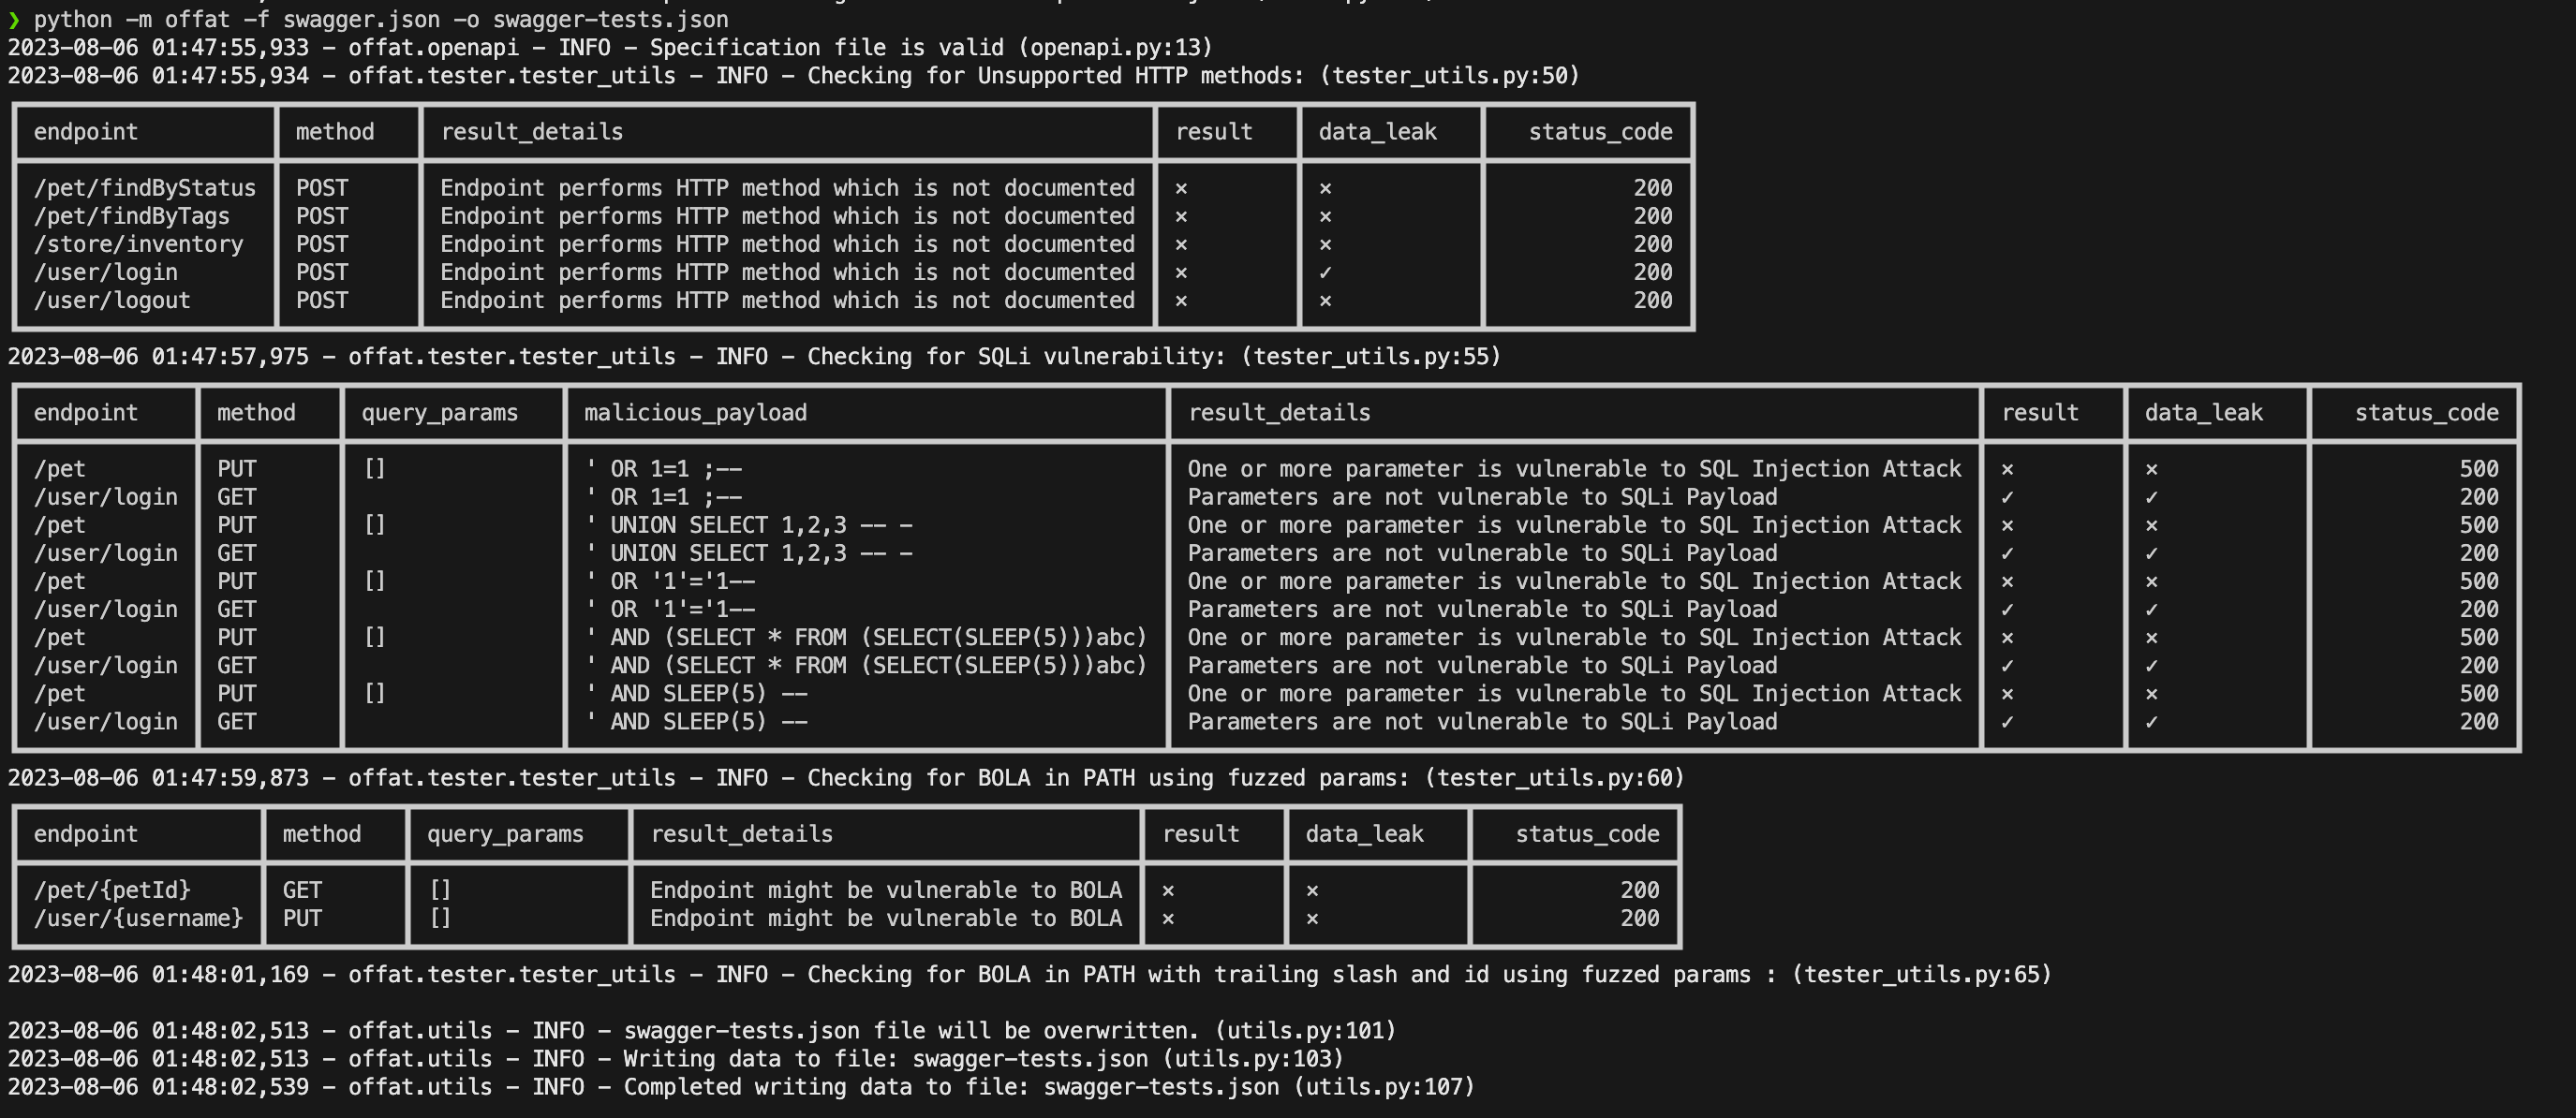 owasp/offat
Automated API security testing tool that generates tests from OpenAPI specs, fuzzes inputs, and checks for OWASP API Top 10 vulnerabilities including…
 mseclab/pyjfuzz
PyJFuzz - Python JSON Fuzzer
 akha-security/akca
Evidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.
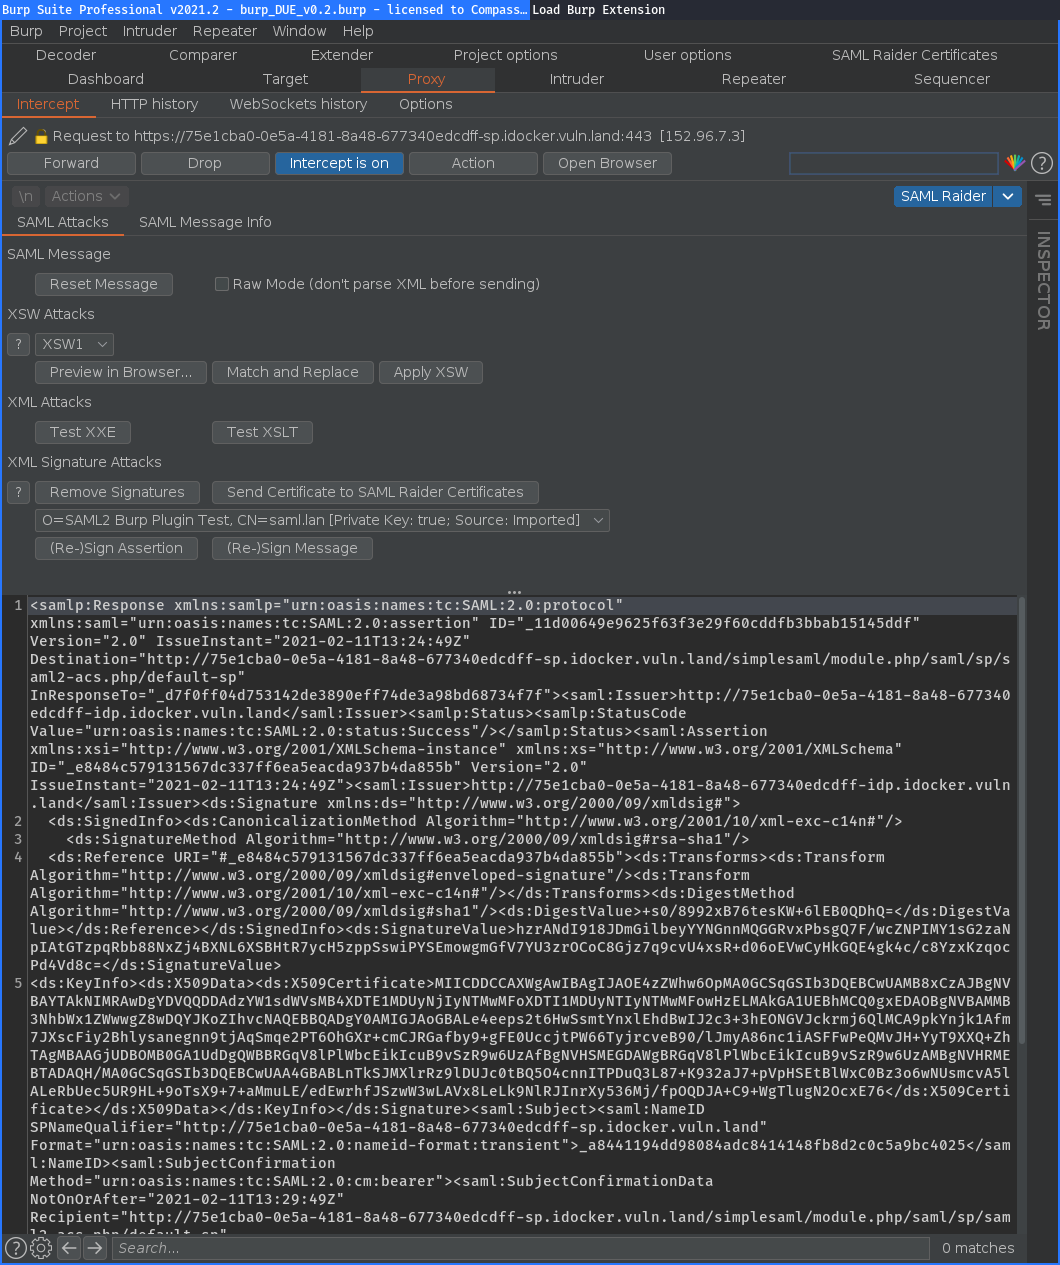 compasssecurity/samlraider
SAML2 Burp Extension
 teycir/burpapisecuritysuite
Burp Suite extension for API security testing with 15 attack types, 108+ payloads, intelligent fuzzing, BOLA/IDOR detection, AI integration, and…
 tno-s3/wuppiefuzz
A coverage-guided REST API fuzzer developed on top of LibAFL
 net-hunter121/api-wordlist
Curated wordlists of API function names, verbs, and nouns for fuzzing web application endpoints with Burp Suite Intruder.
 hellsender01/llmmap
Automated prompt injection testing framework for LLM-integrated applications with dual-LLM architecture.
 moopinger/smugglefuzz
A rapid HTTP downgrade smuggling scanner written in Go.
 forefy/reburp
A Burp Suite extension that exposes the full Montoya API as a local REST API, with Swagger UI
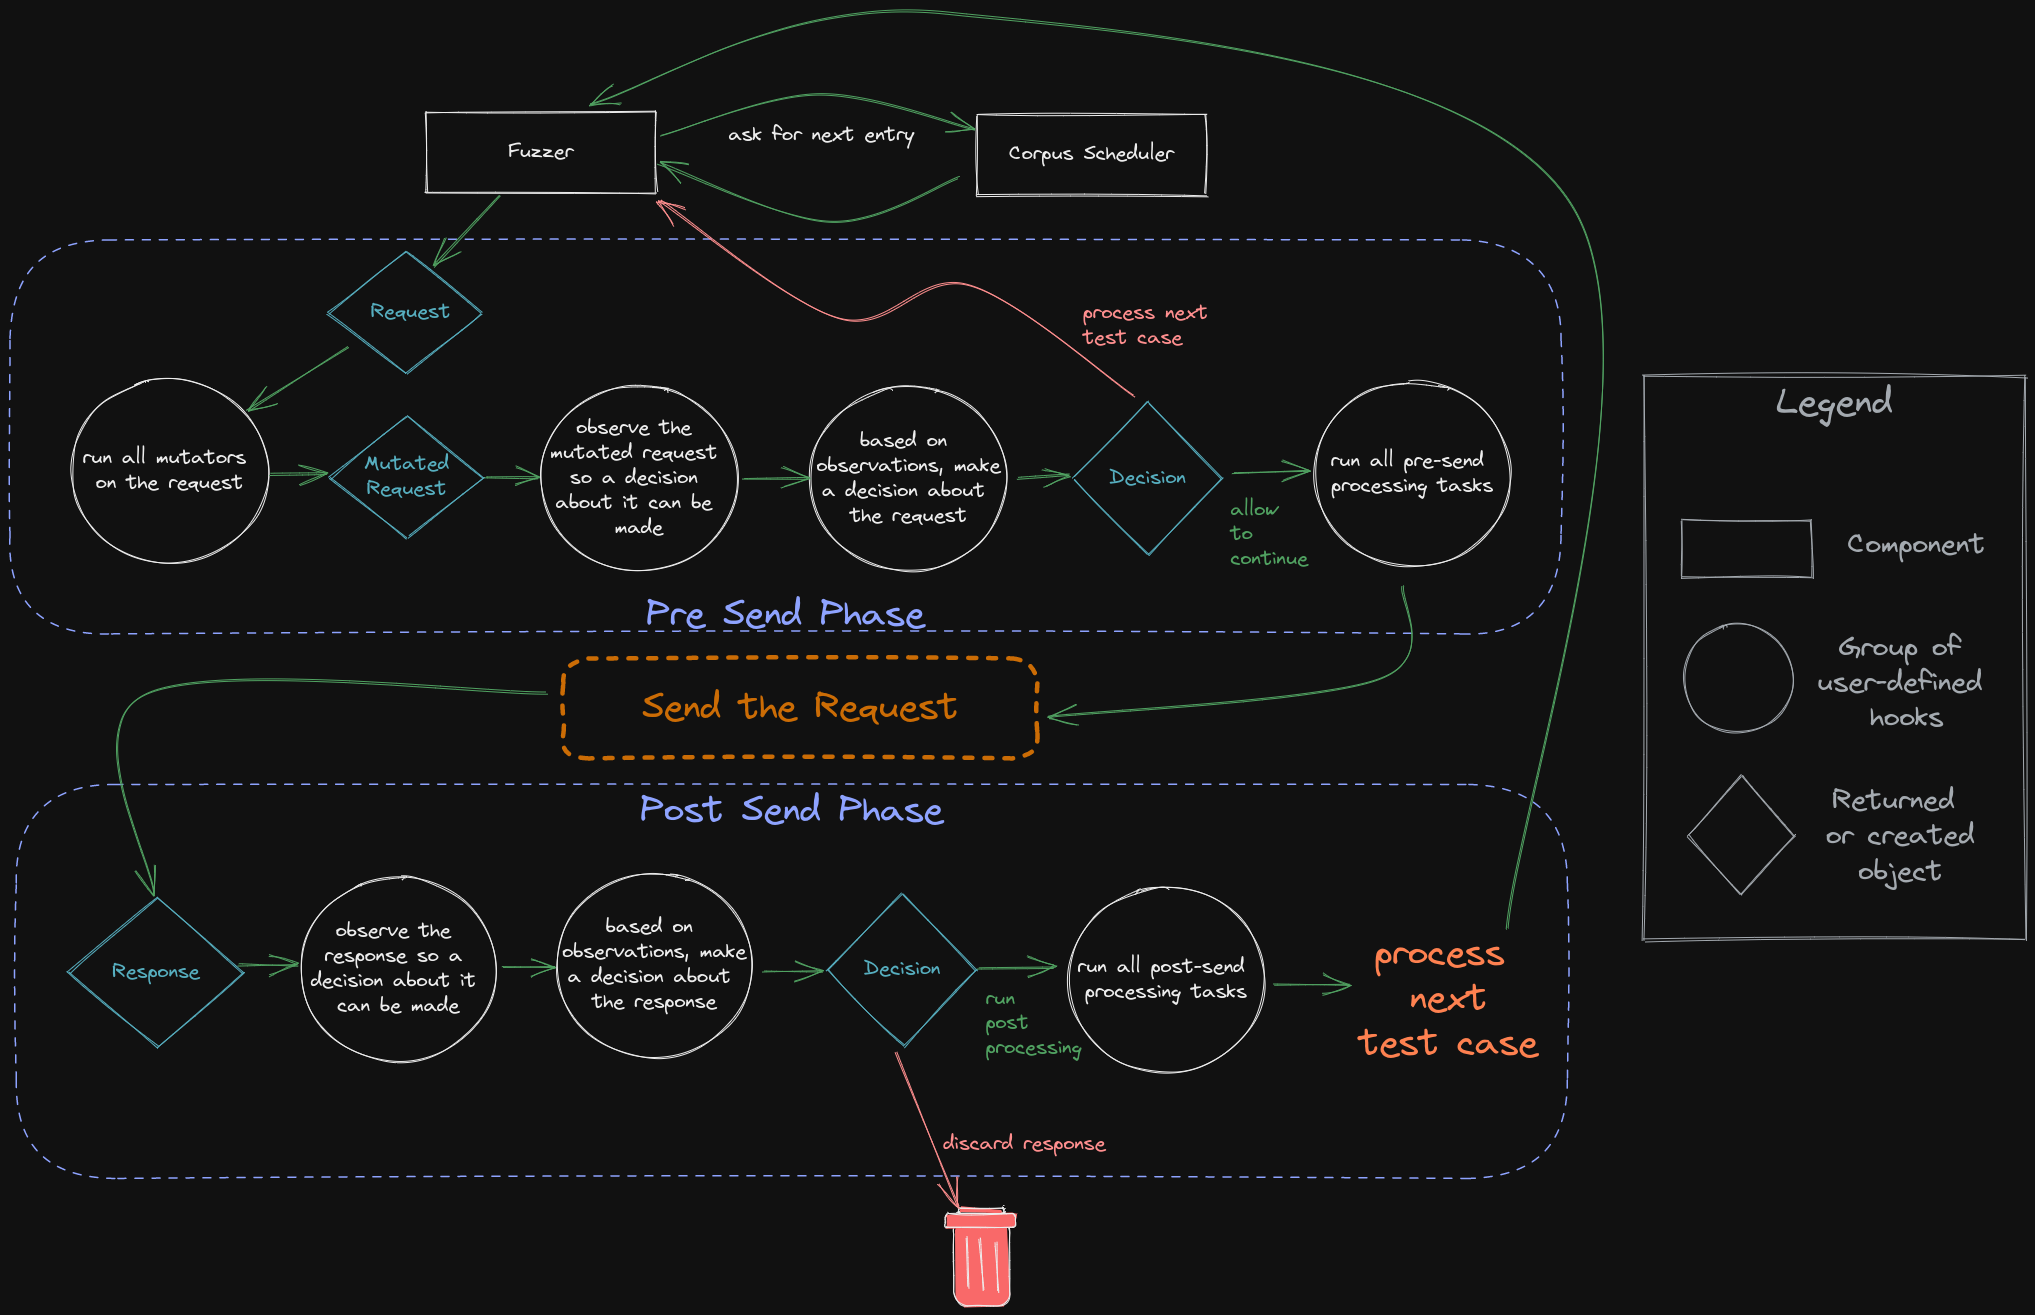 epi052/feroxfuzz
Build structure-aware black-box HTTP fuzzers in Rust with composable mutators, schedulers, observers, deciders, and processors for custom web and API…
 hackinglz/maps_scanner
MAPS cloud scanner and response parser for Microsoft Defender research.
 piratesshield/apiharvester
The one shot API attacker tool - finds the API url from the given root simulate the automated attacks
 raz0r/burp-radamsa
Radamsa fuzzer extension for Burp Suite