extended-ssrf-search
 damian89/extended-ssrf-search
Smart ssrf scanner using different methods like parameter brute forcing in post and get...
fuzzingpenetration-testingvulnerability-scanners+1
277
damian89/extended-ssrf-searchSmart ssrf scanner using different methods like parameter brute forcing in post and get...
 internon/inter-recon
Script to perform automatic initial web and vulnerability recon
 sexyshoelessgodofwar/cve-2025-47256
Stack overflow in LibXMP
 akha-security/akca
Evidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.
 vitaliy-grigoriev/protocol-analyzer
Fuzz testing framework for network protocols.
 cao-wuhui/cve-2025-69720
Advisory for CVE-2025-69720: stack-based buffer overflow in GNU ncurses infocmp (CWE-121)
 xmendez/wfuzz
Modular web fuzzer for automated security testing. Injects payloads into any HTTP request field to discover vulnerabilities, brute-force parameters,…
 devanshbatham/openredirex
A fuzzer for detecting open redirect vulnerabilities
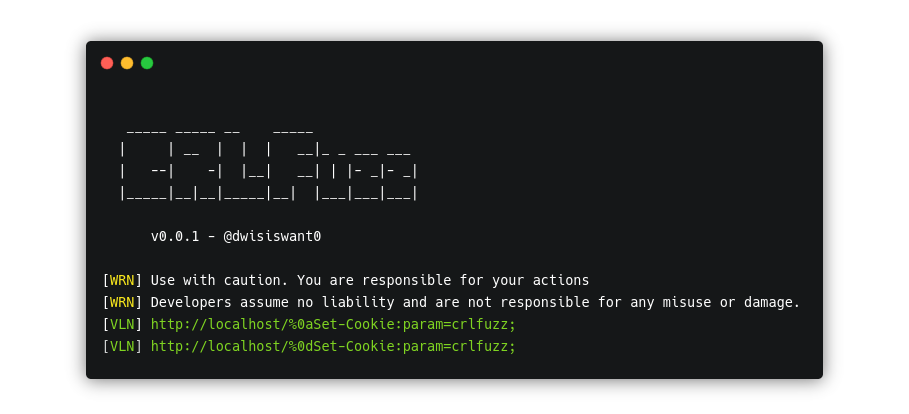 dwisiswant0/crlfuzz
A fast tool to scan CRLF vulnerability written in Go
 lc/theftfuzzer
TheftFuzzer is a tool that fuzzes Cross-Origin Resource Sharing implementations for common misconfigurations.
 fcavallarin/htcap
htcap is a web application scanner able to crawl single page application (SPA) recursively by intercepting ajax calls and DOM changes.
 dwisiswant0/ppfuzz
A fast tool to scan client-side prototype pollution vulnerability written in Rust. 🦀
 sjkim1127/reversecore_mcp
A security-first MCP server that empowers AI agents to perform automated reverse engineering, malware analysis, forensics, vulnerability research,…
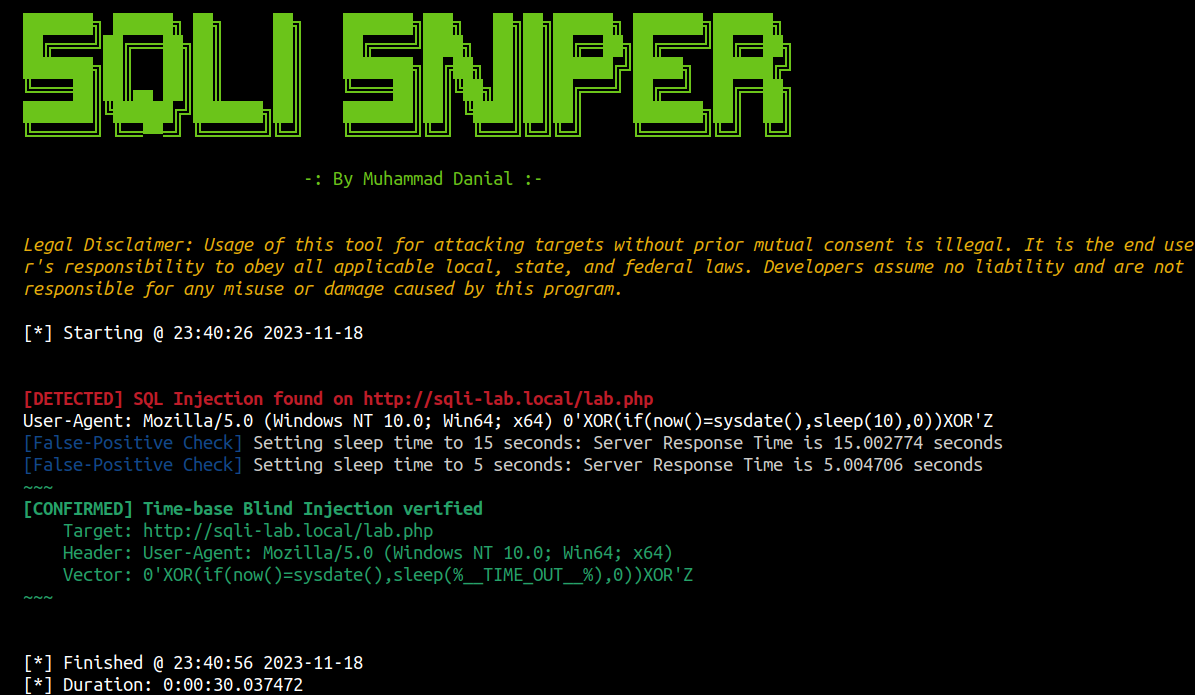 danialhalo/sqlisniper
Advanced Time-based Blind SQL Injection fuzzer for HTTP Headers
 brum3ns/firefly
High-performance black-box fuzzer for web applications with built-in payload engine, request verification, tampering, encoding, and advanced…
 andreiverse/vaf
Multi-threaded web fuzzer for URL path, HTTP header, and POST data brute-forcing with proxy support, status code filtering, and reflexive content…
 nescau-ufla/fuzzingtool
Software for fuzzing, used on web application pentestings.