
Archived
peafl64
 sentinel-one/peafl64
Static Binary Instrumentation tool for Windows x64 executables
binary-analysisdynamic-code-analysisfuzzing+2
207
 ttdennis/fpicker
Frida-based in-process fuzzing suite with AFL++ proxy, standalone active/passive modes, and shared memory communication for high-performance…
 fatmo666/cve-2023-38545-libcurl-socks5-heap-buffer-overflow
Proof-of-concept exploit for CVE-2023-38545, a heap buffer overflow in libcurl's SOCKS5 proxy handshake triggered via a malicious HTTP 301 redirect…
 dbrugman/cve-2023-38545-poc
Proof-of-concept for CVE-2023-38545 heap buffer overflow in curl's SOCKS5 proxy handling, demonstrating exploitation via rate-limit buffer reduction.
 jvbotelho/cve-2026-69243-poc-aiohttp-smuggling
Reproduces aiohttp CWE-444 request smuggling via rejected WebSocket upgrades, with Python/Rust payloads and Docker lab demonstrating proxy…
 starrynightsecurity/cve-2025-54574-squid-heap-buffer-overflow
Vulnerability Found on Squid Proxy.
 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
 hahwul/gori
A fast, keyboard-driven HTTP intercepting proxy and hacking & pentesting toolkit for the terminal.
 pennacle-security/summit
Open-source web security testing platform: proxy, scanner and fuzzer in one CLI. By Pennacle Security.
 0xmarik/aresius
Native HTTP/HTTPS interception proxy for penetration testers and bug bounty hunters with live request tampering, request replay, high-speed fuzzing,…
 ericmtzmtz/pwnproxy
An open, local-first security testing platform for pentesters, AI agents, CI/CD pipelines, and teams.


 ticarpi/jwt_tool
:snake: A toolkit for testing, tweaking and cracking JSON Web Tokens
 s0md3v/arjun
HTTP parameter discovery tool that finds valid query parameters for URL endpoints using a large dictionary, supporting GET/POST/JSON/XML requests,…
 wapiti-scanner/wapiti
Web vulnerability scanner written in Python3
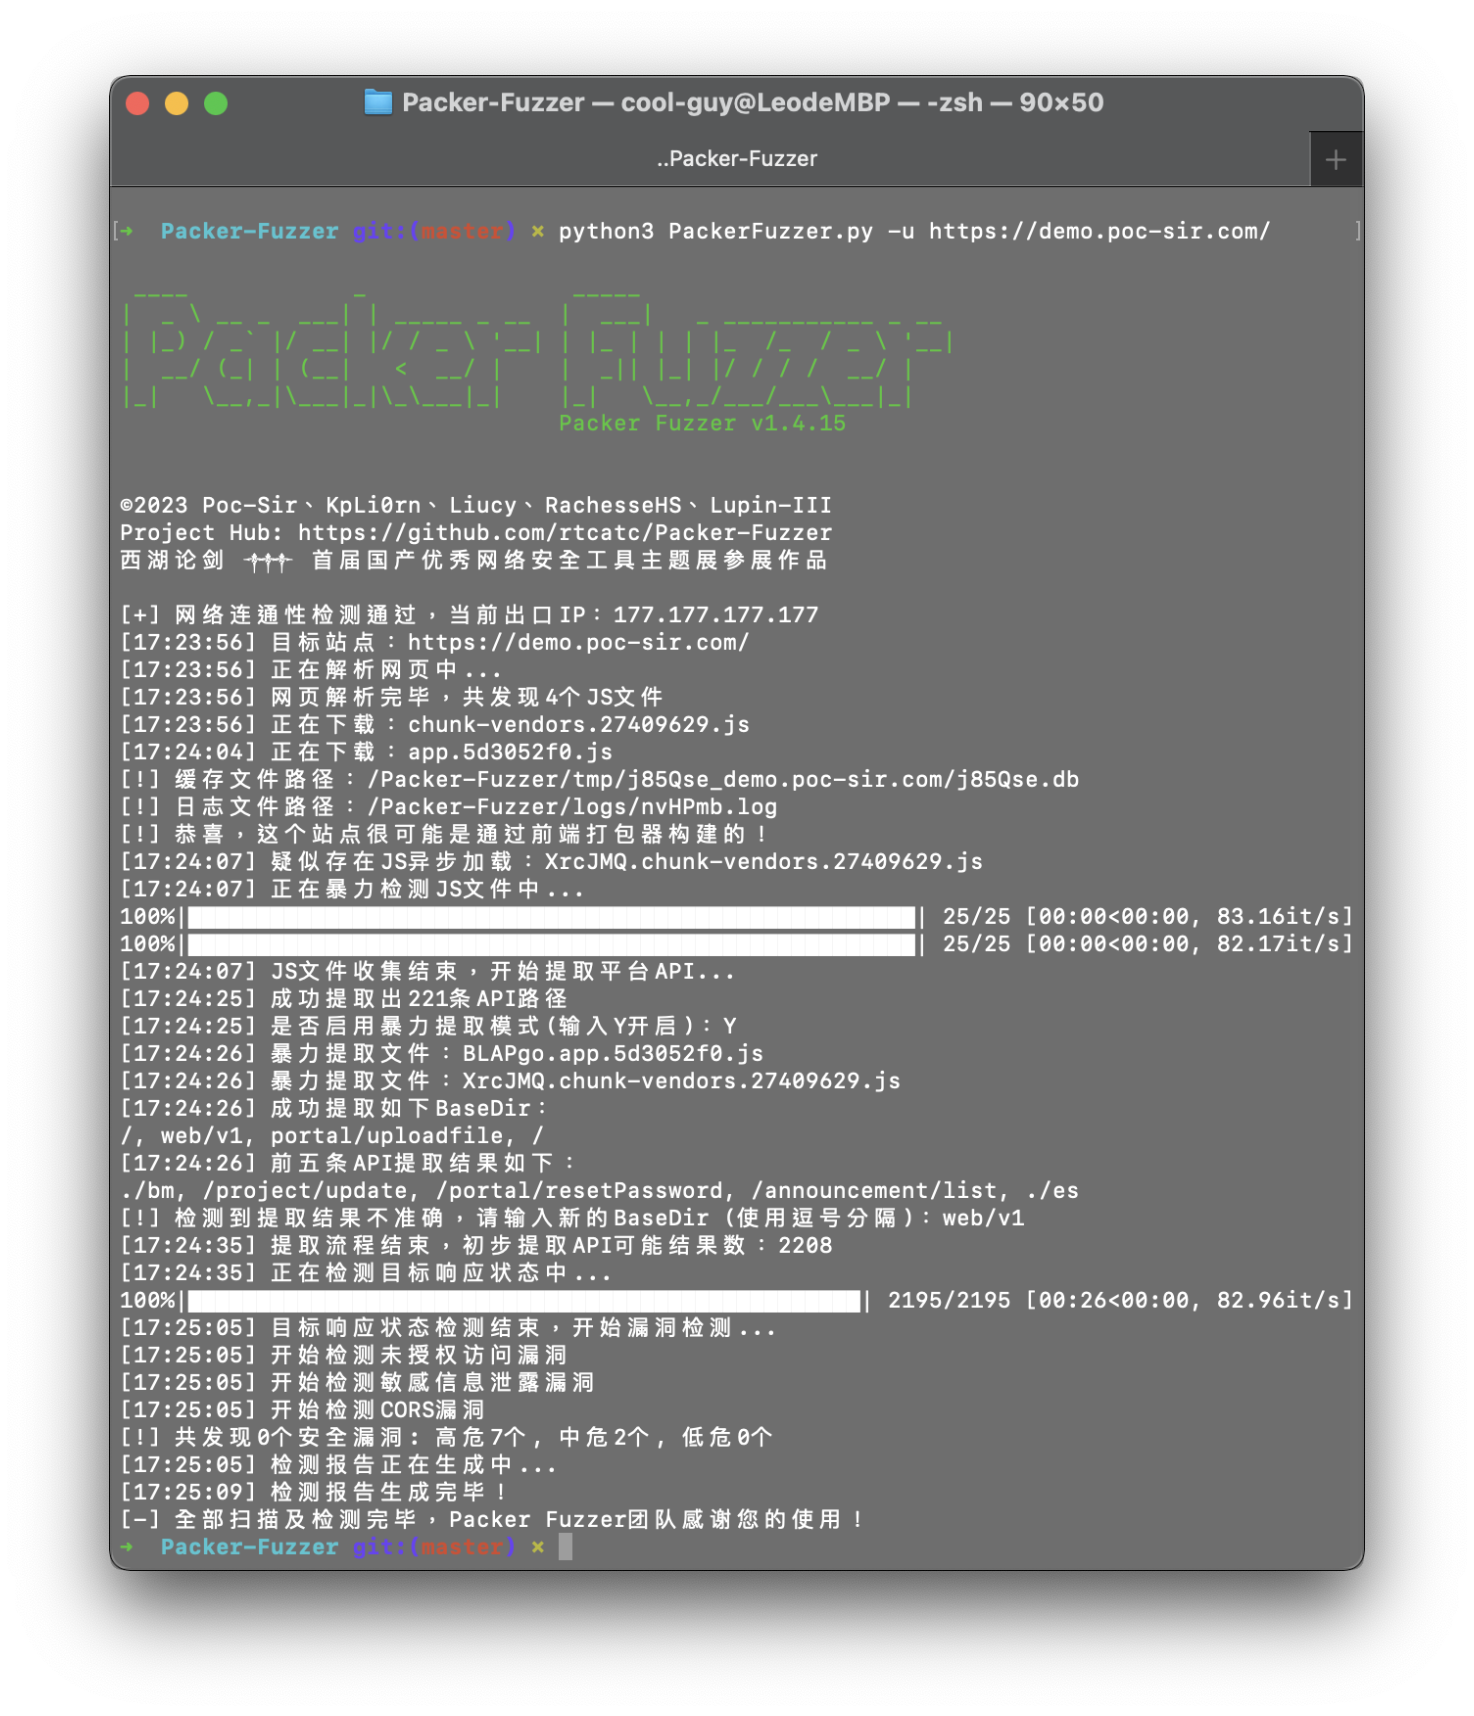 rtcatc/packer-fuzzer
Packer Fuzzer is a fast and efficient scanner for security detection of websites constructed by javascript module bundler such as Webpack.