extract75-cve-2020-13995

Control flow hijack exploit for CVE-2020-13995 with Docker-based deployment and Mayhem fuzzing integration for automated vulnerability testing.

Control flow hijack exploit for CVE-2020-13995 with Docker-based deployment and Mayhem fuzzing integration for automated vulnerability testing.

Mass exploiter for CVE-2020-6308 with multi-worker support, enabling automated exploitation of vulnerable SAP NetWeaver systems.

Collection of fuzzers built with libFuzzer and AddressSanitizer for automated bug detection in C/C++ code.

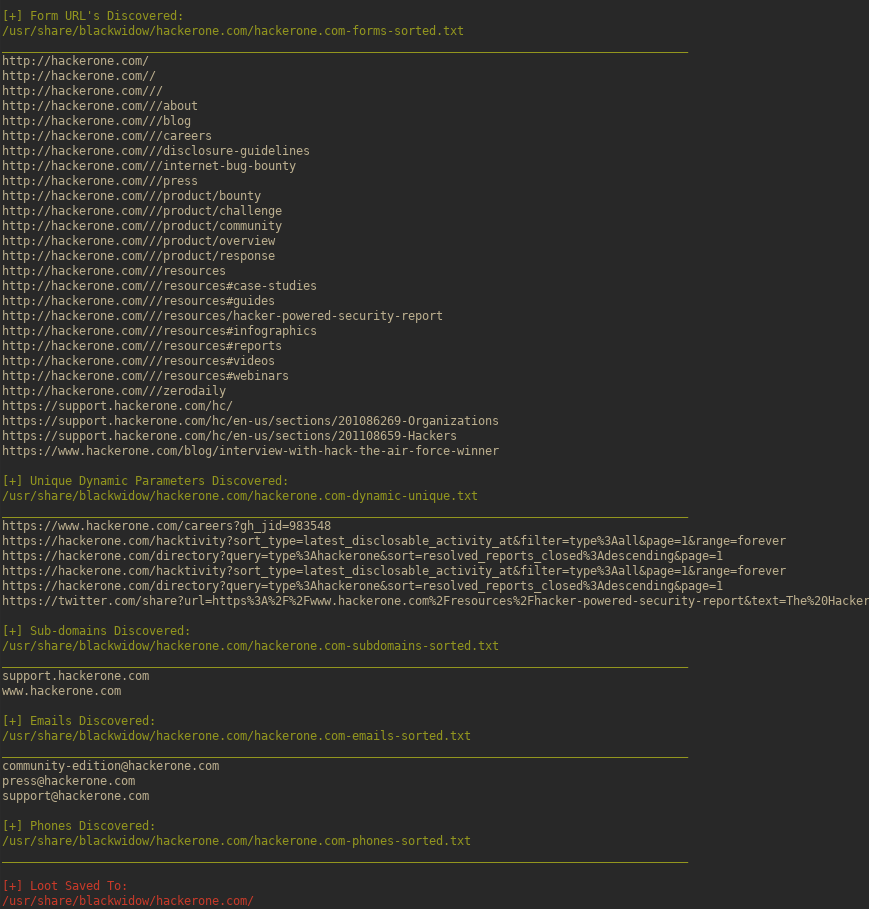
Vajra is a highly customizable target and scope based automated web hacking framework to automate boring recon tasks and same scans for multiple…

Coverage-guided fuzzer for UEFI NVRAM variables using Qiling emulation and AFL++ to discover firmware vulnerabilities through automated input…

A Python based web application scanner to gather OSINT and fuzz for OWASP vulnerabilities on a target website.

Static binary vulnerability scanner using abstract interpretation on Ghidra Pcode. Detects CWE classes like buffer overflows, use-after-free, and…

AegisGraph: graph-based application-layer assessment evidence platform for Secure Messaging Applications (SMAs). DARPA ASEMA HR0011SB20254-12 Tier 3…


Security oriented software fuzzer. Supports evolutionary, feedback-driven fuzzing based on code coverage (SW and HW based)

XSS spider - 66/66 wavsep XSS detected

Automatic SSTI detection tool with interactive interface

Cargo subcommand for coverage-guided Rust fuzzing with libFuzzer: create and run fuzz targets, minimize failures and corpora, and report coverage.

Differential testing framework for HTTP implementations

LLM powered fuzzing via OSS-Fuzz.

Web application security scanner created by lcamtuf for google - Unofficial Mirror

Coverage-guided fuzzer that uses taint tracking and scalar optimization to solve path constraints without symbolic execution, improving branch…