
firefly
 brum3ns/firefly
High-performance black-box fuzzer for web applications with built-in payload engine, request verification, tampering, encoding, and advanced…
fuzzingpenetration-testingvulnerability-scanners+1
442
brum3ns/fireflyHigh-performance black-box fuzzer for web applications with built-in payload engine, request verification, tampering, encoding, and advanced…
 gbrindisi/xsssniper
An automatic XSS discovery tool
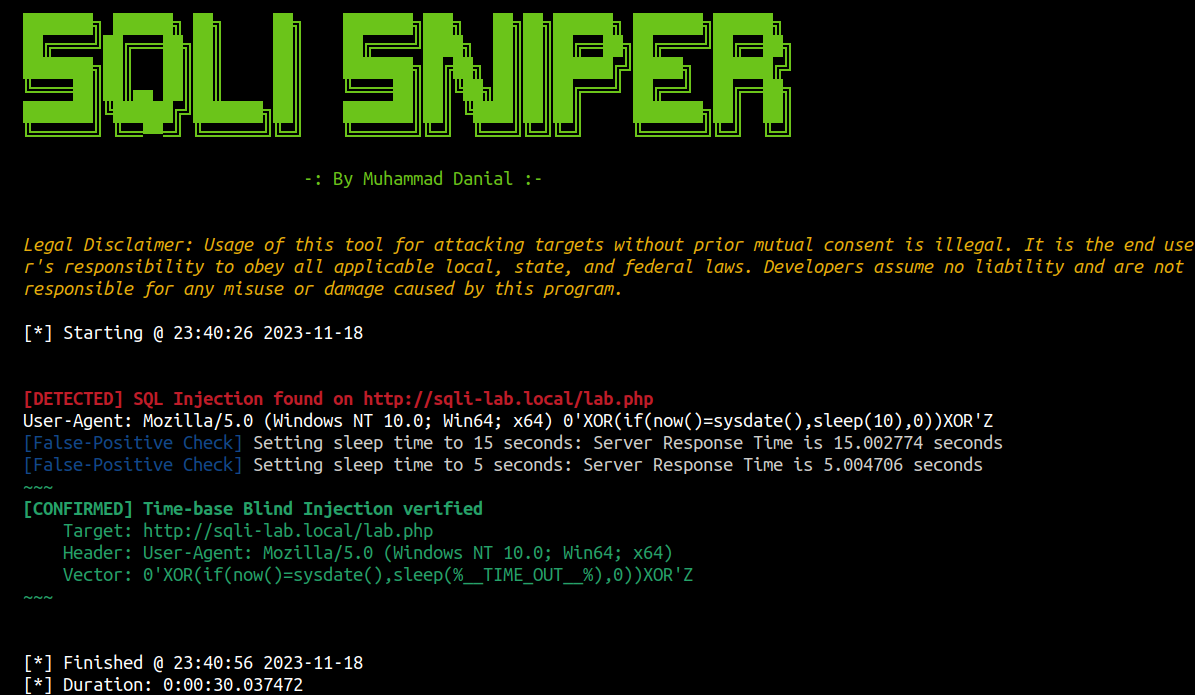 danialhalo/sqlisniper
Advanced Time-based Blind SQL Injection fuzzer for HTTP Headers
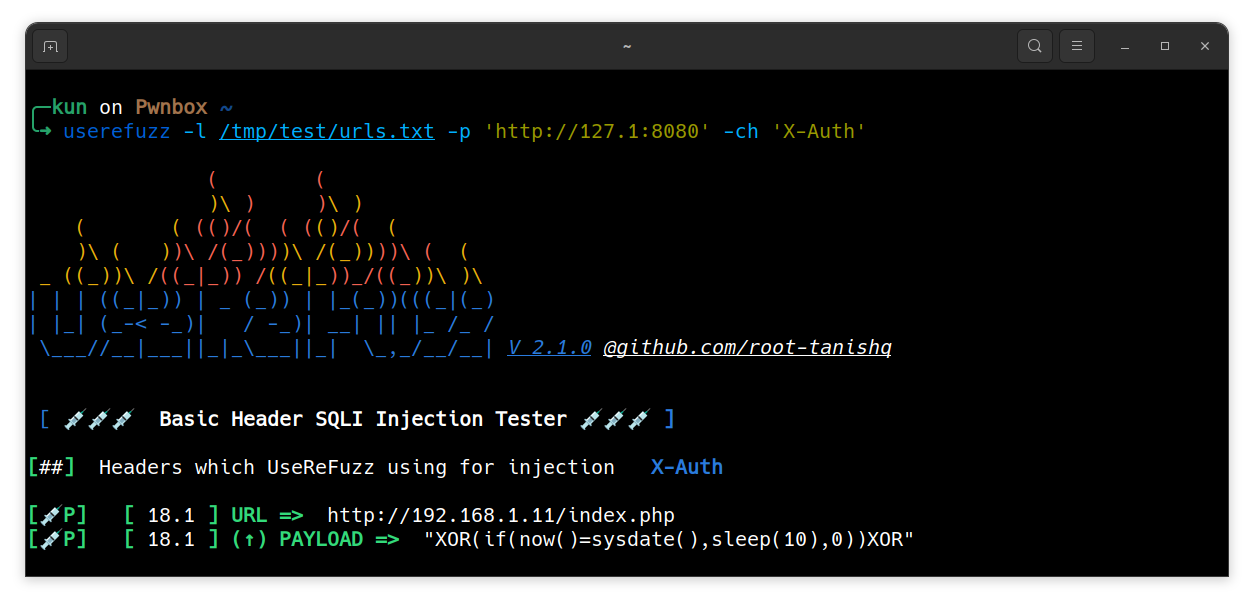 root-tanishq/userefuzz
User-Agent , X-Forwarded-For and Referer SQLI Fuzzer
 andreiverse/vaf
Multi-threaded web fuzzer for URL path, HTTP header, and POST data brute-forcing with proxy support, status code filtering, and reflexive content…
 mindpatch/lorsrf
Fast CLI tool to find the parameters that can be used to find SSRF or Out-of-band resource load :artificial_satellite: :crab:
 nescau-ufla/fuzzingtool
Software for fuzzing, used on web application pentestings.
 ryandamour/ssrfuzz
SSRFuzz is a tool to find Server Side Request Forgery vulnerabilities, with CRLF chaining capabilities
 hakaioffsec/navgix
Multi-threaded Go tool to detect nginx alias traversal vulnerabilities using heuristic and brute-force techniques for identifying vulnerable…
 juanschallibaum/cve-2024-38473-nuclei-template
Nuclei template to detect Apache servers vulnerable to CVE-2024-38473
 ethicalhackingplayground/crlfmap
CRLFMap is a tool to find HTTP Splitting vulnerabilities
 soltanali0/cve-2024-40725
exploit CVE-2024-40725 (Apache httpd) with
 d4rk007/f5-big-ip-cve-2020-5902-mass-exploiter
Mass exploiter for CVE-2020-5902 targeting F5 Big-IP devices, with multi-threaded scanning and exploitation capabilities for unauthenticated remote…
 yahoo/gryffin
Gryffin is a large scale web security scanning platform.
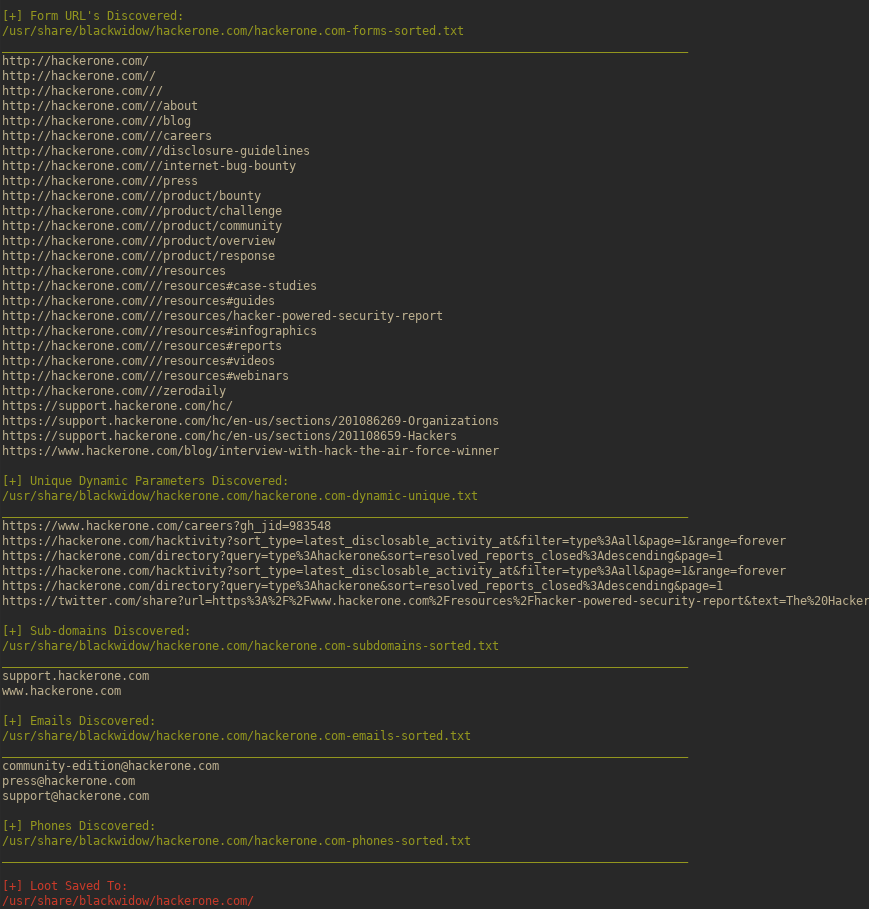 1n3/blackwidow
A Python based web application scanner to gather OSINT and fuzz for OWASP vulnerabilities on a target website.
 akha-security/akca
Evidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.
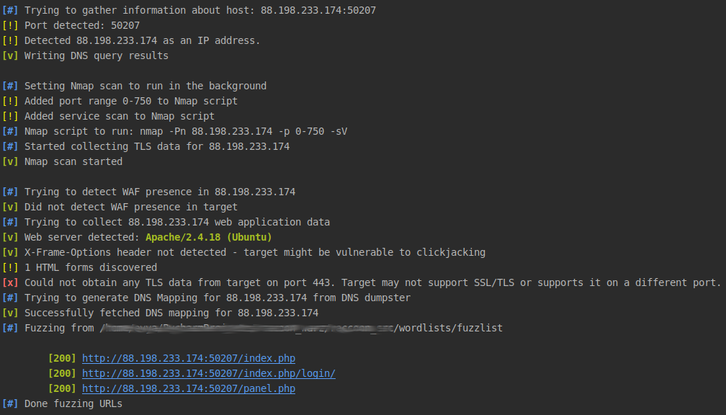 evyatarmeged/raccoon
A high performance offensive security tool for reconnaissance and vulnerability scanning
 gadievron/raptor
Autonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…