
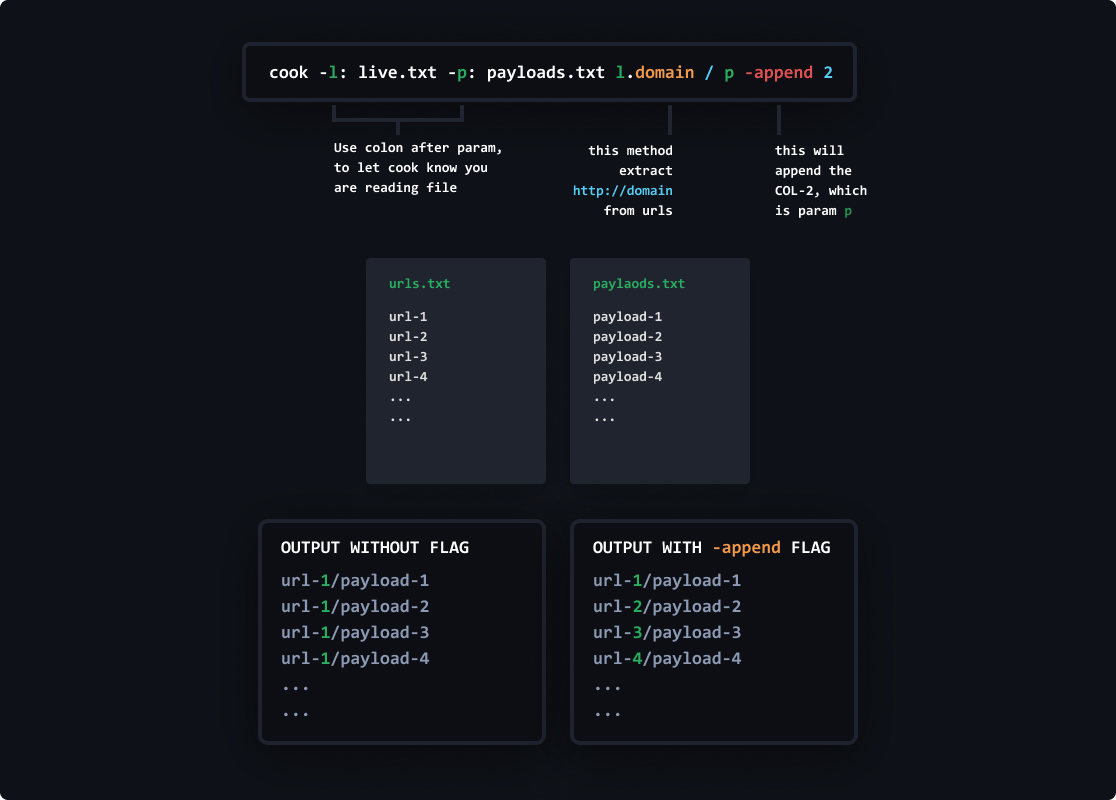
cook
 glitchedgitz/cook
A wordlist framework to fullfill your kinks with your wordlists. For security researchers, bug bounty and hackers.
fuzzingpassword-crackingpenetration-testing+1
1.4k
glitchedgitz/cookA wordlist framework to fullfill your kinks with your wordlists. For security researchers, bug bounty and hackers.
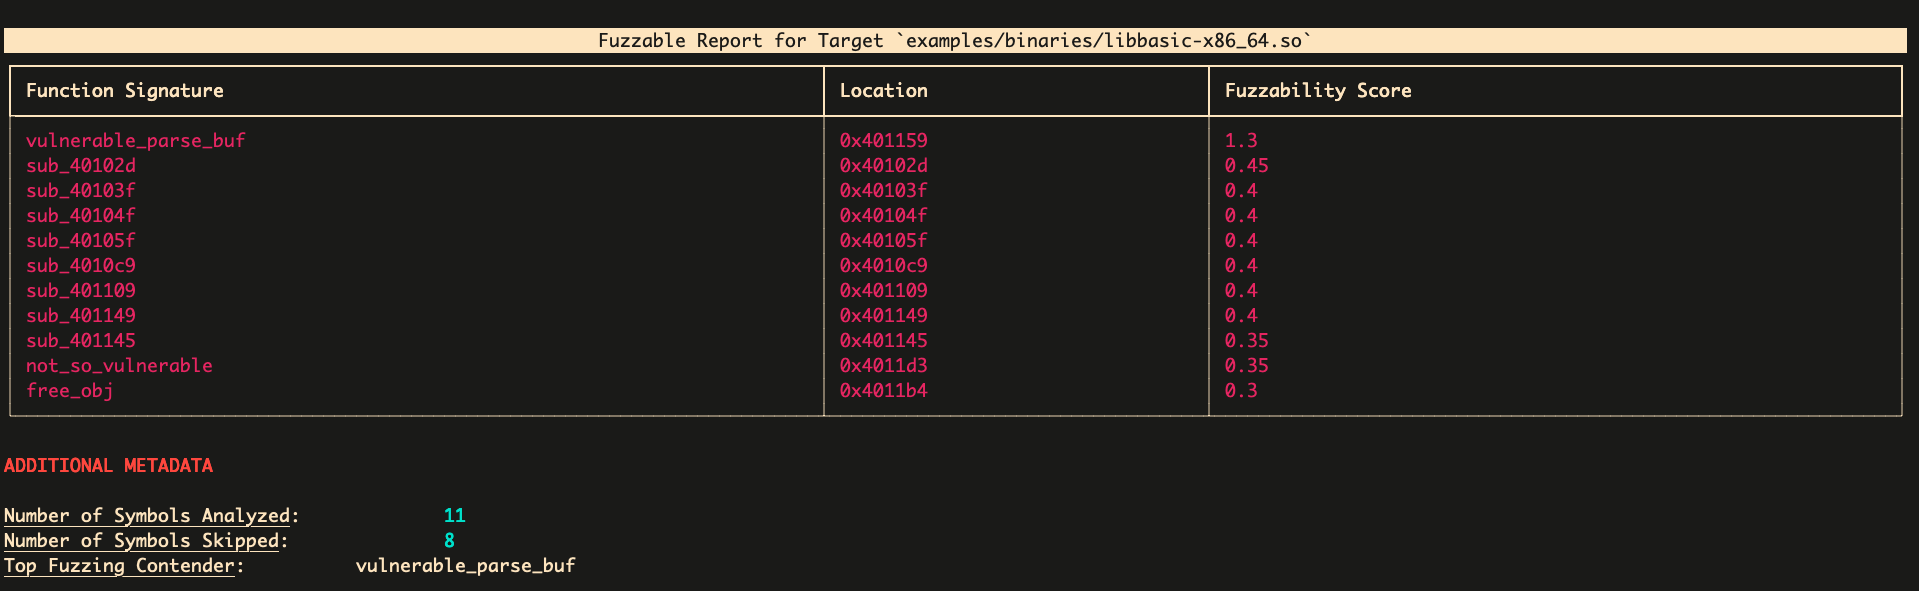 ex0dus-0x/fuzzable
Static analysis framework that identifies fuzzable function targets in source code and binaries, generates harness templates, and integrates with…
 cisco-sas/kitty
Fuzzing framework written in python
 0xricksanchez/fisy-fuzz
This is the full file system fuzzing framework that I presented at the Hack in the Box 2020 Lockdown Edition conference in April.
 oxagast/ansvif
A Not So Very Intelligent Fuzzer: An advanced fuzzing framework designed to find vulnerabilities in C/C++ code.
 s4dhulabs/vimana-framework
Vimana is a modular security framework for auditing Python APIs and Web applications. The plugin-based architecture enables security professionals to…

 gitlab-org/security-products/protocol-fuzzer-ce
This is the community edition of GitLab's protocol fuzzing framework. This framework is based on Peach Fuzzer Professional with some features removed.
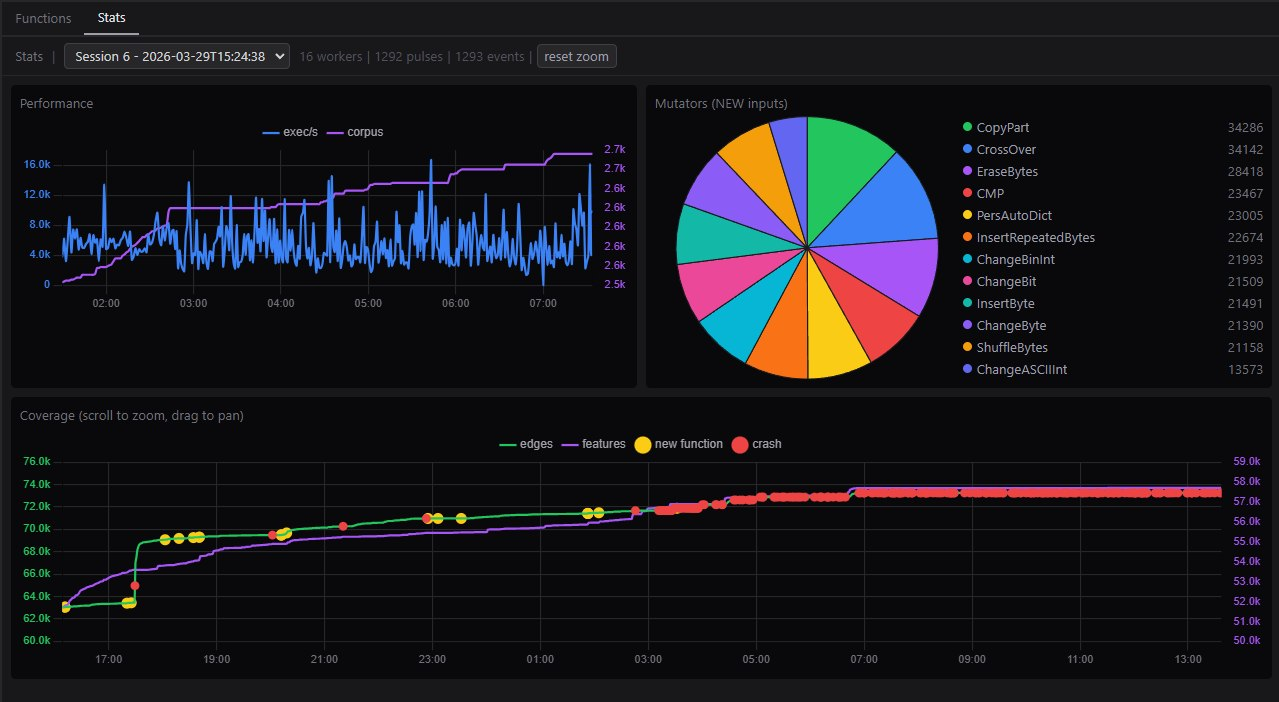 0xbigshaq/apatchy
Fuzzing Framework for Modules in Apache HTTPD Server
 agampreet-singh/redroot
RedRoot is a Python-based, CLI-driven offensive security framework that brings essential red teaming tools into one unified terminal environment.…
 futureslab/binvariants
Register-level invariant-guided fuzzing framework for closed-source binaries, leveraging likely invariant violations to discover crashes and bugs in…
 infiniteloopers/cve-2019-2107
Proof-of-concept exploit for CVE-2019-2107, demonstrating remote code execution via crafted HEVC video on Android media framework. Includes crash…
 hexrom/imagemagick-cve-2017-15277
Proof-of-concept exploit for ImageMagick CVE-2017-15277 memory leak vulnerability, designed for use with the gifoeb fuzzing framework.
 harsh-bothra/bheem
Scope-based reconnaissance automation framework that orchestrates multiple open-source tools for subdomain enumeration, vulnerability scanning, and…
 ioactive/laf
This project intends to provide a series of tools to craft, parse, send, analyze and crack a set of LoRaWAN packets in order to audit or pentest the…
 google/oss-fuzz-gen
LLM powered fuzzing via OSS-Fuzz.
 cisco-talos/mutiny-fuzzer
Network protocol fuzzer that replays PCAP traffic through a mutational engine (Radamsa) to quickly discover vulnerabilities in target hosts via…
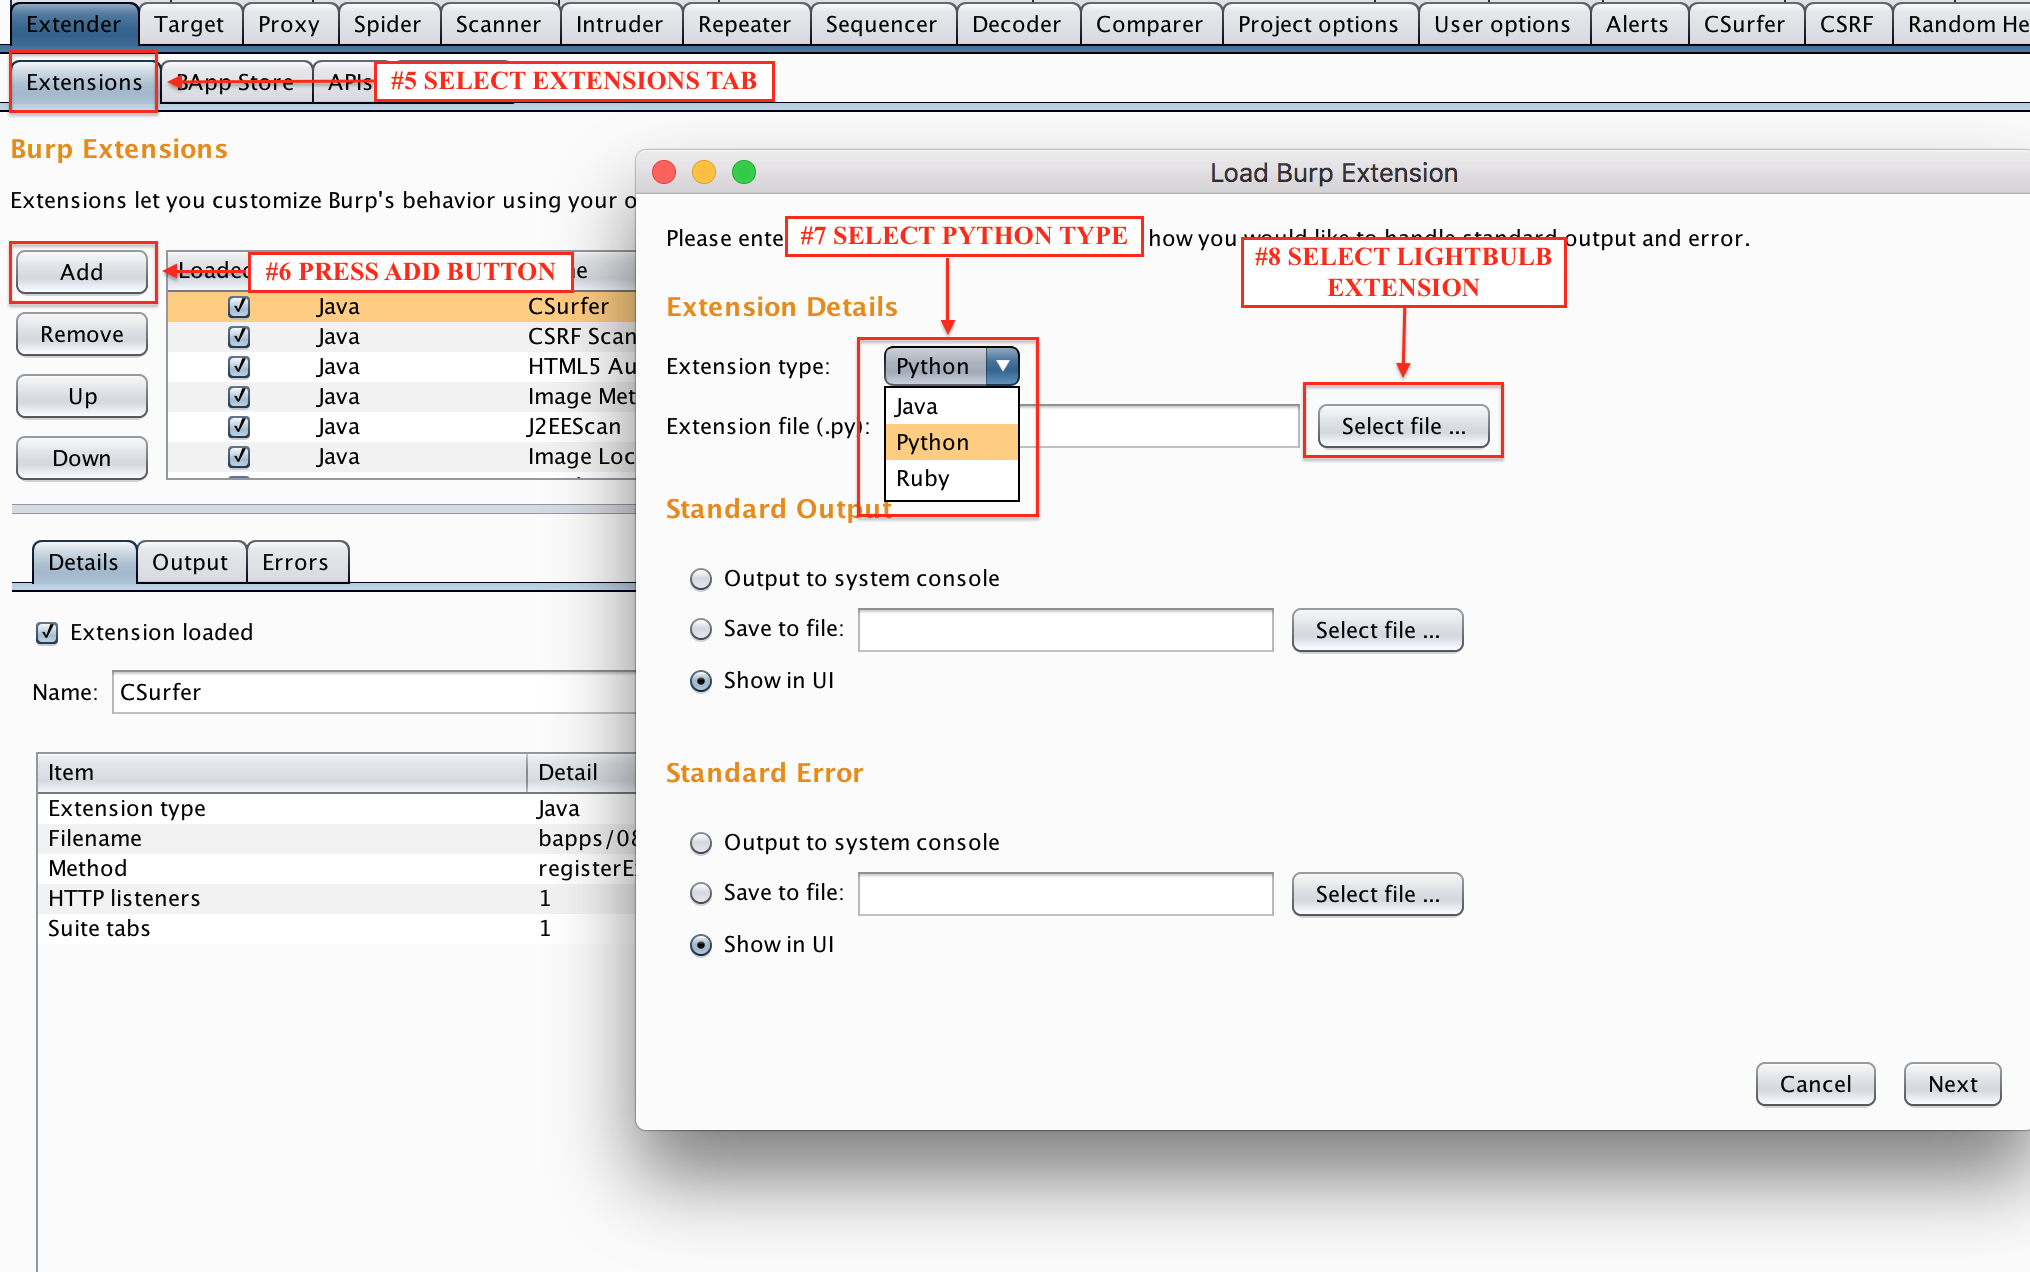 lightbulb-framework/lightbulb-framework
Tools for auditing WAFS