
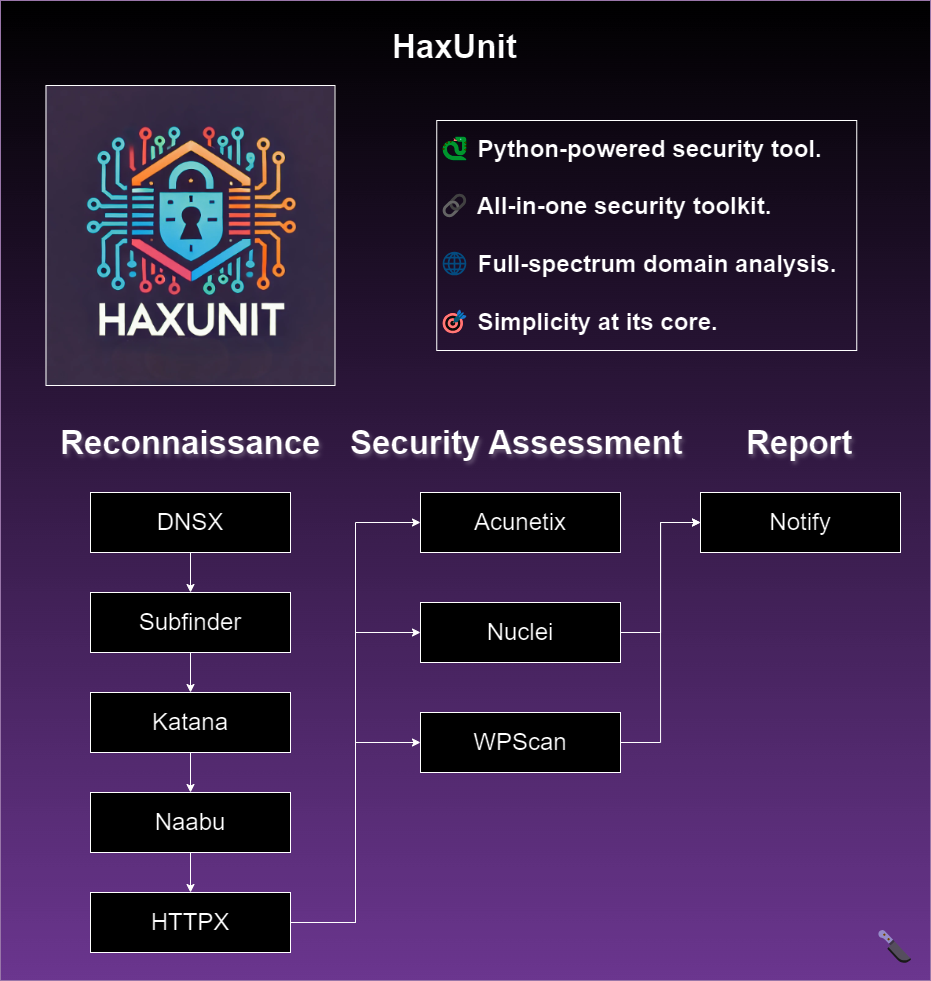
haxunit
 bandit-haxunit/haxunit
Automated web domain reconnaissance and security assessment tool integrating subdomain enumeration, port scanning, vulnerability scanning, and…
ai-securitycrawlerfuzzing+7
331
bandit-haxunit/haxunitAutomated web domain reconnaissance and security assessment tool integrating subdomain enumeration, port scanning, vulnerability scanning, and…
 s_r_e_e_r_a_j/reconhound
ReconHound is a Python-based web reconnaissance tool designed for penetration testers, bug bounty hunters, and ethical hackers. It supports directory…
 harsh-bothra/bheem
Scope-based reconnaissance automation framework that orchestrates multiple open-source tools for subdomain enumeration, vulnerability scanning, and…
 danielmiessler/seclists
Curated collection of wordlists for security assessments, including usernames, passwords, URLs, fuzzing payloads, and sensitive data patterns for…
 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
 vavkamil/awesome-bugbounty-tools
Curated directory of bug bounty tools organized by category: reconnaissance, subdomain enumeration, port scanning, content discovery, exploitation,…
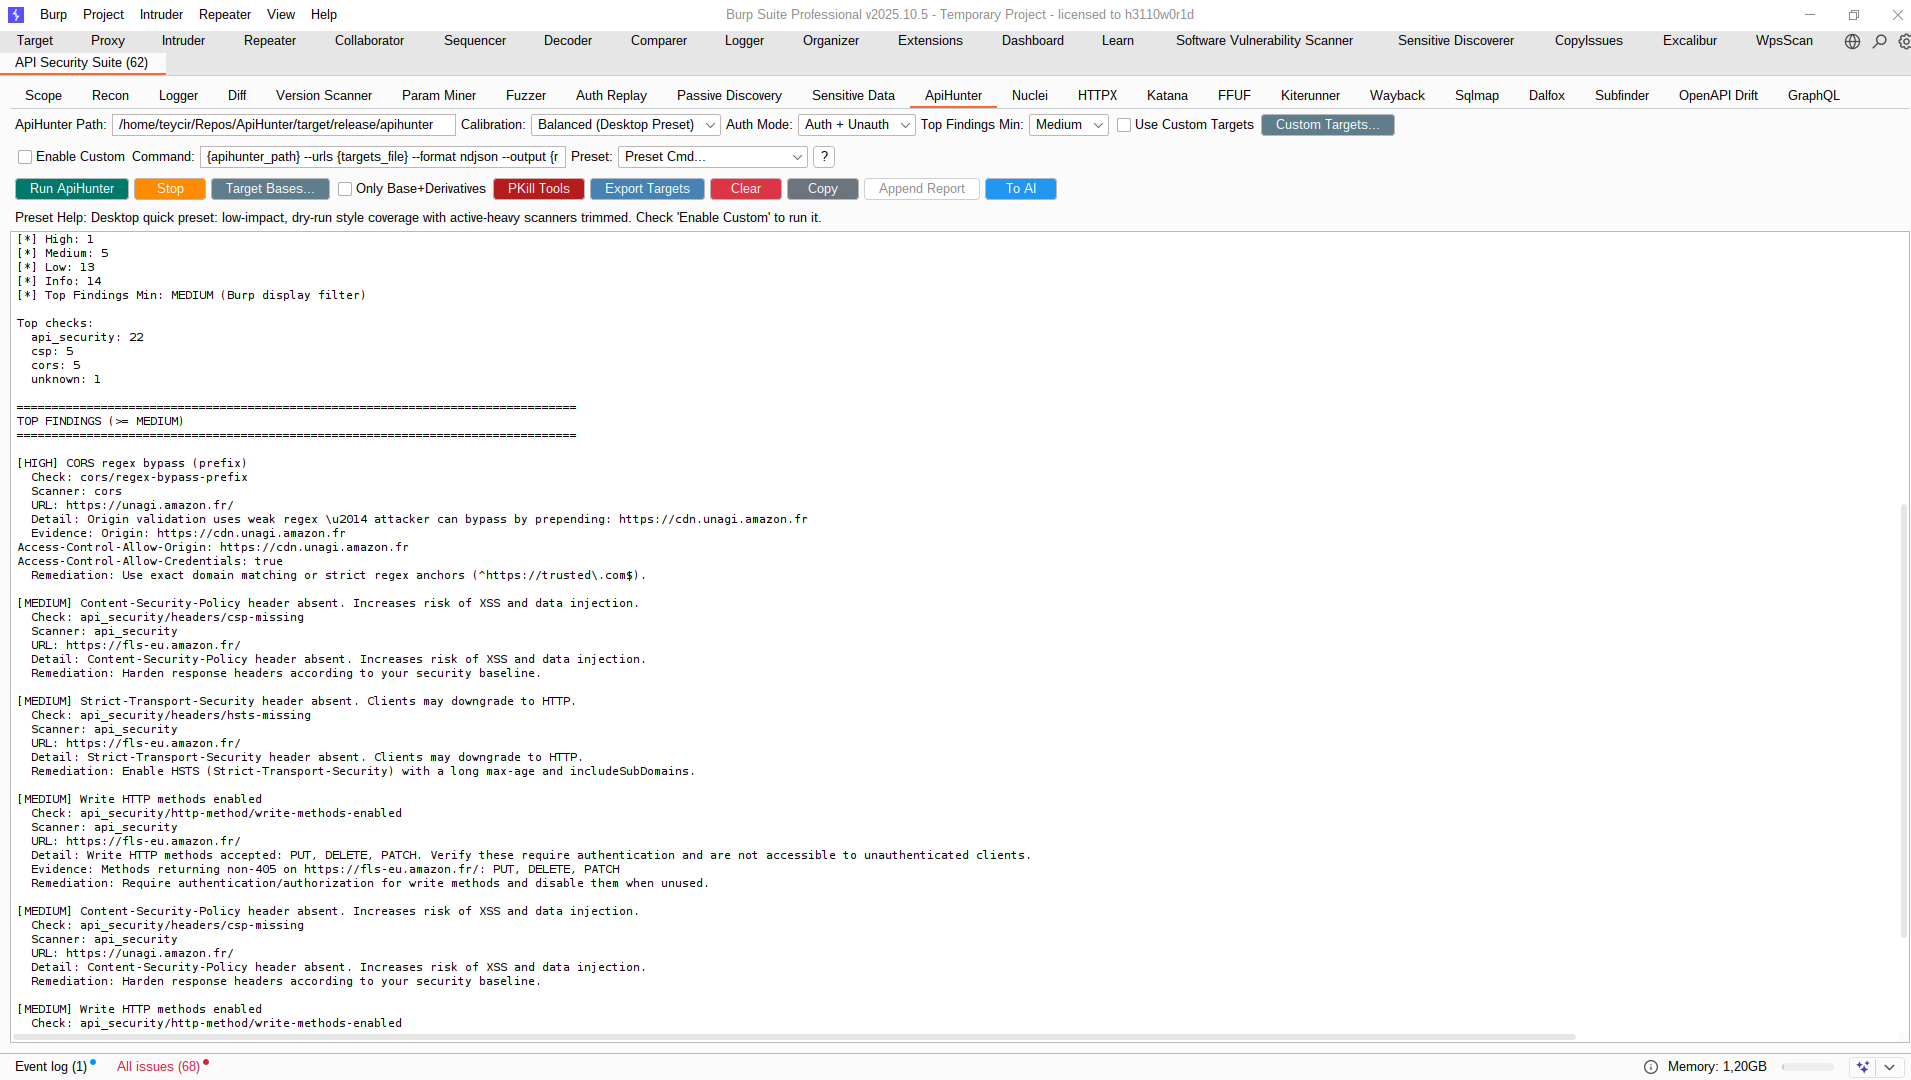 teycir/burpapisecuritysuite
Burp Suite extension for API security testing with 15 attack types, 108+ payloads, intelligent fuzzing, BOLA/IDOR detection, AI integration, and…
 dozermx/argus
Multi-phase reconnaissance and attack-surface scanner that maps domains, IPs, ASNs, cloud assets, and CVEs into a knowledge graph with CVSS scoring…
 hmrumman777-beep/netaudit-iot
Research-driven UPnP vulnerability scanner focusing on libupnp 1.6.19 and CVE-2012-5958.
 oj/gobuster
Directory/File, DNS and VHost busting tool written in Go
 gwen001/pentest-tools
A collection of custom security tools for quick needs.
 elceef/dnstwist
Domain name permutation engine for detecting homograph phishing attacks, typo squatting, and brand impersonation
 ghosttroops/scan4all
Official repository vuls Scan: 15000+PoCs; 23 kinds of application password crack; 7000+Web fingerprints; 146 protocols and 90000+ rules Port…
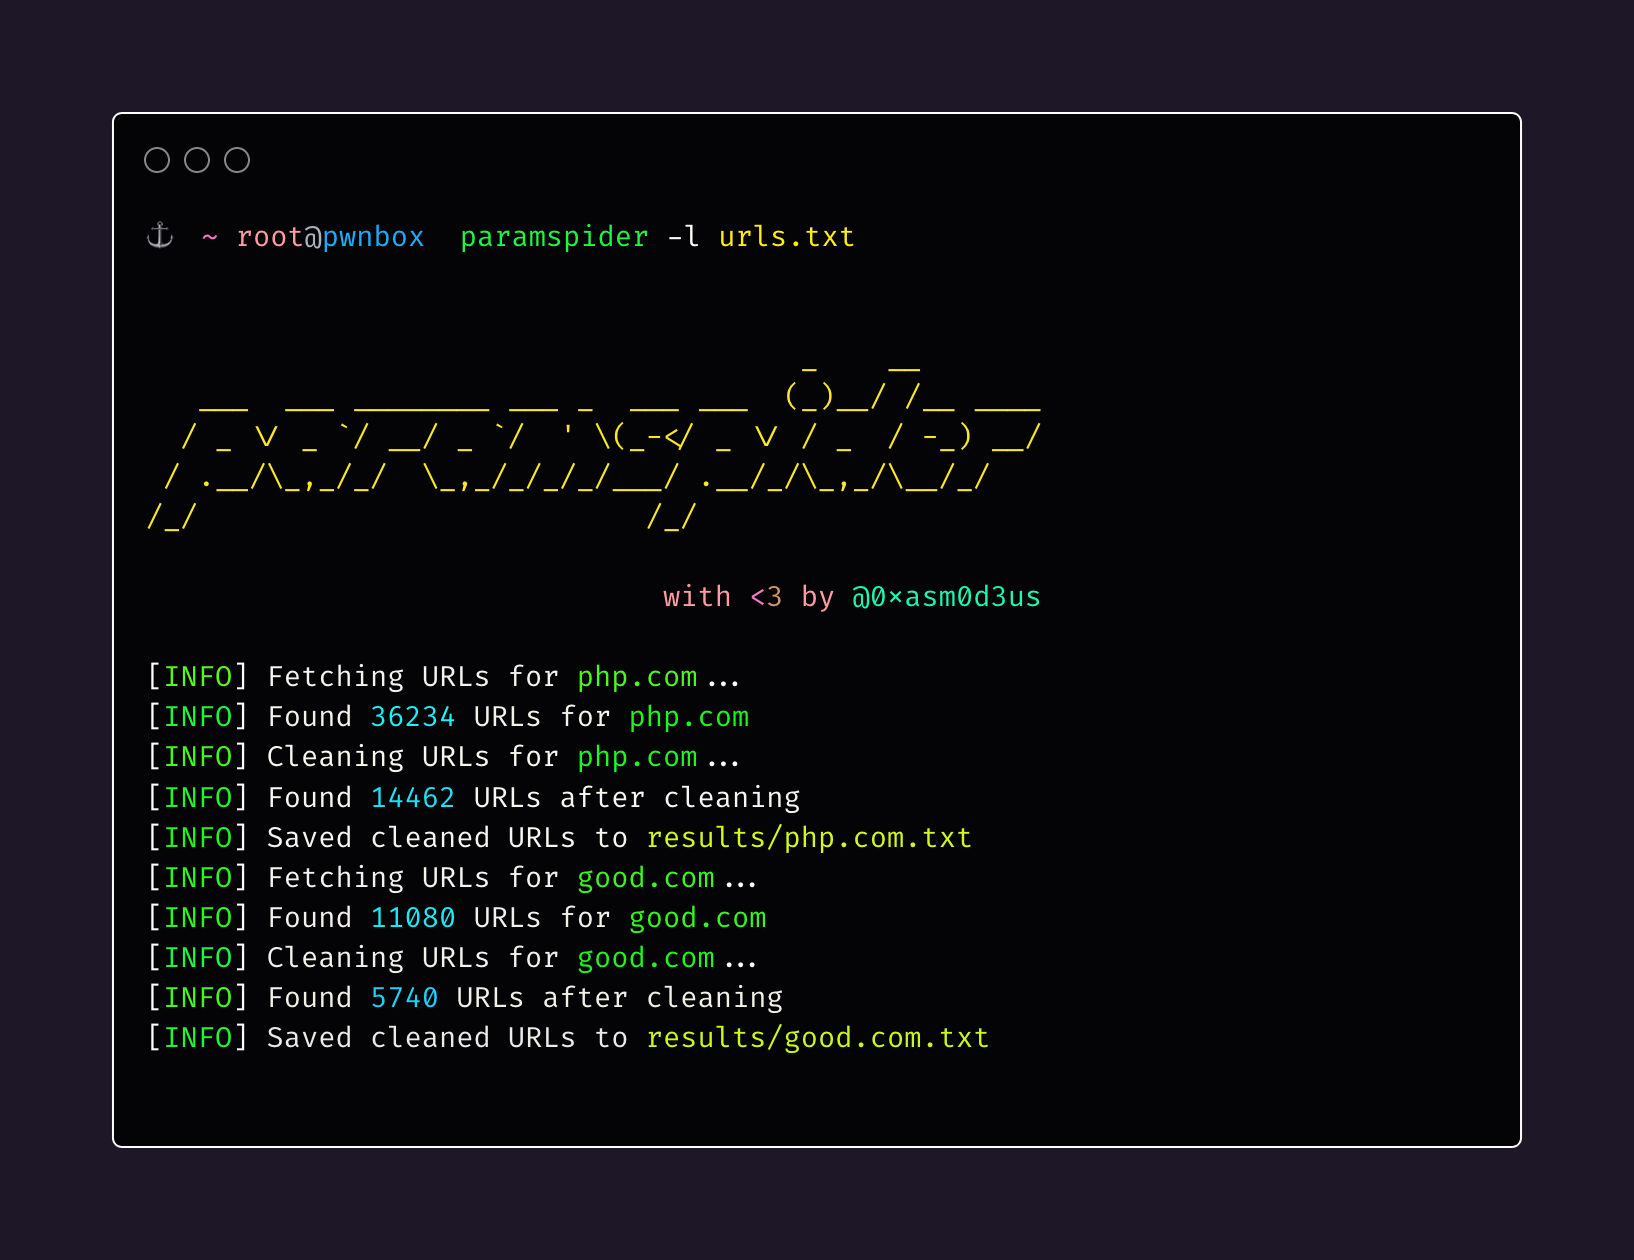 devanshbatham/paramspider
Mining URLs from dark corners of Web Archives for bug hunting/fuzzing/further probing
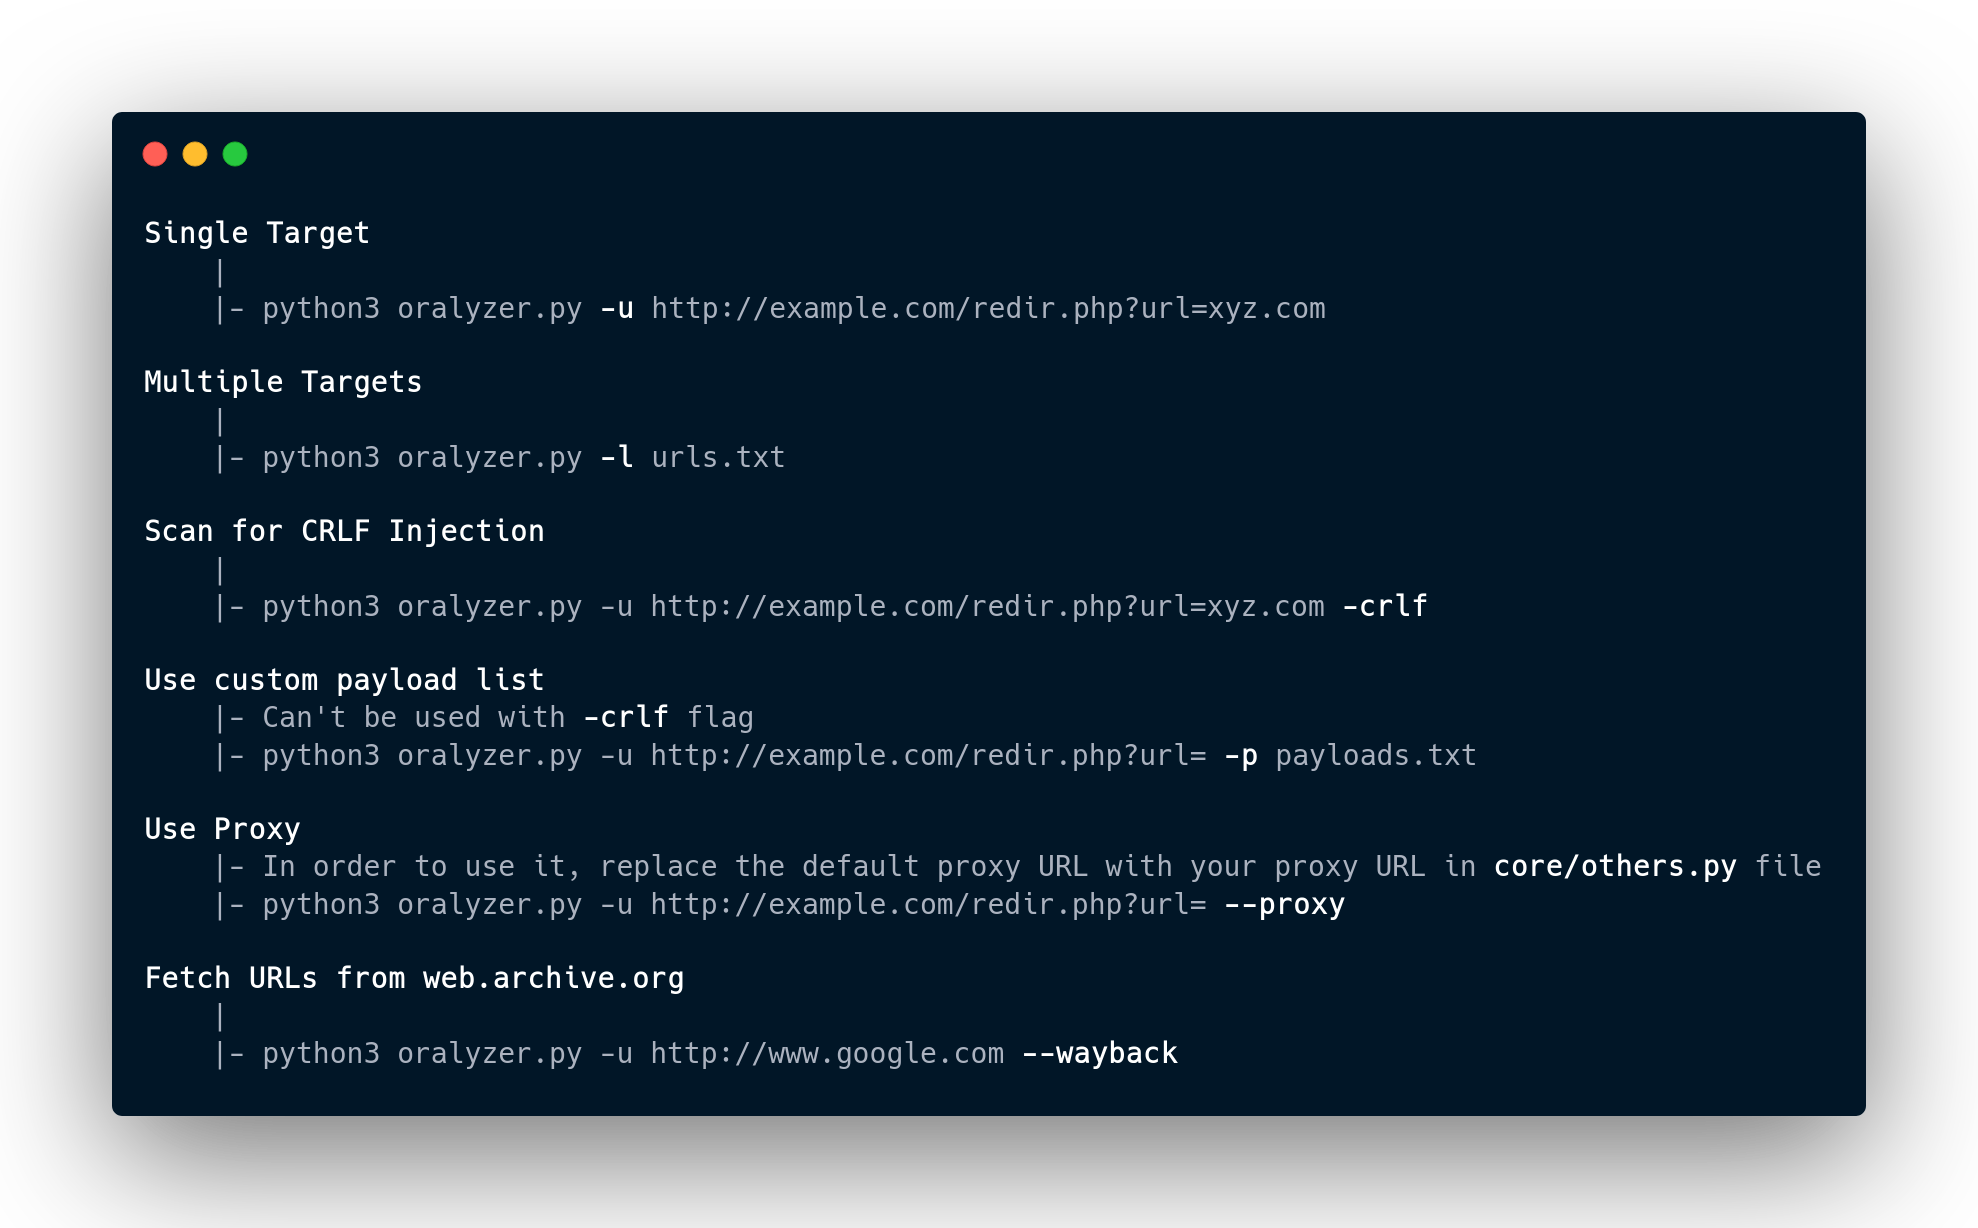 r0075h3ll/oralyzer
Python-based open redirect vulnerability scanner that fuzzes URLs to detect header, JavaScript, and meta tag-based redirects, with integrated…
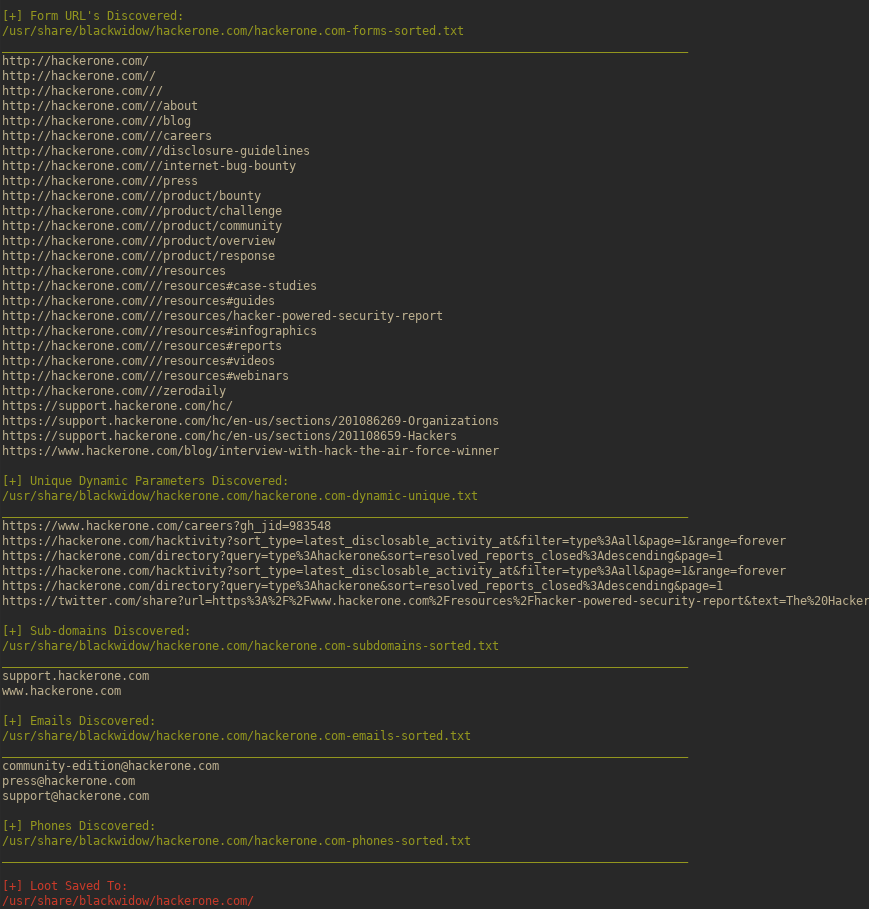 1n3/blackwidow
A Python based web application scanner to gather OSINT and fuzz for OWASP vulnerabilities on a target website.