
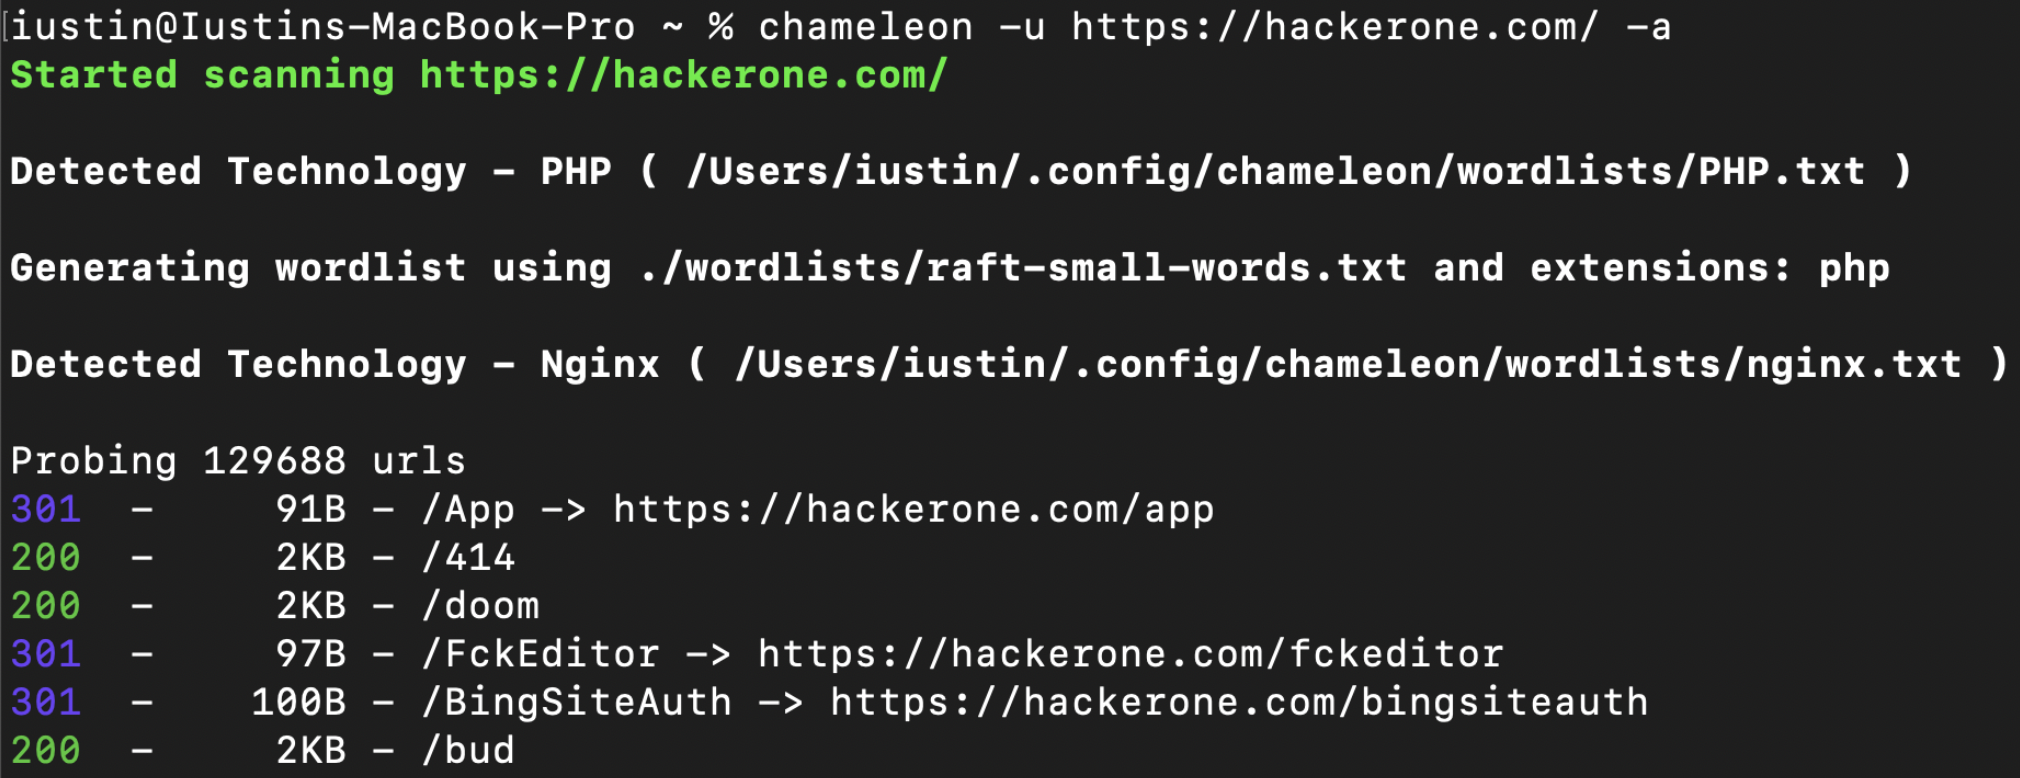
chameleon
 iustin24/chameleon
Technology-aware web content discovery scanner: detects Wappalyzer fingerprints, adapts wordlists/extensions, and performs fast directory bruteforce…
fuzzinginformation-gatheringpenetration-testing+2
384
iustin24/chameleonTechnology-aware web content discovery scanner: detects Wappalyzer fingerprints, adapts wordlists/extensions, and performs fast directory bruteforce…
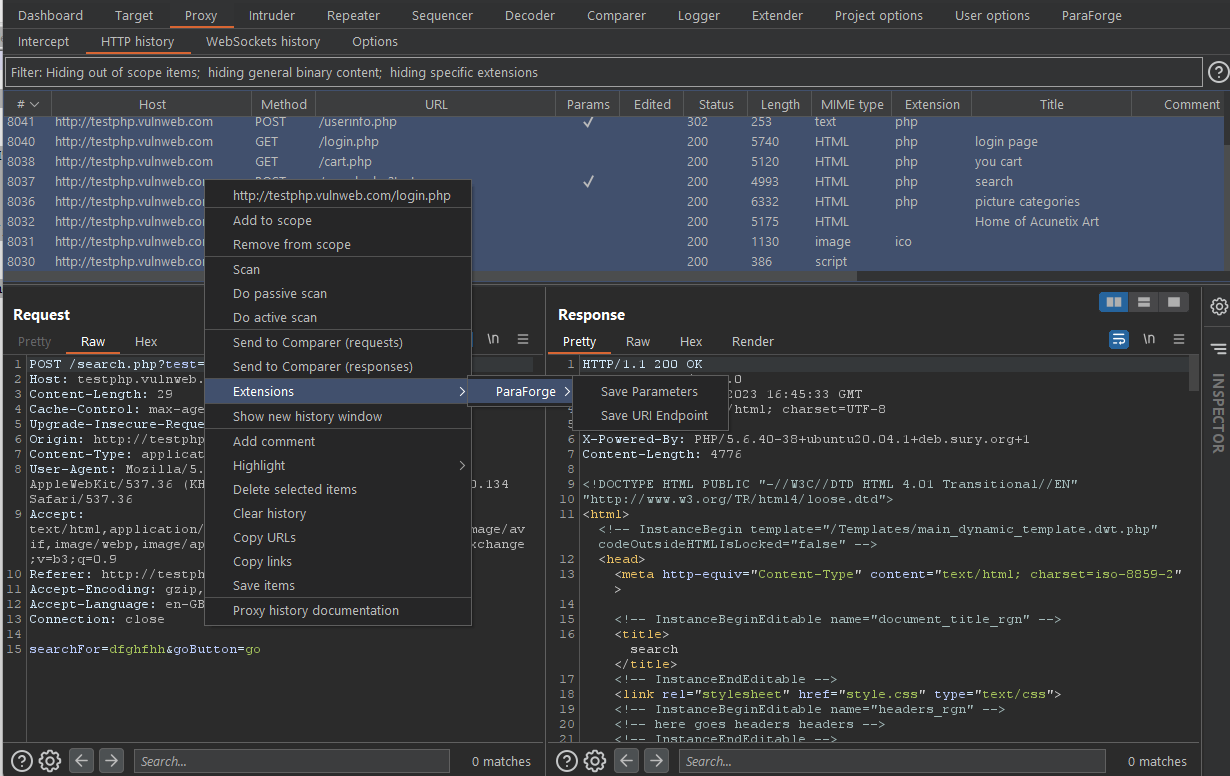 anof-cyber/paraforge
A BurpSuite extension to create a custom word-list of endpoint and parameters for enumeration and fuzzing
 overspace-labs/caa
BurpSuite plugin for HTTP packet analysis and fuzzing dictionary generation. Extracts parameters, paths, and files from requests, counts frequency,…
 puzzlepeaches/ffufw
Automates web content discovery and directory bruteforcing with multithreaded ffuf execution, tech-aware wordlists, endpoint filtering, WAF…
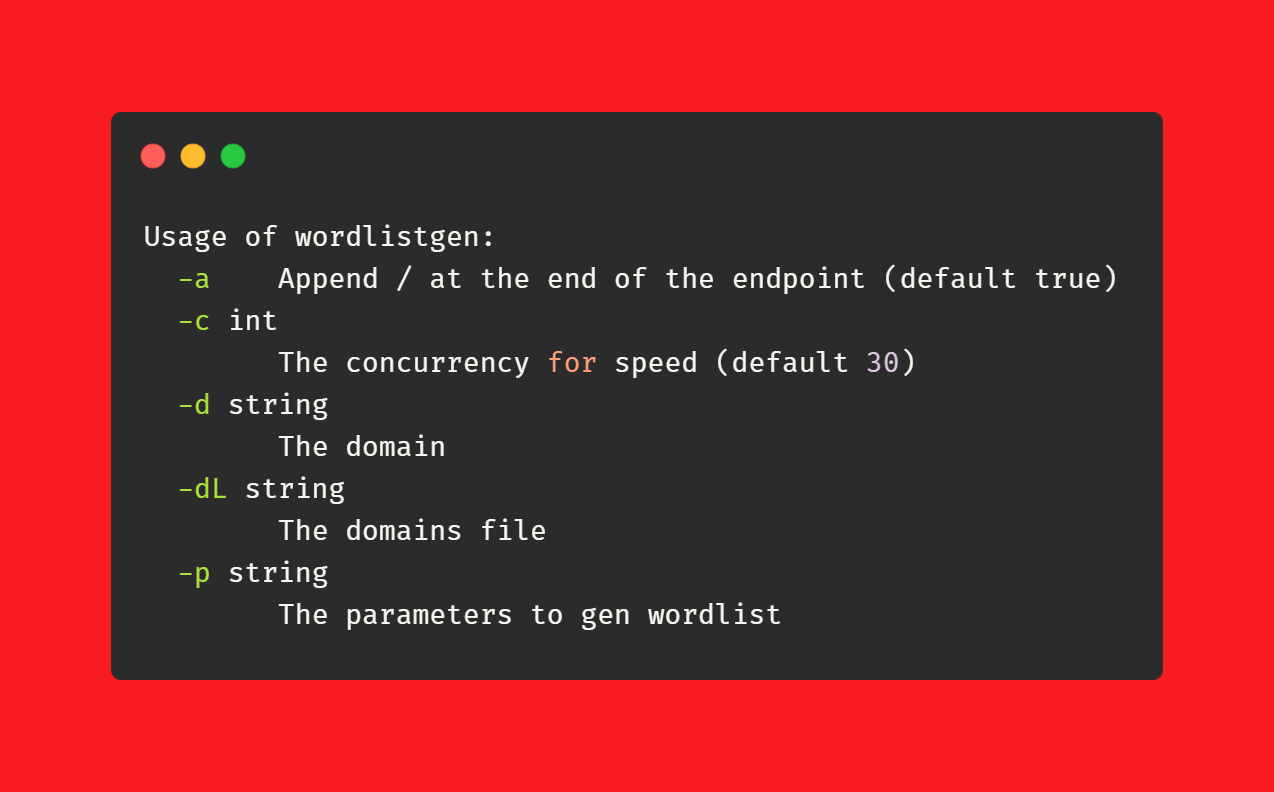 ethicalhackingplayground/wordlistgen
Generates target specific word lists for Fuzzing with fuff
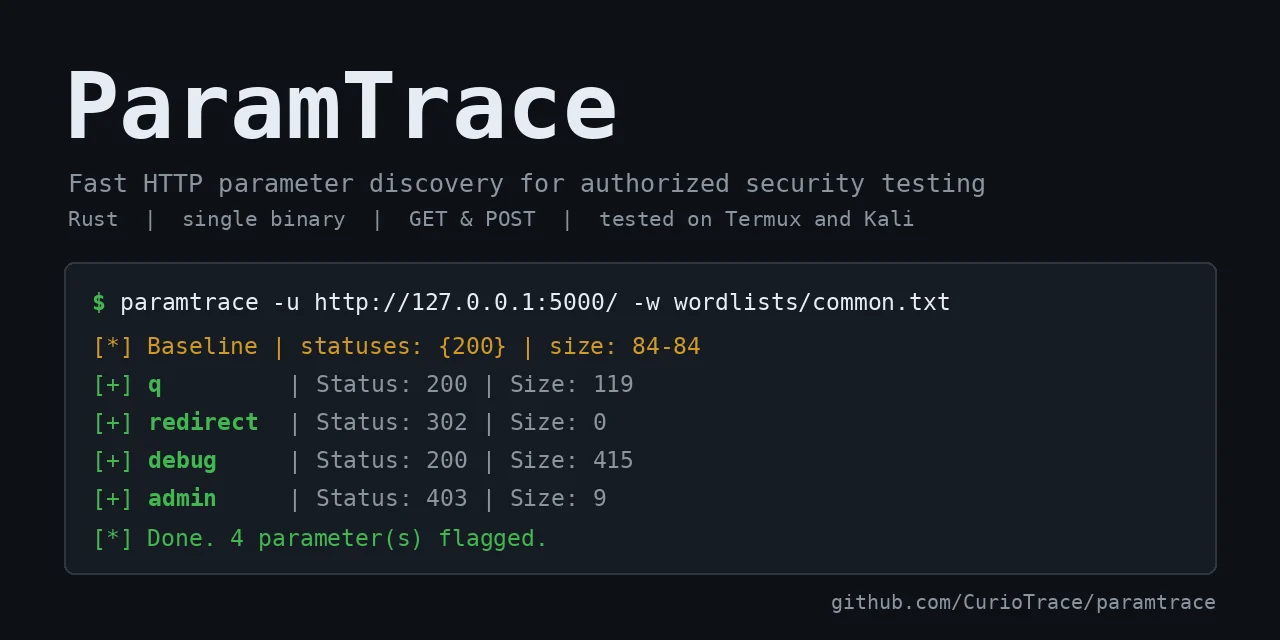 curiotrace/paramtrace
Fast HTTP parameter discovery for authorized security testing
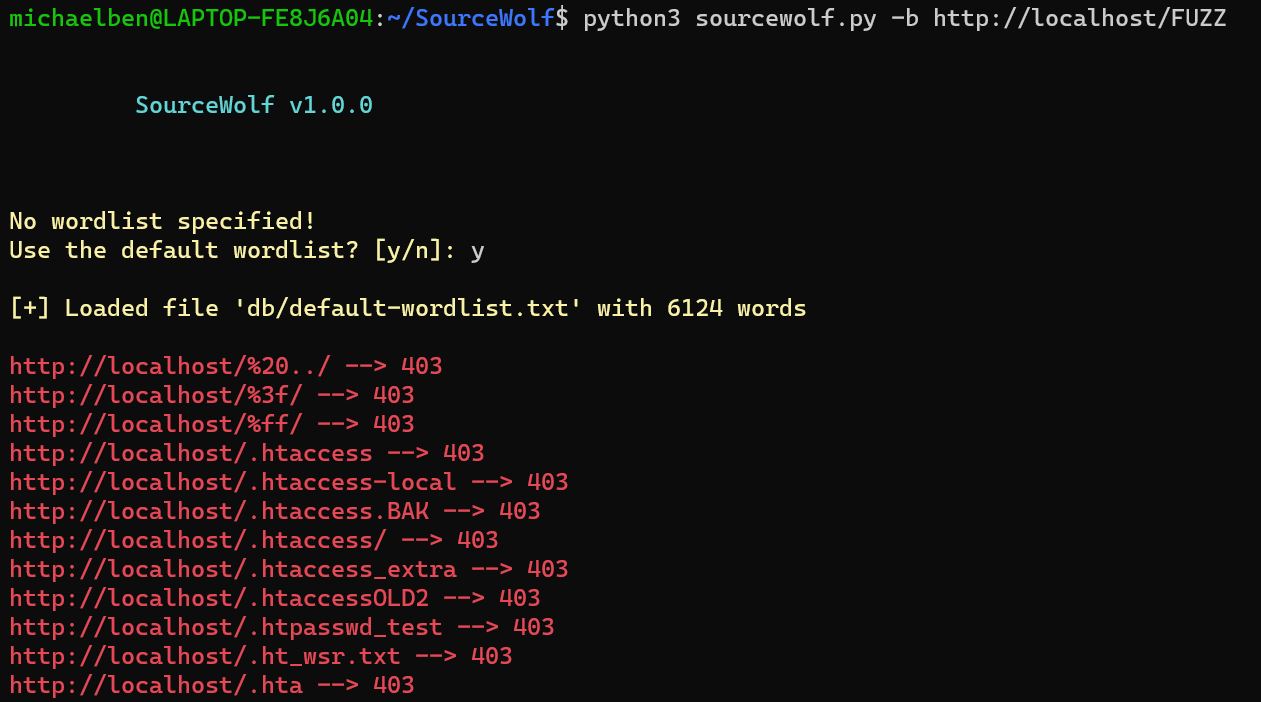 ksharinarayanan/sourcewolf
Amazingly fast response crawler to find juicy stuff in the source code! 😎🔥
 orange-cyberdefense/bof
BOF (Boiboite Opener Framework) is a testing framework for industrial protocols implementations and devices.
 internon/inter-recon
Script to perform automatic initial web and vulnerability recon
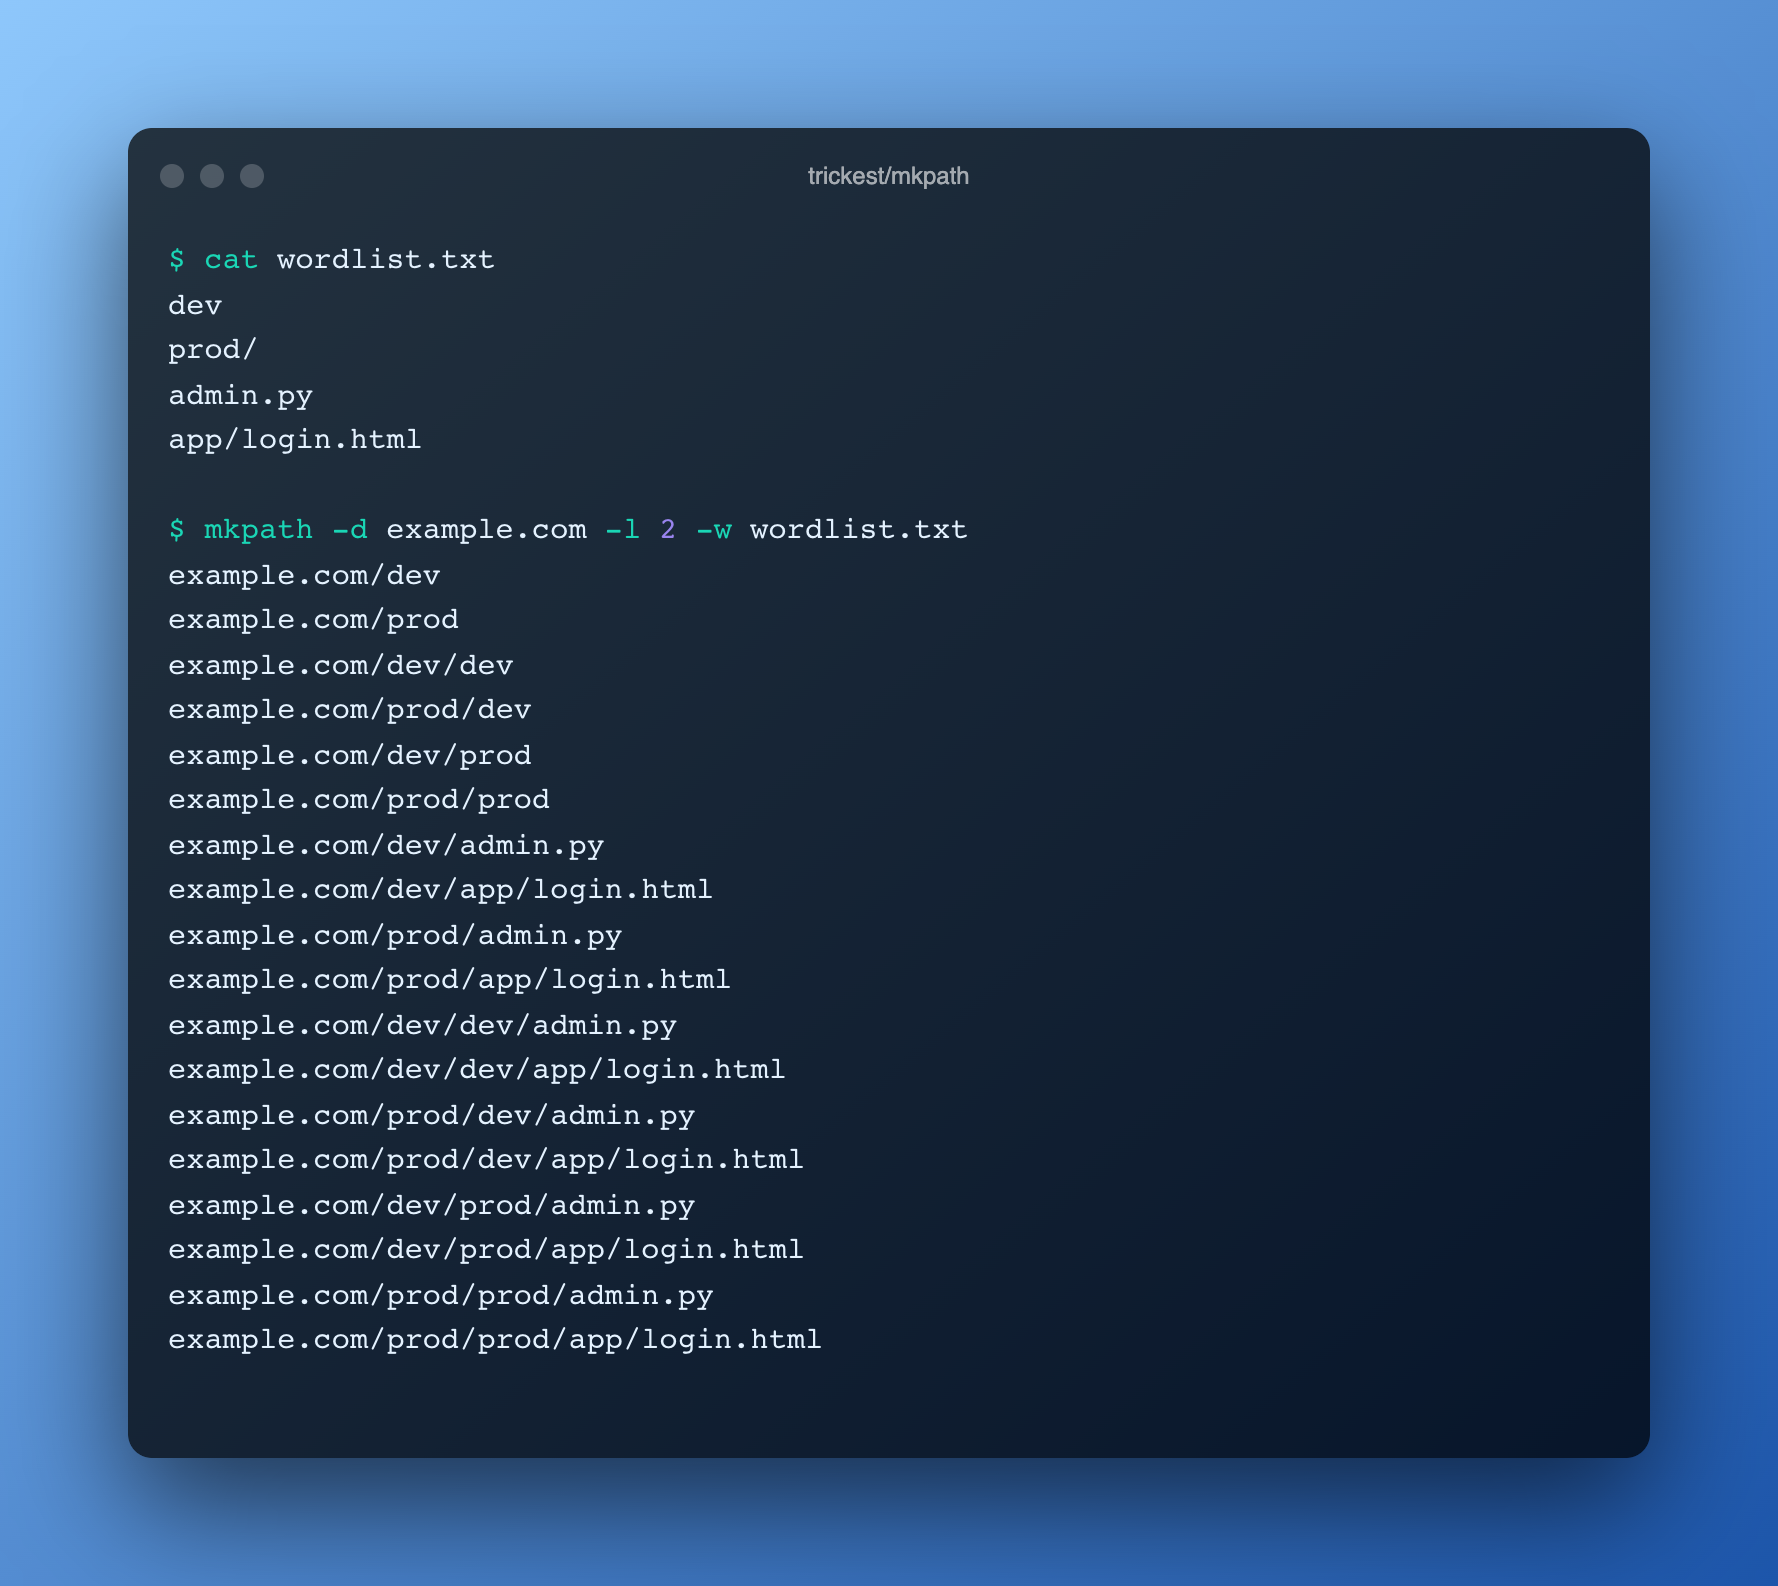 trickest/mkpath
Make URL path combinations using a wordlist
 harsh-bothra/bheem
Scope-based reconnaissance automation framework that orchestrates multiple open-source tools for subdomain enumeration, vulnerability scanning, and…
 ihebski/angryfuzzer
Tools for information gathering
 0xsobky/hackvault
A container repository for my public web hacks!
 syaifulandy/cve-2024-38475
CVE-2024-38475 Scanner using FFUF + Seclists
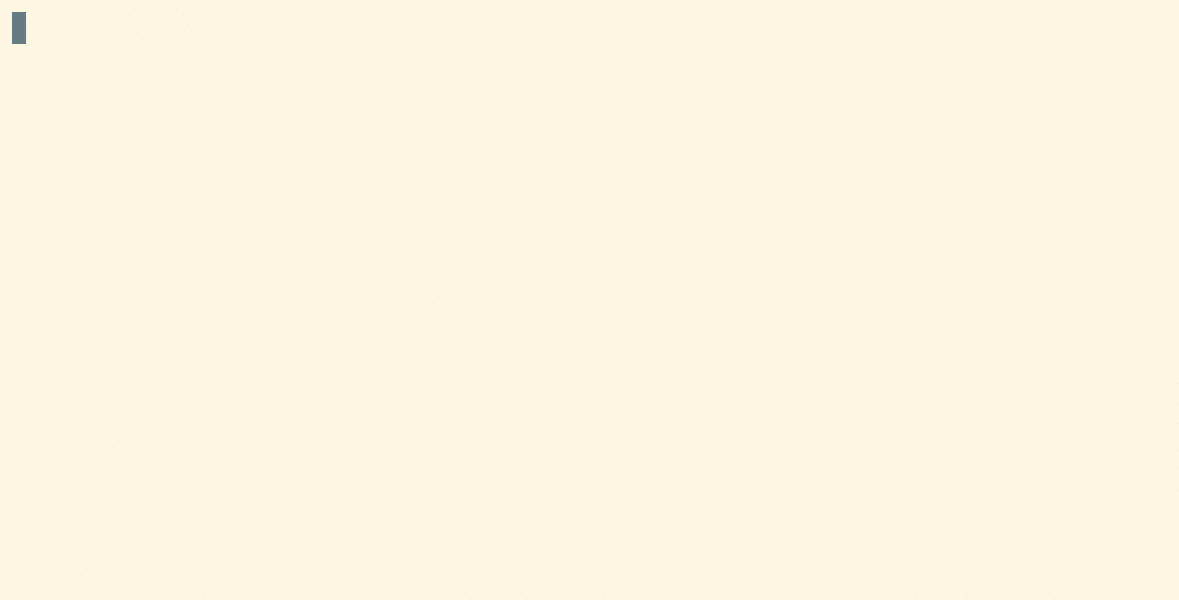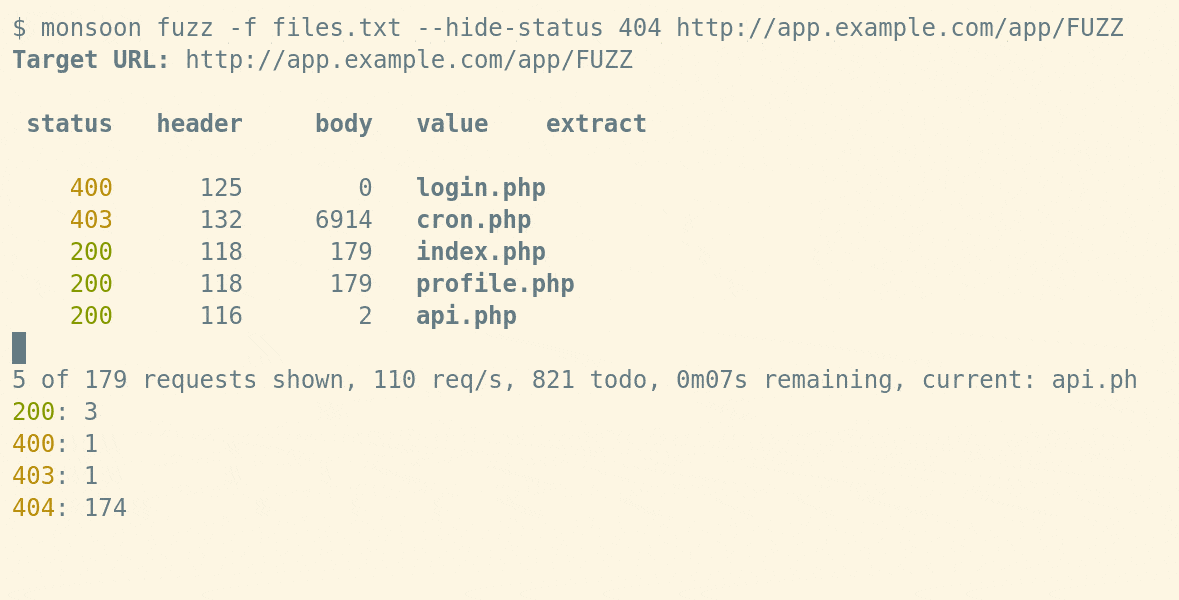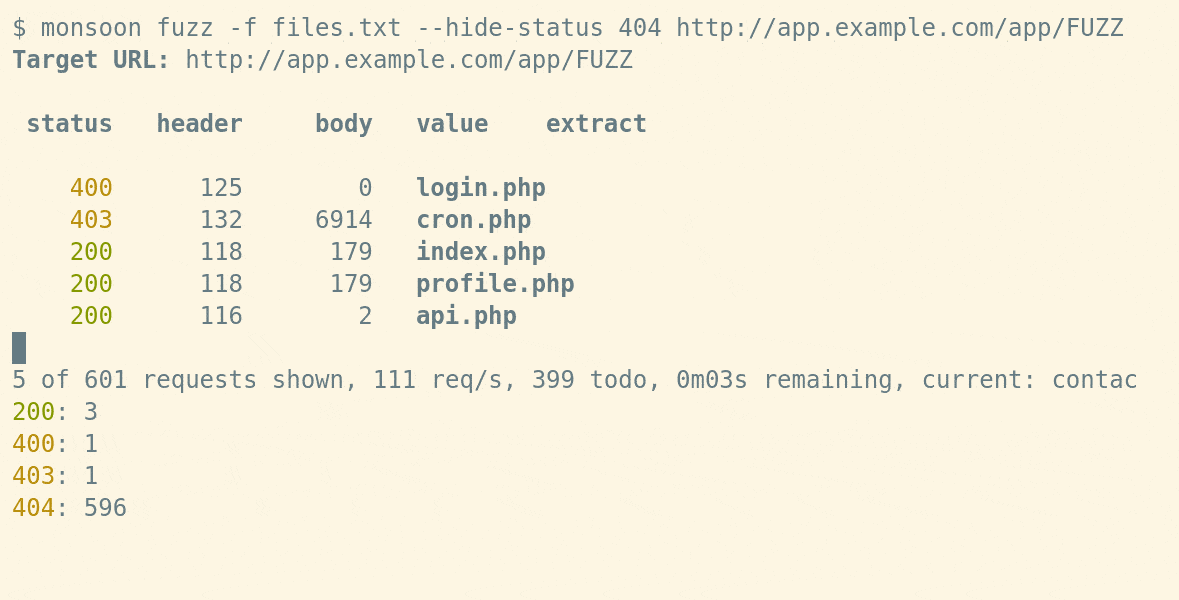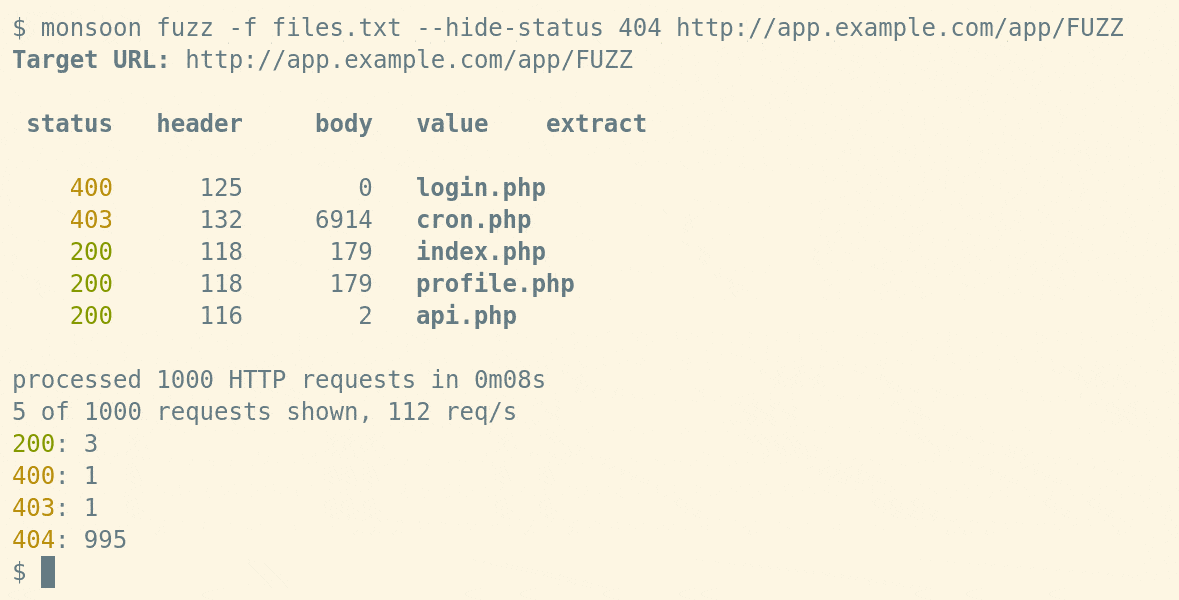 redteampentesting/monsoon
Fast HTTP enumerator
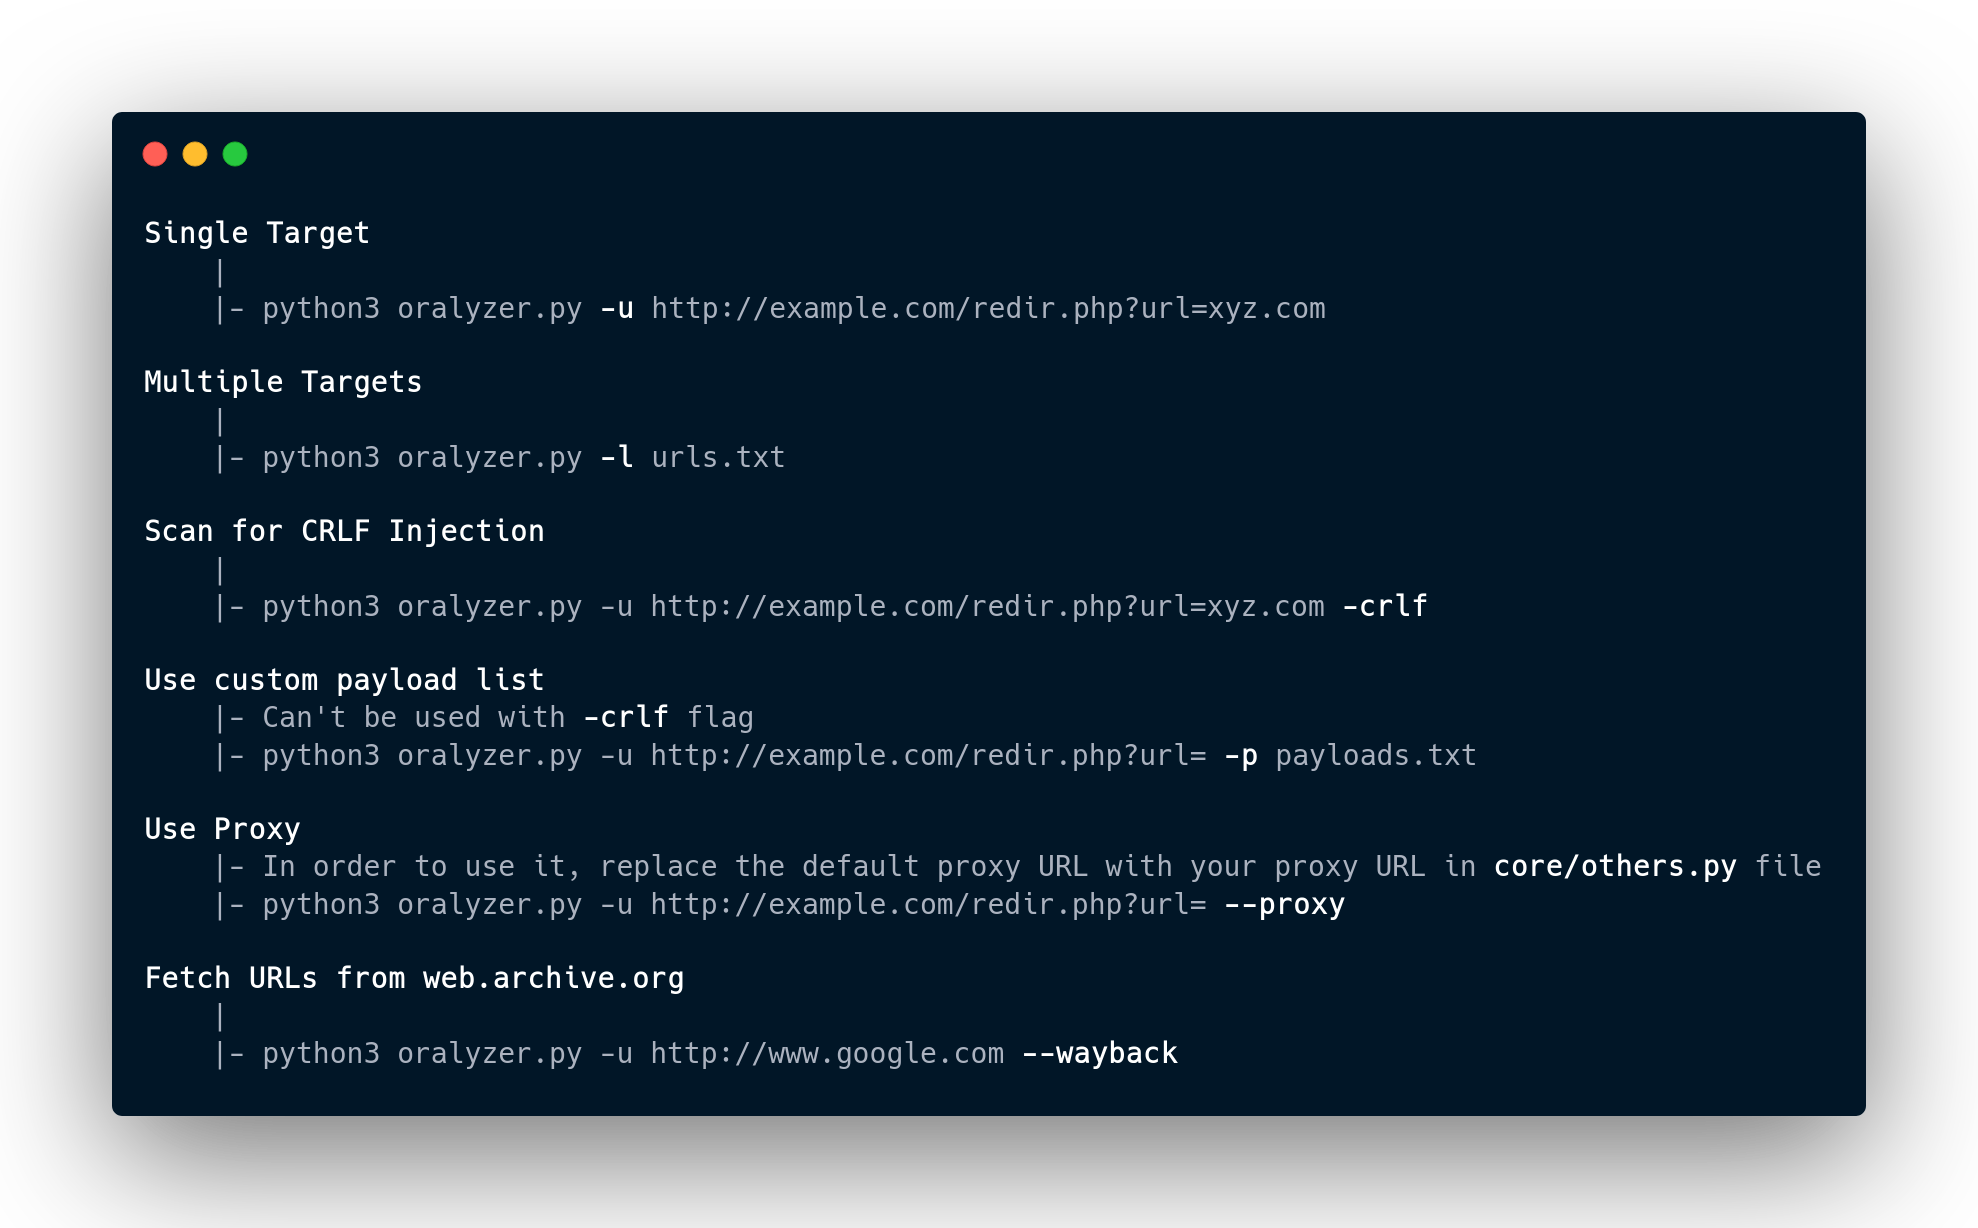 r0075h3ll/oralyzer
Python-based open redirect vulnerability scanner that fuzzes URLs to detect header, JavaScript, and meta tag-based redirects, with integrated…
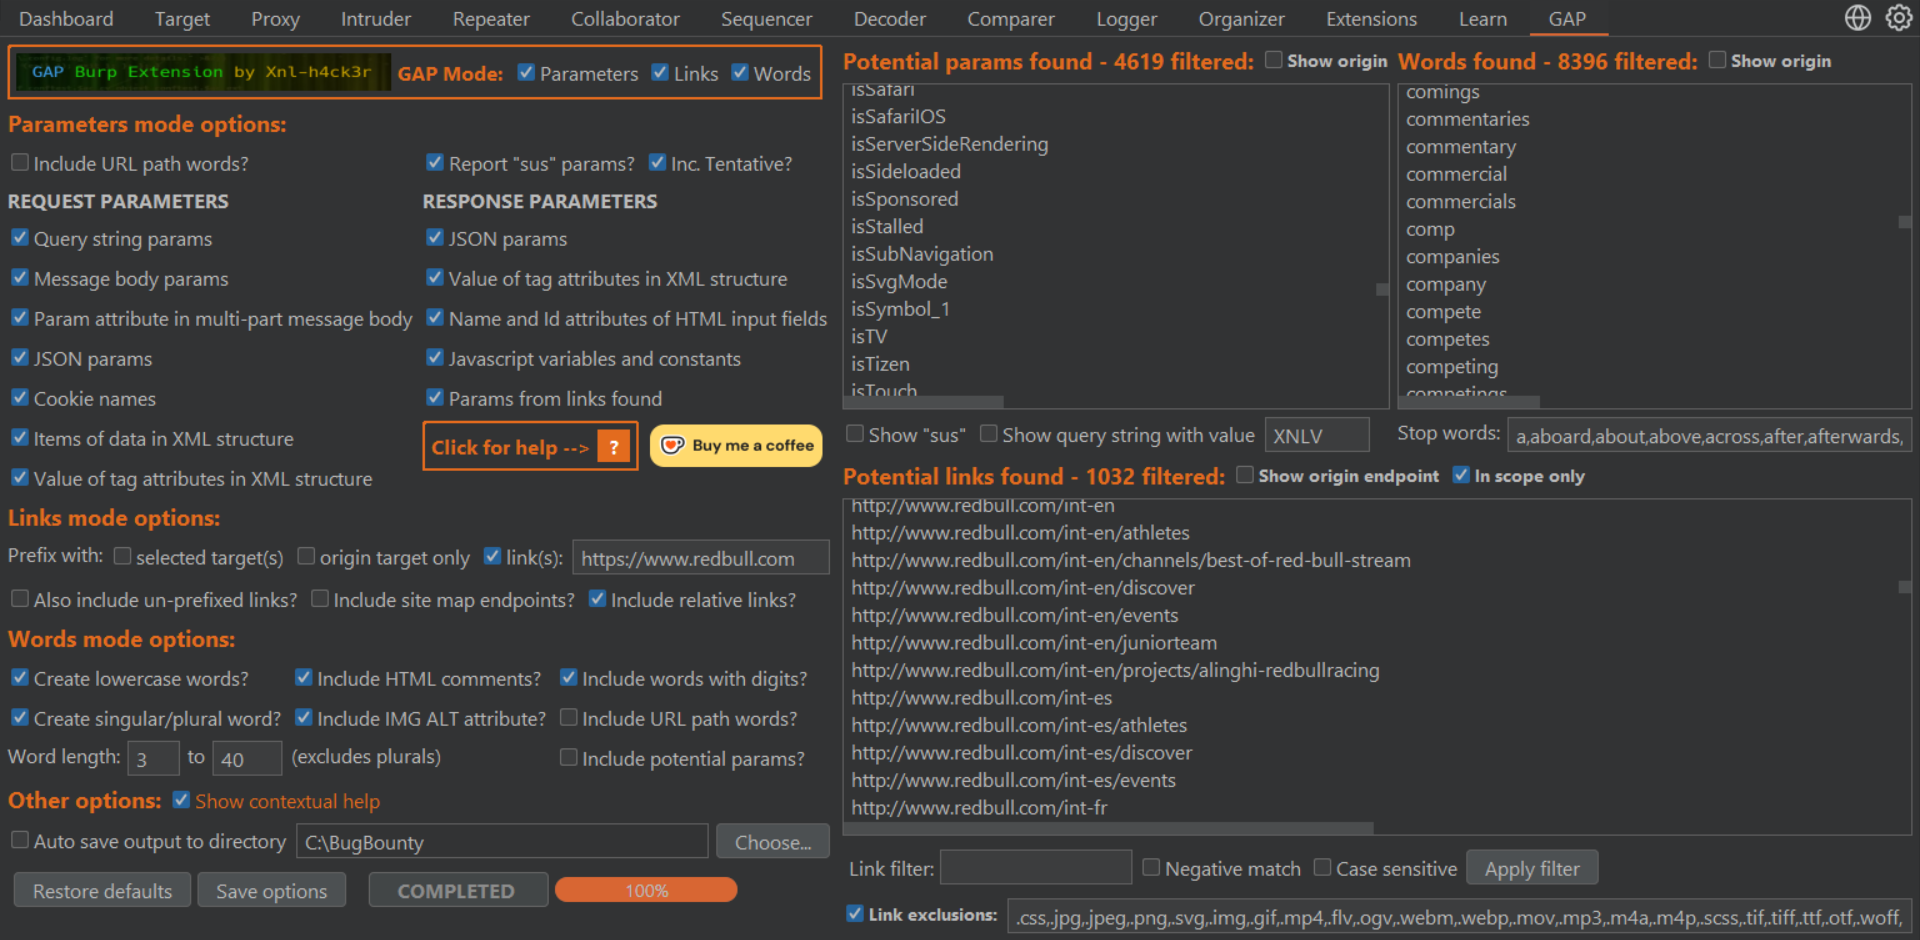 xnl-h4ck3r/gap-burp-extension
Burp Extension to find potential endpoints, parameters, and generate a custom target wordlist
 devanshbatham/paramspider
Mining URLs from dark corners of Web Archives for bug hunting/fuzzing/further probing