
Popcorn-TJNULL-OSCP-
 r3fr4kt/popcorn-tjnull-oscp-
Popcorn HTB write-up covering advanced directory fuzzing, file upload bypass via magic numbers/extension spoofing using Burp Suite, and privilege…
ctfeducationexploitation+7
r3fr4kt/popcorn-tjnull-oscp-Popcorn HTB write-up covering advanced directory fuzzing, file upload bypass via magic numbers/extension spoofing using Burp Suite, and privilege…
 lucadibello/tmux-fuzzing
Enhanced fuzzing for tmux using OSS-Fuzz. Includes custom `cmd-fuzzer` and `argument-fuzzer` harnesses for improved code coverage and a PoC for…
 mohitsinghpapola/cve-2023-20052
Fixed Docker build for CVE-2023-20052 ClamAV XXE exploit. Resolves OpenSSL 3.0 compilation errors using Ubuntu 18.04 with OpenSSL 1.0 for…
 wildwestcybersecurity/cve-2019-13288
Replicated using afl fuzzer instrumentation! Shoutz to antonio-morales.
 personnumber3377/windows_tcpip_fuzz
This is my attempt at fuzzing the tcpip.sys driver in windows via using scapy. This is inspired by this vulnerability here:…
 almkuznetsov/cve-2024-1441
Reproduces fuzzing and crash analysis for CVE-2024-1441 using AFL++ and CASR, with detailed setup and commands for libvirt.
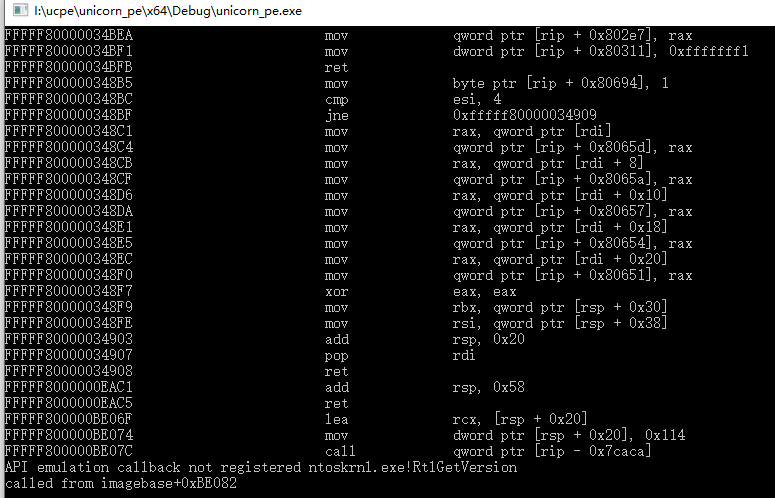 hzqst/unicorn_pe
Emulates Windows PE execution using Unicorn engine for malware analysis, unpacking packed binaries, and decrypting VMProtect strings and imports.
 boschresearch/gdbfuzz
Fuzzing Embedded Systems using Hardware Breakpoints
 sentinel-one/efi_fuzz
Coverage-guided fuzzer for UEFI NVRAM variables using Qiling emulation and AFL++ to discover firmware vulnerabilities through automated input…

 aflplusplus/libafl
Advanced Fuzzing Library - Slot your Fuzzer together in Rust! Scales across cores and machines. For Windows, Android, MacOS, Linux, no_std, ...
 mxmssh/drafl
AFL + DynamoRIO = fuzzing binaries with no source code on Linux
 parallelbeings/cve-2019-14079
USB device fuzzing on Android Phone
 bshyuunn/bandiview-7.05-vuln-poc
bandiview (7.05) vuln PoC | CVE-2024-45870, CVE-2024-45871, CVE-2024-45872
 kamorin/dhcpig
DHCP exhaustion script written in python using scapy network library
 owasp/pysap
pysap is an open source Python library that provides modules for crafting and sending packets using SAP's NI, Diag, Enqueue, Router, MS, SNC, IGS,…
 rfidtool/esp-rfid-tool
A tool for logging data/testing devices with a Wiegand Interface. Can be used to create a portable RFID reader or installed directly into an existing…