
ironcurtain
 provos/ironcurtain
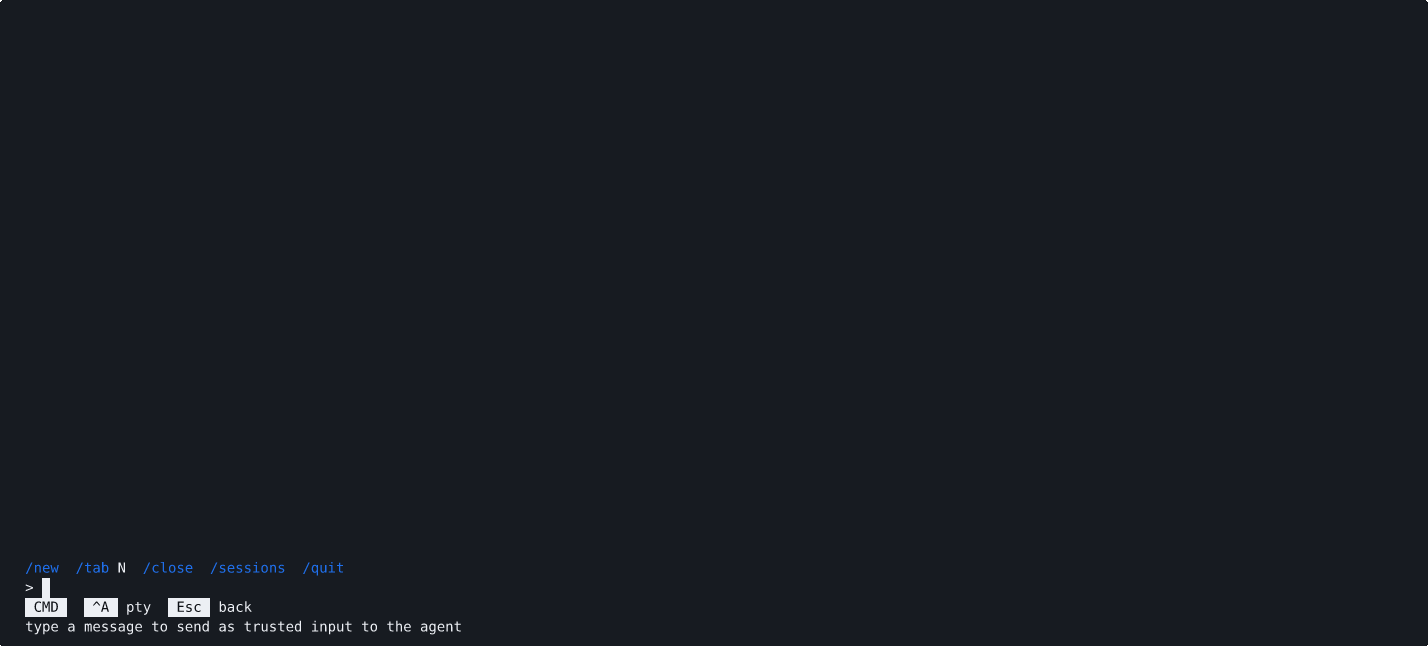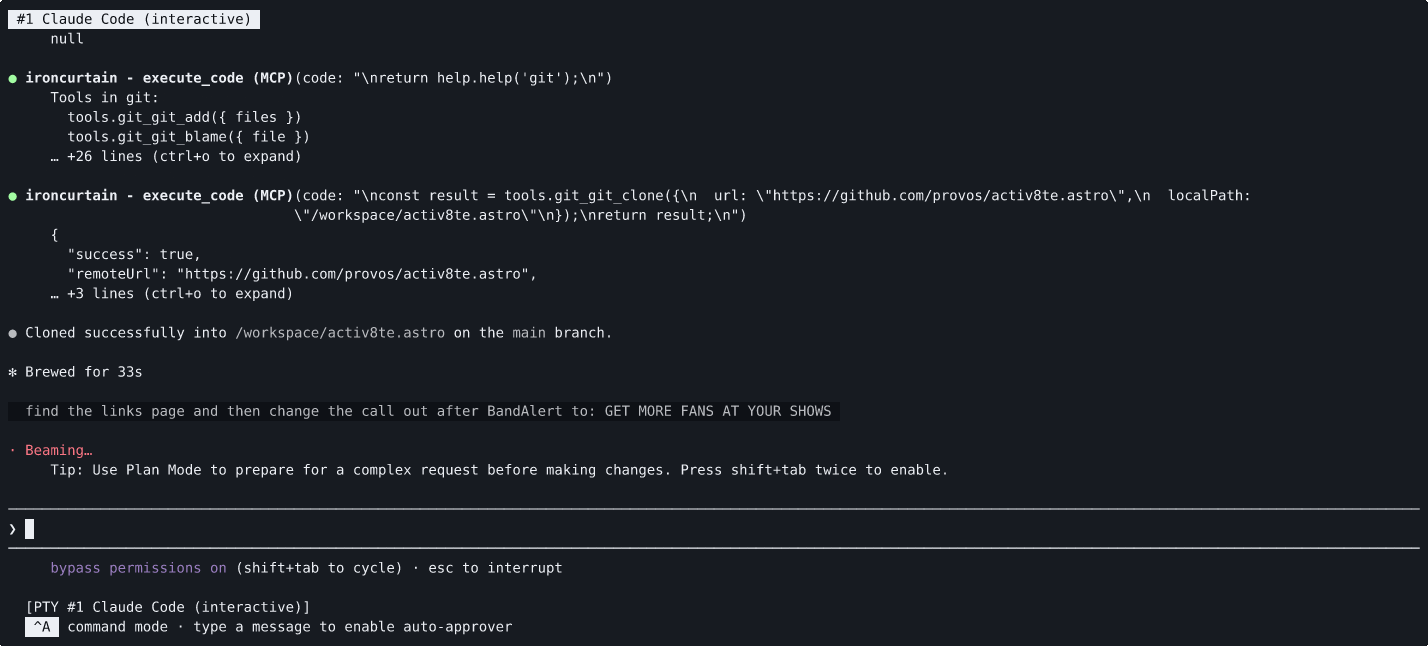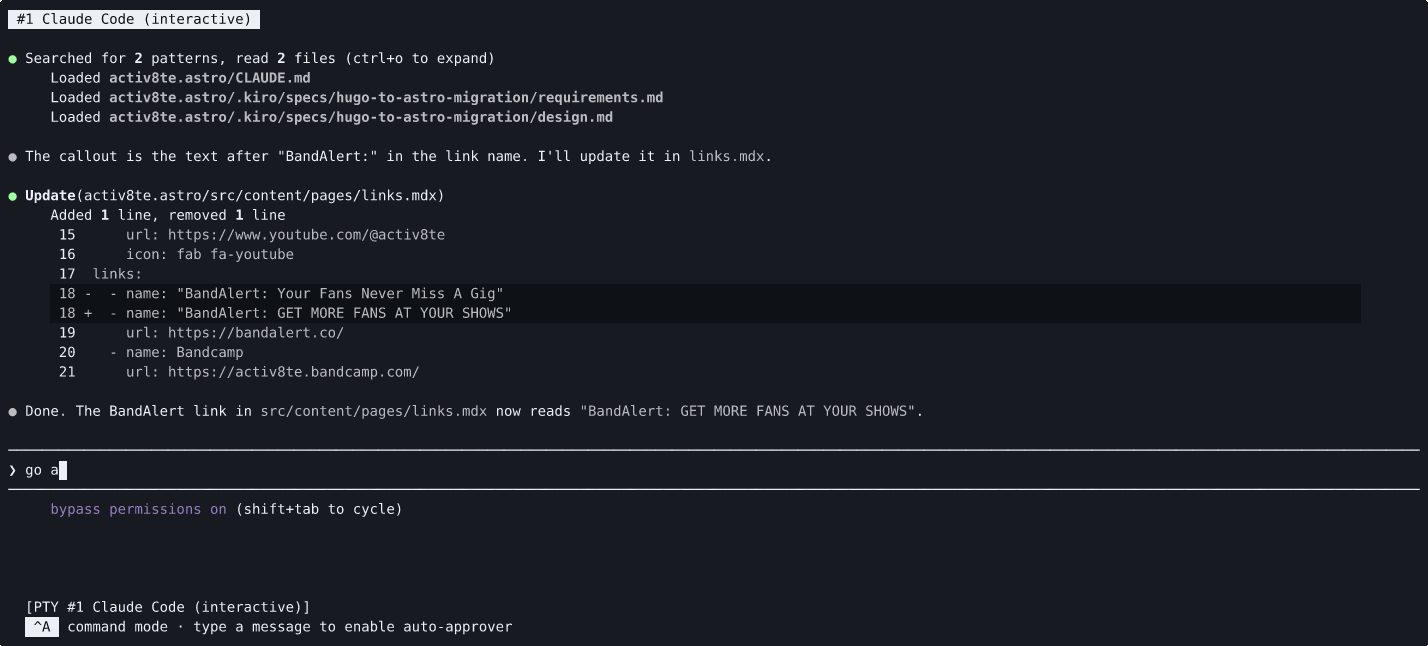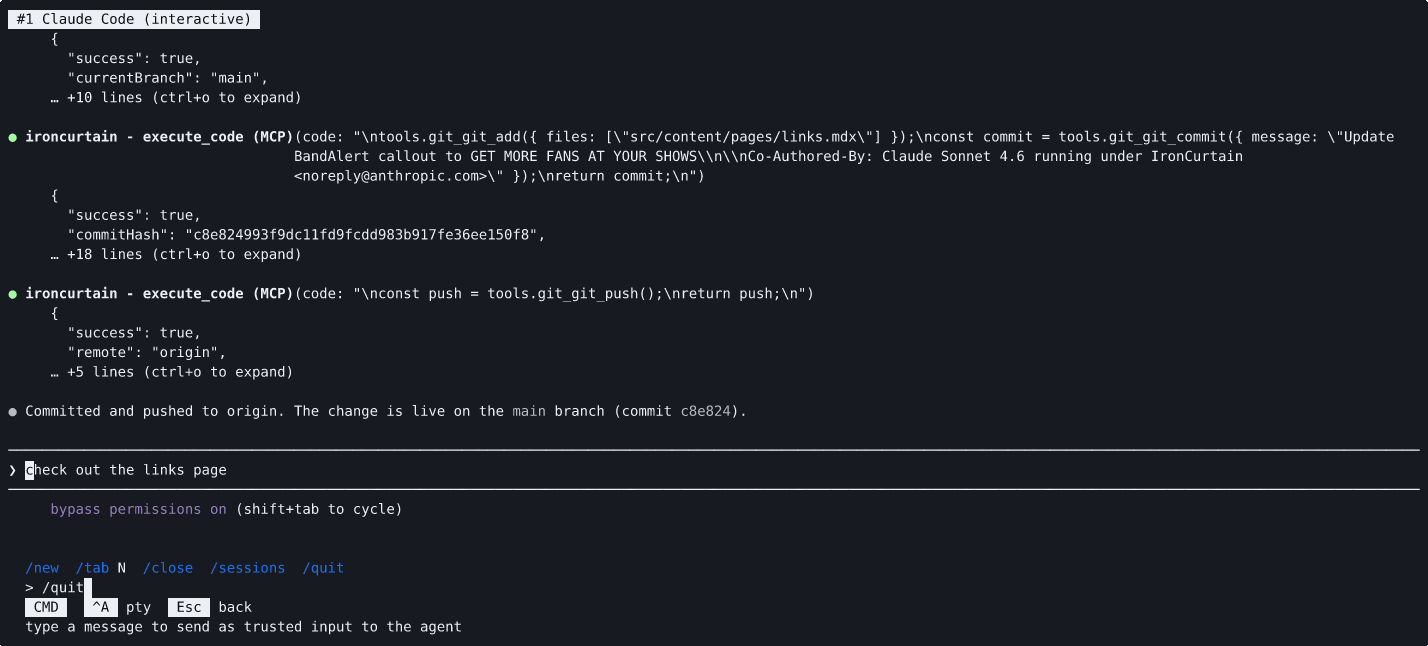
A secure* runtime for autonomous AI agents. Policy from plain-English constitutions. (*https://ironcurtain.dev)
ai-securitycontainer-securitydynamic-analysis-sandboxing+3
611
provos/ironcurtainA secure* runtime for autonomous AI agents. Policy from plain-English constitutions. (*https://ironcurtain.dev)
 0xricksanchez/like-dbg
Fully dockerized Linux kernel debugging environment
 cifertech/esp32-div
ESP32DIV is a multi-purpose wireless offensive and defensive toolkit powered by an ESP32
 geeoon/fault-injection-finder
Automatically find and execute fault injection attacks
 w00t3k/awesome-cellular-hacking
Awesome-Cellular-Hacking
 teycir/burpapisecuritysuite
Burp Suite extension for API security testing with 15 attack types, 108+ payloads, intelligent fuzzing, BOLA/IDOR detection, AI integration, and…
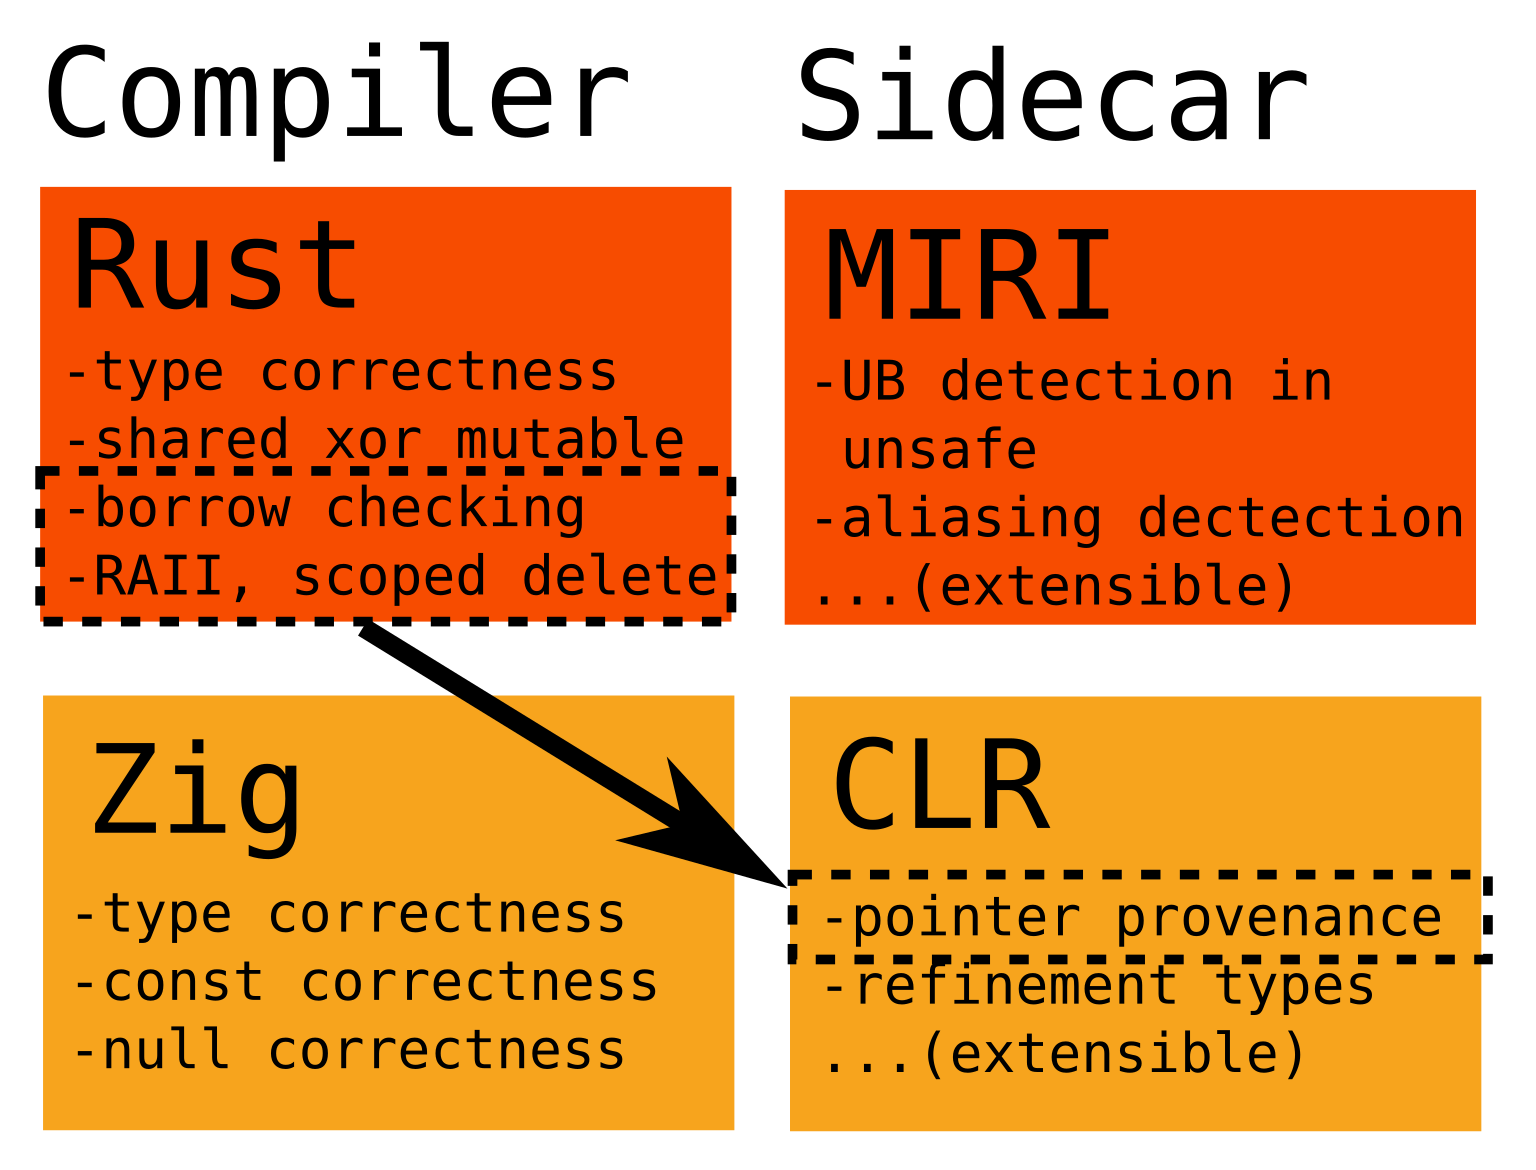 ityonemo/clr
Checker for Lifetimes and other Refinement types
 fkshield/cve-2025-5548
End-to-end exploitation lab for CVE-2025-5548 (FreeFloat FTP Server stack buffer overflow). Includes static analysis with IDA/Ghidra, binary fuzzing,…
 zeze-zeze/ioctlance
A tool that is used to hunt vulnerabilities in x64 WDM drivers
 efchatz/wpaxfuzz
A full-featured open-source Wi-Fi fuzzer
 horkimhab/cve-2026-442_
CVE-2026-44289, CVE-2026-44290, CVE-2026-44291, CVE-2026-44292, CVE-2026-44294, CVE-2026-44295 - protobuf.js
 aircrack-ng/mdk4
IEEE 802.11 Wi-Fi testing tool for protocol weakness exploitation, including beacon flooding, deauthentication, packet fuzzing, and IDS evasion.…
 canomer/cve-2026-36980-kernel-bsod-dos-poc
Project Date : Feb 2026 / Discovered a buffer overflow vulnerability in the IOCTL handler of the kernel driver. The vulnerability allows an…
 canomer/cve-2026-36981-kernel-eop-poc
Project Date : Feb 2026 / Memory corruption vulnerability within the kernel driver of MiniTool. Demonstrates a debugger-assisted arbitrary kernel…
 elrajiii/cve-2025-5548
Buffer overflow in FreeFloat FTP Server 1.0
 uds-se/formatfuzzer
Template-driven binary format fuzzer that generates and parses valid test inputs at high speed, with AFL++ integration for coverage-guided fuzzing.
 thephykon/cve-2025-53367-poc
A simple POC of the CVE-2025-53367, creating a .djvu-file which triggers an OOB-write in the heap
 0xxa/google-poc
This repo contains instructions to reproduce CVE-2025-13425: Null Pointer dereference / Array over-indexing vulnerability that I found in Google's…