

dynamorio
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
binary-analysiscode-analysisdebuggers+3
3.2k
dynamorio/dynamorioRuntime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
 rfidresearchgroup/proxmark3
Hardware tool for RFID analysis, emulation, and penetration testing. Supports 125kHz, 13.56MHz protocols (MIFARE, iClass, ISO14443/15693) with key…
 google/syzkaller
Unsupervised coverage-guided kernel fuzzer for Linux and major OS kernels; automatically discovers security vulnerabilities through intelligent…
 secdev/scapy
Python-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…
 google/honggfuzz
Security oriented software fuzzer. Supports evolutionary, feedback-driven fuzzing based on code coverage (SW and HW based)
 kmkz/exploits
Original CVEs, exploit PoCs, and security advisories with detailed vulnerability chains, privilege escalation, and container escape techniques for…
 portswigger/turbo-intruder
High-speed Burp Suite extension for sending large volumes of HTTP requests with a custom stack, Python-based attack configuration, and advanced…
 aftermathlabs/discord-crasher
Some bugs found via binary instrumentation and fuzzing
 aflplusplus/libafl
Advanced Fuzzing Library - Slot your Fuzzer together in Rust! Scales across cores and machines. For Windows, Android, MacOS, Linux, no_std, ...
 microsoft/windowsprotocoltestsuites
⭐⭐ Join us at SNIA SDC for the SMB3 IO Lab (September 28 - October 1, 2026), see upcoming Interoperability Events
 416rehman/deepzero
Find zero-days while you sleep. DeepZero is an automated vulnerability research framework that parses, decompiles, and analyzes thousands of Windows…
 vsvalinx/cve-2025-5548
Educational repository documenting the full exploitation lifecycle of a stack buffer overflow in FreeFloat FTP Server 1.0, including fuzzing, EIP…
 qilingframework/qiling
A True Instrumentable Binary Emulation Framework
 0vercl0k/wtf
Distributed, code-coverage guided snapshot-based fuzzer for user and kernel-mode targets on Windows and Linux, with emulator and hypervisor backends.
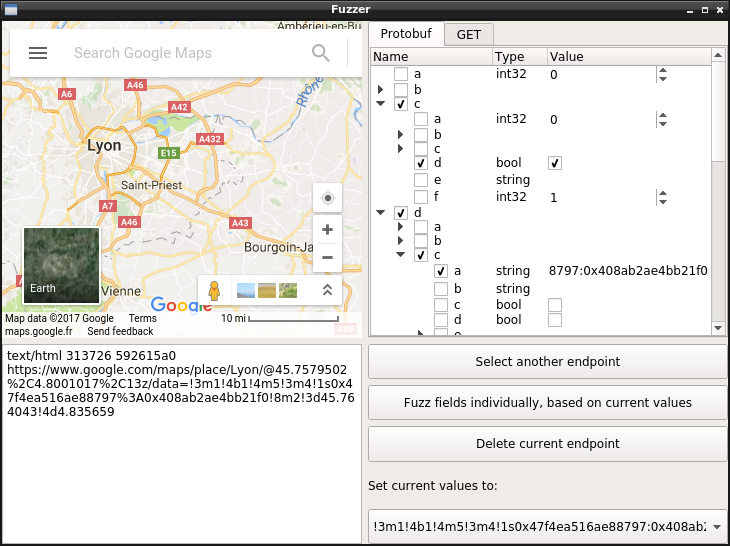 marin-m/pbtk
A toolset for reverse engineering and fuzzing Protobuf-based apps
 pigyon/mcpwner
Model Context Protocol server for autonomous vulnerability discovery
 josephfarah-ciso/cve-2026-9999-exploit
Proof-of-concept and GLSL fuzzer for CVE-2026-9999 in Chrome's ANGLE/Metal WebGL backend, with build fingerprinting, curated shaders, and crash…
 godoy-sec/cve-2017-14980
Study of a classic stack-based buffer overflow vulnerability in a controlled lab environment for educational purposes.