


 owasp/offat
Automated API security testing tool that generates tests from OpenAPI specs, fuzzes inputs, and checks for OWASP API Top 10 vulnerabilities including…
 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
 google/silifuzz
Fuzzes CPU implementations by generating test inputs from software proxies, then executes them on real hardware to detect microarchitecture defects…
 provos/ironcurtain
A secure* runtime for autonomous AI agents. Policy from plain-English constitutions. (*https://ironcurtain.dev)
 xen0bit/netprobe-cve-2026-98432
Black-box remote probe that detects CVE-2026-98432, a Linux IPv4 TCP ireq_opt use-after-free, via differential SYN-ACK option echo, plus static…

 sunblaze-ucb/exploitgym
ExploitGym is a large-scale, realistic benchmark built from real-world vulnerabilities designed to evaluate AI agents' ability to develop exploits.
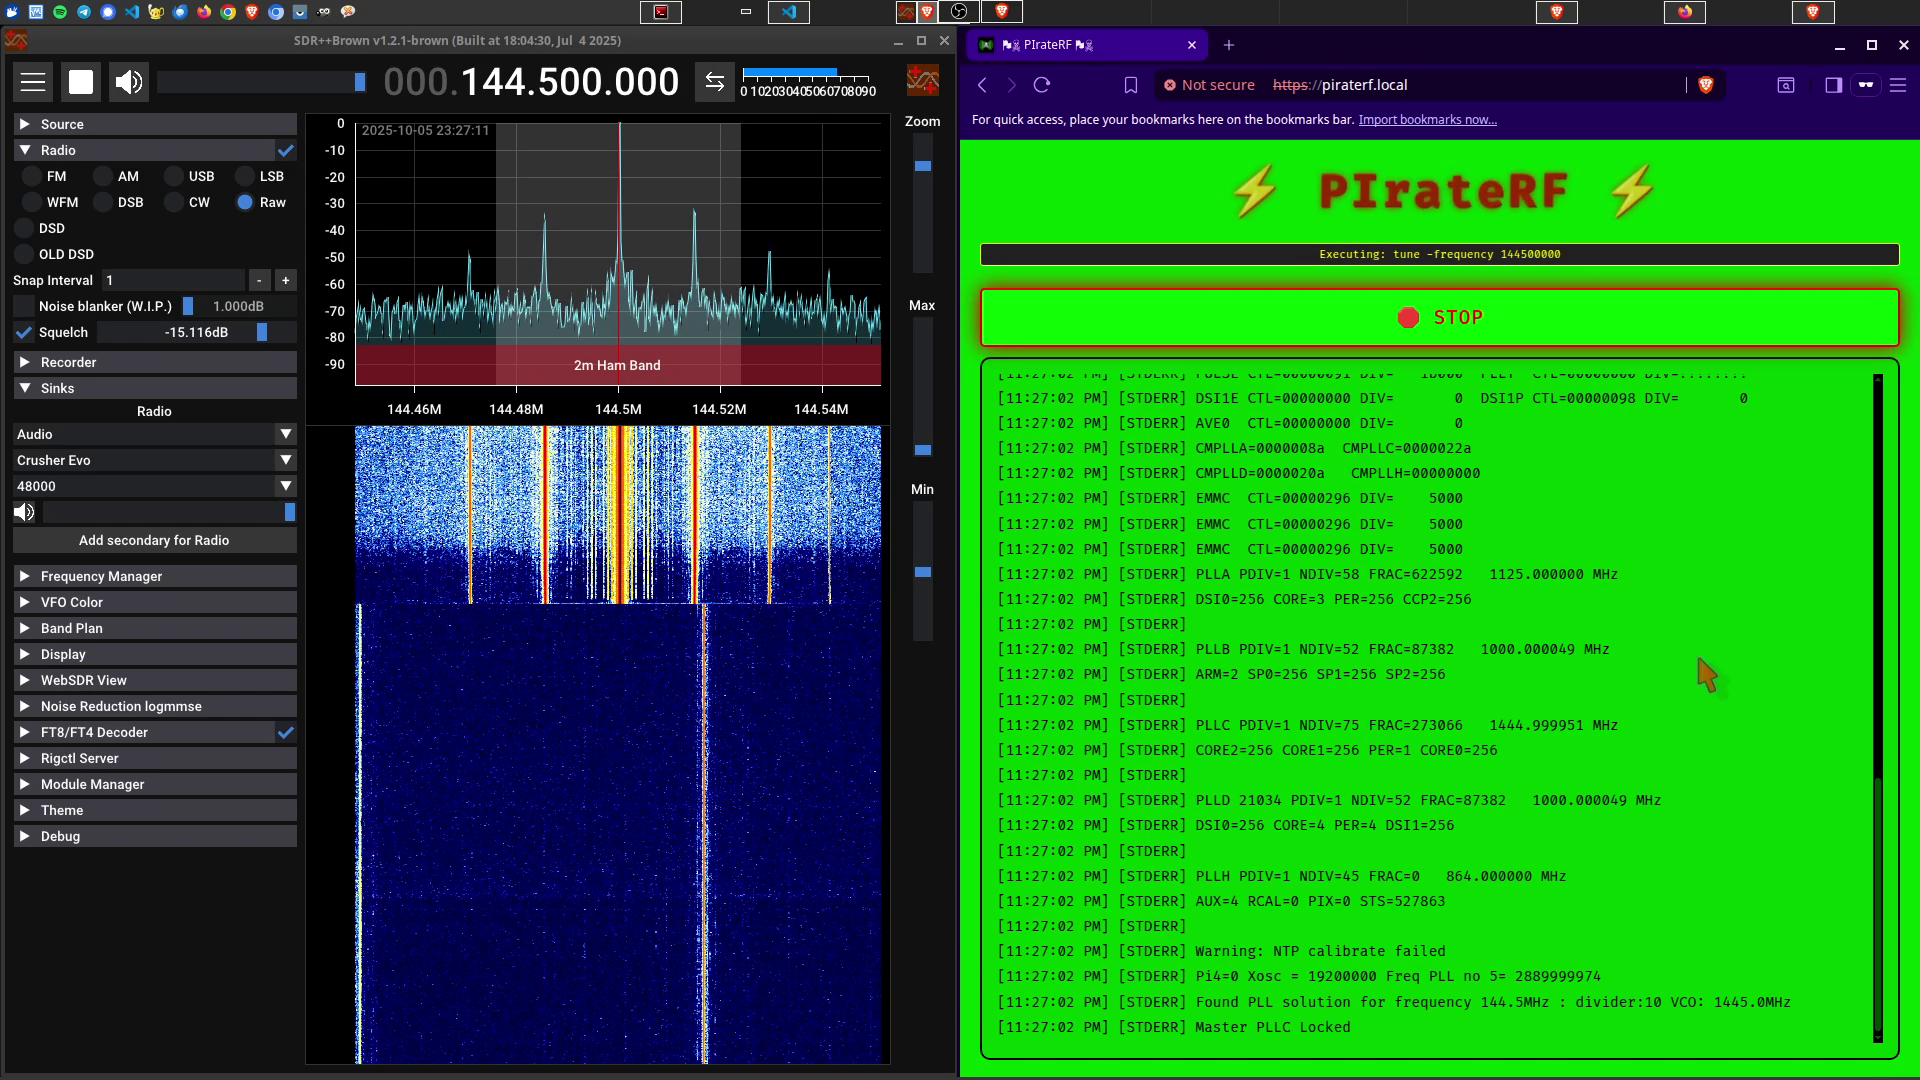 psyb0t/piraterf
PIrateRF transforms your Raspberry Pi Zero W into a portable RF signal generator that spawns its own WiFi hotspot. Control everything from FM…
 asaotomo/hx0-hawkeye
一个轻量级浏览器抓包与安全分析扩展,在浏览器侧边栏中即可完成抓包、拦截、修改、重放、规则检测与AI辅助分析的完整工作流。(A lightweight browser extension for traffic capture and security analysis, enabling…
 gromhacks/payload-and-polyglot-lists
GromHacks Labs -- The payload lists they don't want you to have. 1,324 injection probes beamed down from the mothership to detect what's injectable…
 xteardx/diaphora-mcp
MCP server for automated binary diffing.
 reversenseorg/dexcalibur
[Official] Android reverse engineering tool focused on dynamic instrumentation automation leveraging Frida. It disassembles dex, analyzes it…
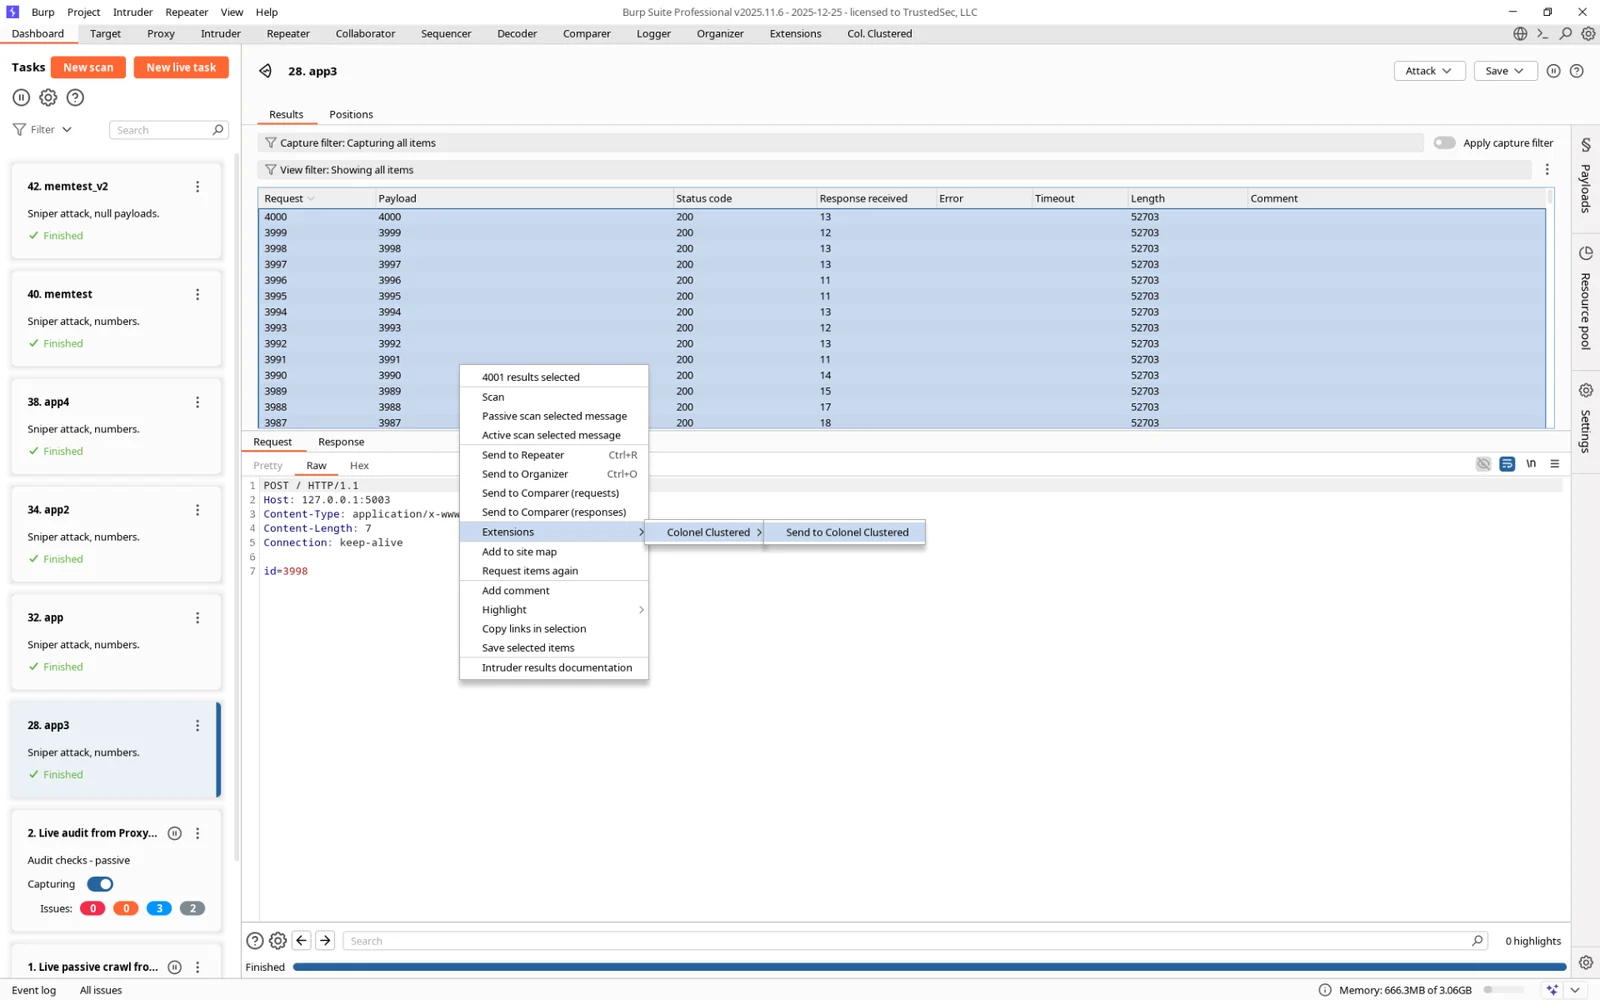 hoodoer/colonelclustered
A Java Burp Plugin that performs text clustering on responses to identify outliers/groups based on the actual content of the server responses, say…
 concollmic/concollmic
LLM-agent-powered concolic execution engine that instruments source code, summarizes path constraints in natural language, and generates test cases…
 r3n3r0/cve-2026-27280
In-depth analysis and proof-of-concept for CVE-2026-27280, an out-of-bounds write in Adobe DNG SDK's dng_render_task::ProcessArea, reachable via…
 piratesshield/apiharvester
The one shot API attacker tool - finds the API url from the given root simulate the automated attacks
 redteampentesting/monsoon
Fast HTTP enumerator