
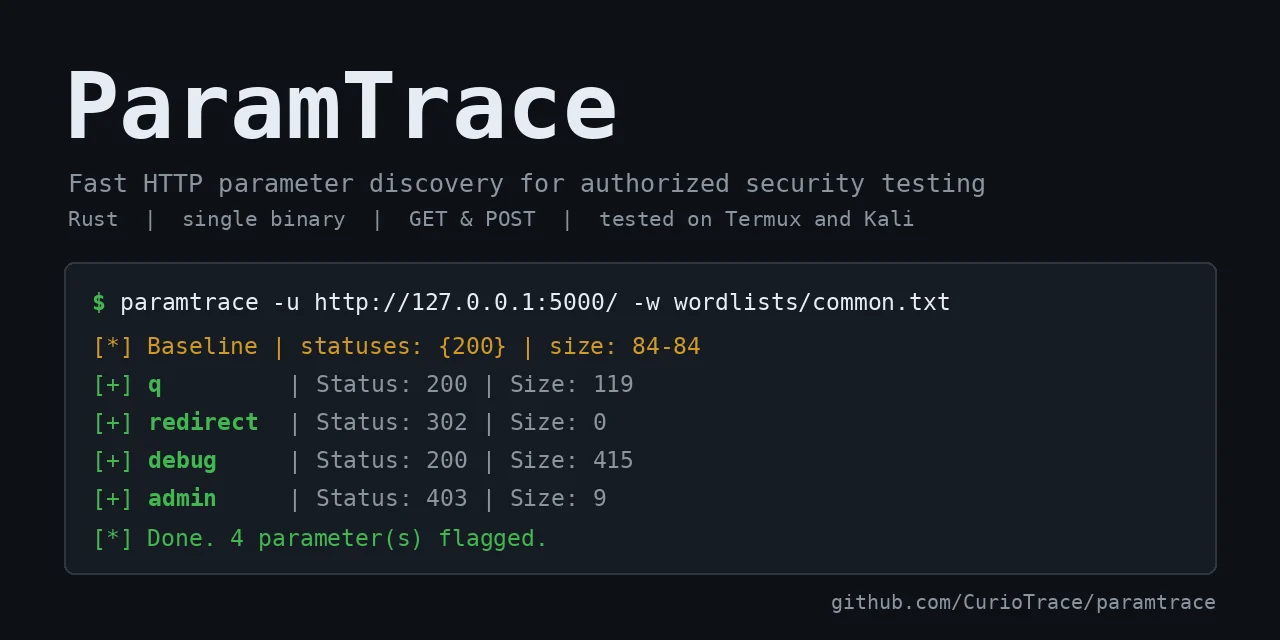
paramtrace
 curiotrace/paramtrace
Fast HTTP parameter discovery for authorized security testing
fuzzinginformation-gatheringpenetration-testing+5
214 days ago
curiotrace/paramtraceFast HTTP parameter discovery for authorized security testing
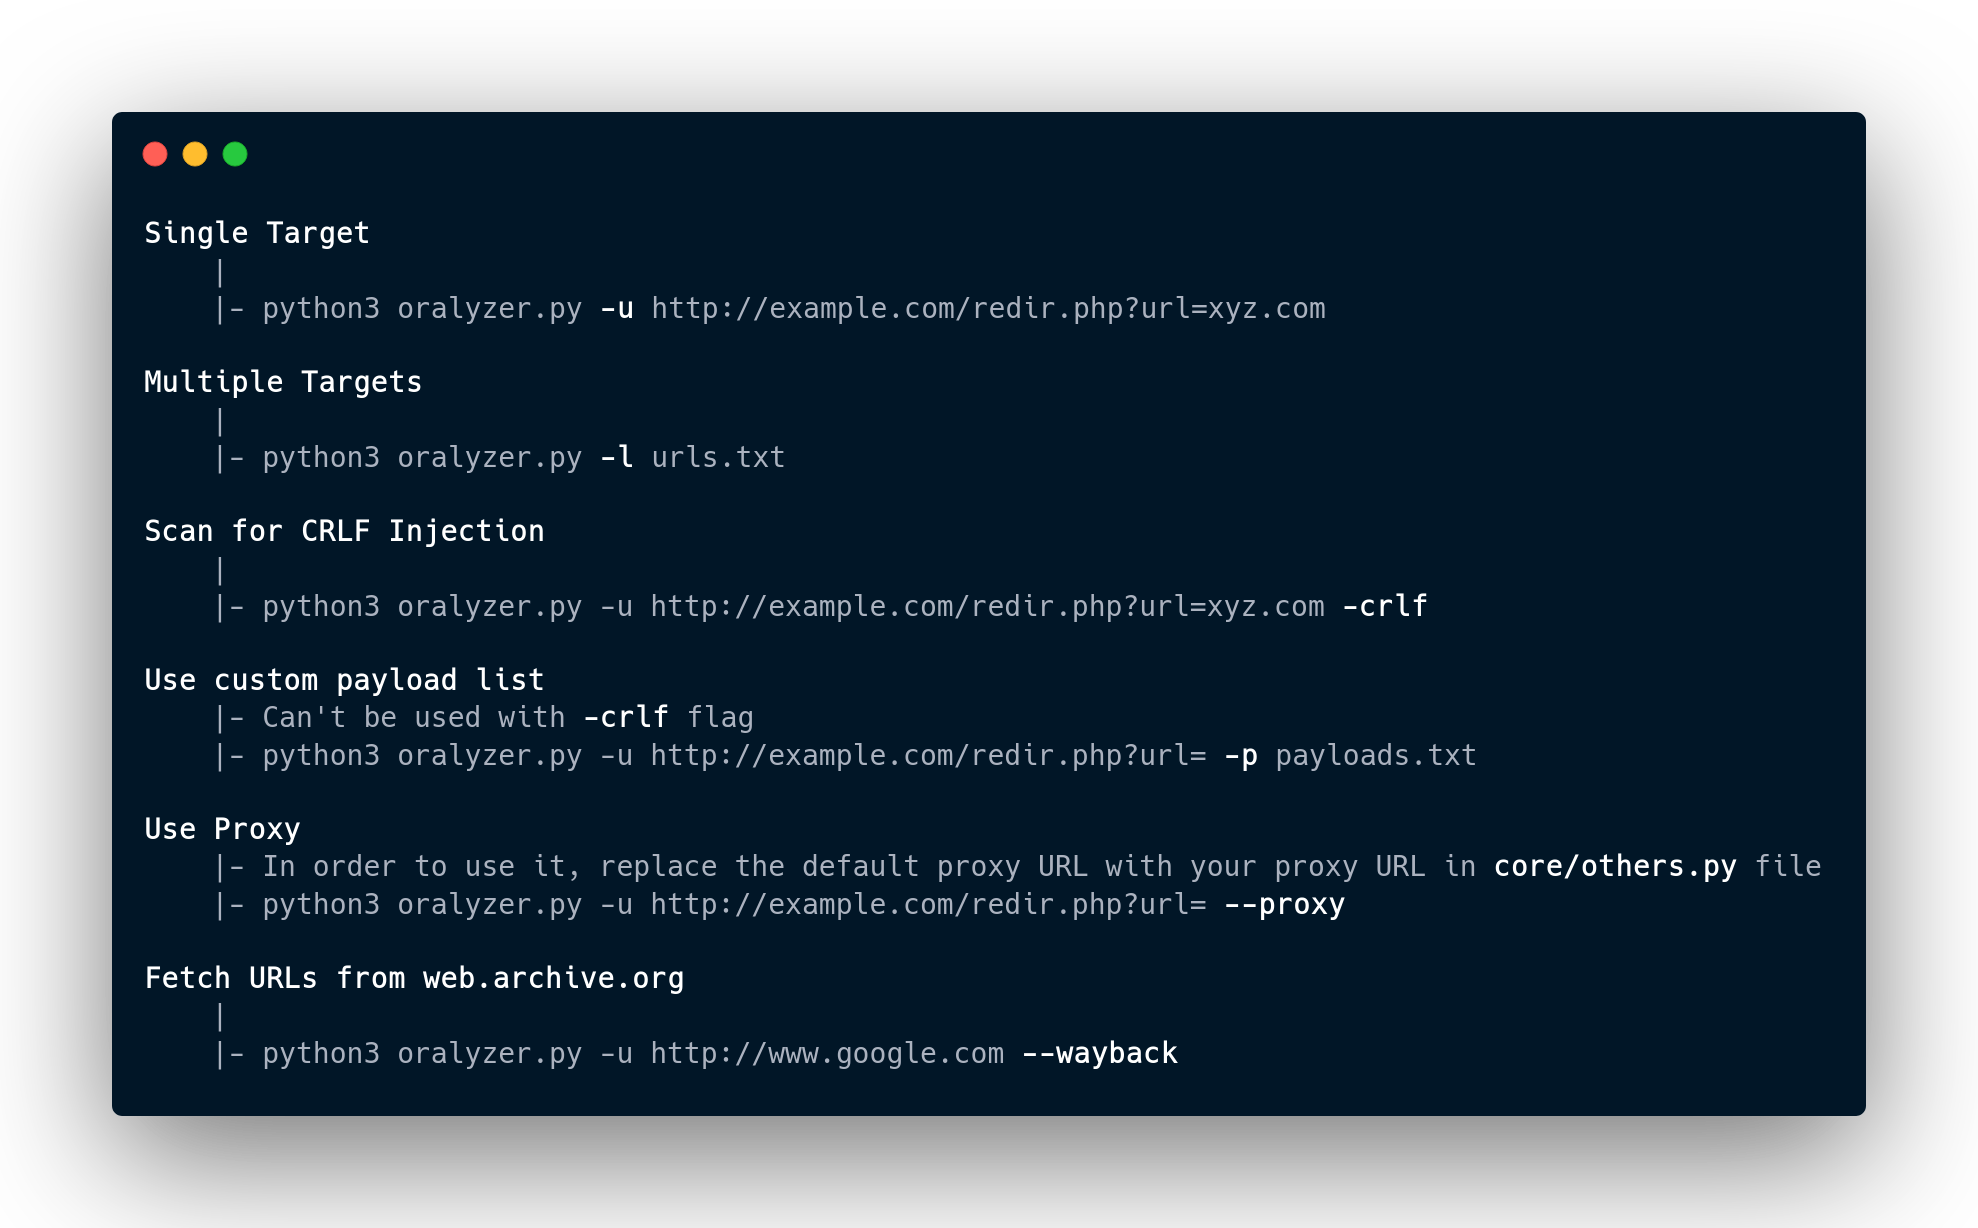 r0075h3ll/oralyzer
Python-based open redirect vulnerability scanner that fuzzes URLs to detect header, JavaScript, and meta tag-based redirects, with integrated…
 mycode83/godirb
Fast and easy-to-use directory brute-forcer written in Go.
 meliht/mr.sip
SIP Security Assessment Framework for VoIP Pentesters. Presented at DEFCON, BlackHat & Offzone.
 pepelux/sippts
Set of tools to audit SIP based VoIP Systems
 mreza-en/cve-2021-21994_poc
Validates and exploits VMware ESXi SFCB authentication bypass (CVE-2021-21994) via a probe/fuzz harness, enabling unauthenticated CIM-XML enumeration.
 redteampentesting/monsoon
Fast HTTP enumerator
 madexploits/ninja-form-exploit
CVE-2026-0740
 noptrix/lulzbuster
A multithreaded, very fast and smart HTTP(S) directory and file bruteforcer written in C on top of libcurl
 overspace-labs/caa
BurpSuite plugin for HTTP packet analysis and fuzzing dictionary generation. Extracts parameters, paths, and files from requests, counts frequency,…
 s_r_e_e_r_a_j/reconhound
ReconHound is a Python-based web reconnaissance tool designed for penetration testers, bug bounty hunters, and ethical hackers. It supports directory…
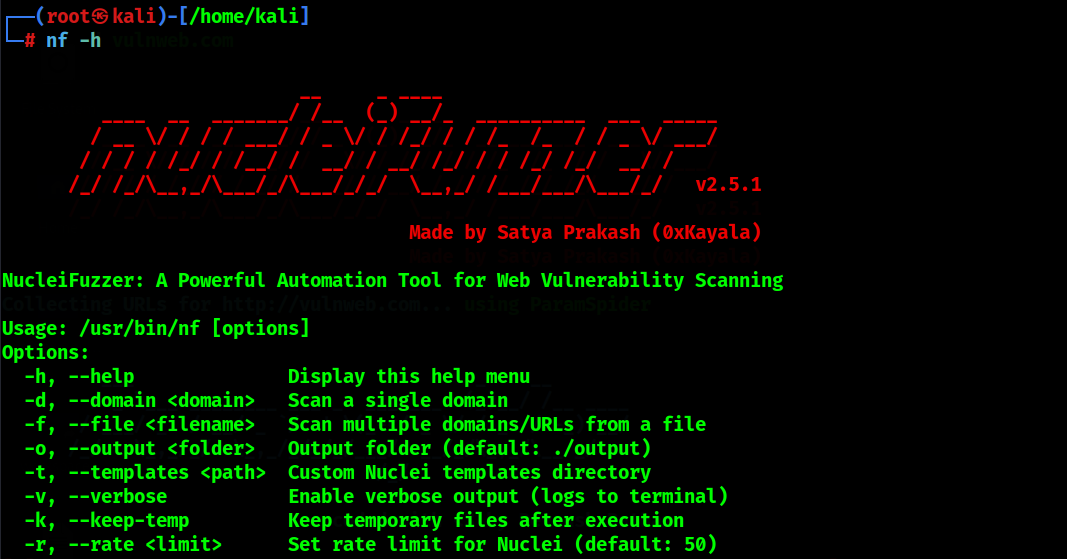 0xkayala/nucleifuzzer
Automated web vulnerability scanner combining URL discovery tools (ParamSpider, waybackurls, gauplus, hakrawler, katana) with Nuclei fuzzing…
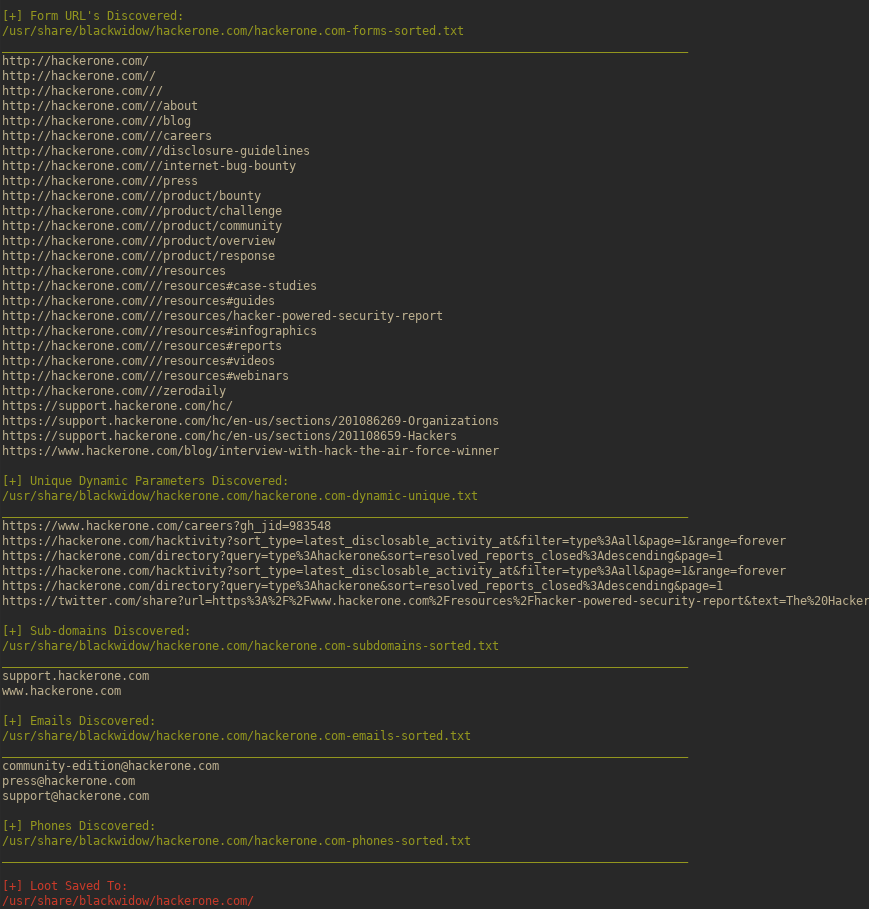 1n3/blackwidow
A Python based web application scanner to gather OSINT and fuzz for OWASP vulnerabilities on a target website.
 dozermx/argus
Multi-phase reconnaissance and attack-surface scanner that maps domains, IPs, ASNs, cloud assets, and CVEs into a knowledge graph with CVSS scoring…
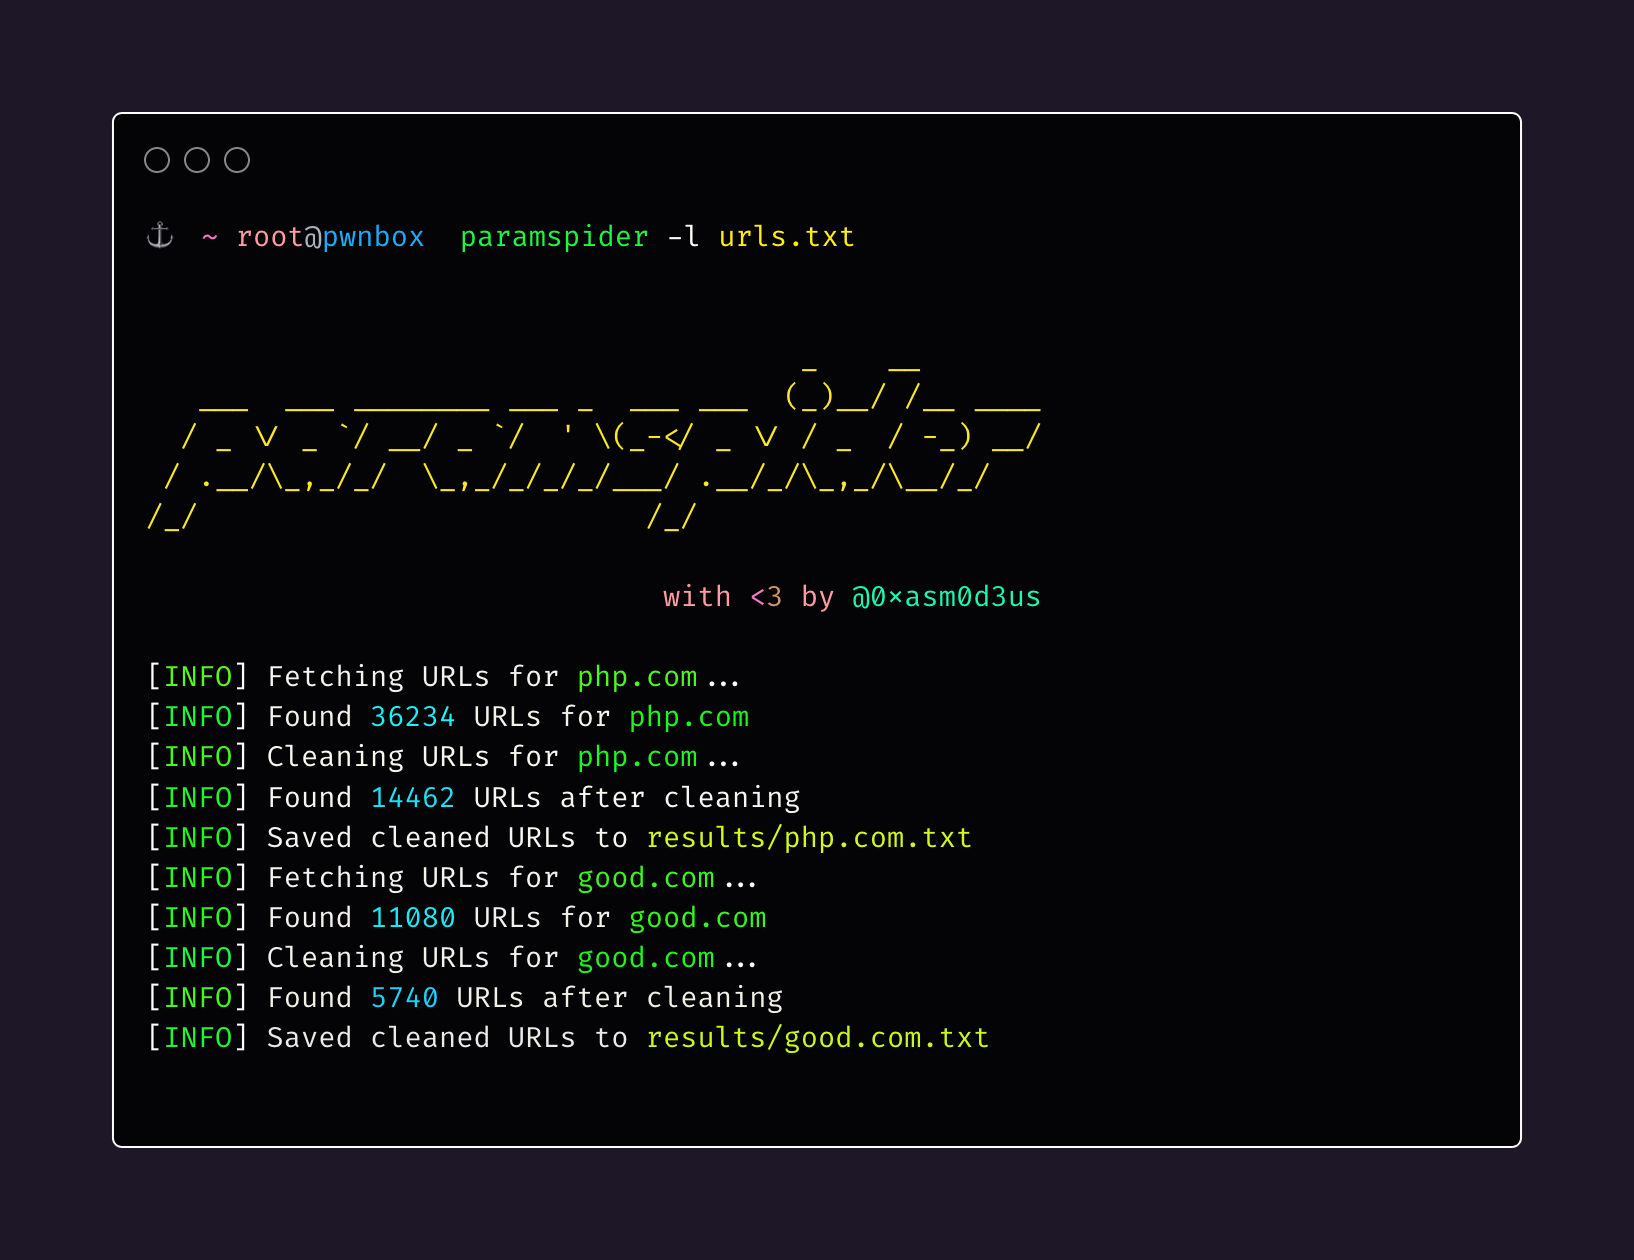 devanshbatham/paramspider
Mining URLs from dark corners of Web Archives for bug hunting/fuzzing/further probing
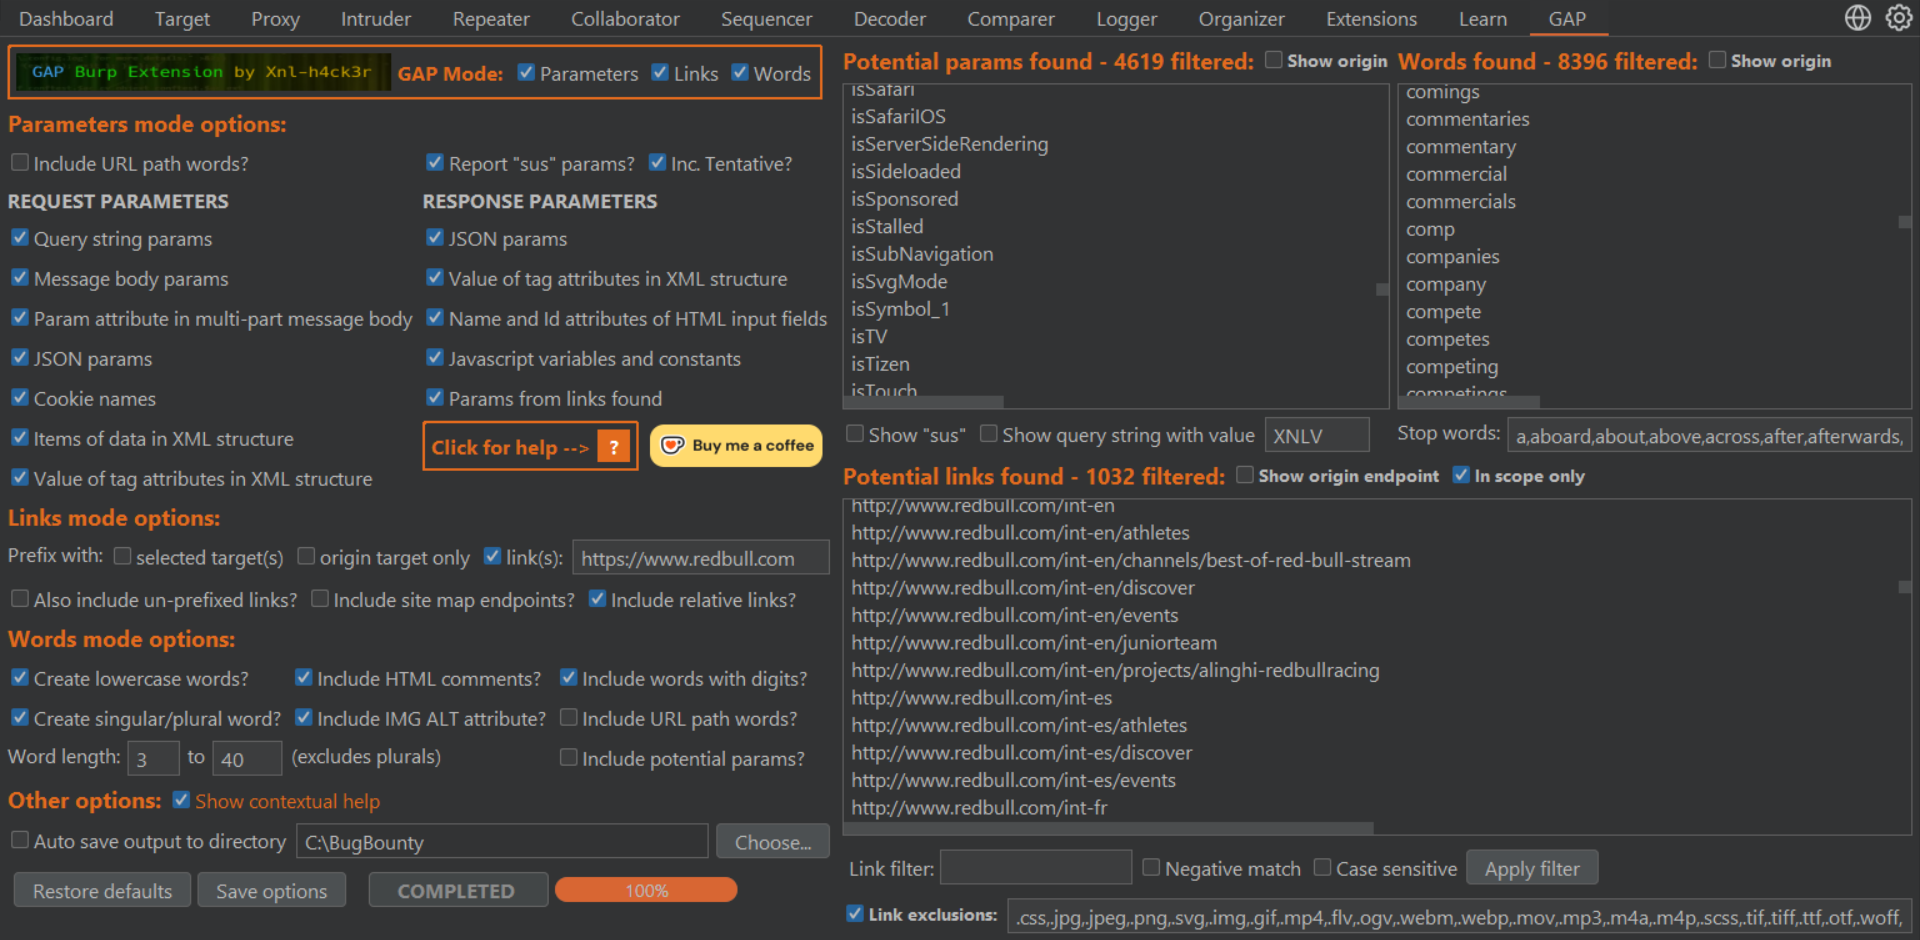 xnl-h4ck3r/gap-burp-extension
Burp Extension to find potential endpoints, parameters, and generate a custom target wordlist
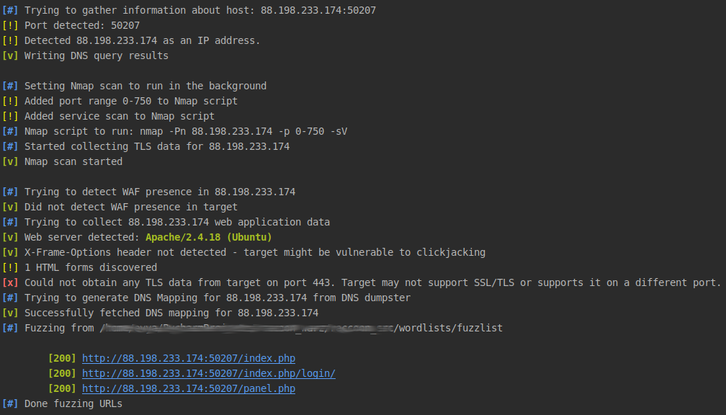 evyatarmeged/raccoon
A high performance offensive security tool for reconnaissance and vulnerability scanning