
FISSURE
 ainfosec/fissure
The RF and reverse engineering framework for everyone. Follow and ★ to show your support!
ctfeducationfuzzing+2
ainfosec/fissureThe RF and reverse engineering framework for everyone. Follow and ★ to show your support!
 danielmiessler/seclists
Curated collection of wordlists for security assessments, including usernames, passwords, URLs, fuzzing payloads, and sensitive data patterns for…
 yaklang/yakit
All-in-one penetration testing platform with MITM proxy, web fuzzer, reverse connection handler, and plugin system for automated security testing and…
 angr/angr
A powerful and user-friendly binary analysis platform!
 secdev/scapy
Python-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…
 dinosn/php-cve-2026-10961x-lab-poc
PHP CVE-2026-109618/109619 — self-contained unauthenticated RCE on stock PHP 8.5.11 (in-band PS(id)→cookie memory disclosure + UAF chain), full…
 vmoranv/jshookmcp
A search-first, profile-aware reverse-engineering workspace for AI agents — 735 tools across 36 domains in one MCP server.
 xuehuolll/cve-2026-109618-109619-audit
CVE-2026-109618 / CVE-2026-109619 audit: session poisoning to command execution reproduced; BGCTX OOM precondition reproduced; claimed progress-array…
 ntop/ndpi
Open Source Deep Packet Inspection Software Toolkit

 albinowax/activescanplusplus
Burp Suite extension that extends active and passive scanning with checks for host header attacks, XXE, expression language injection, shellshock and…
 rfidresearchgroup/proxmark3
Hardware tool for RFID analysis, emulation, and penetration testing. Supports 125kHz, 13.56MHz protocols (MIFARE, iClass, ISO14443/15693) with key…
 curiotrace/paramtrace
Fast HTTP parameter discovery for authorized security testing
 libssh/libssh-mirror
C library implementing the SSH protocol for secure remote access, authentication, and encrypted communication. Includes fuzzing support via OSS-Fuzz…
 tls-attacker/tls-attacker
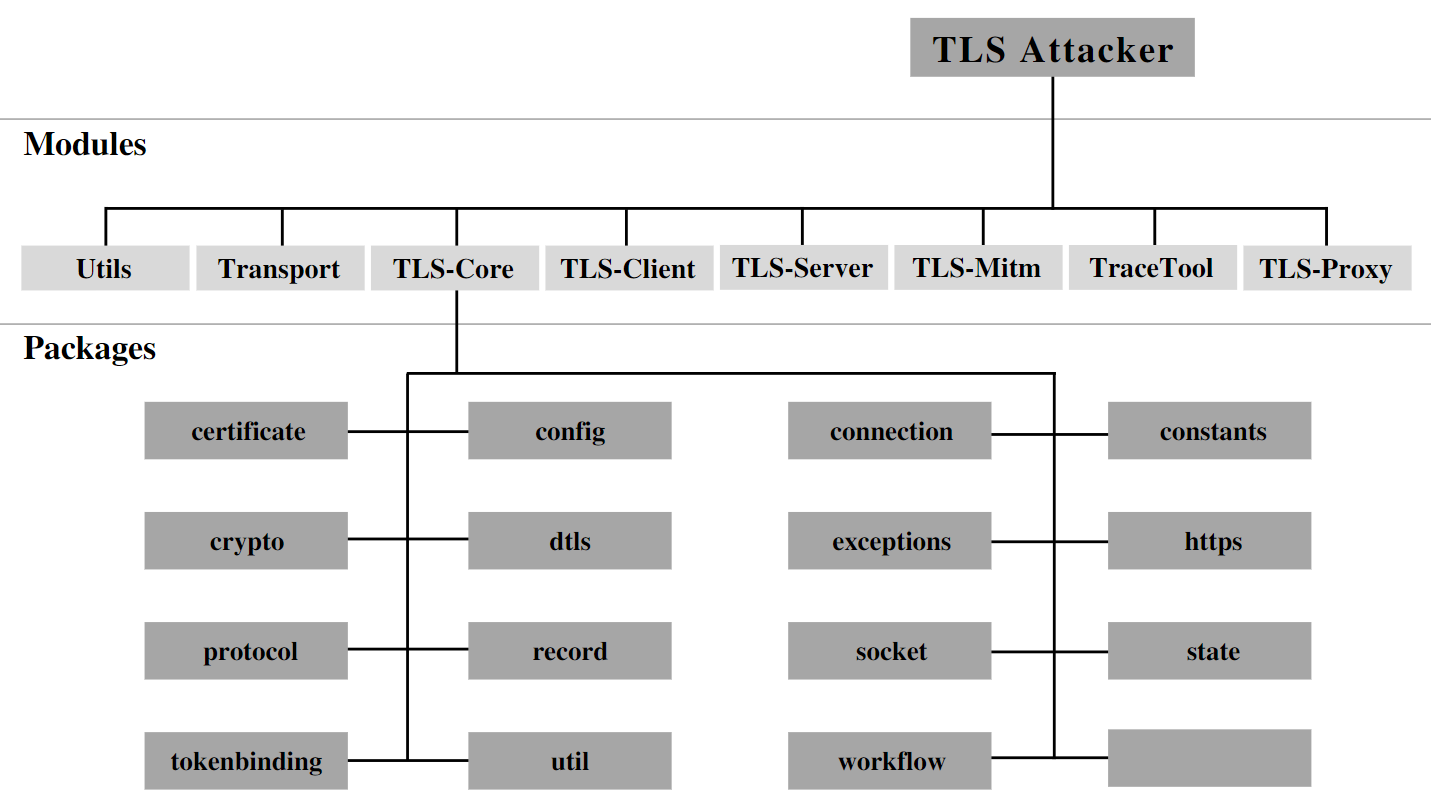
Java-based framework for systematic fuzzing and analysis of TLS libraries. Enables arbitrary protocol message crafting, modification, and testing of…
 vigiloss/vigil
AI harness for long-running code audits, web pentests, and bug bounty hunting, built around how real investigations fail: anchored hypotheses, false…
 gwen001/pentest-tools
A collection of custom security tools for quick needs.
