Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
529 results
splitting-the-email-atom preview

splitting-the-email-atom

GitHubportswigger/splitting-the-email-atom

Research materials and tooling for exploiting email address parser discrepancies to bypass access controls, including fuzzers, Hackvertor tags, CSS…

ctfeducationemail-security+7
99
10 months ago
h2spacex preview

h2spacex

GitHubnxenon/h2spacex

HTTP/2 Last Frame Synchronization (also known as Single Packet Attack) low Level Library / Tool based on Scapy‌ + Exploit Timing Attacks

exploitationfuzzingnetwork-security+6
2293 months ago
ActiveScanPlusPlus preview

ActiveScanPlusPlus

GitHubalbinowax/activescanplusplus

Burp Suite extension that extends active and passive scanning with checks for host header attacks, XXE, expression language injection, shellshock and…
api-security-testingdefensive-toolsexploitation+7
66717 days ago
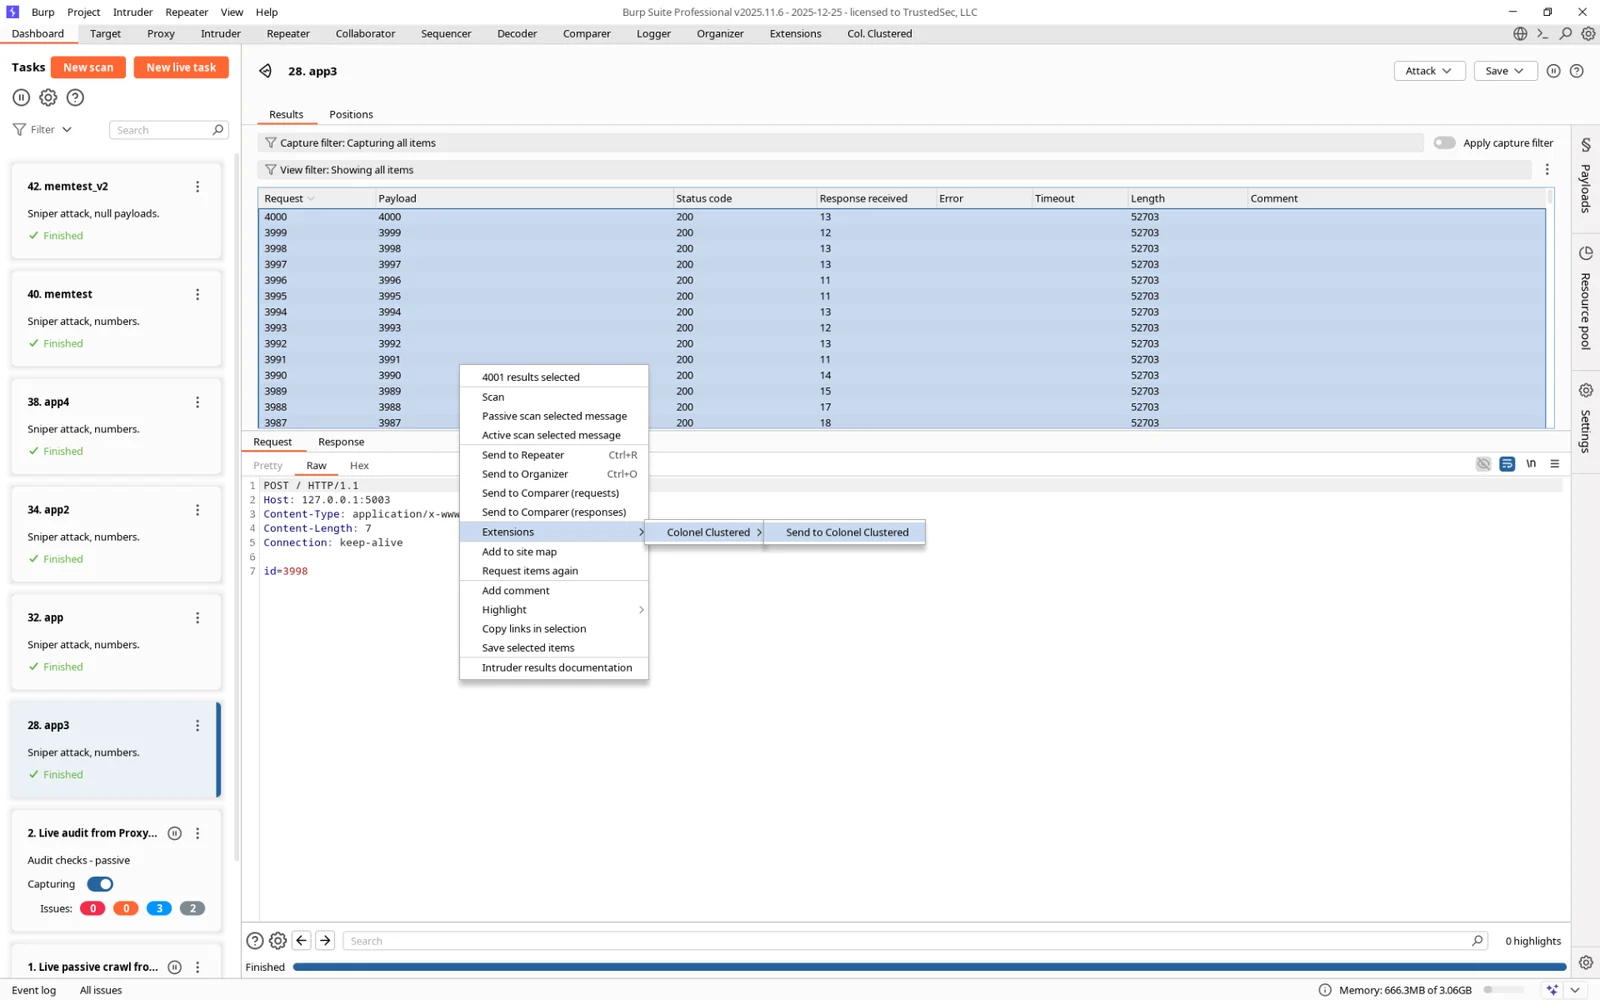
ColonelClustered preview

ColonelClustered

GitHubhoodoer/colonelclustered

A Java Burp Plugin that performs text clustering on responses to identify outliers/groups based on the actual content of the server responses, say…
fuzzingmachine-learningpenetration-testing+5
1218 days ago
WebSocketTurboIntruder preview

WebSocketTurboIntruder

GitHubd0ge/websocketturbointruder

Burp Suite extension for fuzzing WebSocket messages with custom Python code, supporting multiple engines, HTTP middleware routing, and response…

api-security-testingfuzzingpenetration-testing+5
121 year ago
shadow-repeater preview

shadow-repeater

GitHubhackvertor/shadow-repeater

Burp Suite Repeater extension that automatically mutates payloads and analyzes responses to uncover path traversal, SQL injection, XSS, and other web…

ai-securityapi-security-testingfuzzing+6
4310 months ago
APIHarvester preview

APIHarvester

GitHubpiratesshield/apiharvester

The one shot API attacker tool - finds the API url from the given root simulate the automated attacks
api-securityapi-security-testingcrawler+9
322 months ago
http-terminator preview

http-terminator

GitHubportswigger/http-terminator

AI-assisted research pipeline that extracts HTTP desync techniques, generates malformed request test-cases, validates them via Burp, and confirms…

ai-securityexploitationfuzzing+8
1242 months ago
akca preview

akca

GitHubakha-security/akca

Evidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.
api-security-testingdefensive-toolsdynamic-analysis-sandboxing+9
2224 days ago
WordList preview

WordList

GitHubrix4uni/wordlist

Curated collection of custom wordlists for fuzzing, DNS enumeration, parameter discovery, and default credentials, plus a Go generator for nuclei…
dns-subdomain-enumerationfuzzinginformation-gathering+6
1553 months ago
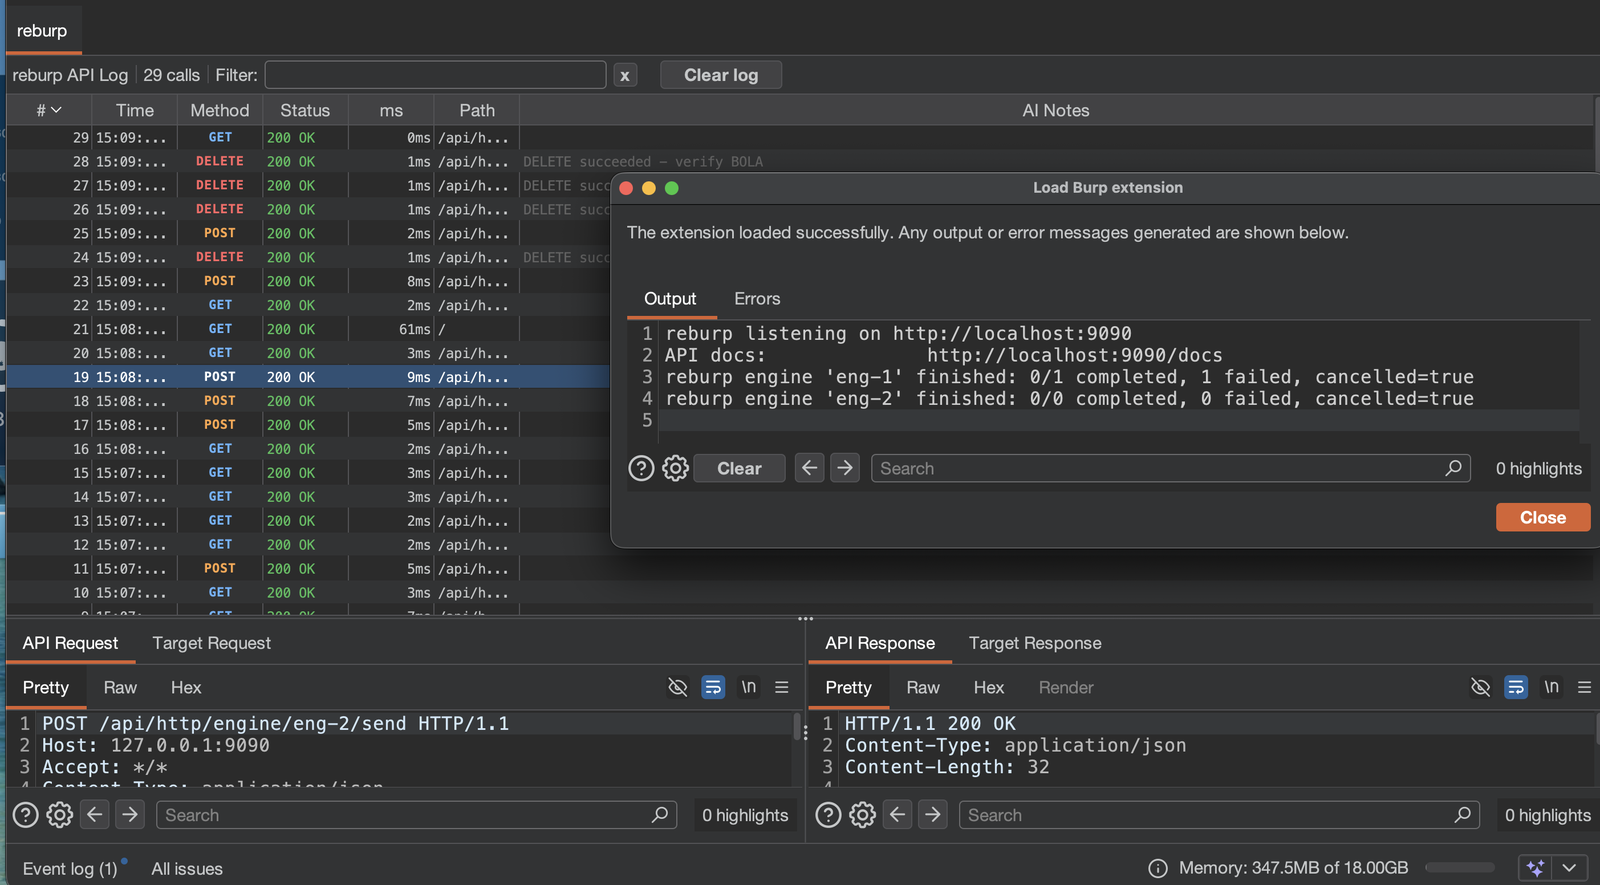
reburp preview

reburp

GitHubforefy/reburp

A Burp Suite extension that exposes the full Montoya API as a local REST API, with Swagger UI
ai-securityapi-security-testingfuzzing+7
1173 days ago
PixelSmash preview

PixelSmash

GitHubse1ims/pixelsmash

Proof-of-concept and lab harness for CVE-2026-8461, an out-of-bounds write in FFmpeg's MagicYUV decoder, with payload generator and Qt demo player.
binary-exploitationeducationexploitation+6
13 days ago
rcekit preview

rcekit

GitHubkabiri-labs/rcekit

RCE detection and confirmation toolkit that tests URLs or captured HTTP requests for command injection, SSTI, blind and OOB paths, returning tiered…
command-and-controlexploitationfuzzing+8
256 days ago
cve-2021-44790-lab preview

cve-2021-44790-lab

GitHubmohammadalimehri/cve-2021-44790-lab

Dockerized Apache mod_lua lab with a Python PoC reproducing the CVE-2021-44790 multipart boundary buffer overflow for local defensive testing and…

educationexploitationfuzzing+5
18 days ago
Veridiff preview

Veridiff

GitHubveridiff/veridiff

Dynamic branch-divergence finder for native code -- traces two Frida executions and finds the exact instruction where they diverge.

binary-analysisbinary-exploitationcode-analysis+7
67 days ago
OmniSec-Hex preview

OmniSec-Hex

GitHubvighnesh91/omnisec-hex

Browser-local security monorepo with six modules for mobile APK/IPA triage, client-side DAST fuzzing, OSINT directories, offline AI threat scoring,…
ai-securitybinary-analysisfuzzing+9
217 days ago
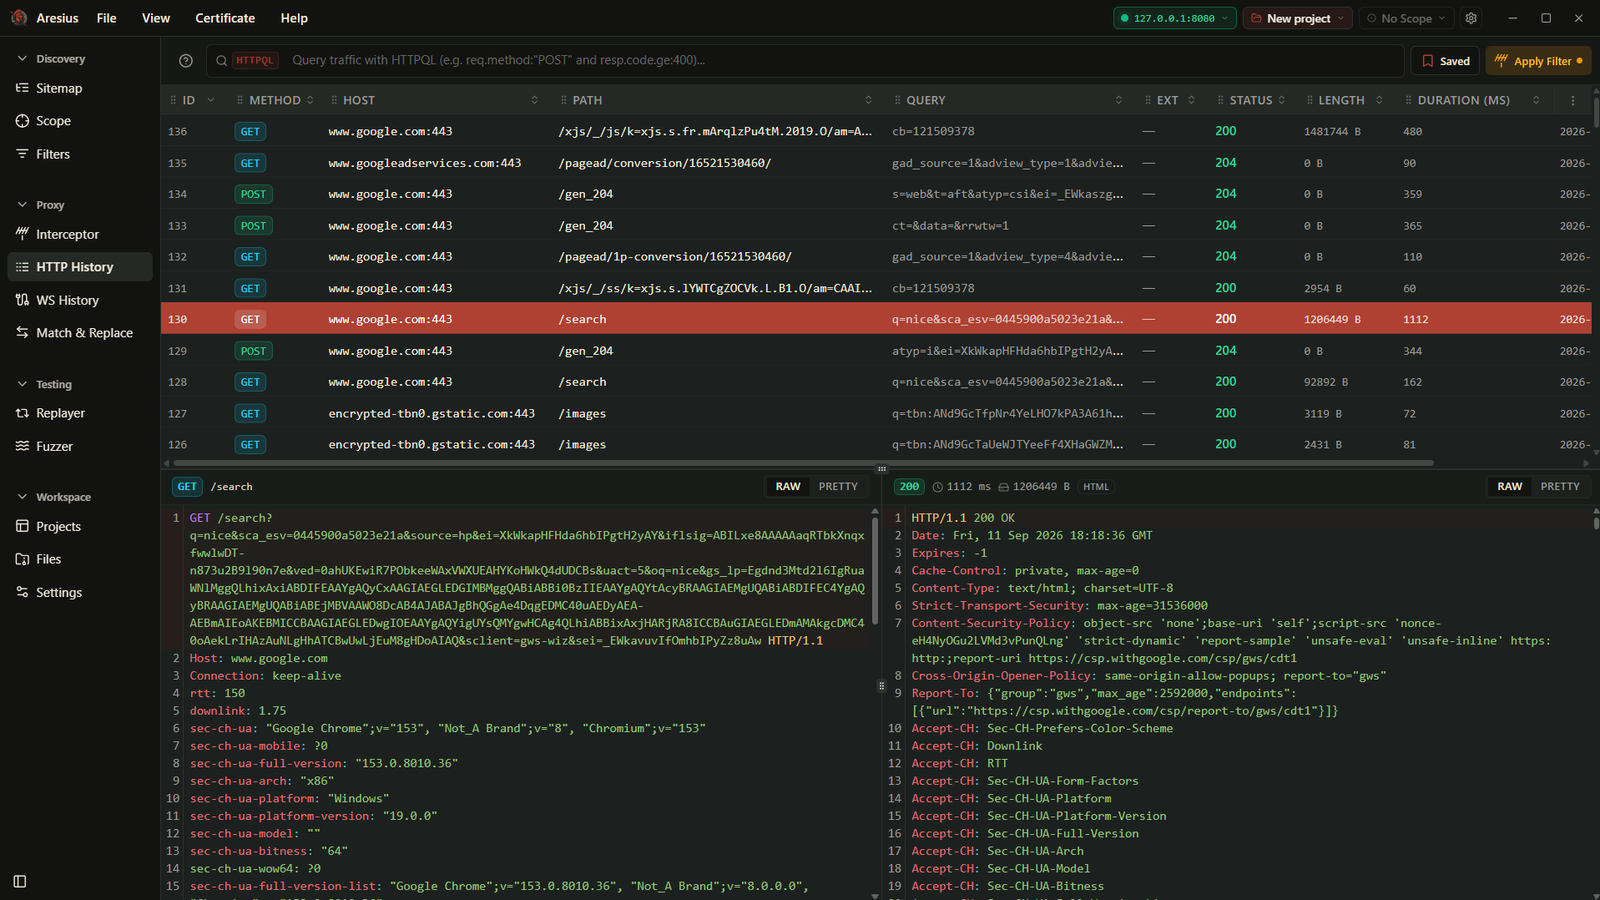
Aresius preview

Aresius

GitHub0xmarik/aresius

Native HTTP/HTTPS interception proxy for penetration testers and bug bounty hunters with live request tampering, request replay, high-speed fuzzing,…
api-security-testingfuzzinginformation-gathering+6
720 days ago
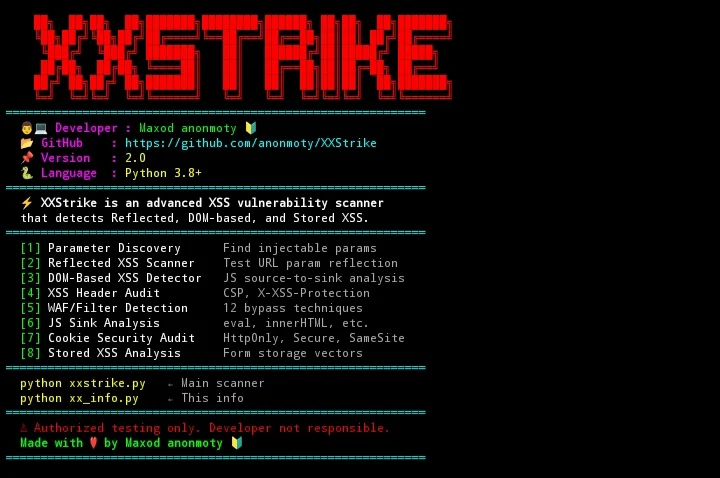
XXStrike preview

XXStrike

GitHubanonmoty/xxstrike

XSStrike based XSS scanner with custom features. Detects XSS vulnerabilities in web applications.

dynamic-code-analysisfuzzingpenetration-testing+5
323 days ago
Previous12…30Next
