
discord-crasher
 aftermathlabs/discord-crasher
Some bugs found via binary instrumentation and fuzzing
binary-analysisdynamic-analysis-sandboxingexploitation+5
23
aftermathlabs/discord-crasherSome bugs found via binary instrumentation and fuzzing
 vsvalinx/cve-2025-5548
Educational repository documenting the full exploitation lifecycle of a stack buffer overflow in FreeFloat FTP Server 1.0, including fuzzing, EIP…
 canomer/cve-2026-36981-kernel-eop-poc
Project Date : Feb 2026 / Memory corruption vulnerability within the kernel driver of MiniTool. Demonstrates a debugger-assisted arbitrary kernel…
 google/honggfuzz
Security oriented software fuzzer. Supports evolutionary, feedback-driven fuzzing based on code coverage (SW and HW based)
 rust-fuzz/cargo-fuzz
Cargo subcommand for coverage-guided Rust fuzzing with libFuzzer: create and run fuzz targets, minimize failures and corpora, and report coverage.
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
 josephfarah-ciso/cve-2026-9999-exploit
Proof-of-concept and GLSL fuzzer for CVE-2026-9999 in Chrome's ANGLE/Metal WebGL backend, with build fingerprinting, curated shaders, and crash…
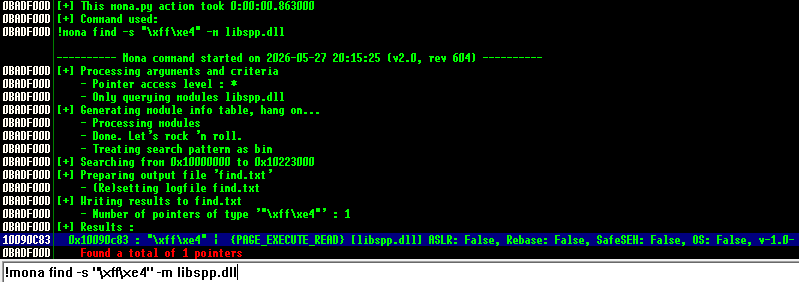 godoy-sec/cve-2017-14980
Study of a classic stack-based buffer overflow vulnerability in a controlled lab environment for educational purposes.
 quarkslab/rewind
Snapshot-based coverage-guided windows kernel fuzzer
 tandasat/hypervisor-101-in-rust
The materials of "Hypervisor 101 in Rust", a one-day long course, to quickly learn hardware-assisted virtualization technology and its application…
 hugsy/windbg_js_scripts
Toy scripts for playing with WinDbg JS API
 intellabs/kafl
A fuzzer for full VM kernel/driver targets
 turtlesec-software/crlf-desyncs
Nuclei templates and exploit resources for CRLF based desync attacks
 skylined/bugid
Detect, analyze and uniquely identify crashes in Windows applications
 nccgroup/dibf
Windows NT ioctl bruteforcer and modular fuzzer
 nccgroup/memscan
Searches for strings, regex, credit card numbers of magnetic stripe card tracks in a Windows process's memory space
 nccgroup/mnemosyne
A Generic Windows Memory Scraping Tool
 google/syzkaller
Unsupervised coverage-guided kernel fuzzer for Linux and major OS kernels; automatically discovers security vulnerabilities through intelligent…