
red-teaming-auto-mode
 safety-research/red-teaming-auto-mode
Research code for red-teaming AI auto-mode monitors, including simulation evals, fuzzing, and monitor implementations for Claude Code and Codex…
ai-securityeducationfuzzing+3
1
safety-research/red-teaming-auto-modeResearch code for red-teaming AI auto-mode monitors, including simulation evals, fuzzing, and monitor implementations for Claude Code and Codex…
 ivanesk315/cve-2026-42533
Docker lab reproducing CVE-2026-42533, a pre-auth nginx heap overflow and info leak via two-pass capture clobbering, with PoC scripts and patched…
 johanneslks/cve-2026-32945
PJSIP DNS Compression Pointer Heap OOB Read (Remote DoS)
 zpol/cve-2026-23398-poc
Reproducible lab for CVE-2026-23398, a Linux kernel NULL dereference in icmp_tag_validation() triggered by ICMP Fragmentation Needed packets, causing…
 trailofbits/polytracker
An LLVM-based instrumentation tool for universal taint tracking, dataflow analysis, and tracing.
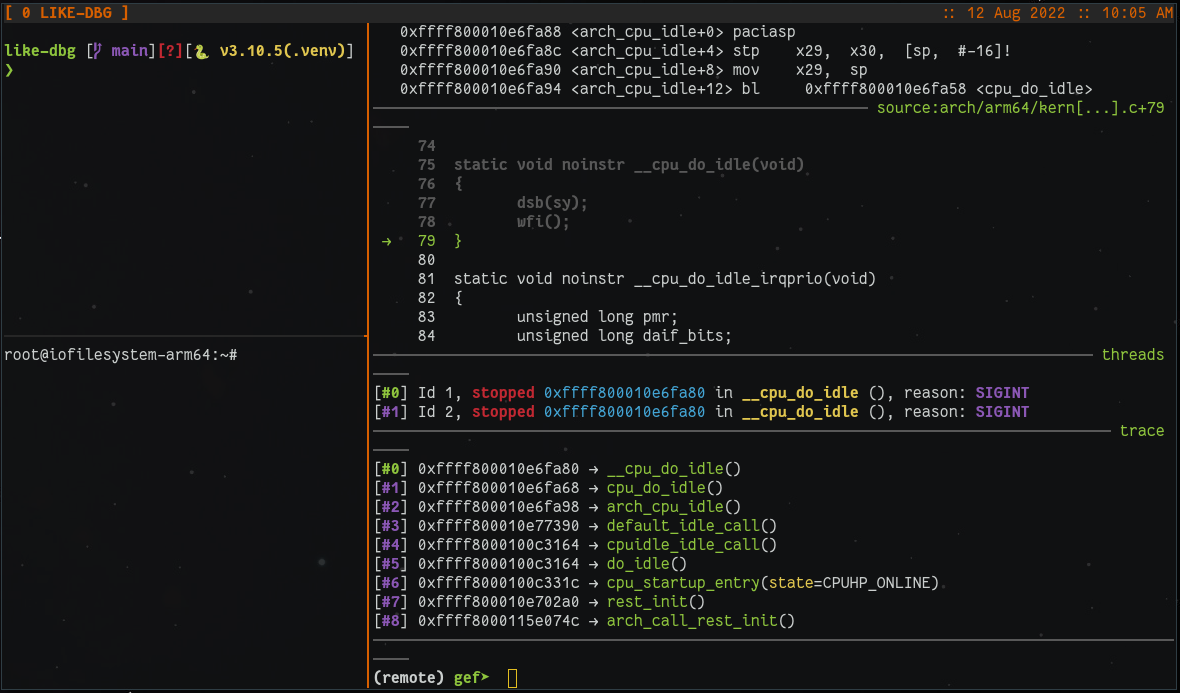 0xricksanchez/like-dbg
Fully dockerized Linux kernel debugging environment
 impalabs/hyperpom
AArch64 fuzzer based on the Apple Silicon hypervisor
 tandasat/hypervisor-101-in-rust
The materials of "Hypervisor 101 in Rust", a one-day long course, to quickly learn hardware-assisted virtualization technology and its application…
 uni-due-syssec/efcf-framework
EF/CF - Extremely Fast smart Contract Fuzzing
 intellabs/kafl
A fuzzer for full VM kernel/driver targets
 awslabs/snapchange
Lightweight fuzzing of a memory snapshot using KVM
 narfindustries/http-garden
Differential testing framework for HTTP implementations
 xairy/vmware-exploitation
A collection of links related to VMware escape exploits
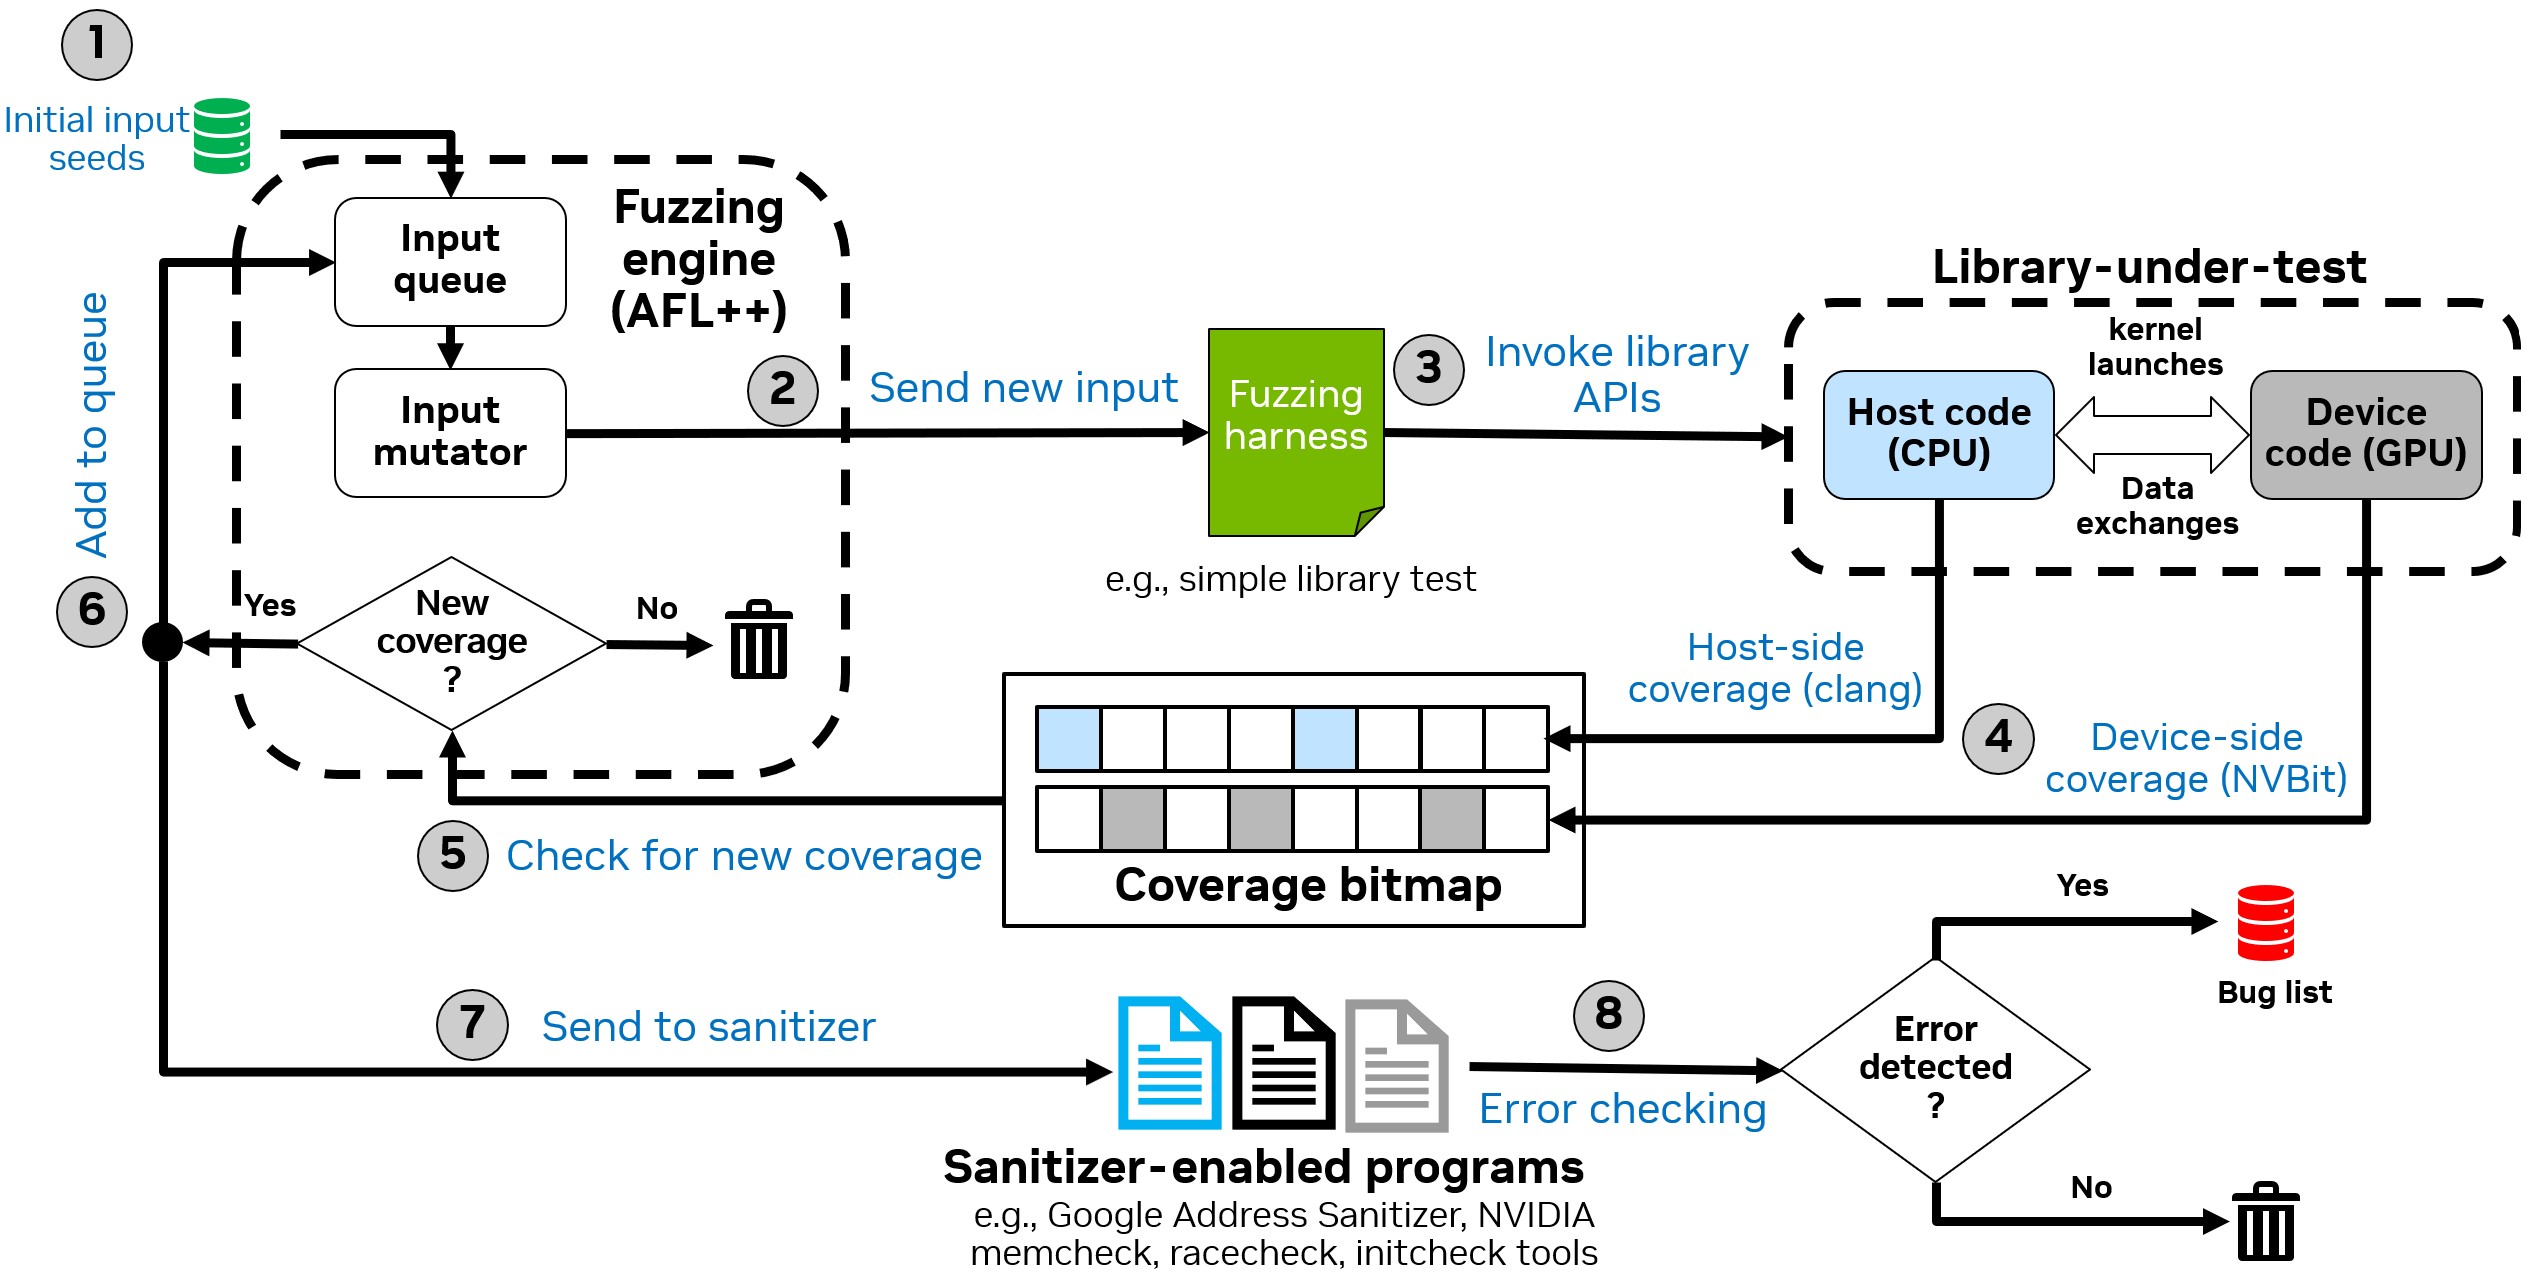 nvlabs/cufuzz
A GPU-oriented coverage-guided fuzzer for userland CUDA applications
 alt3kx/cve-2026-23918
CVE-2026-23918 Apache mod_http2 Double-Free Detector
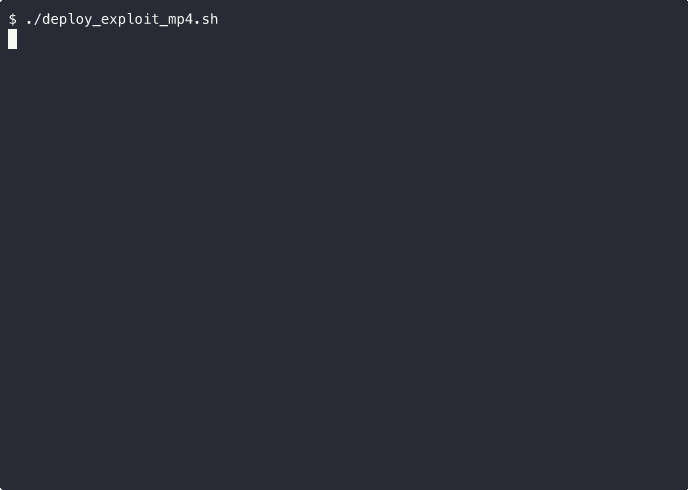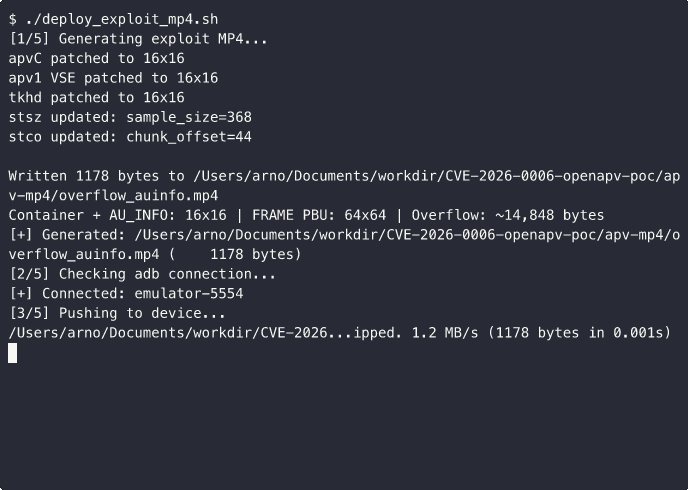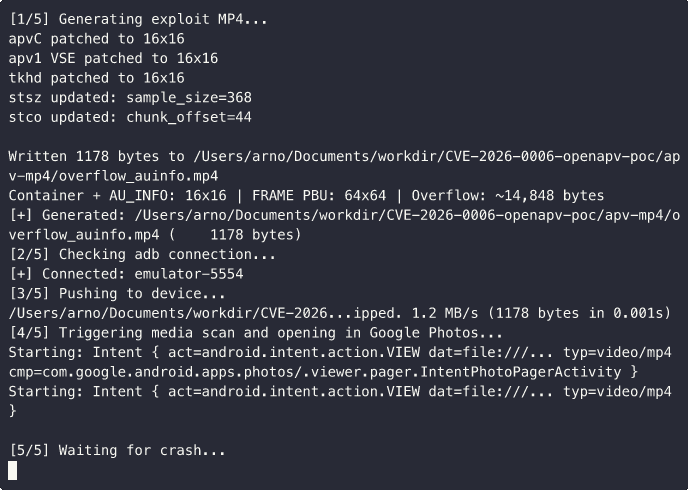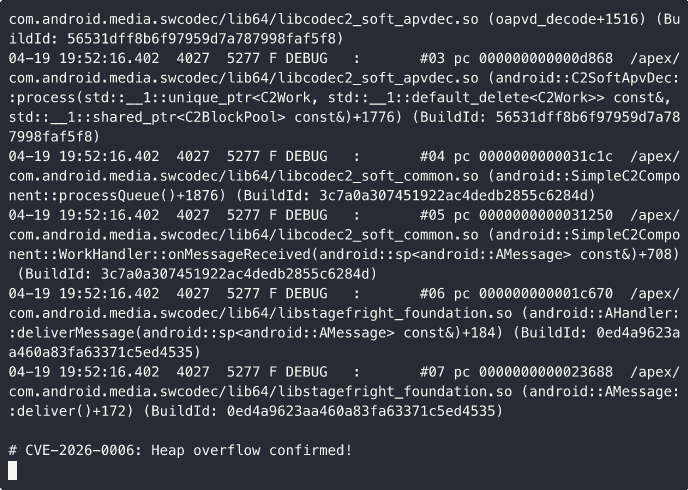 mobilehackinglab/cve-2026-0006-openapv-poc
CVE-2026-0006: Heap buffer overflow PoC for libopenapv (Android APV codec) - CVSS 9.8
 sunblaze-ucb/exploitgym
ExploitGym is a large-scale, realistic benchmark built from real-world vulnerabilities designed to evaluate AI agents' ability to develop exploits.
 kmkz/exploits
Original CVEs, exploit PoCs, and security advisories with detailed vulnerability chains, privilege escalation, and container escape techniques for…