
cve-2026-86547-mrubyc-op-enter
 harshrajsinghania/cve-2026-86547-mrubyc-op-enter
Standalone proof of concept for CVE-2026-86547, a NULL pointer dereference in mrubyc op_enter() through 4.0.0.
embedded-systems-securityexploitationfuzzing+3
harshrajsinghania/cve-2026-86547-mrubyc-op-enterStandalone proof of concept for CVE-2026-86547, a NULL pointer dereference in mrubyc op_enter() through 4.0.0.
 isukasanuj/cve-2026-85769
Proof-of-concept exploit for CVE-2026-85769, a heap out-of-bounds read in libtpms TPM 2.0 state deserialization, demonstrating denial of service via…
 acen28/cve-2026-26399-disclosure
Disclosure of a stack-based use-after-return vulnerability in Arduino_Core_STM32, detailing technical root cause, affected versions, and fix, with…
 0xbbdd/cve-2026-33317
Proof-of-concept for CVE-2026-33317, an out-of-bounds write in OP-TEE PKCS#11 TA, demonstrating Secure World heap corruption via a malformed…
 darkflippers/unleashed-firmware
Custom firmware for Flipper Zero enabling Sub-GHz radio, NFC/RFID emulation, infrared, and BadUSB attack features for hardware security testing.
 quarkslab/rewind
Snapshot-based coverage-guided windows kernel fuzzer
 nccgroup/edidfuzzer
EDID (Enhanced Display Identification Data) Fuzzer
 nccgroup/nobex
nOBEX allows emulating the PBAP, MAP, and HFP profiles to test vehicle infotainment systems and similar devices using these profiles

 tothi/pwn-hisilicon-dvr
Proof-of-concept exploit and vulnerability disclosure for HiSilicon hi3520d DVR/NVR devices. Demonstrates RCE via web interface, backdoor…
 rfidtool/esp-rfid-tool
A tool for logging data/testing devices with a Wiegand Interface. Can be used to create a portable RFID reader or installed directly into an existing…
 openrce/sulley
A pure-python fully automated and unattended fuzzing framework.
 openrce/paimei
A reverse engineering framework written in Python.
 nccgroup/cecster
A GUI-based tool to perform security testing against the HDMI CEC (Consumer Electronics Control) and HEC (HDMI Ethernet Channel) protocols
 zcutlip/bowcaster
Python-based exploit development framework with payloads, encoders, and connect-back servers, focused on MIPS CPU architecture but designed for…
 yeahhbean/cve-2026-45729
ThorVG NULL pointer dereference via malformed SVG — AFL++ fuzzing writeup
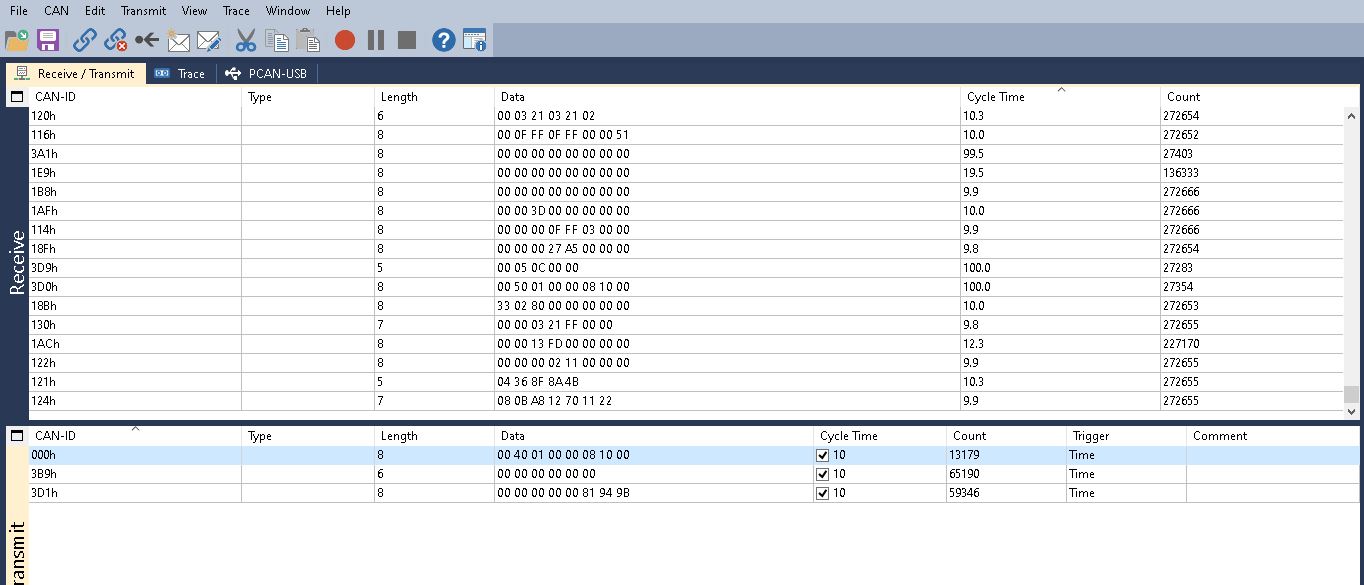 nsbogam/cve-2022-26269
Suzuki connect app is used to get the car information like Fuel, Ignition status, Current location, Seat buckle status etc. In Ignis, Zeta variant…
 passwa11/re11s_1.11-formaccept-commandinjection
CVE-2025-22912